
CVE-2010-2075
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
educationexploitationlabs-practice+7
rushikesh-a-bhujbal/cve-2010-2075UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 muhammad-usama-sardar/intra-handshake-fail
Early Attestation Considered Very Harmful (CVE-2026-92701, CVE-2026-92702, CVE-2026-33697, and more to come)
 mattia-maria-scivoletto/internet-security-project
Academic report and LaTeX sources analyzing Maltego vulnerability CVE-2020-24656, an XXE injection enabling data exfiltration, written for an…
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
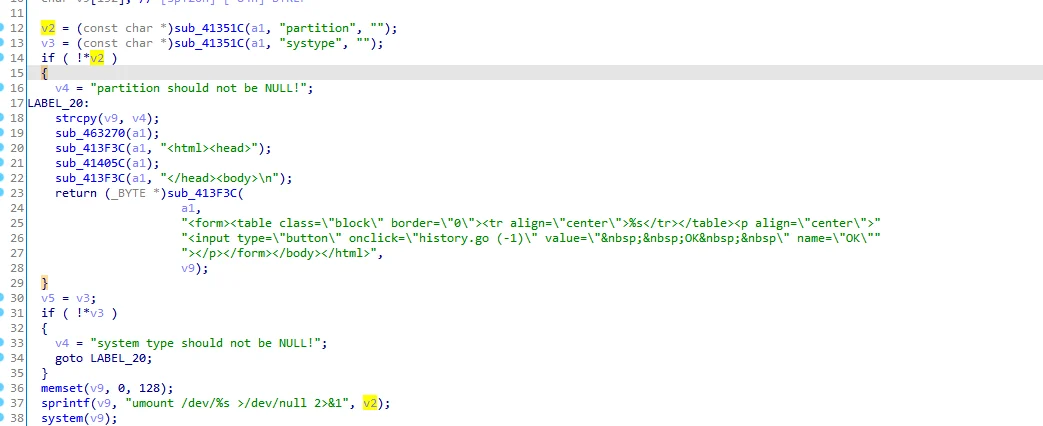 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 kemrec/cve-2025-11142-axis-mediaclip-rce
Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…
 drbloop2000/cve-2026-19745
Learn how I found my first two CVEs by pure accident.
 pedrorichil/cve-2025-49844
Educational lab environment demonstrating CVE-2025-49844 (RediShell) in Redis. Includes Docker setup, exploit PoC script, and security…
 mbanyamer/cve-2026-26235-jung-smart-visu-server-unauthenticated-reboot-shutdown
Proof-of-concept exploit for CVE-2026-26235, an unauthenticated denial-of-service vulnerability in JUNG Smart Visu Server <=1.1.1050, allowing remote…
 mattgsys/cve-2026-0834
Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…
 lastvocher/redis-cve-2025-49844
Educational lab environment with a proof-of-concept exploit for CVE-2025-49844 (RediShell), a critical use-after-free in Redis Lua interpreter,…
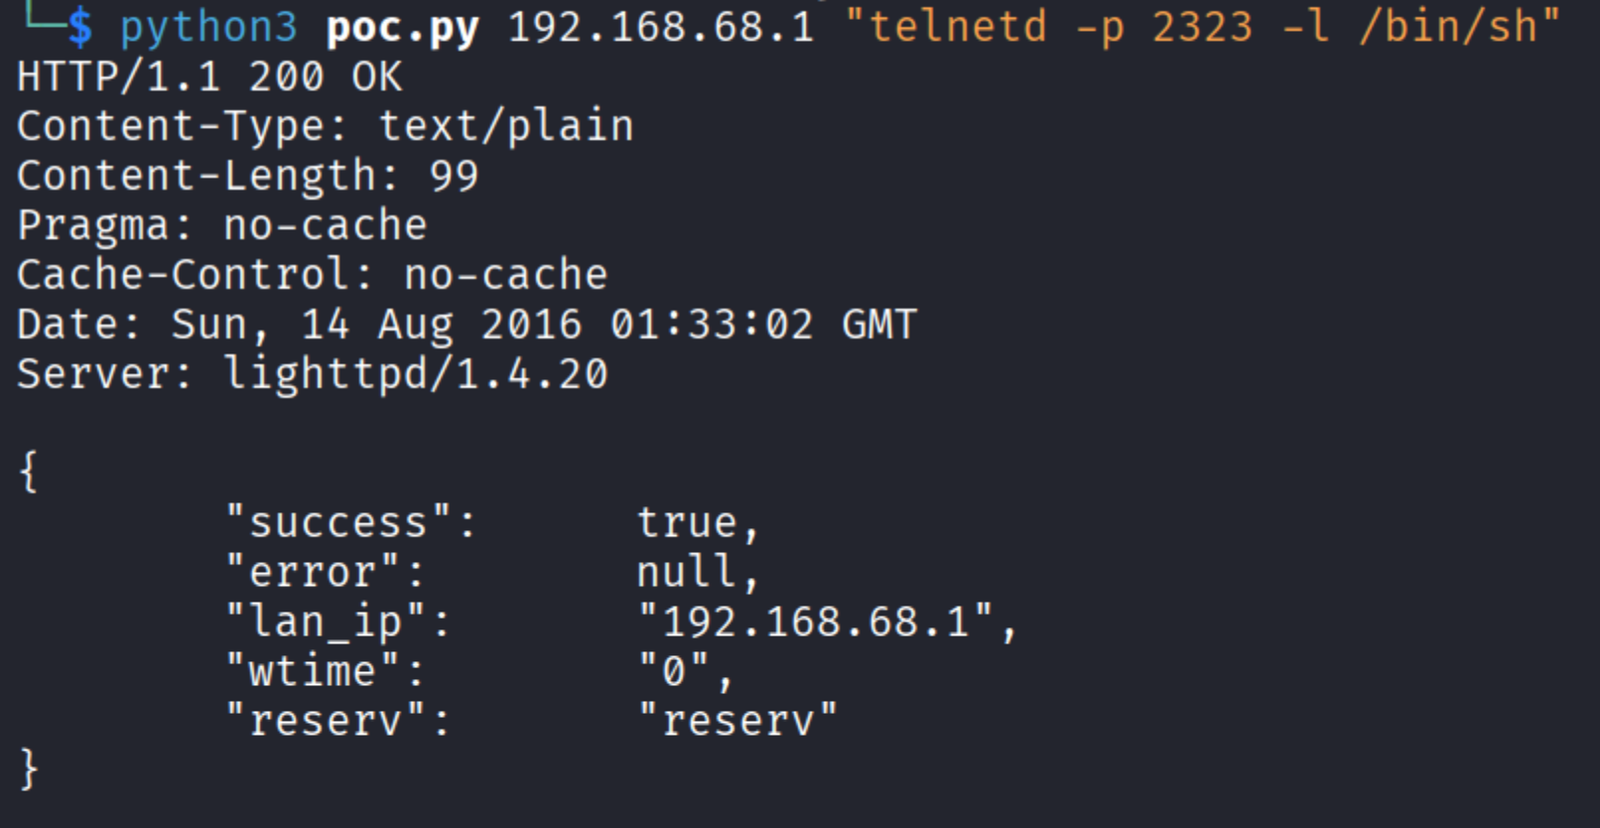 finnvle/cve-2022-28906-poc
Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…
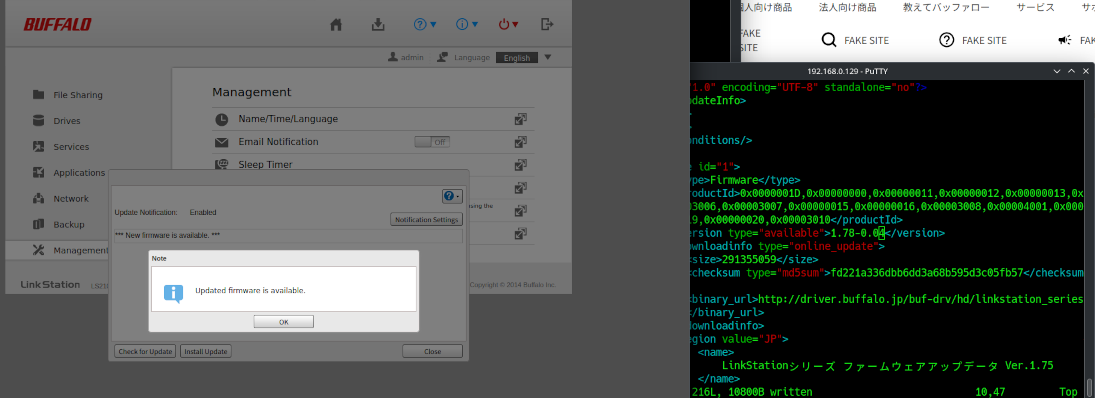 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 ali-py3/exploit-cve-2026-2670
Proof-of-concept exploit for CVE-2026-2670, a command injection vulnerability in Advantech WISE-6610 routers, allowing authenticated attackers to…
 szym0n13k/cve-2025-55972-remote-unauthenticated-denial-of-service-dos-in-tcl-smart-tv-upnp-dlna-avtransport
A TCL Smart TV running a vulnerable UPnP/DLNA MediaRenderer implementation is affected by a remote, unauthenticated Denial of Service (DoS).