
striatum-ctf
 jawh3/striatum-ctf
Research artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
ai-securityctfcurated-resources+5
2
jawh3/striatum-ctfResearch artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
 konstruktoid/prescryb
MCP server for CVE/config remediation orchestration: SSH inventory, OSV/NVD lookups, CIS/DISA STIG-mapped Ansible playbook suggestions.
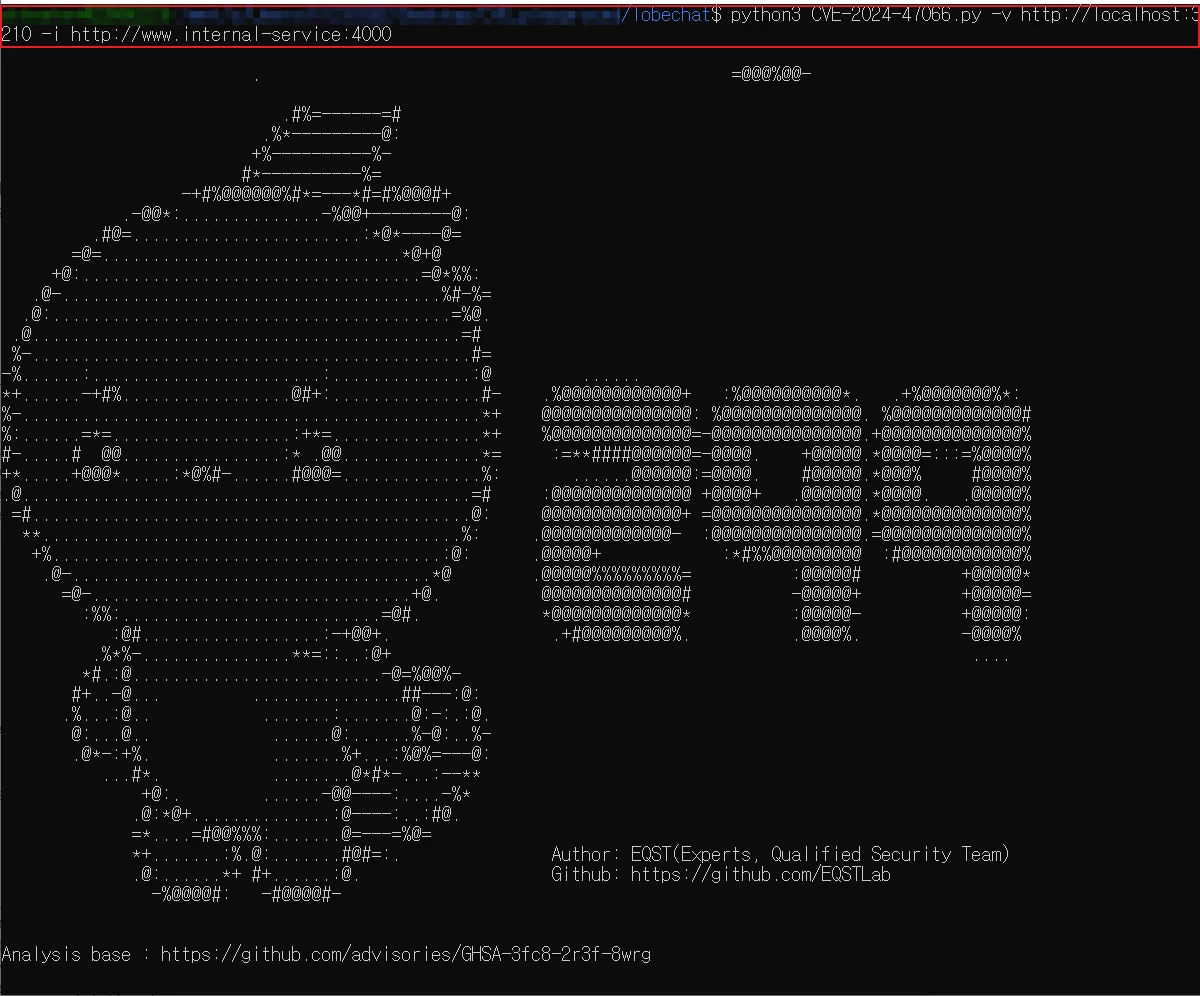 eqstlab/cve-2024-47066
Lobe Chat Server-Side Request Forgery exploit
 rvsh3ll/nxc-vulnscan
NetExec module: run every stock Windows vuln-check in one pass (check-only, no exploit)
 anasfik/flutterguard
Offline security audits for Flutter APKs on Android. Inspect permissions, SDKs, endpoints and potential secrets. No root, account, ads or analytics.
 xsscx/fuzz
Commodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
 cujanovic/crlf-injection-payloads
Collection of CRLF injection payloads gathered from bug bounty reports, used as a reference for testing HTTP header and response splitting…
 cujanovic/open-redirect-payloads
Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…
 minimaxir/big-list-of-naughty-strings
Curated list of malicious and edge-case input strings (blns.txt/blns.json) for QA and security testing of user-input validation, injection, and…
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 nishikawaakira/waf-dojo
Hands-on AWS WAF training game with tutorials, scored labs, and exams where players write Web ACL rules to block real attack shapes while avoiding…
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
 fare9/dragon-tales
Binary analysis library built on LLVM for disassembling, lifting, and symbolically executing machine code across x86, ARM, and RISC-V, with CFG…
 mas0nshi/cve-2026-112445
Proof-of-concept for CVE-2026-112445, a macOS local privilege escalation where an unprivileged console user abuses the launchd com.apple.xpc.uscwoap…
 jfrog/jfrog-openssl-tools
Python utilities to check whether a TLS server requires client certificates and to scan local ELF binaries for vulnerable OpenSSL 3.x code linked to…
 omar-tamerr/horuseye
AI-Powered Active Directory Attack Platform
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…