
libextractor-privesc
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
binary-exploitationeducationexploitation+3
haitam-lazaar/libextractor-privescProof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 pvharmo2/gha-lab-e8902eccd3
Security research lab: reproduction of CVE-2025-52467 (pgai pull_request_target workflow code execution / GITHUB_TOKEN exfiltration) — snapshot of…
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 mbanyamer/cve-2026-26988-librenms-sqli
Proof-of-concept exploit for unauthenticated SQL injection in LibreNMS ajax_table.php, demonstrating time-based and boolean-based blind injection…
 nexxus67/cve-2026-25676
Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 george0papasotiriou/cve-2026-5050-blind-ldap-injection-via-unescaped-filter
Reproduces CVE-2026-5050 with a simulated Flask LDAP server and exploit script, demonstrating blind LDAP injection via unescaped filters to bypass…
 anthropics/cryptography-research-demo
Reproducible cryptanalysis artifacts for single-key recovery attacks on reduced-round AES, including black-box key recovery, DDT-Gray search, S-box…
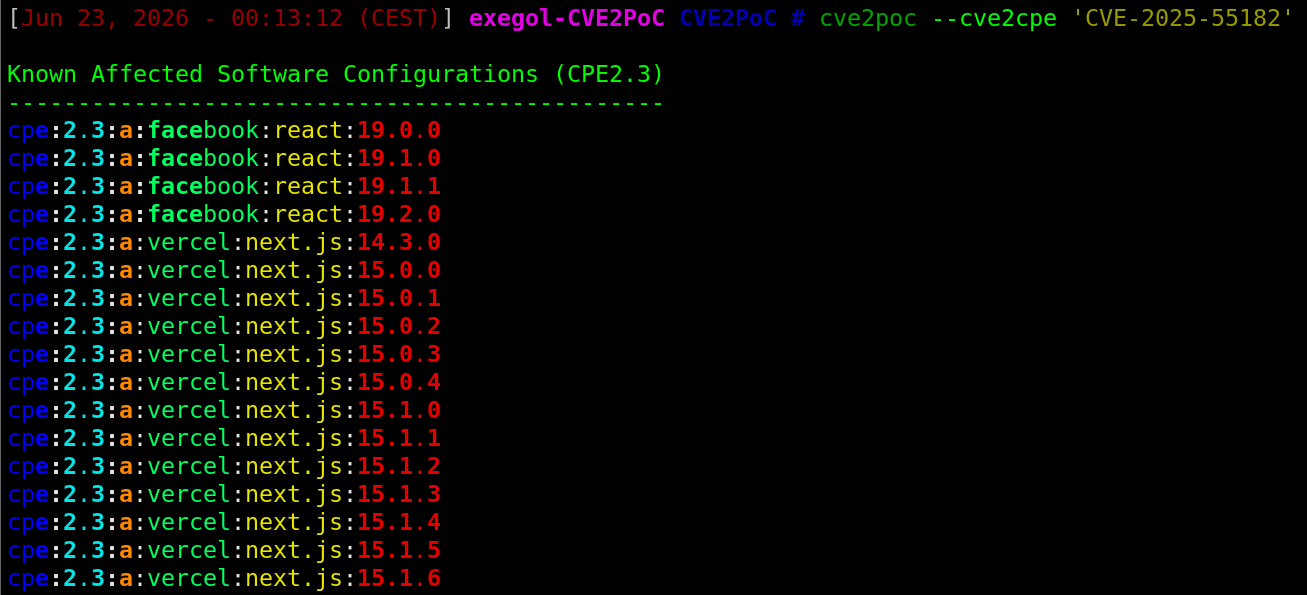 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 projectdiscovery/awesome-search-queries
Community curated list of search queries for various products across multiple search engines.
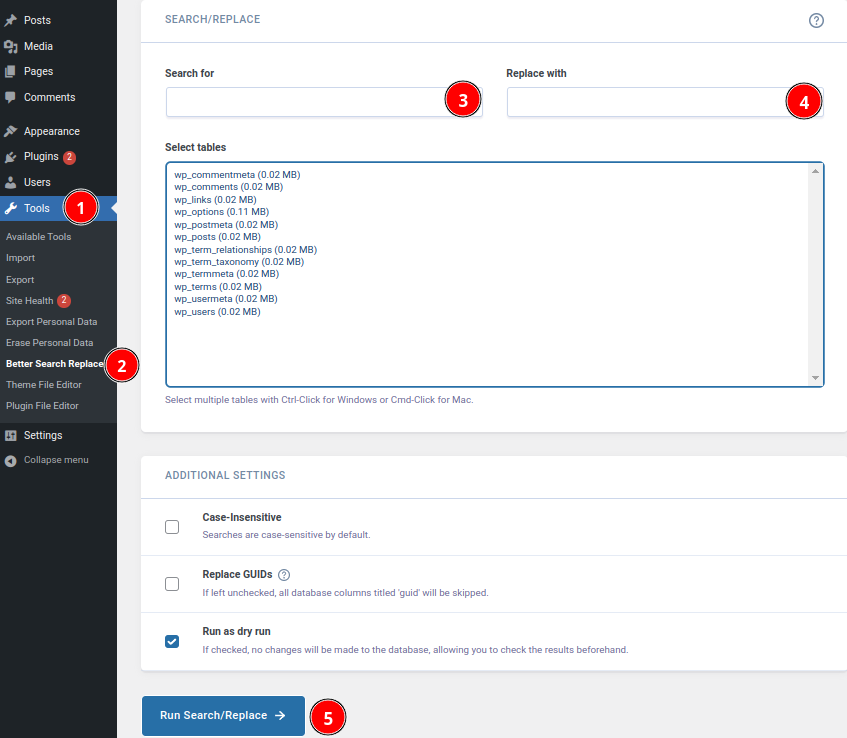 w2xim3/cve-2023-6933
Introduction to CVE-2023-6933 Vulnerability
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 sourcegraph/log4j-cve-code-search-resources
Using code search to help fix/mitigate log4j CVE-2021-44228
 t0kx/exploit-cve-2015-1427
Elasticsearch 1.4.0 < 1.4.2 Remote Code Execution exploit and vulnerable container
 ocmenog/cve-2025-55998
Documented reflected XSS vulnerability (CVE-2025-55998) in Mezereon's Smart Search and Filter app for Shopify and BigCommerce, with proof-of-concept…
 nxploited/cve-2025-39538
WordPress WP-Advanced-Search <= 3.3.9.3 - Arbitrary File Upload Vulnerability
 yup-ivan/cve-2024-9796
POC (SQLi) -> CVE-2024-9796