CVE-2026-66066
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
exploitationpenetration-testingreconnaissance+3
1
shinthink/cve-2026-66066CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 rapid7/recog
Pattern recognition for hosts, services, and content
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
 mpgn/cve-2019-5418
CVE-2019-5418 - File Content Disclosure on Ruby on Rails
 z3n70/cve-2021-41277
simple program for exploit metabase
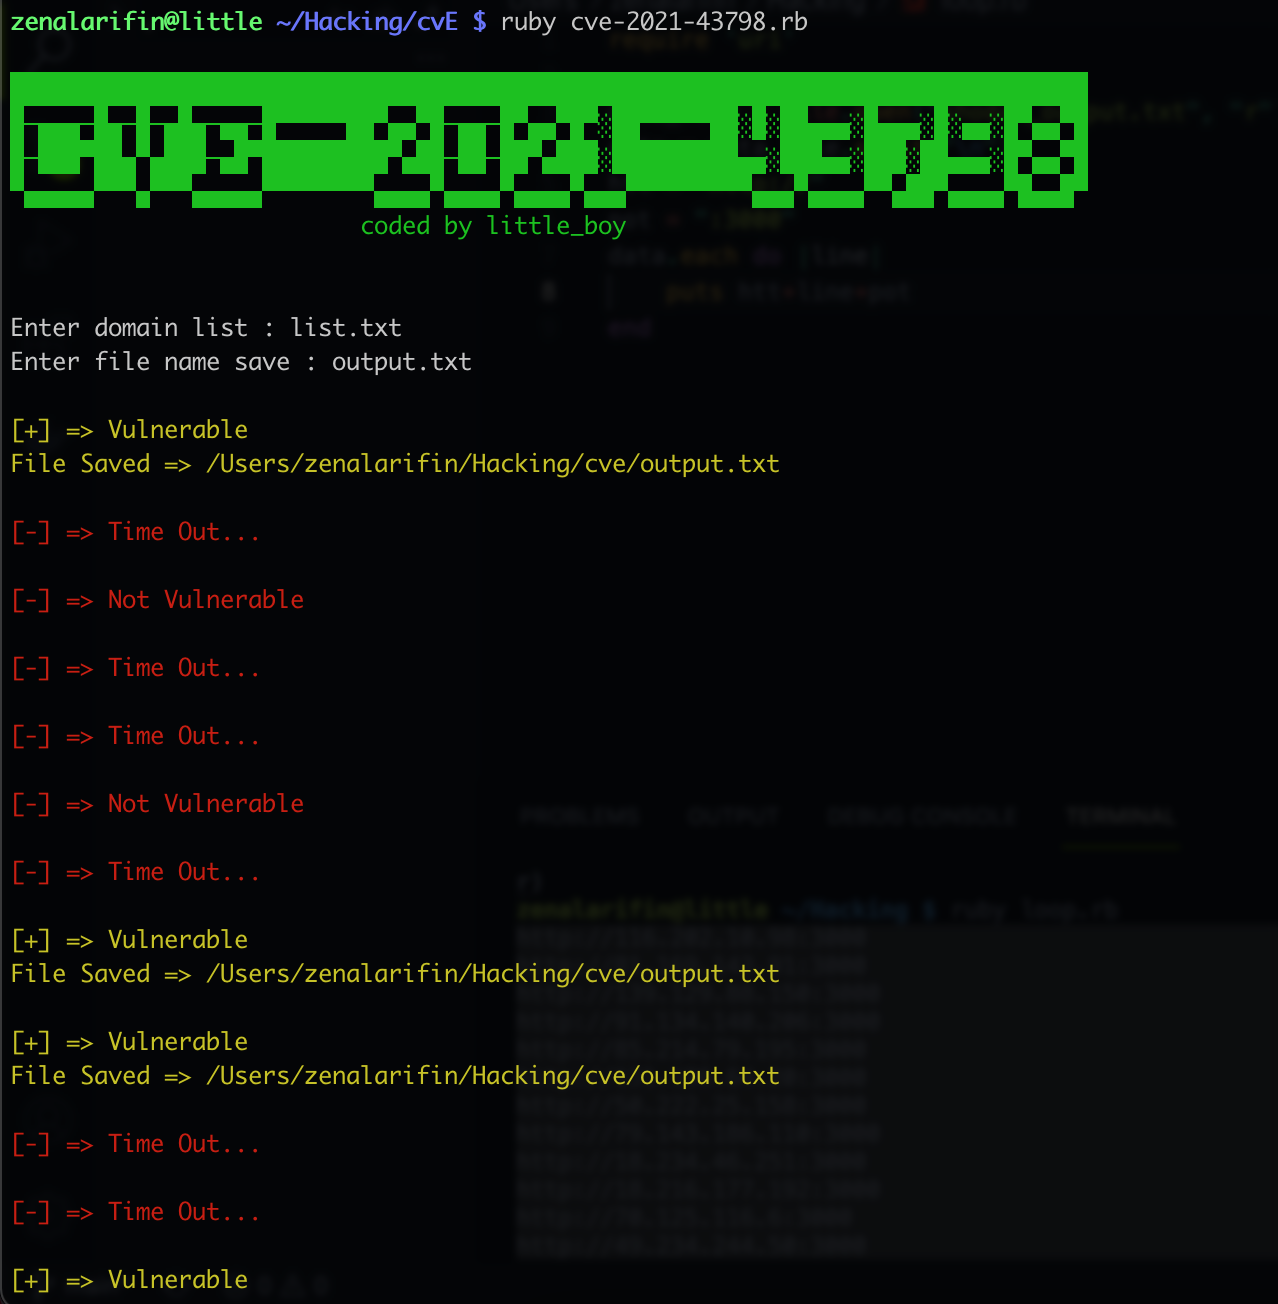 z3n70/cve-2021-43798
Simple program for exploit grafana
 omaratallahh/cve-2023-23138
short view of ruby on rails properties misconfiguration
 svaltheim/cve-2023-23752
Python exploit for Joomla! v4.2.8 unauthenticated information disclosure vulnerability (CVE-2023-23752). Extracts sensitive configuration data from…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 mlr0p/cve-2021-33564
Argument Injection in Dragonfly Ruby Gem
 omarkurt/cve-2014-0130
cve-2014-0130 rails directory traversal vuln
 dorkerdevil/cve-2021-33564
Argument Injection in Dragonfly Ruby Gem exploit (backup)
 advaitpathak21/cve-2024-46987
Exploit created using Python
 m0nad/hellraiser
Vulnerability scanner using Nmap for scanning and correlating found CPEs with CVEs.
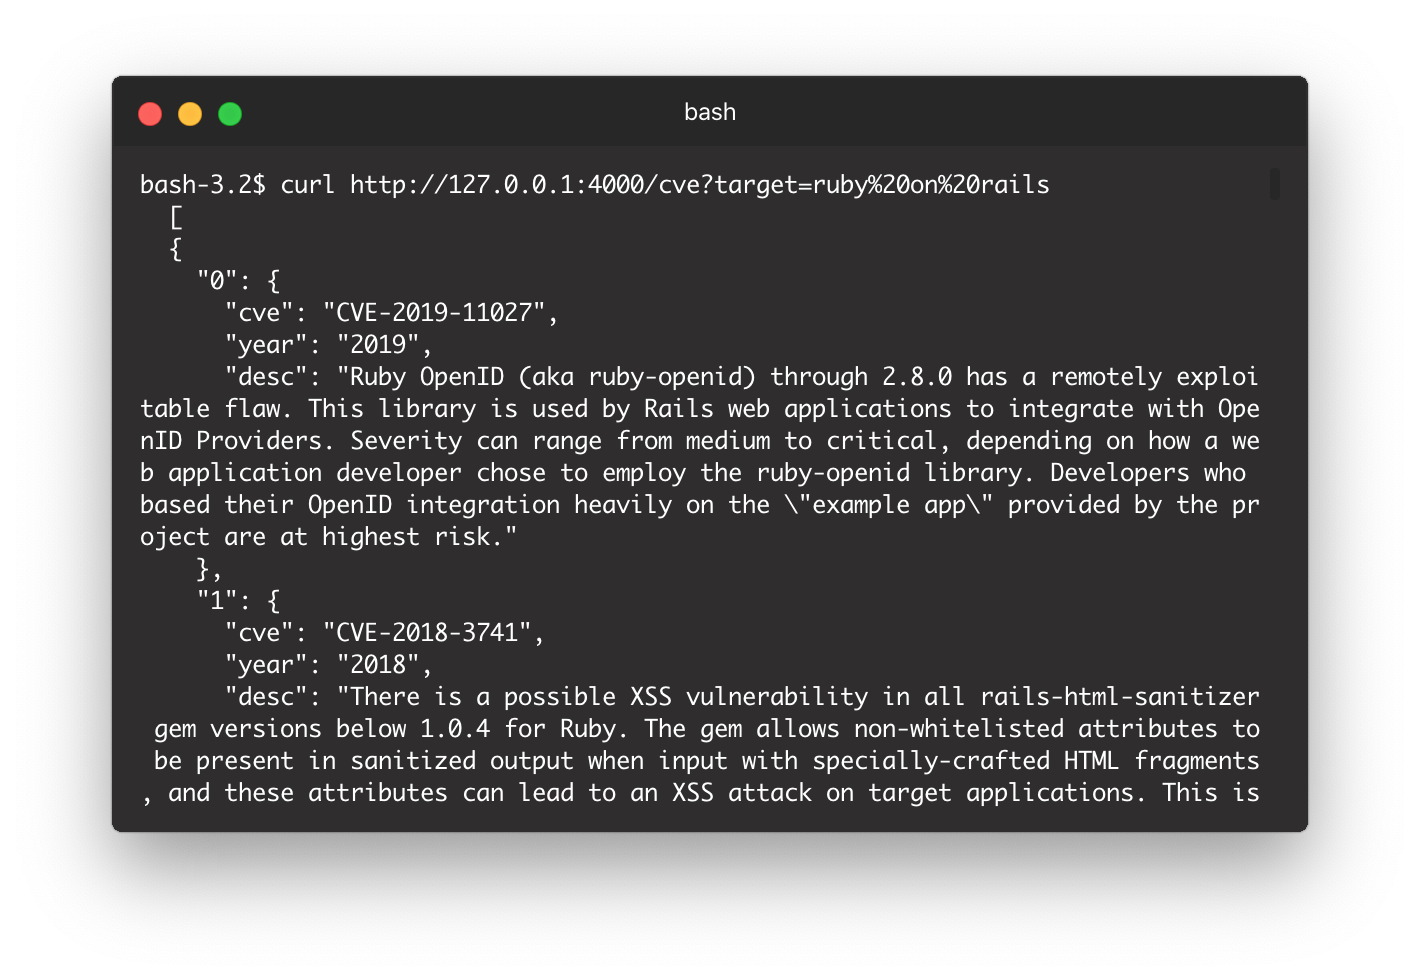 beyarz/cve-api
Unofficial api for cve.mitre.org