
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Cve-api — Unofficial api for cve.mitre.org | Kitploit
Tools/GitHubGitHub/beyarz/cve-api
Vulnerability AnalysisInformation GatheringThreat IntelligenceAPI Security
GitHubbeyarz/cve-api

Cve-api

Unofficial api for cve.mitre.org

View Repository
405396 years agoReviewed by Kitploit
Share

name

Parse & filter the latest CVEs from https://cve.mitre.org

Docs

Usage

http://localhost:4000/cve?target=KEYWORD

The year parameter is optional.
http://localhost:4000/cve?target=KEYWORD&year=YEAR

Examples

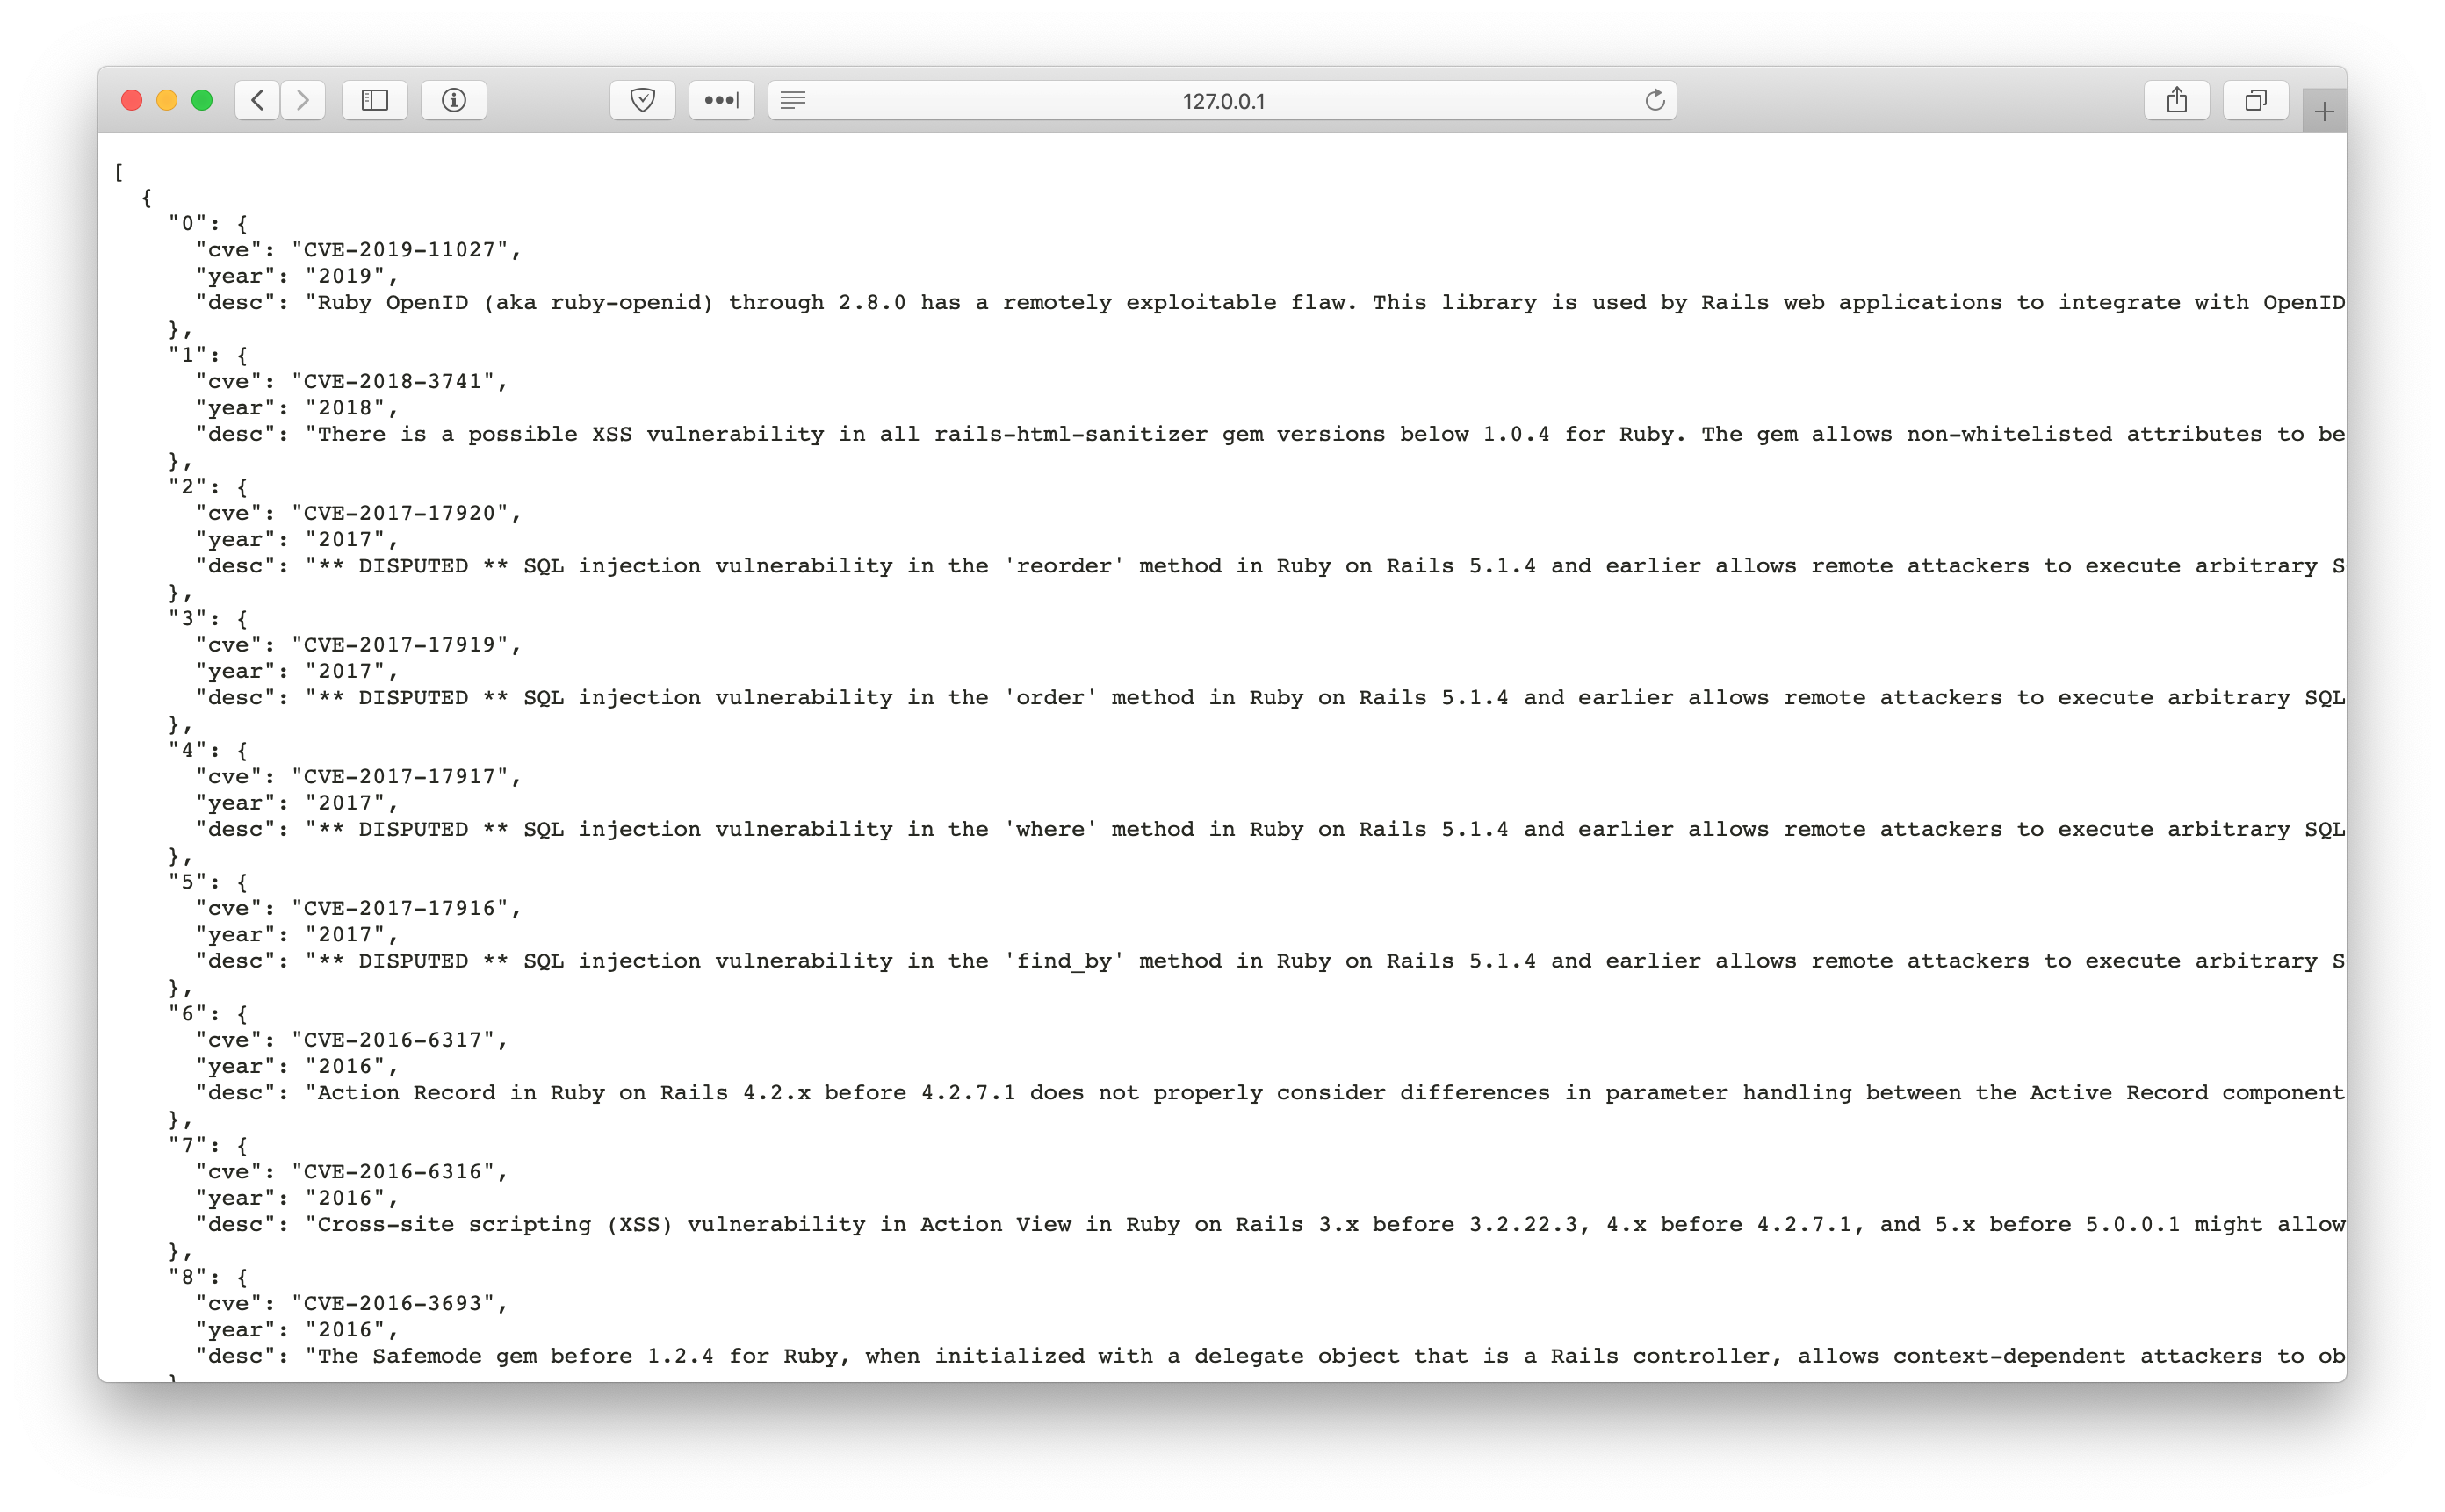
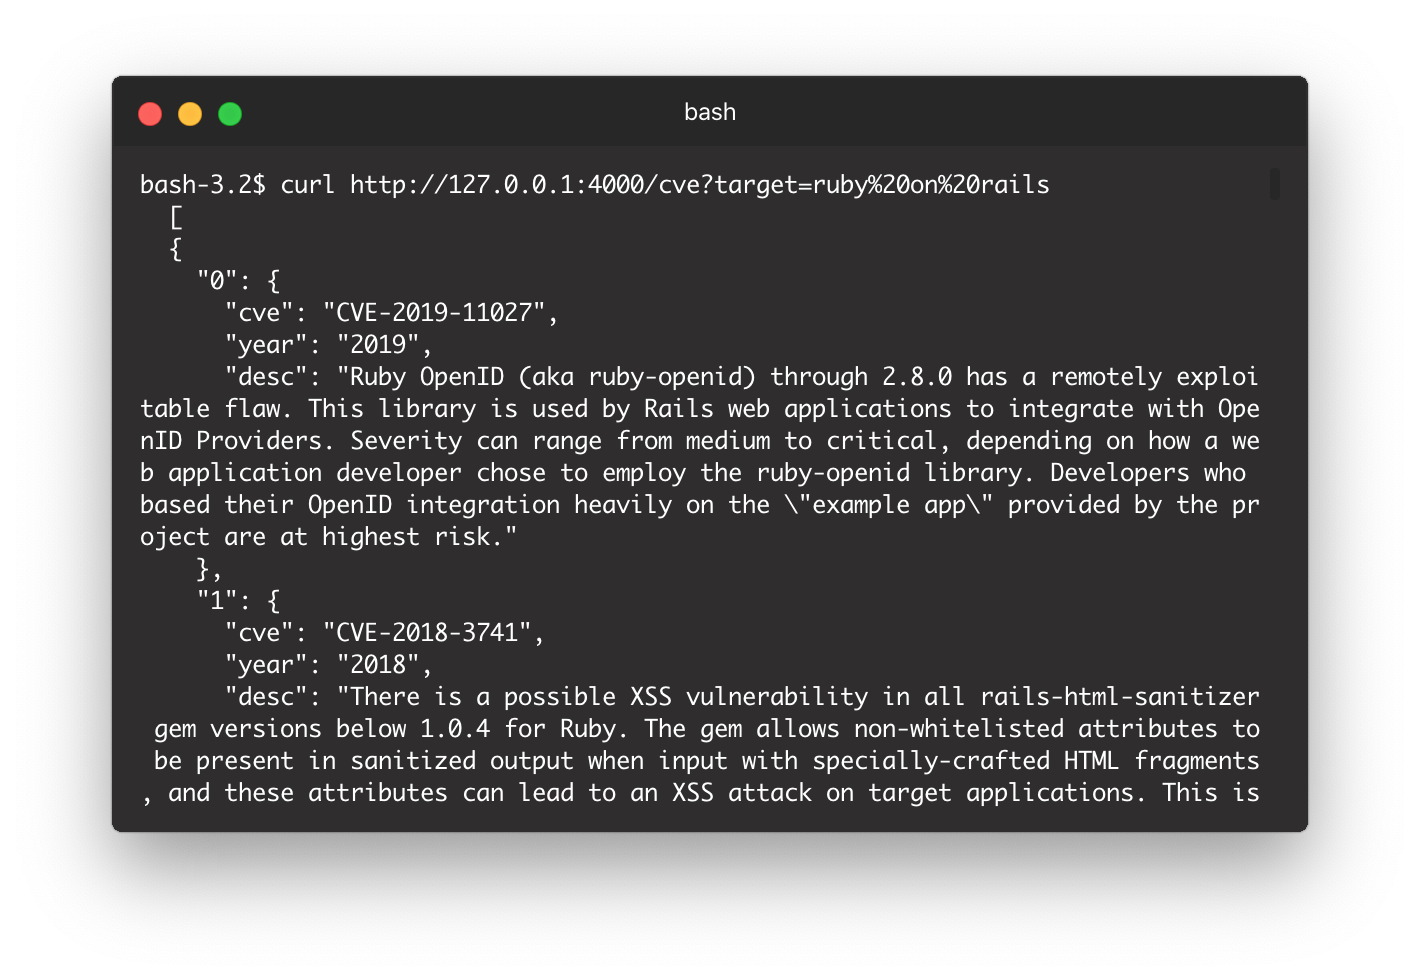
http://localhost:4000/cve?target=ruby%20on%20rails
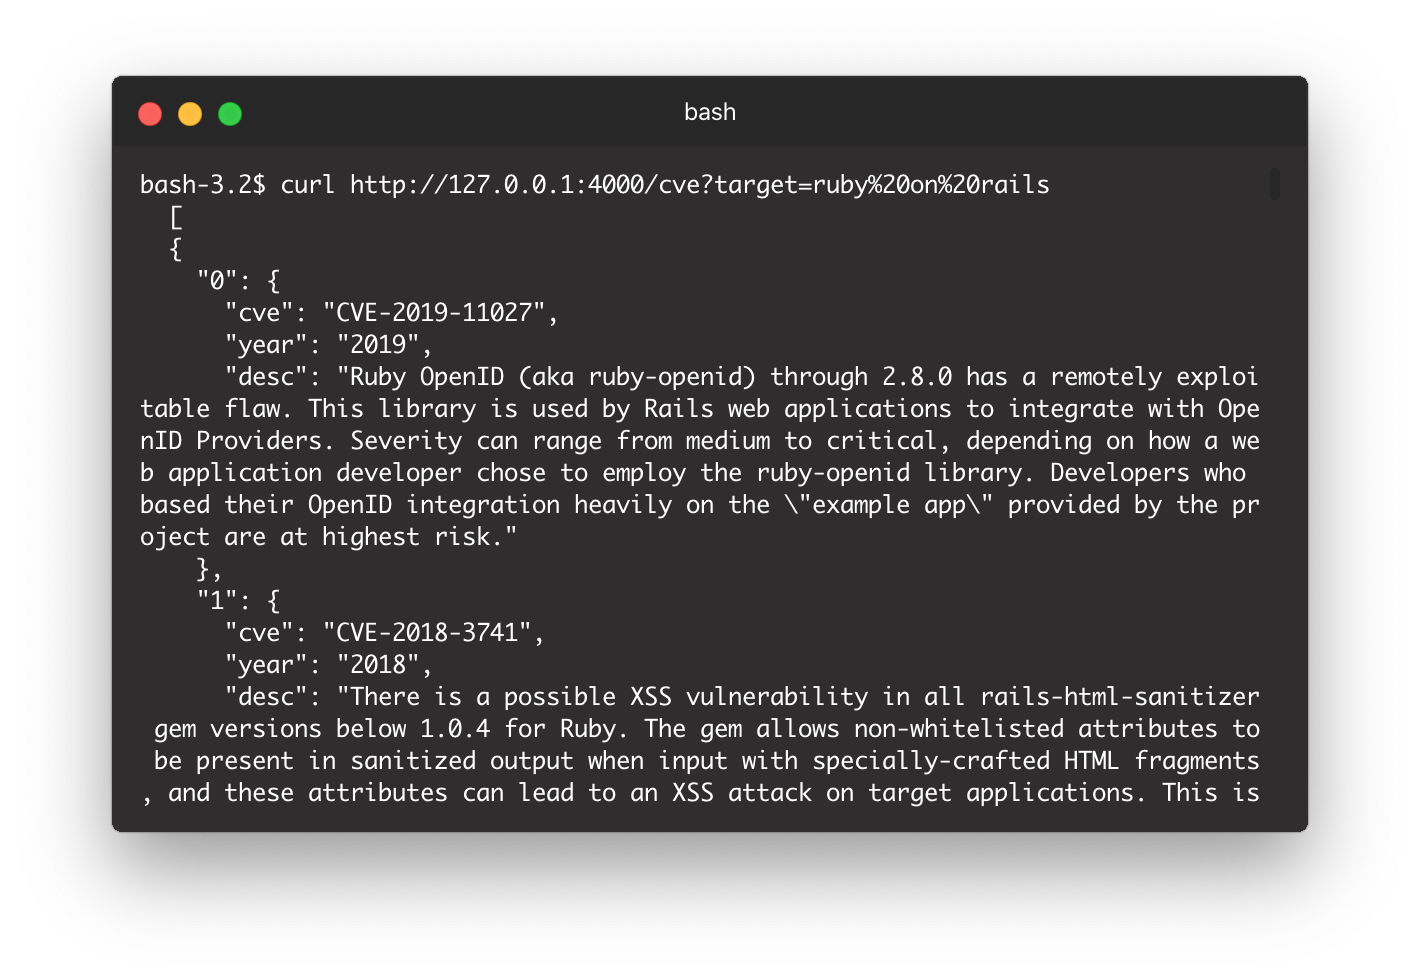
terminal browser

http://localhost:4000/cve?target=ruby%20on%20rails&year=2020

If you want to parse the latest year, use the "latest" keyword.
http://localhost:4000/cve?target=ruby%20on%20rails&year=latest

Getting started

  • Download the project
  • bundle install
  • ruby rest.rb

Requirements

  • Ruby
  • Docker (Optional, only required if you want to run through a container.)

Environment

You can switch between prod & dev at config/environment.rb
You need to create one yourself, an example can be found here.

Healthcheck

The url will return a status code of 200 which means the api is healthy.
If 200 is not shown then you should assume there is something wrong.
http://localhost:4000/status

Manage image

Access

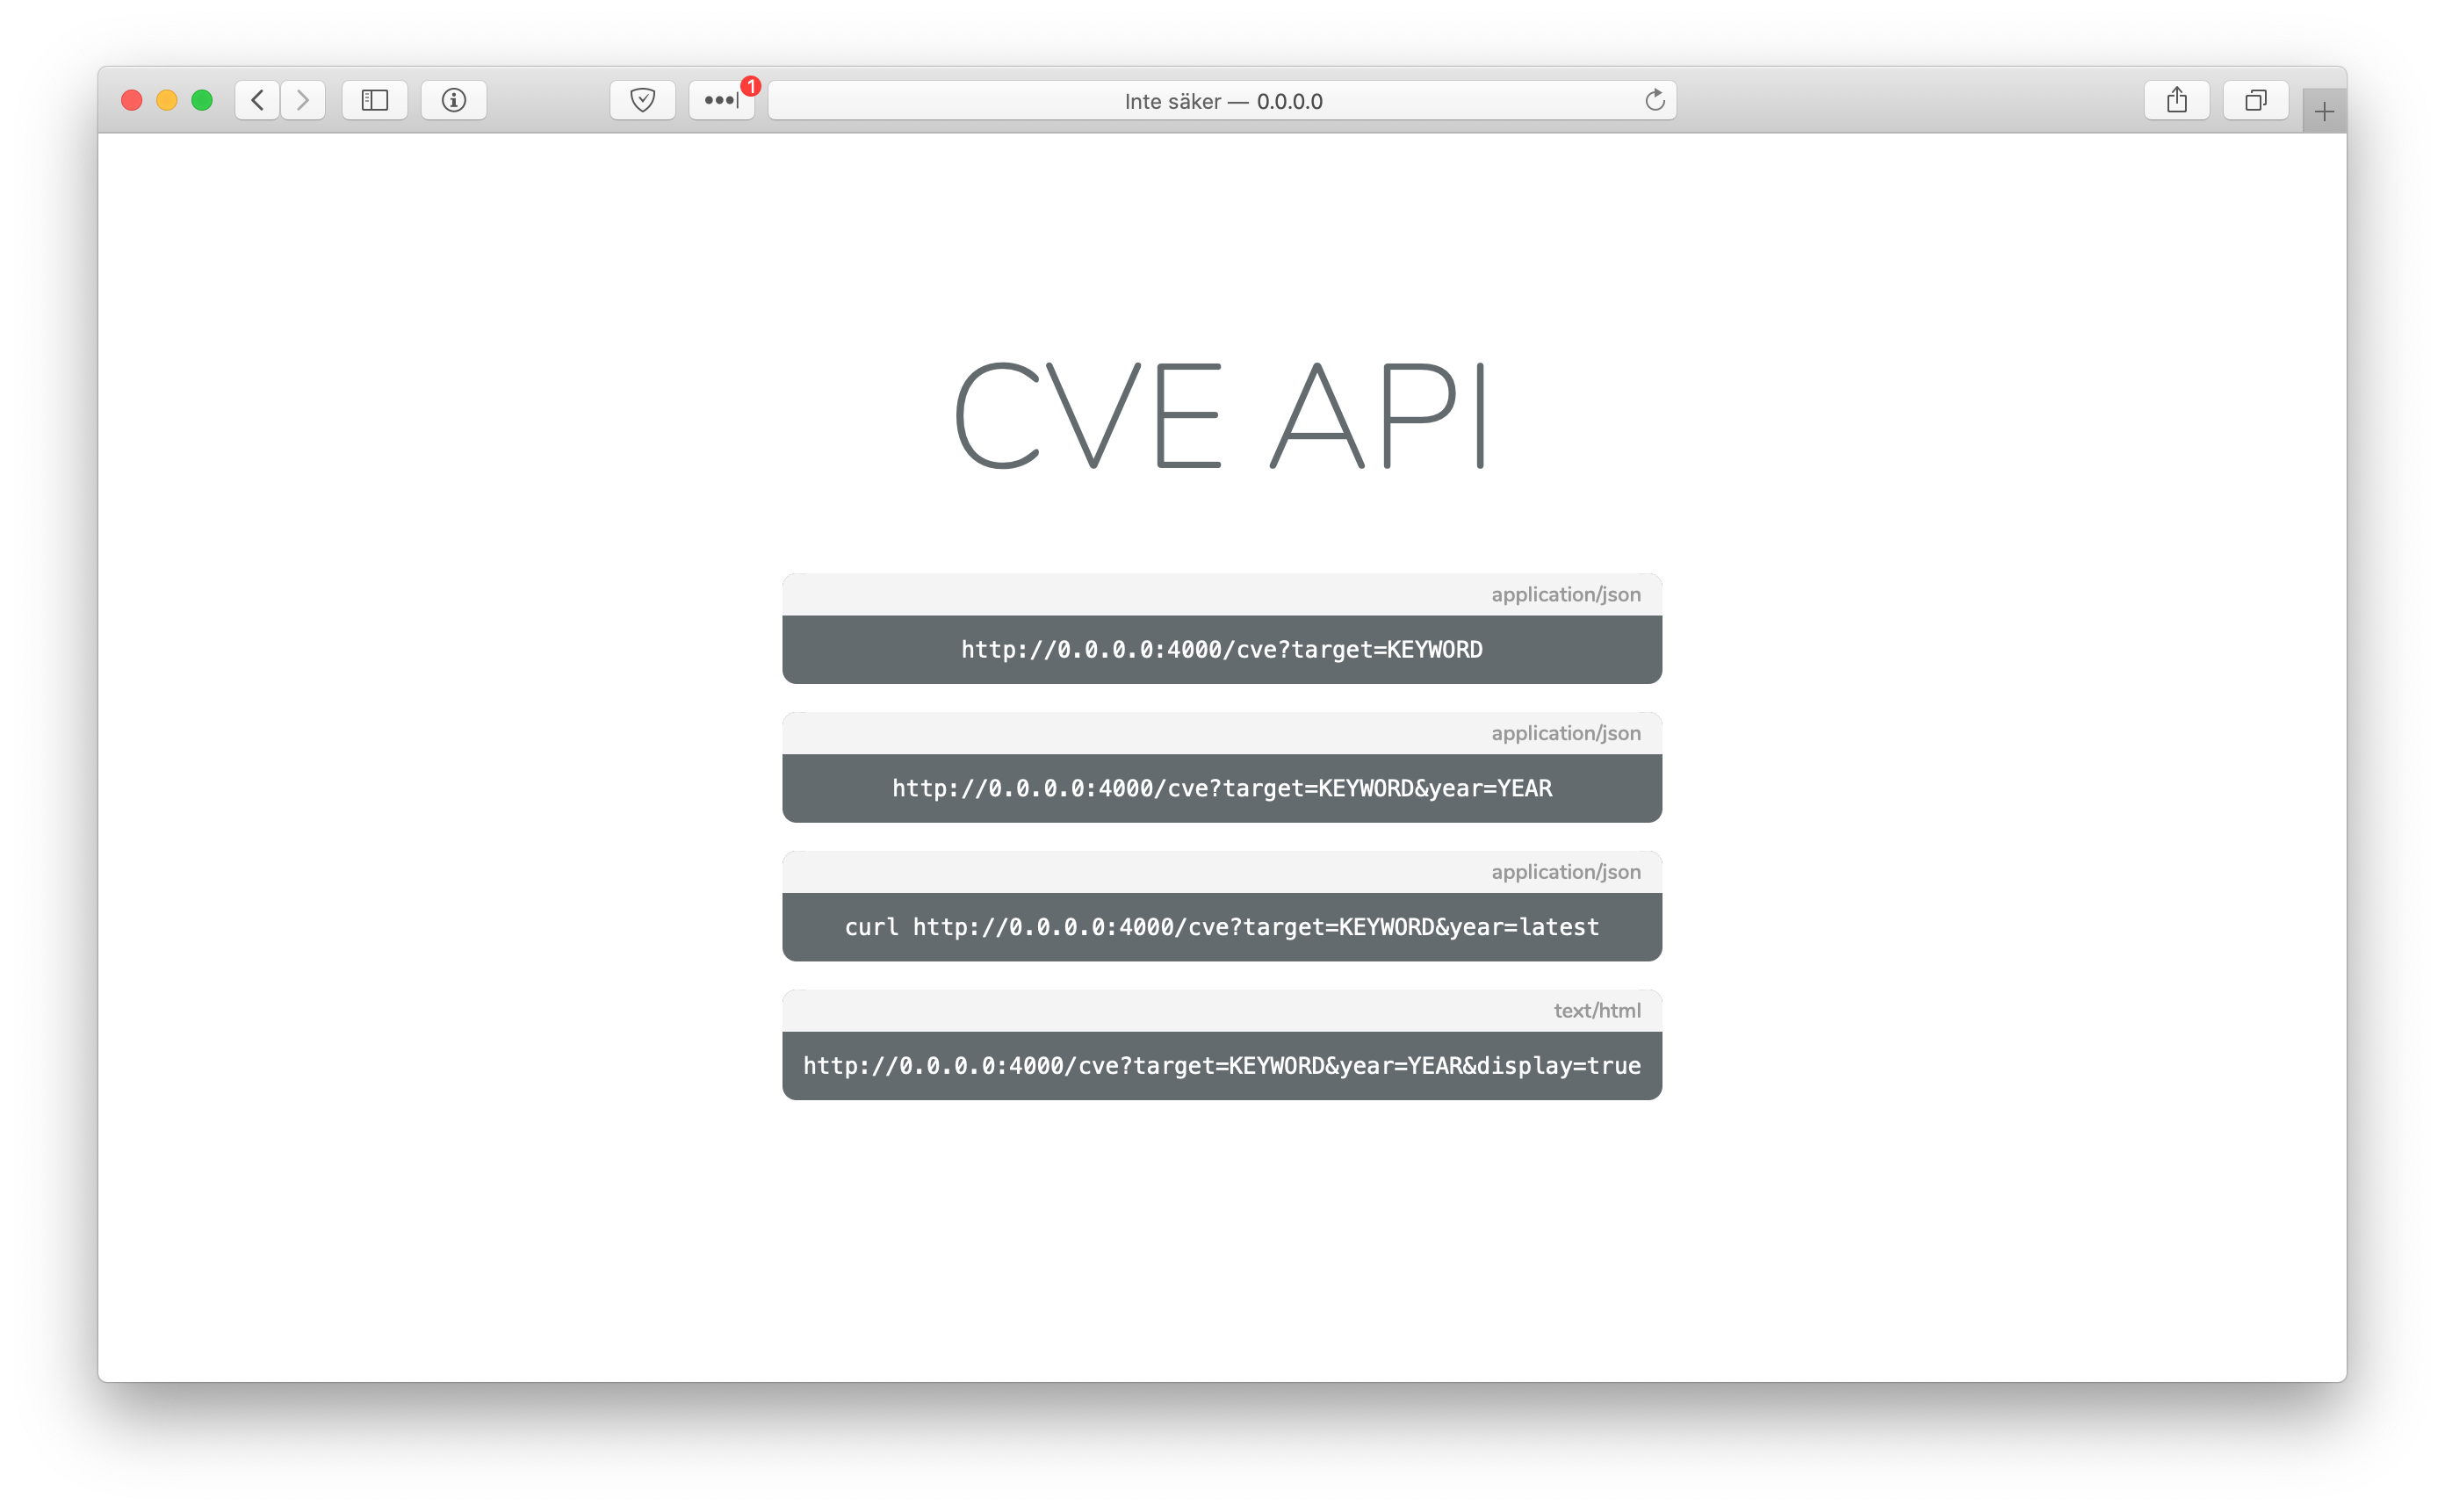
You can access the api via http://localhost:4000/
You should be able to view the index page from the url. index
Build image

docker build . -t cve-api

Run image

docker run -p 4000:4000 -d cve-api

Get id

docker ps

Stop image

docker stop ID

Remove image

docker rmi cve-api

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    498
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    465
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    340
  • 4

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    332
  • 5

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    307
  • 6

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    294

Explore all tools

Browse our collection of tools

View all tools →