
vulnerpocalypse-containment
 clearhandreview/vulnerpocalypse-containment
Open-source vulnerability analysis, CVE tracking, patch verification, and temporary security containment tools
configuration-auditingcurated-resourcesdefensive-tools+5
1
clearhandreview/vulnerpocalypse-containmentOpen-source vulnerability analysis, CVE tracking, patch verification, and temporary security containment tools
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
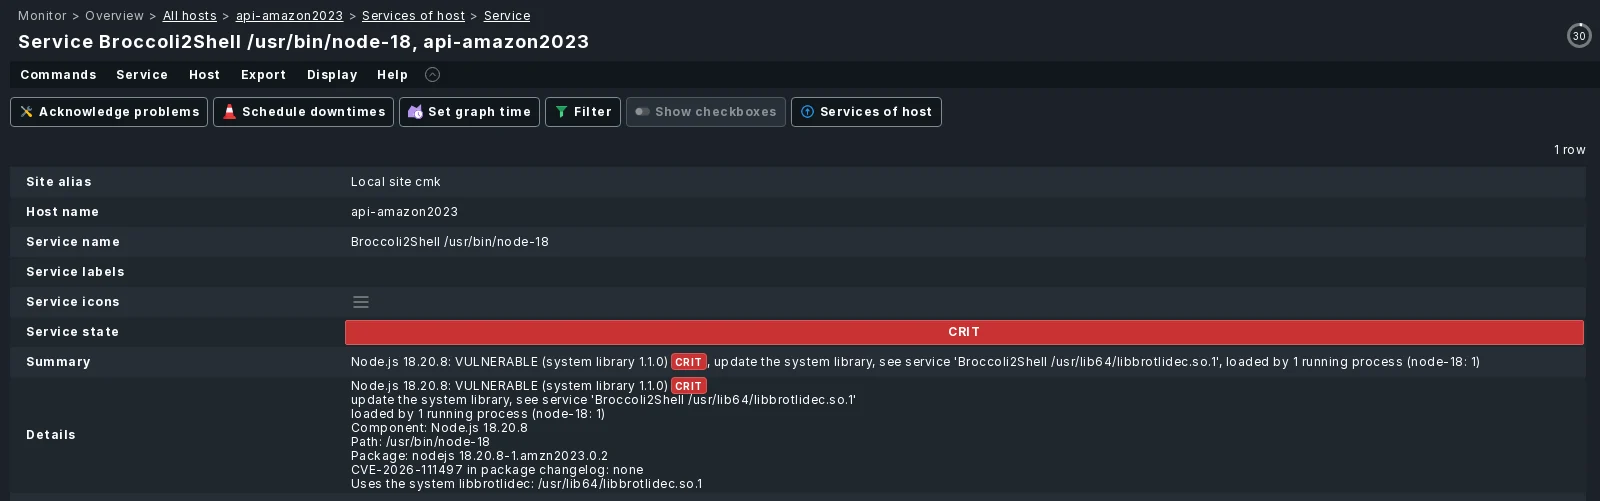
 checkmk1/checkmk_broccoli2shell
Checkmk extension that audits Linux hosts for Brotli decoders (libbrotlidec, Node.js, Python, .NET) affected by CVE-2026-111497, checking versions,…
 canonical/ubuntu-security-notices
Ubuntu vulnerability dataset publishing USN/LSN security notices in OSV and OpenVEX JSON formats for automated vulnerability and VEX-aware dependency…
 checkmk1/checkmk_php2shell
Checkmk extension with an agent plug-in that inventories PHP binaries and Apache mod_php on Linux hosts and reports PHP2Shell…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 0xblackash/cve-2026-111497
Advisory and proof-of-concept toolkit for CVE-2026-111497 (Node2Shell), a Brotli heap overflow in Node.js, with trigger scripts, version checker, and…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 cookiengineer/actual-php2shell
:robot: NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 openai/php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
 4rdr/proofs
Collection of CVE findings, proof-of-concept references, and vulnerability research notes, including ExploitDB entries and credited security…