

sast
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
cloud-securitycode-analysisdefensive-tools+9
23 months ago
vulnz/sastFree offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 vighnesh91/cloudgarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…
 irsdl/webhacklist
Archive of the Top 10 Web Hacking Techniques - every nominee since 2006, preserved
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.
 kolmteistov/gobalance-patch
Security patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 phil-fan/fs-attack
Implementation of the paper "Rethinking Latency Denial-of-Service: Attack the LLM Serving Framework, Not the Model"
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 animeshshaw/pqc-cost-of-delay
Cost-of-delay prioritisation for post-quantum migration: classical and harvest-now-decrypt-later risk in one unit (USD per year). Code, proofs, case…
 neurosaki987/qvm-tool
Static analysis and structure recovery toolkit for ACE .qvm0-protected PE images
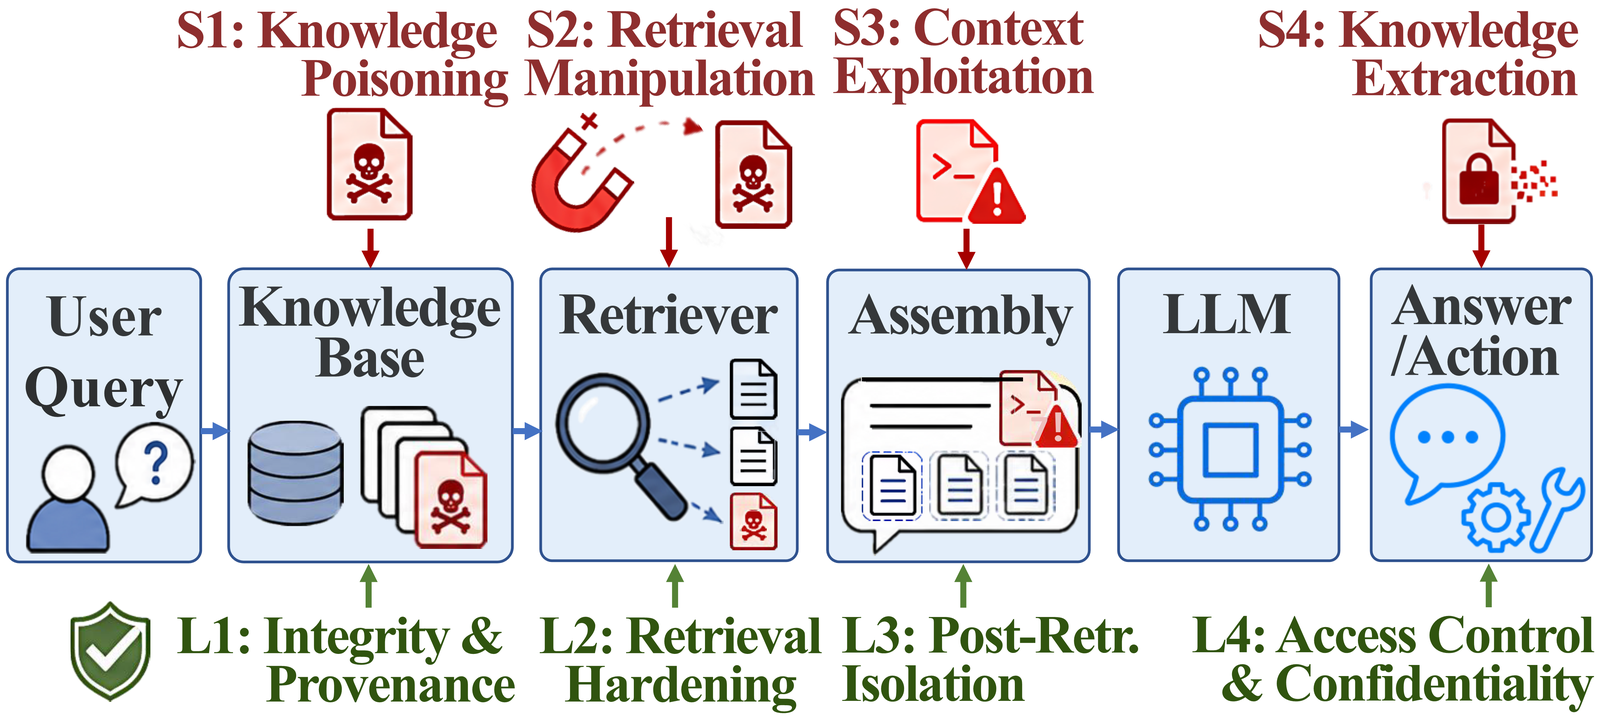 treeai-lab/awesome-rag-security
Curated collection of research papers on retrieval-augmented generation security, organized by the SLOT taxonomy covering knowledge poisoning,…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
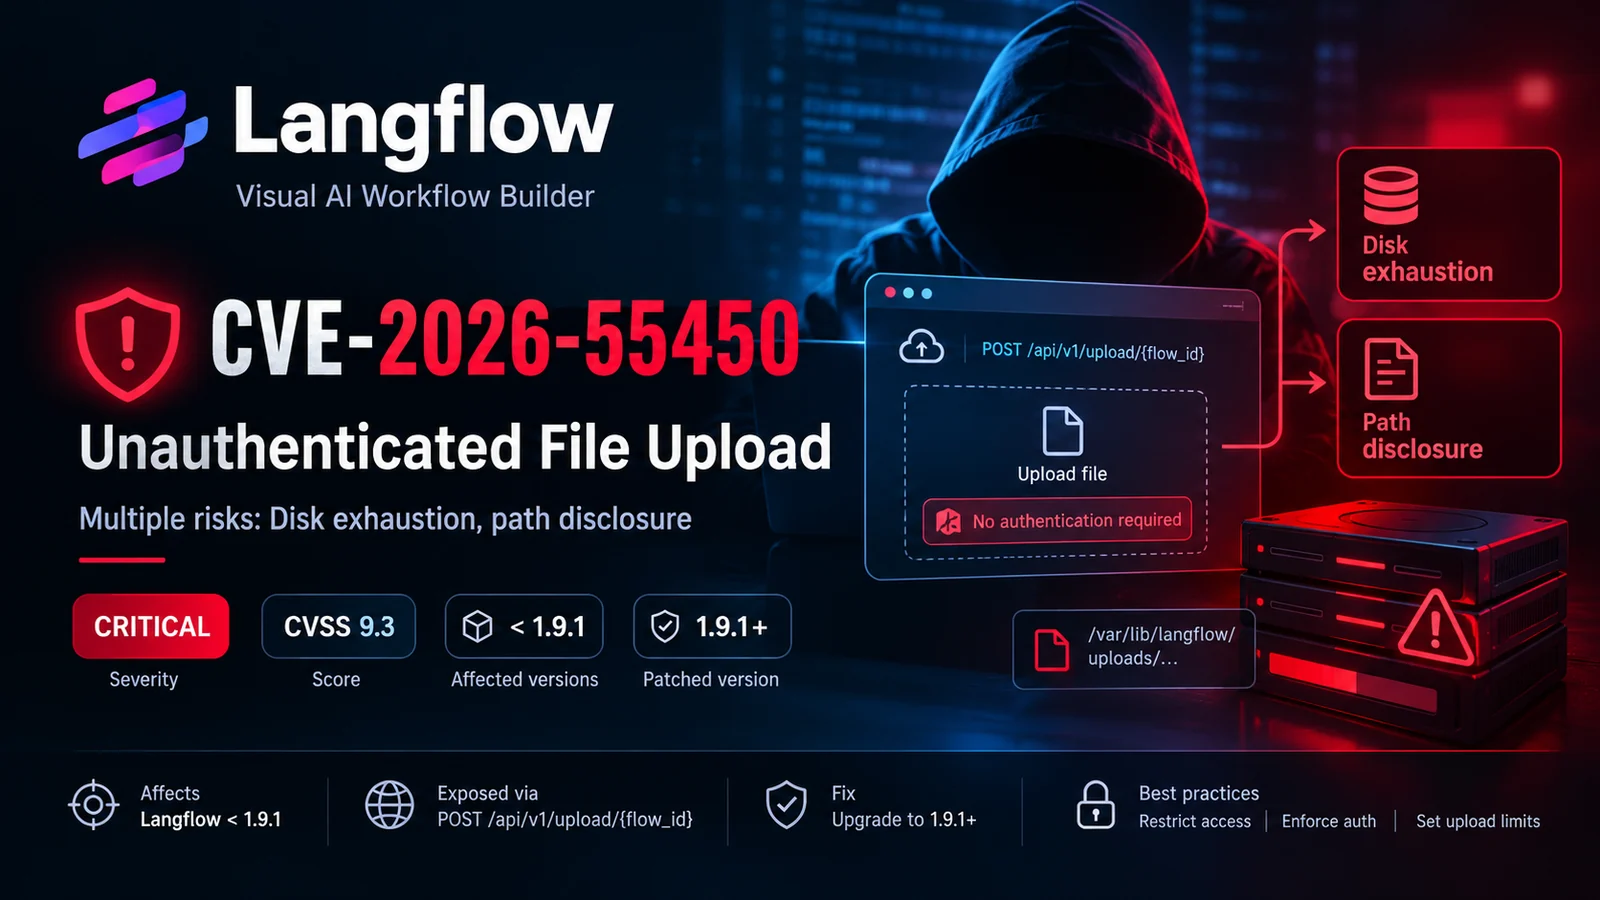 0xblackash/cve-2026-55450
Advisory documenting CVE-2026-55450, an unauthenticated file upload flaw in Langflow, with impact analysis, detection references, and remediation…