
cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Engagement Manager is a web application for tracking offensive security engagements. It features a modern UI, built with Next.js, Prisma, and…

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

Fil-C: completely compatible memory safety for C and C++

An open source threat modeling tool from OWASP

A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

Proof-of-concept demonstrating a combined CORS misconfiguration and CSRF protection bypass in Halo CMS, enabling cross-site request forgery attacks…

PatrowlHears - Vulnerability Intelligence Center / Exploits

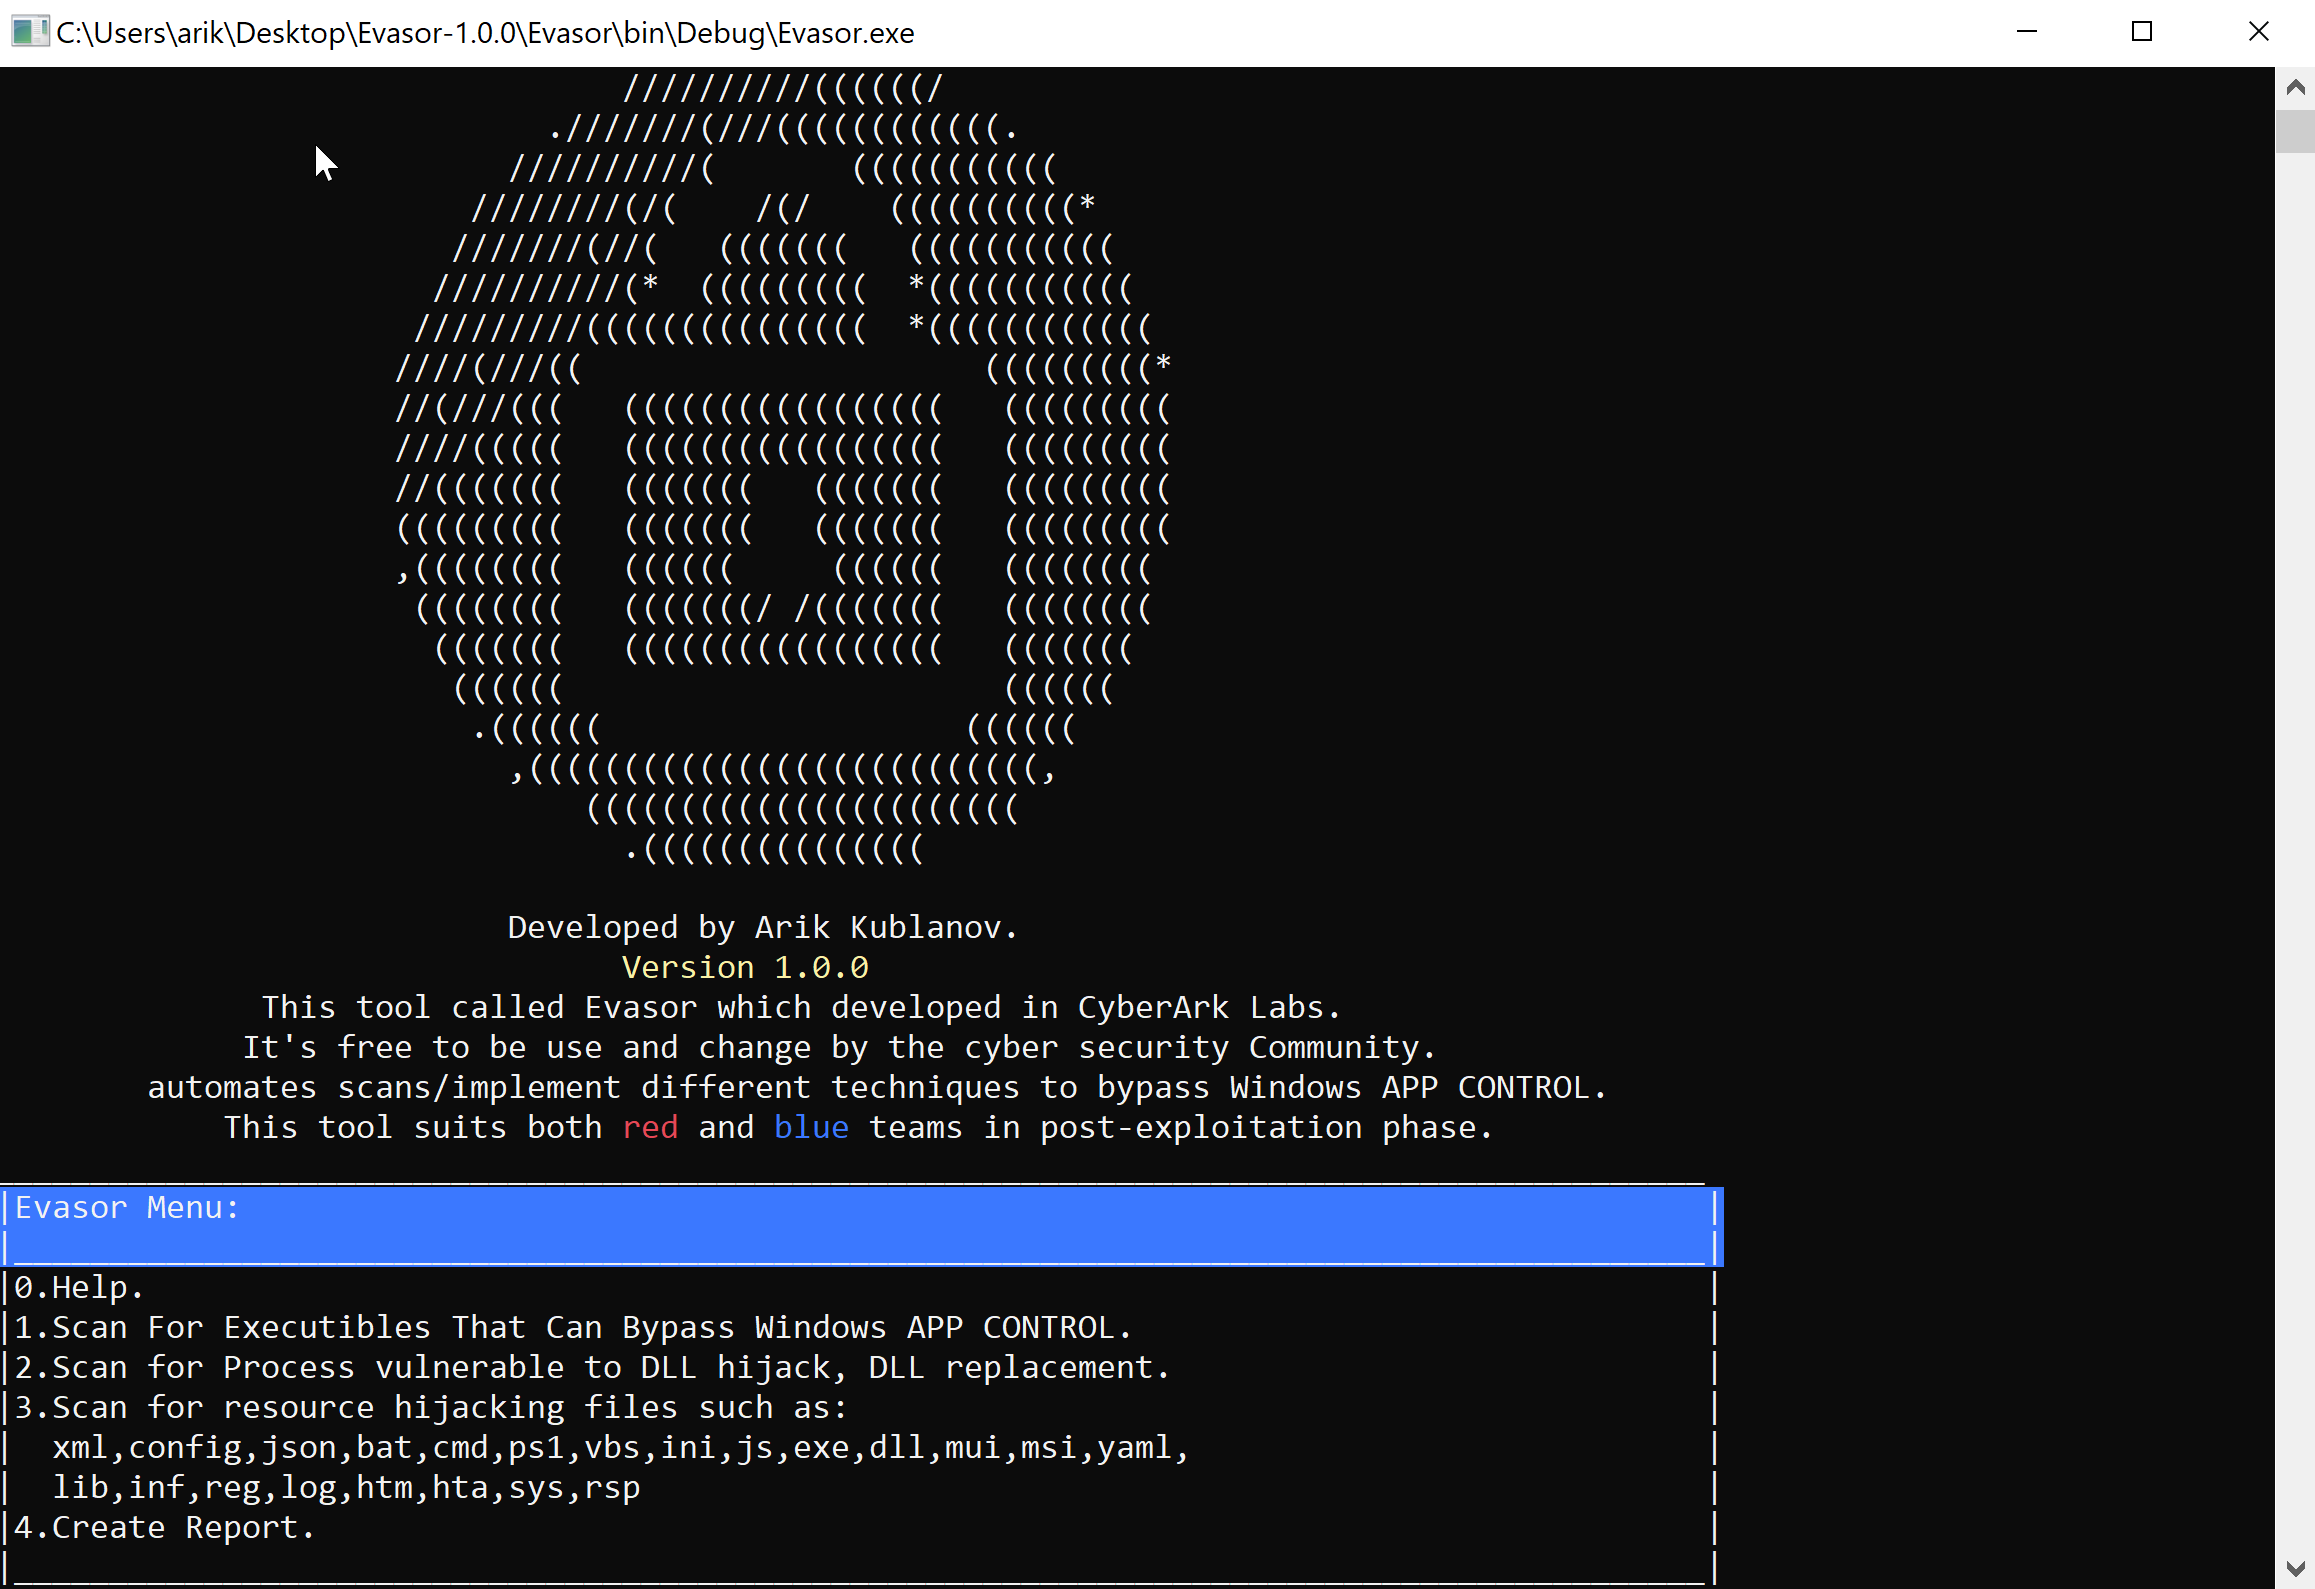
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS

This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.

PoC for CVE-2026-73847 - emlog AI Assistant CSRF to SQL execution to admin takeover (CVSS 6.8)

Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…

Windows Apache Tomcat resource limits implementation guide for CVE-2022-41404 DoS vulnerability protection

Proof-of-concept for CVE-2021-45007, a CSRF vulnerability in Plesk Obsidian 18.0.37, demonstrating request submission without CSRF token protection.

PowerShell script to mitigate CVE-2022-41040 on affected Exchange servers by applying recommended configuration changes.

Proof-of-concept exploit demonstrating a missing CSRF protection vulnerability in PHPgurukul Online Course Registration System, for security testing…