
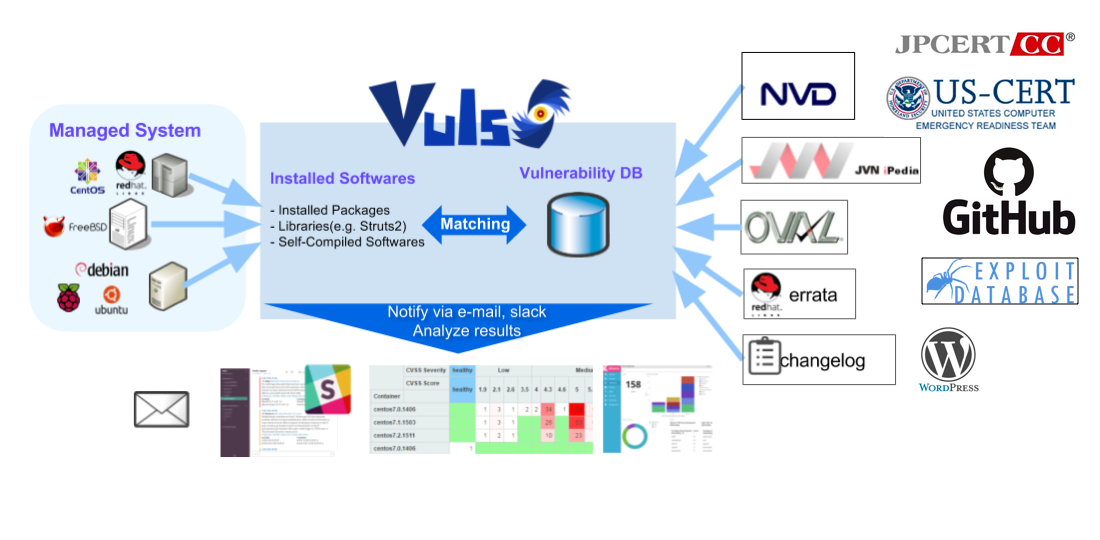
vuls
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
cloud-securityconfiguration-auditingcontainer-security+5
12.3k
future-architect/vulsAgent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 dinosn/cve-2024-21182
Reproducible Docker lab for CVE-2024-21182 Oracle WebLogic T3/IIOP OpaqueReference JNDI injection leading to unauthenticated RCE. One-command…
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…
 hienkiet/cve-2022-21445-for-12.2.1.3.0-weblogic
Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
 freeide/weblogic_cve-2019-2890
Exploit for CVE-2019-2890 targeting Oracle WebLogic Server via XXE injection and deserialization, enabling remote code execution through crafted…
 jas502n/cve-2018-2894
Exploit for CVE-2018-2894 targeting Oracle WebLogic Server remote code execution vulnerability, enabling unauthenticated attackers to execute…
 lonehand/oracle-weblogic-cve-2017-10271-master
Exploit for Oracle WebLogic CVE-2017-10271 (wls-wsat RCE bypass) with PoC scripts for remote command execution and obtaining a cmd shell on…
 kursadalsan/cve-2024-21182
Proof-of-concept exploit for CVE-2024-21182, an Oracle WebLogic Server JNDI injection vulnerability enabling unauthenticated remote code execution.
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 atonysan/cve-2024-20931_weblogic
Standalone proof-of-concept for CVE-2024-20931 targeting Oracle WebLogic Server to trigger remote code execution in unpatched deployments.
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 filosottile/cve-2016-2107
Simple test for the May 2016 OpenSSL padding oracle (CVE-2016-2107)
 ianxtianxt/cve-2017-3248
Proof-of-concept exploit for CVE-2017-3248, a remote code execution vulnerability in Oracle WebLogic Server. Designed for penetration testing and…
 joakimbulow/cve-2026-34308
Proof-of-concept for CVE-2026-34308, a MySQL Server JSON component denial-of-service vulnerability. Demonstrates stack exhaustion via deep $ref…
 quynhle7821/cve-2021-2302
Proof-of-concept exploit for CVE-2021-2302 targeting Oracle WebLogic Server with a deserialization-based RCE gadget chain using MVEL expression…
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…