cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…

Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…

System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

exploitdb // The official Exploit-Database repository

Docker-based vulnerable environment and Python exploit script demonstrating CVE-2017-5638 (Apache Struts2 RCE) for educational security testing.

No-root network monitor, firewall and PCAP dumper for Android

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…

Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques

Atlassian JIRA Template injection vulnerability RCE

Proof-of-concept exploit for CVE-2020-13925, a command injection vulnerability in Apache Kylin's diagnostic API, allowing remote code execution via…

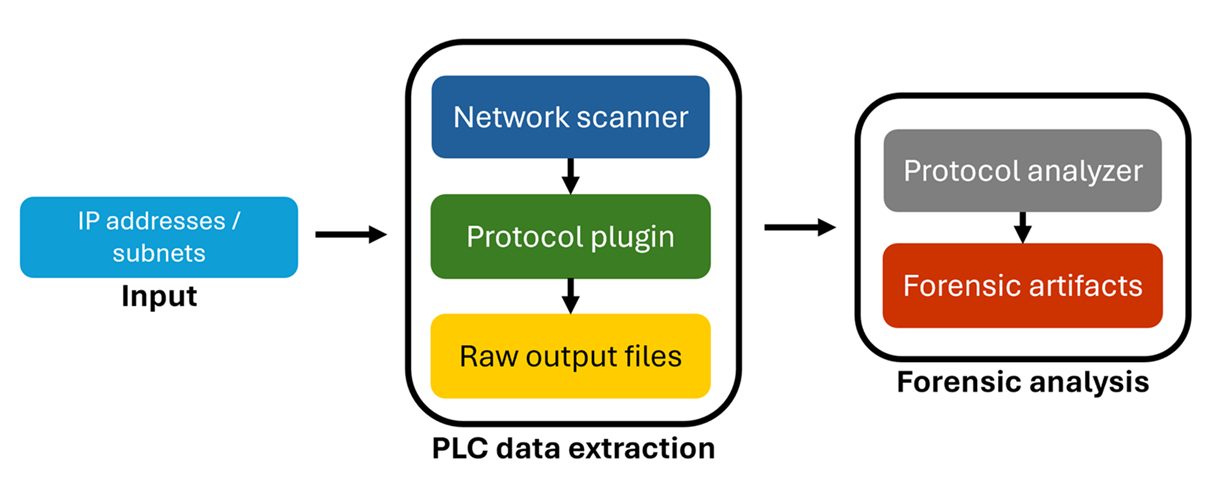
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…

Grand Theft Auto V for PC allows attackers to achieve partial remote code execution or modify files on a PC, as exploited in the wild in January…

This project hosts security advisories and their accompanying proof-of-concepts related to research conducted at Google which impact non-Google owned…

IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…

A full-featured open-source Wi-Fi fuzzer