
CVE-2021-31166
 mauricelambert/cve-2021-31166
CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
exploitationexploit-frameworkspayload-development+4
6
mauricelambert/cve-2021-31166CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 h3x0v3rl0rd/cve-2015-1635
Python exploit for CVE-2015-1635 (MS15-034) targeting HTTP.sys remote code execution vulnerability in IIS servers. Supports custom arguments for…
 h3x0v3rl0rd/cve-2017-7269
Exploit for CVE-2017-7269 targeting IIS 6.0 WebDAV remote code execution vulnerability. Enables buffer overflow exploitation on legacy Windows…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 asepsaepdin/cve-2022-21907
Proof-of-concept exploit for CVE-2022-21907, a remote code execution vulnerability in the HTTP protocol stack (IIS). Includes a Python script and…
 atiilla/cve-2026-42897
CVE-2026-42897 - Exchange Health Checker blind spot: outbound IIS URL Rewrite rules silently ignored, making EOMT mitigations invisible in diagnostic…
 dcscoder/exchange_ioc_hunter
CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, CVE-2021-27065
 corelight/cve-2021-31166
Detection rules (Suricata + Zeek) for CVE-2021-31166 HTTP Protocol Stack vulnerability, providing network-level alerts on exploit attempts against…
 corelight/cve-2022-22954
Zeek package that detects CVE-2022-22954 exploit attempts, logs exploit URIs and attacker response data to aid in incident response and network…
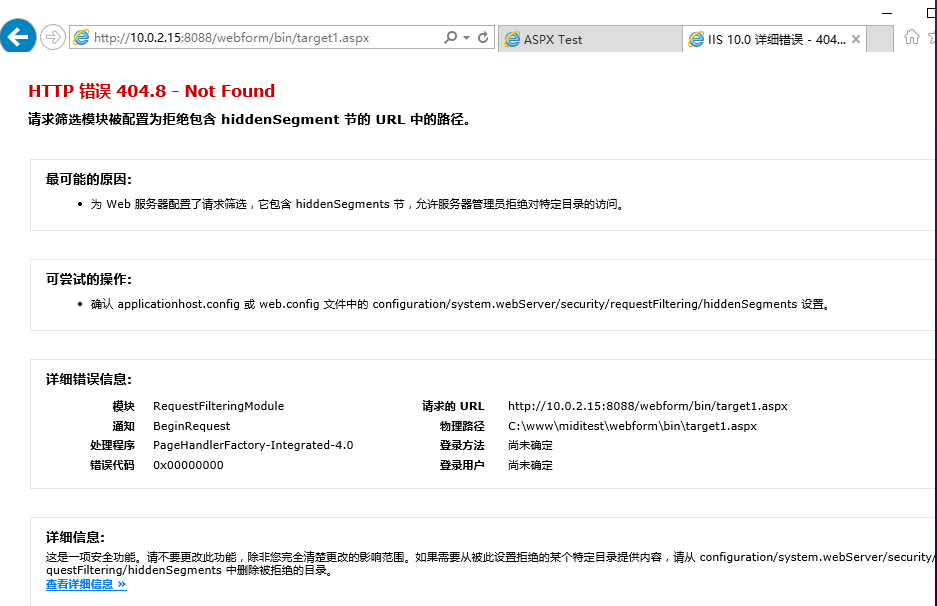 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 admin2099/penetration-testing-assessment-23-04-2026
Penetration testing assessment of a vulnerable IIS 6.0 WebDAV server, demonstrating reconnaissance, enumeration, exploitation (CVE-2017-7269), and…
 nika0x38/cve-2017-7269
A Rust implementation of the POC for CVE-2017-7269, targeting the WebDAV service in Microsoft Internet Information Services (IIS) 6.0.
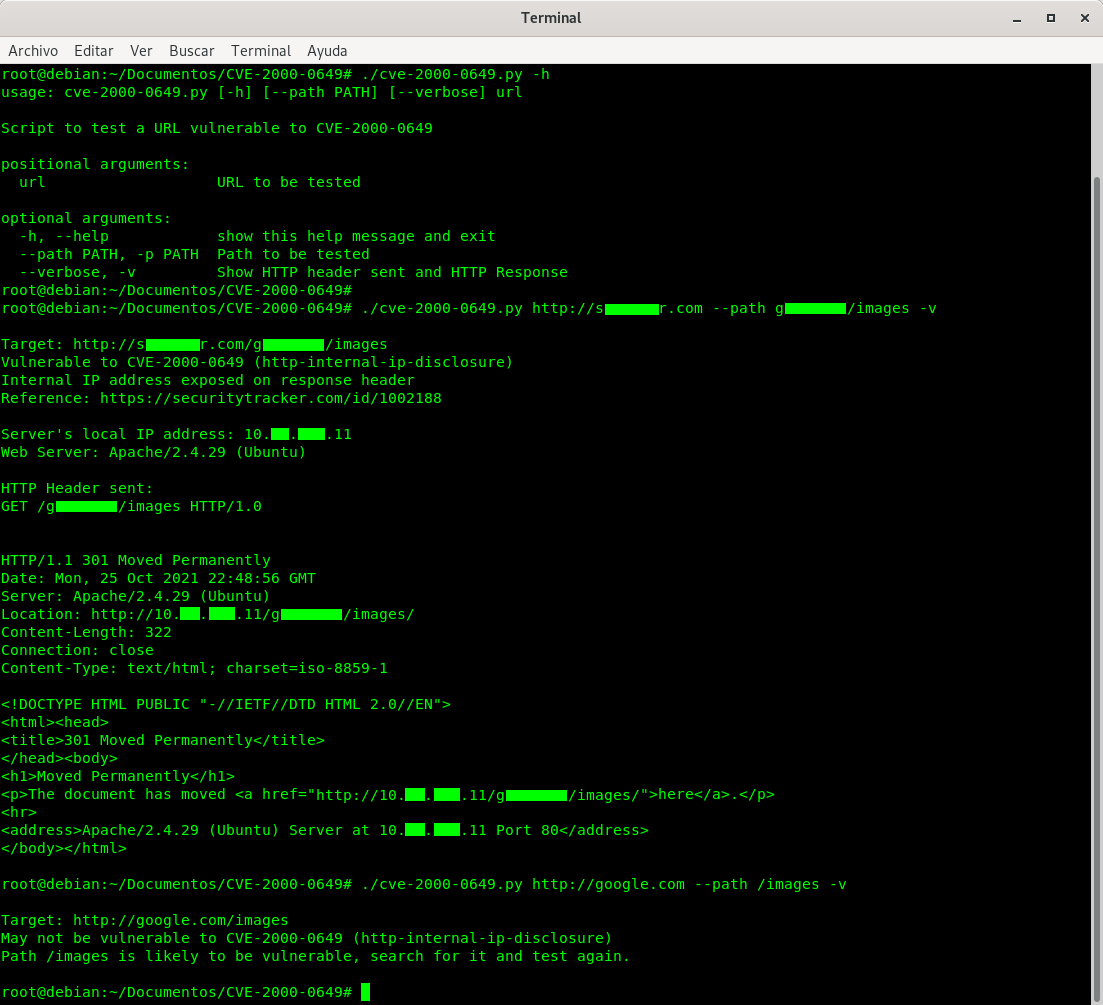 stevenvegar/cve-2000-0649
Script fo testing CVE-2000-0649 for Apache and MS IIS servers
 mauricelambert/cve-2022-21907
CVE-2022-21907: detection, protection, exploitation and demonstration. Exploitation: Powershell, Python, Ruby, NMAP and Metasploit. Detection and…
 llamakko/cve-2015-7214
Proof-of-concept exploit for CVE-2015-7214 demonstrating Same-Origin Policy bypass in Firefox 42.0 via data and view-source URIs, with local and…
 verylazytech/cve-2024-4358
Authentication Bypass Vulnerability — CVE-2024–4358 — Telerik Report Server 2024
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…