cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…


Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Ghidra is a software reverse engineering (SRE) framework

Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…

Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.

Agentic Framework for Synthesizing CodeQL Queries

C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…

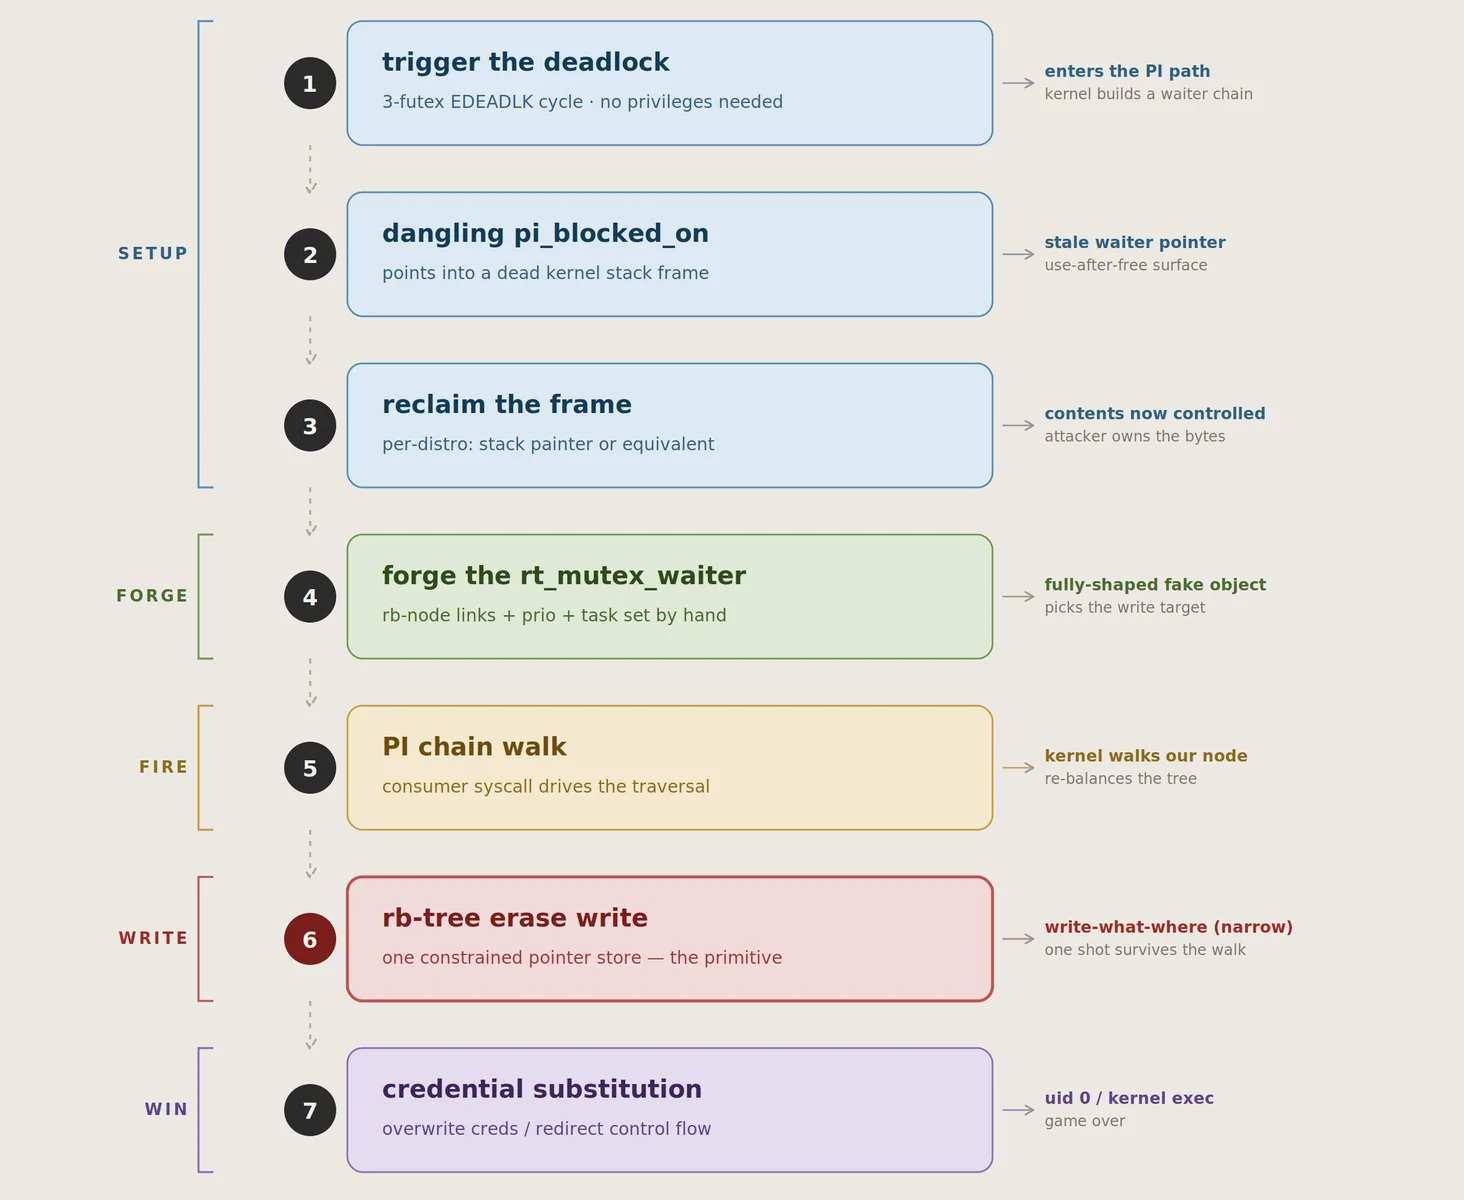
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

Exploit for CVE-2021-1675 (PrintNightmare) enabling local and remote SYSTEM-level privilege escalation on Windows via the Print Spooler service.…

Labtainers: A Docker-based cyber lab framework

Multi-source vulnerability and exploit aggregator with auto-discovery via Nmap and Wappalyzer, searching Exploit-DB, NVD, CVE.org, GitHub, Nuclei,…

MCP Server for Metasploit