

scripts
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
digital-forensicsforensicsincident-response+5
86
clausing/scriptsCollection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
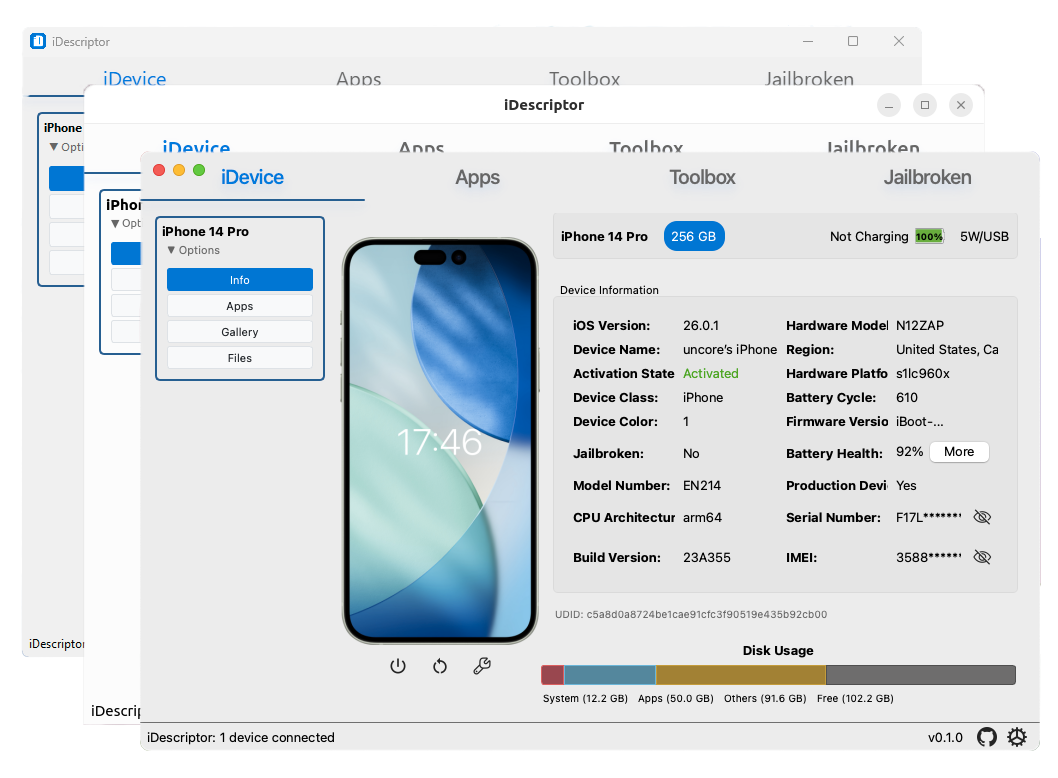 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
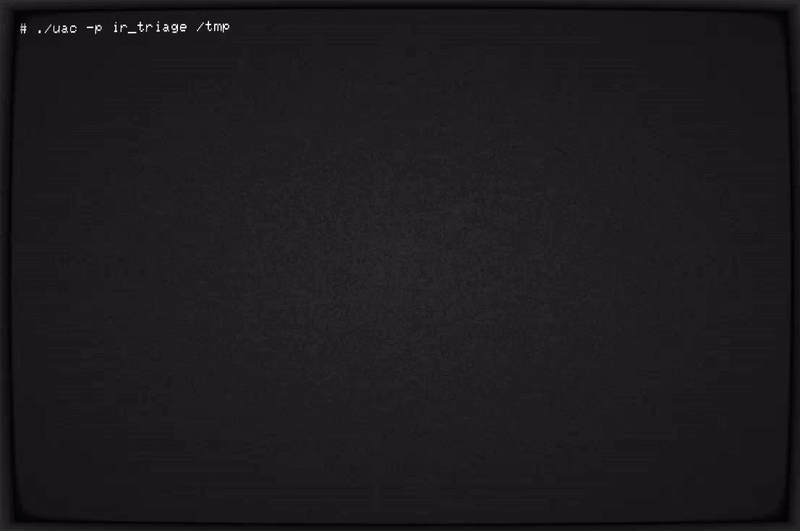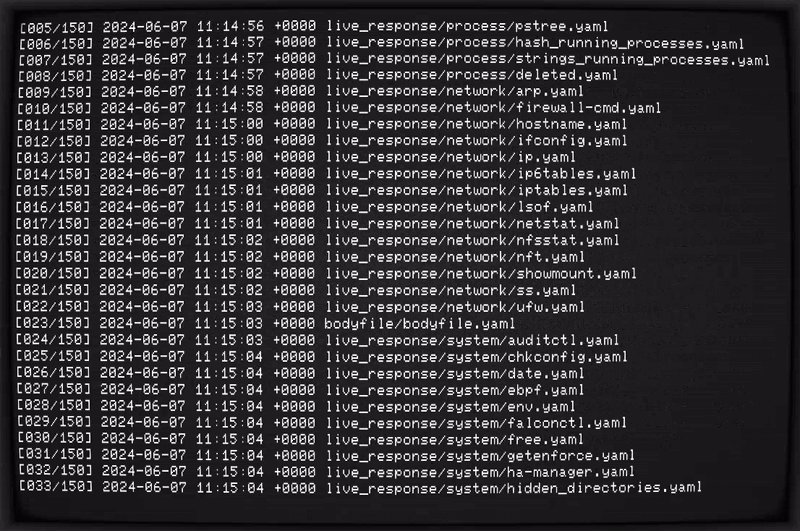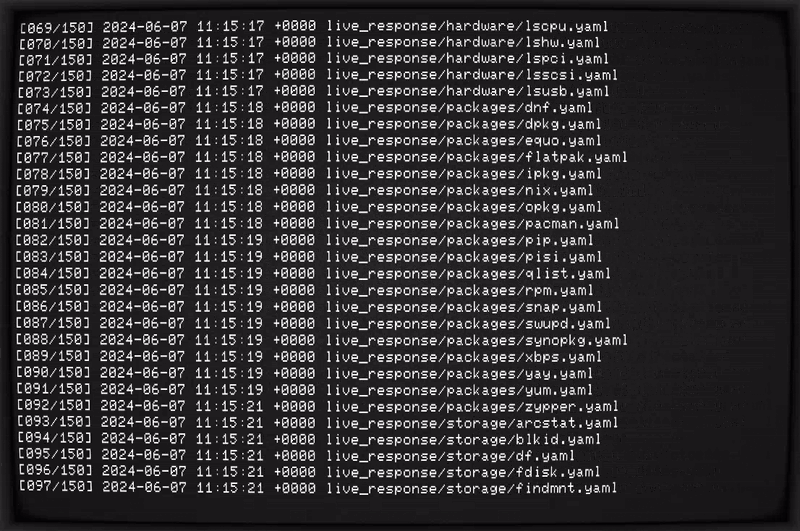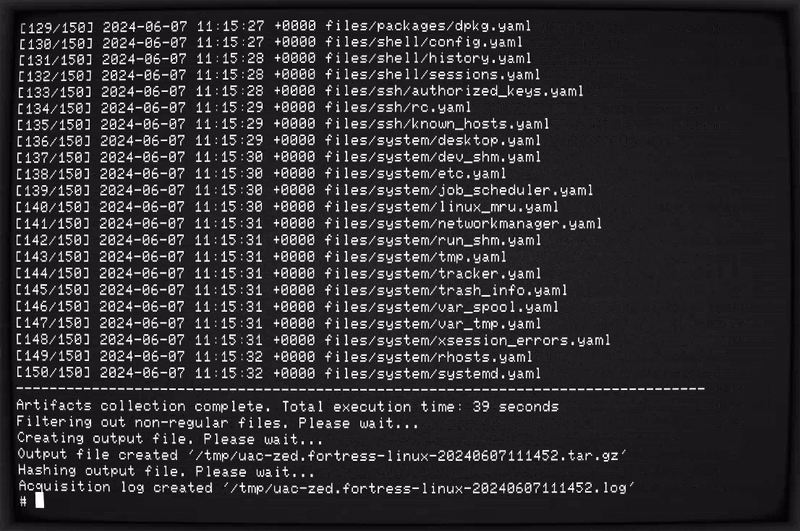 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 securisec/chepy
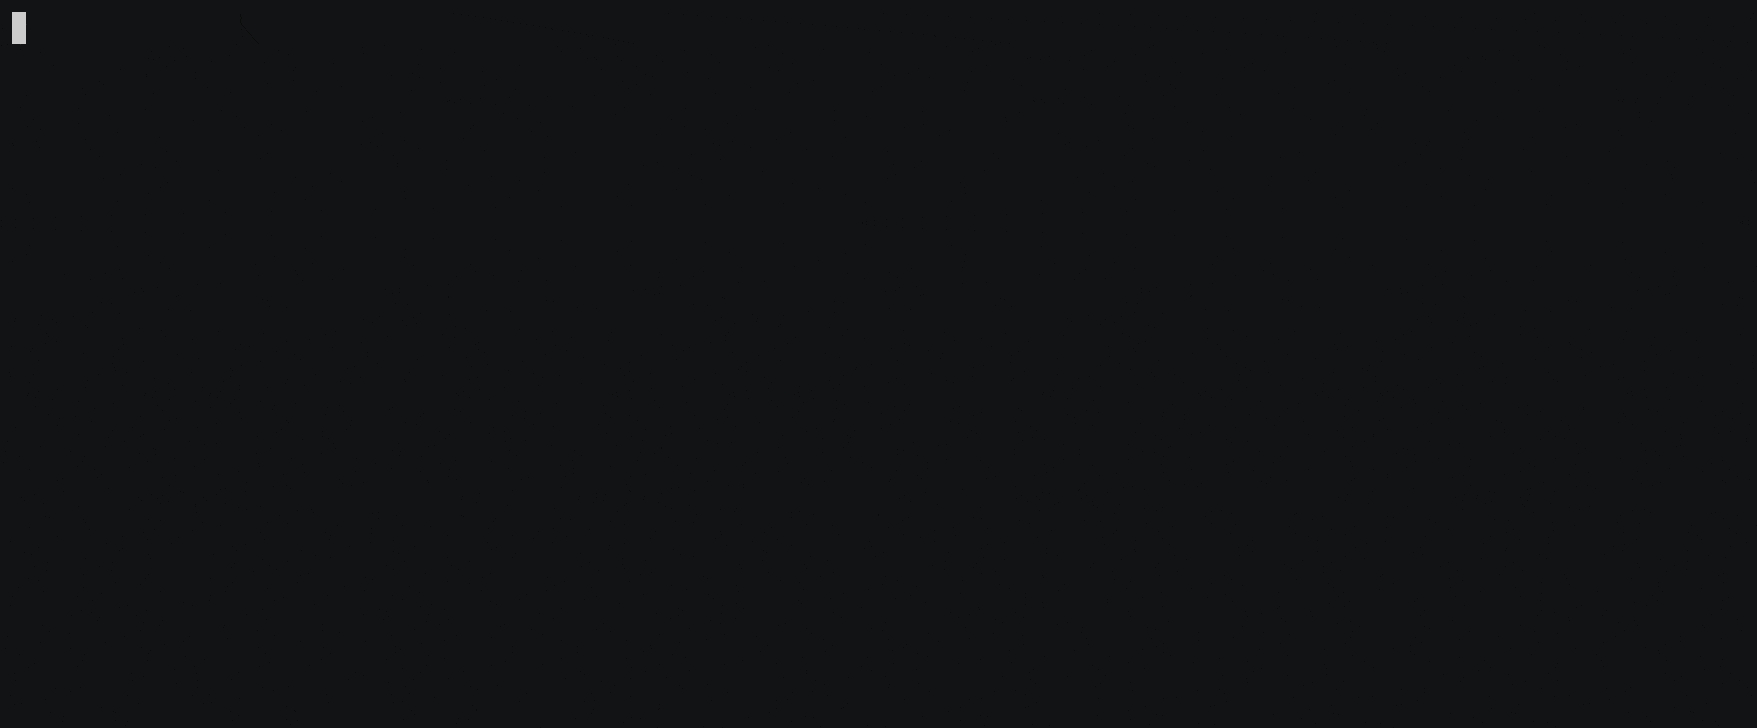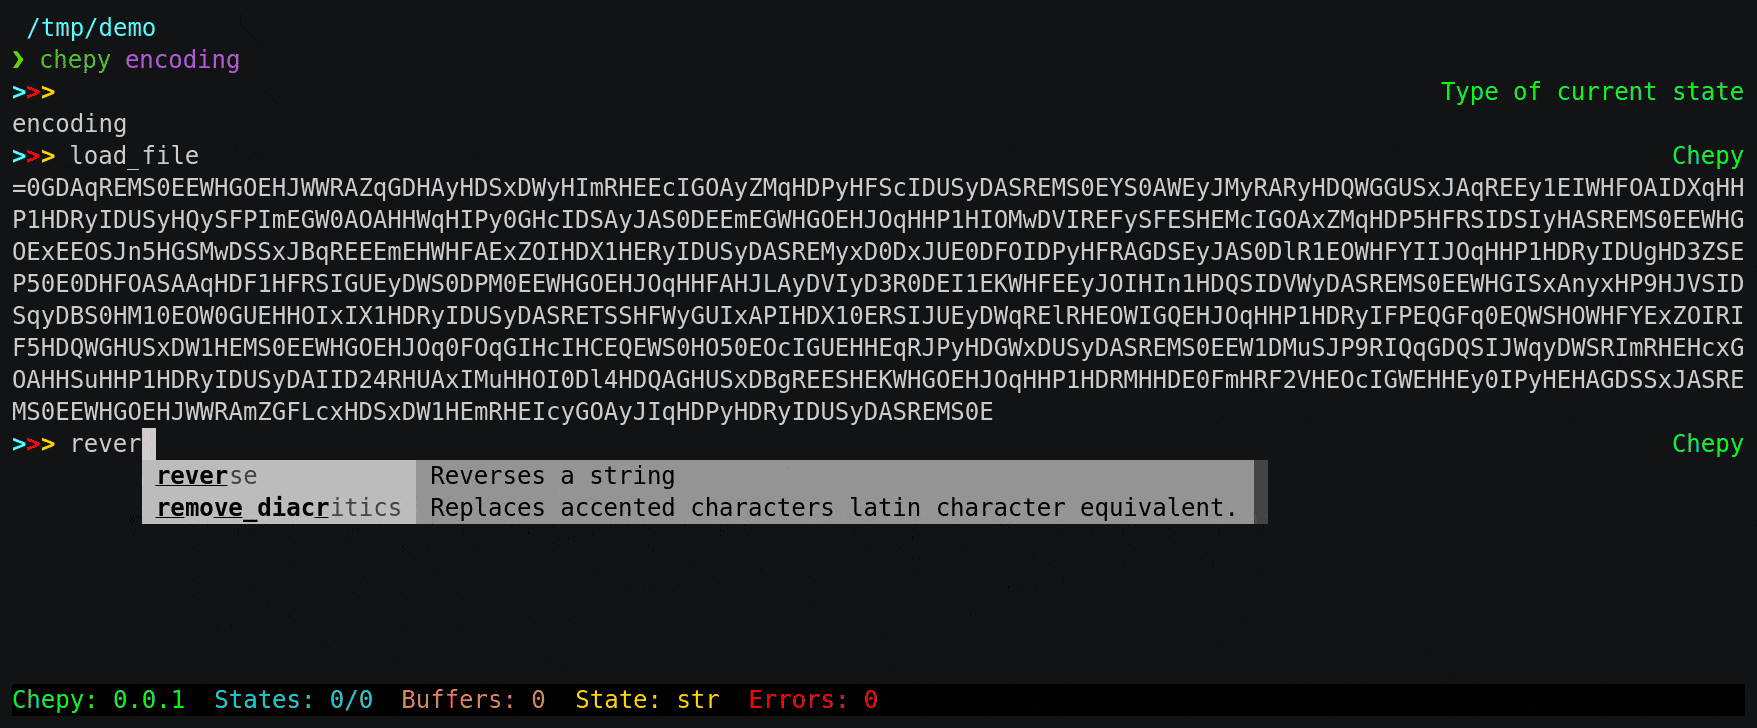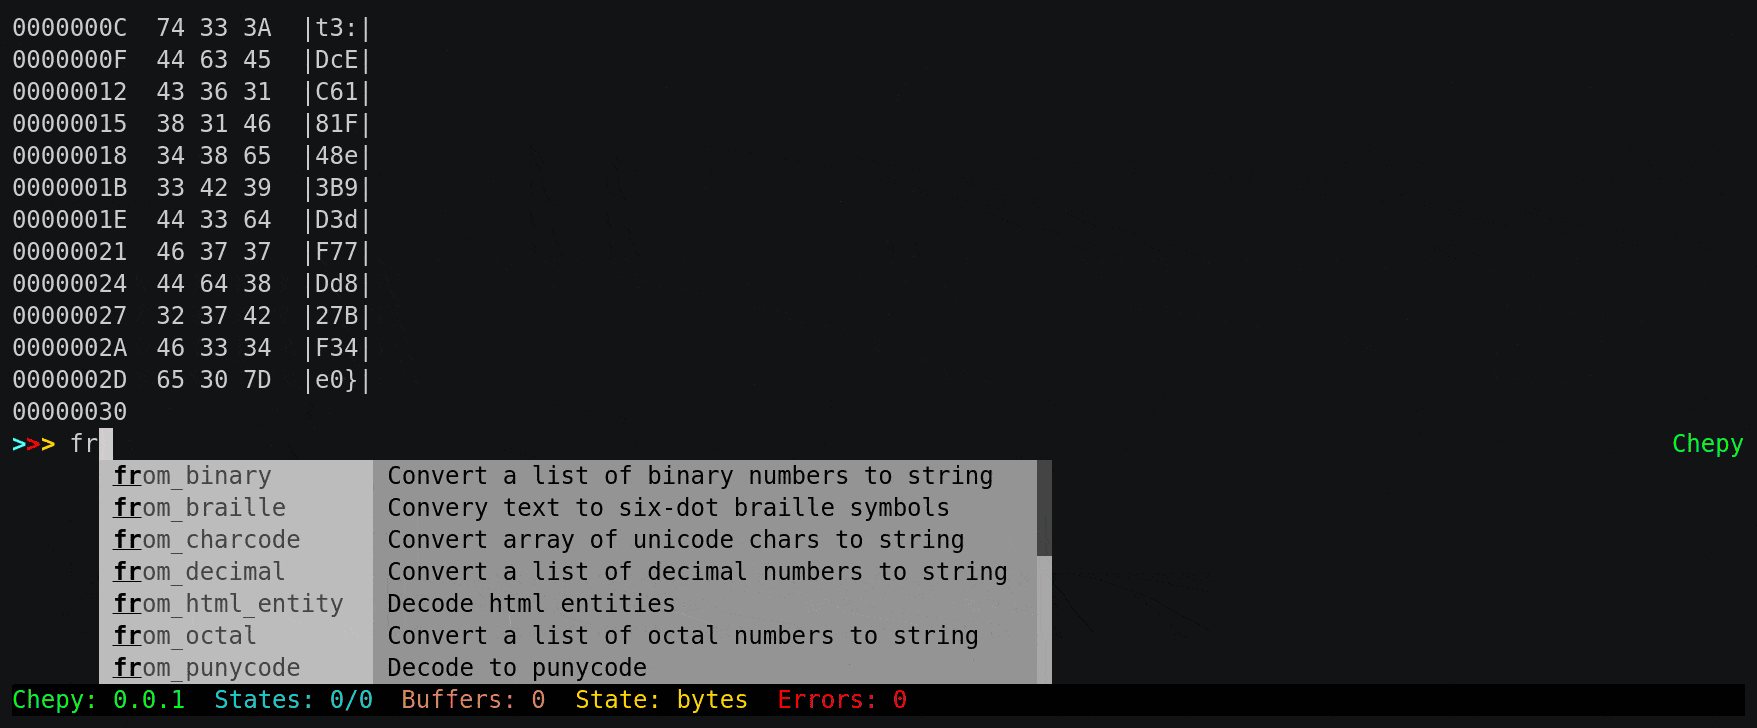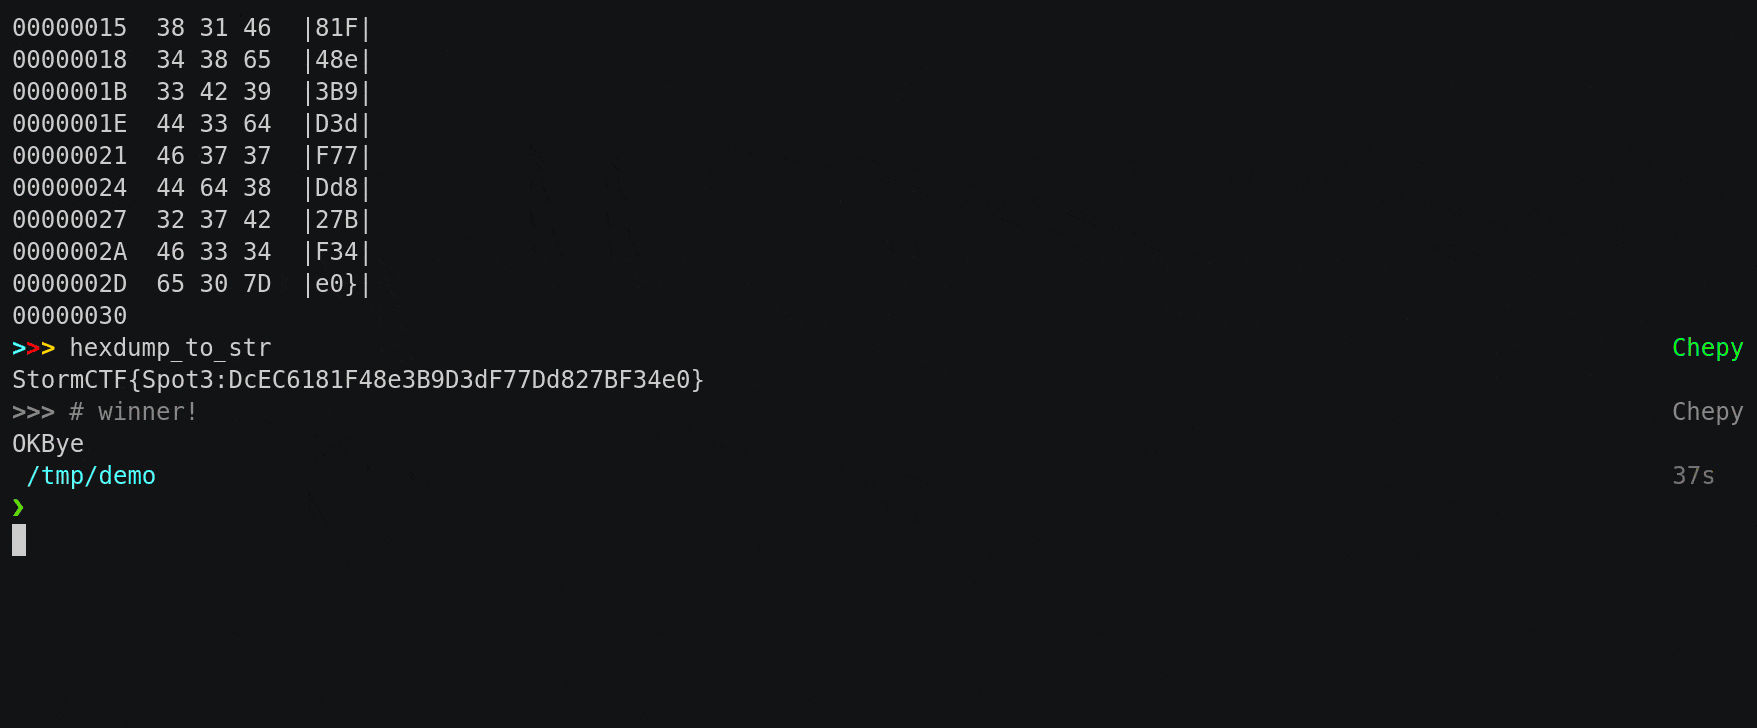
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
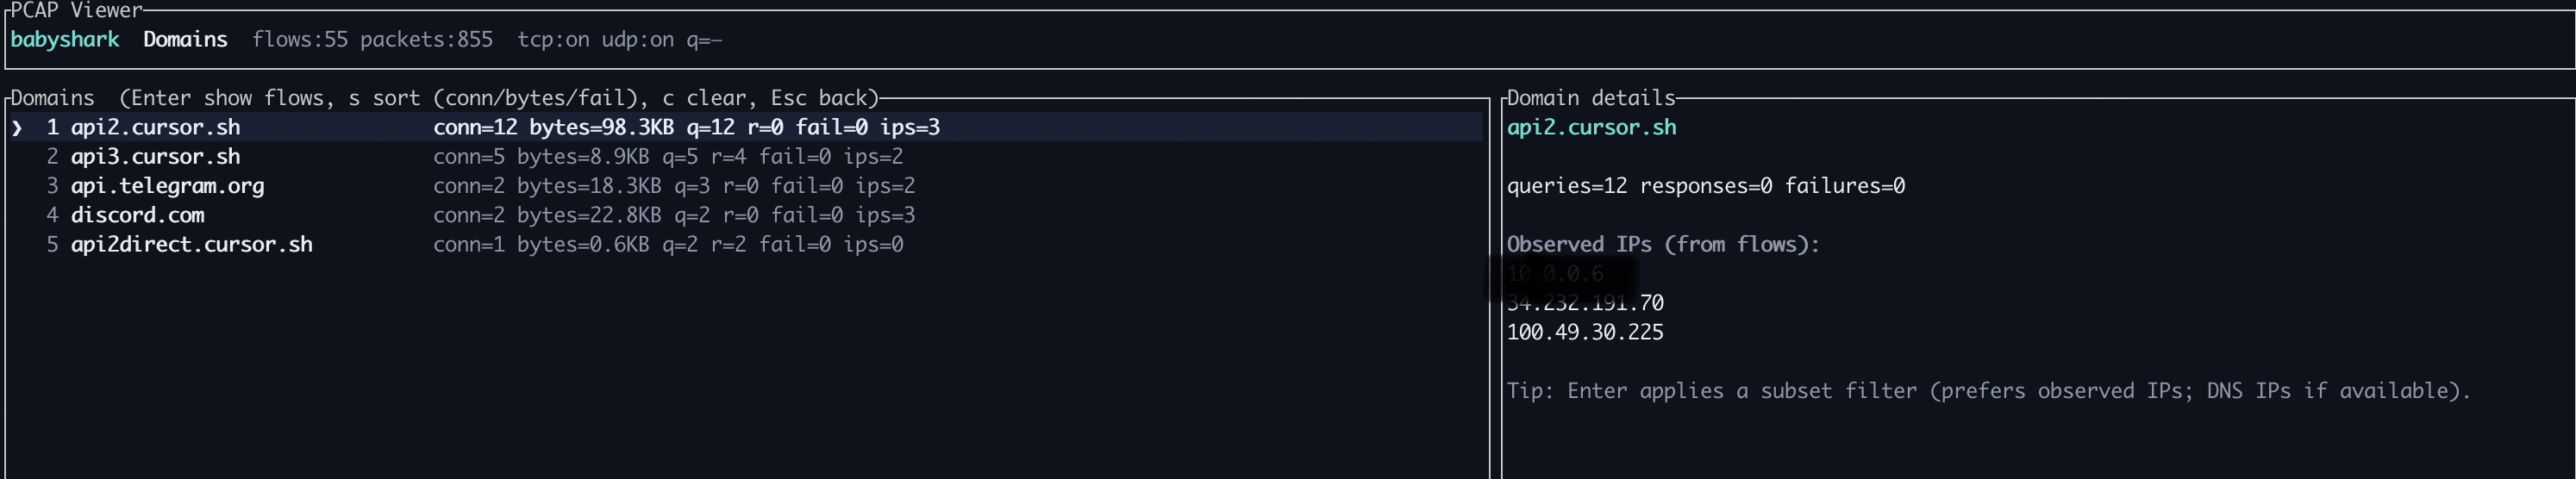 vignesh07/babyshark
Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
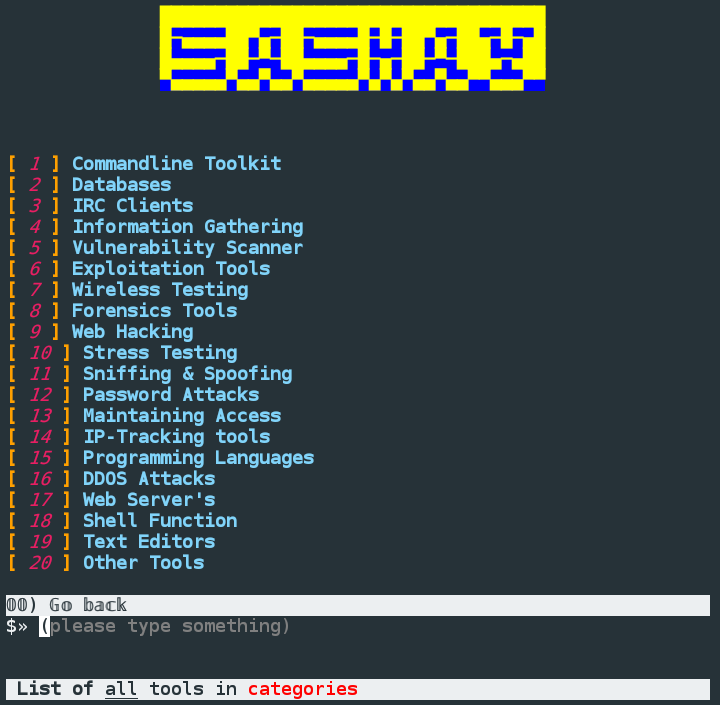 scalabli/sashay
Sashay is an automatic installer for useful tools.
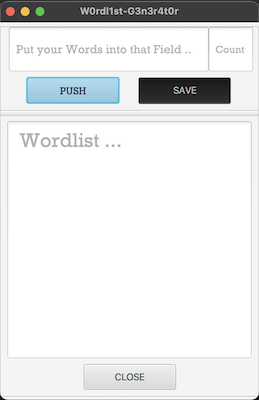 hellgatecorp/docxnginxfx
Deep File Forensic. Create or manipulate Wordlists out of Text Documents (ex: for BruteForcing). Save it Line by Line as a Binary .BIN File or as a…
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 kpcyrd/sn0int
Semi-automatic OSINT framework and package manager
 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 mxrch/ghunt
Async offensive Google framework for OSINT, enabling email/Gaia ID/Drive/geolocation reconnaissance via CLI or Python library with JSON export.
 arxhr007/aliens_eye
AI powered OSINT engine to discover and map 840+ social media identities across the web