

Crimson-Cloak-ISH-wrapper-iOS-
 synchancybersecurity/crimson-cloak-ish-wrapper-ios-
Wrapper to maximize ISH iOS app capabilities without jailbreak
ios-securitymobile-securitypenetration-testing+3
synchancybersecurity/crimson-cloak-ish-wrapper-ios-Wrapper to maximize ISH iOS app capabilities without jailbreak
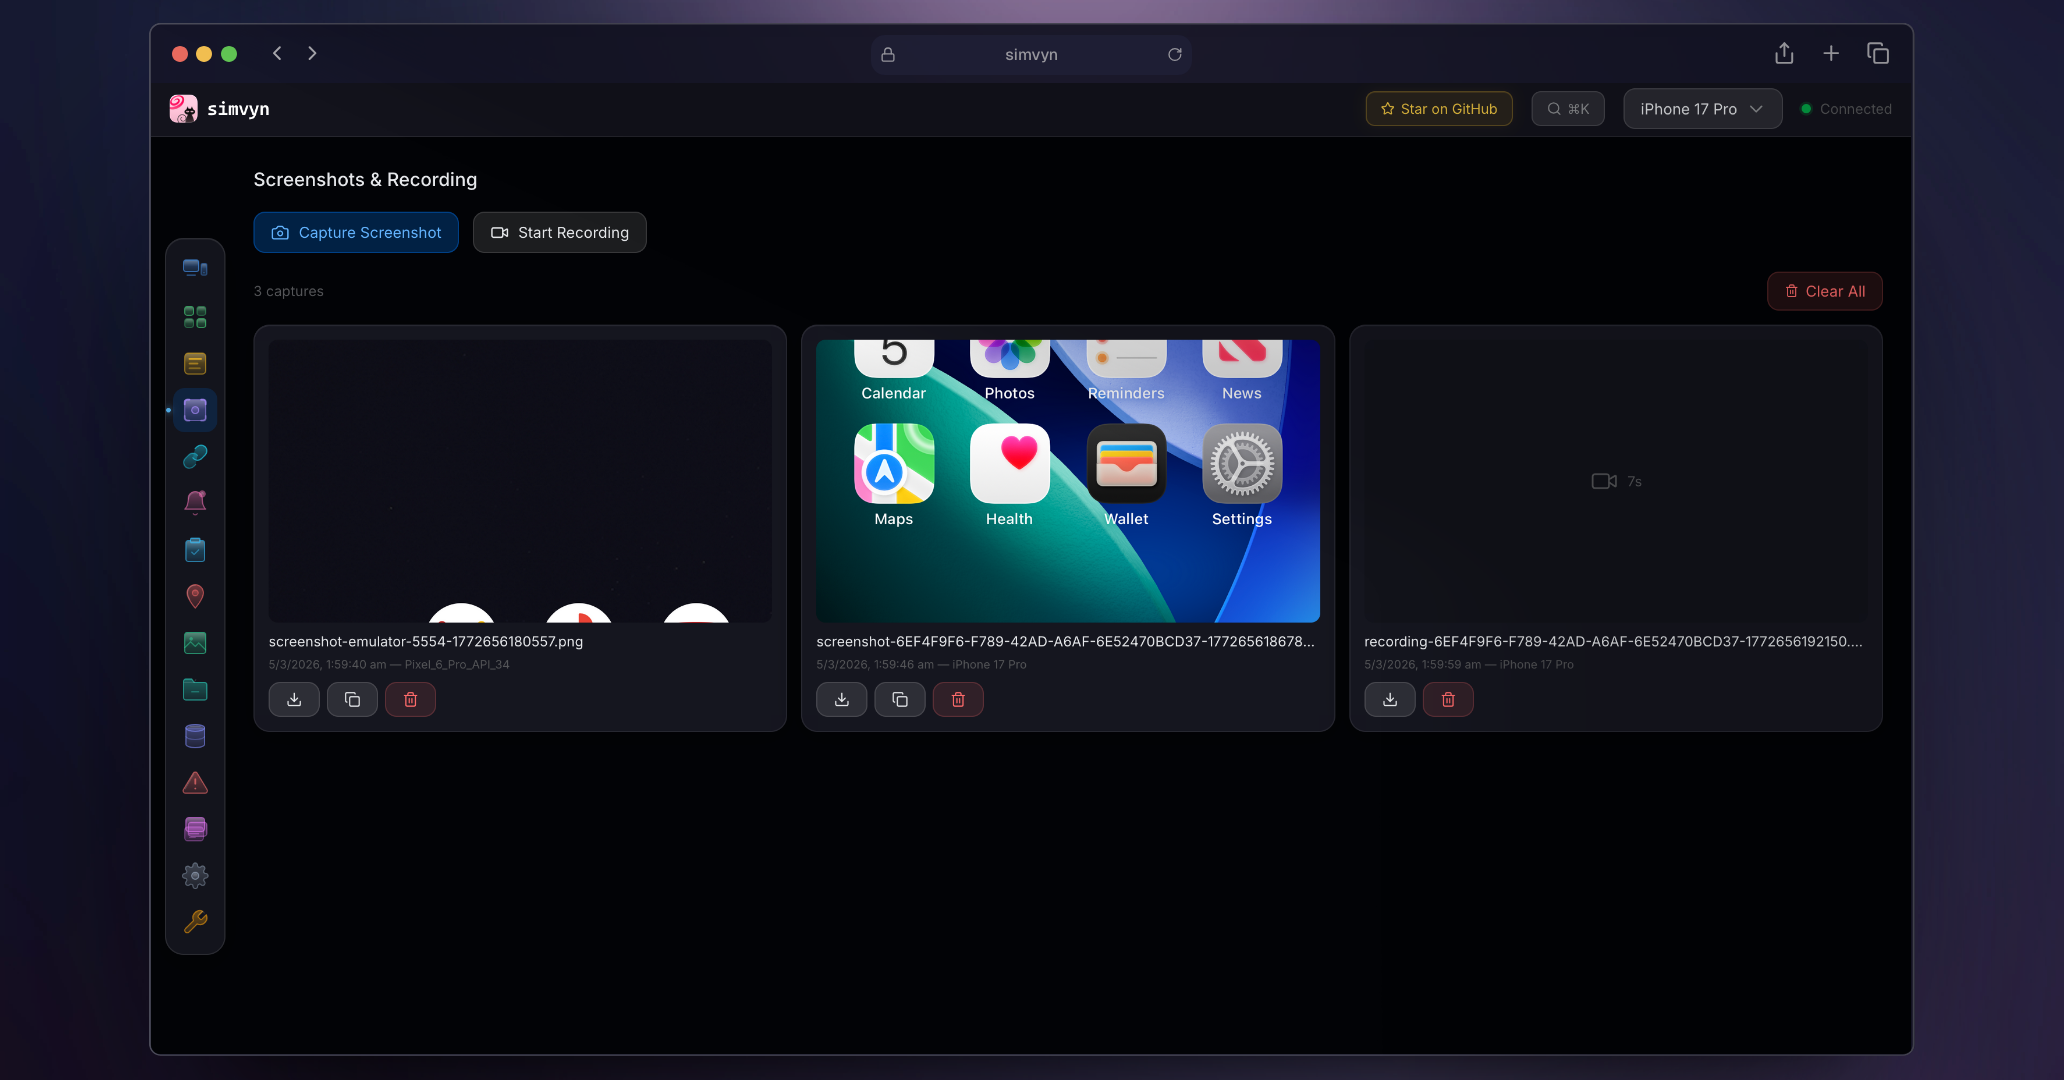 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 mitmproxy/mitmproxy
An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.
 universal-debloater-alliance/universal-android-debloater-next-generation
Cross-platform GUI written in Rust using ADB to debloat non-rooted Android devices. Improve your privacy, the security and battery life of your…
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
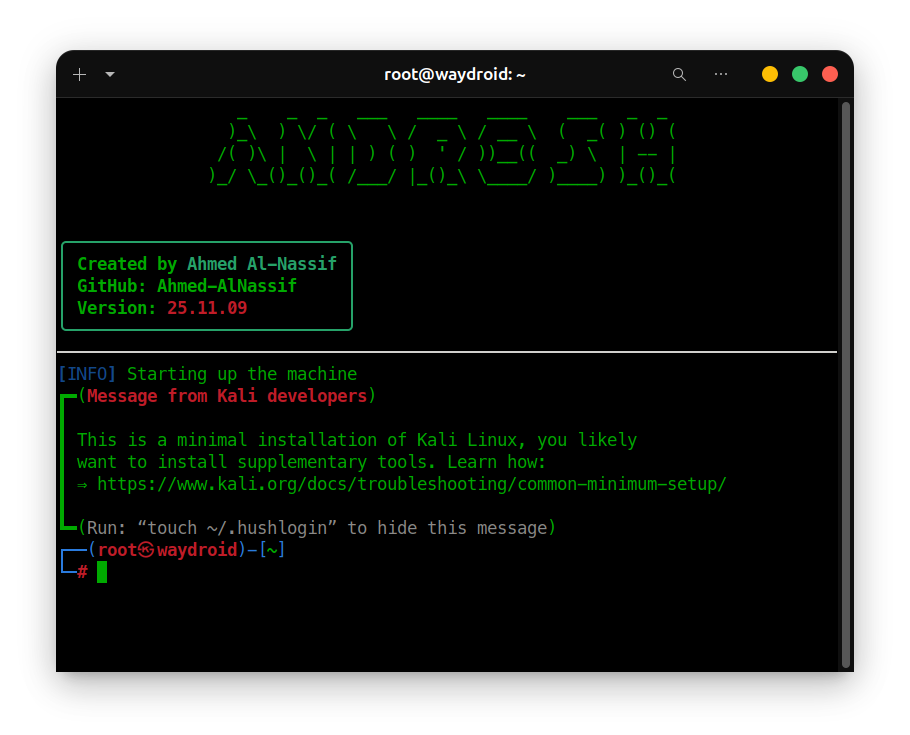 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
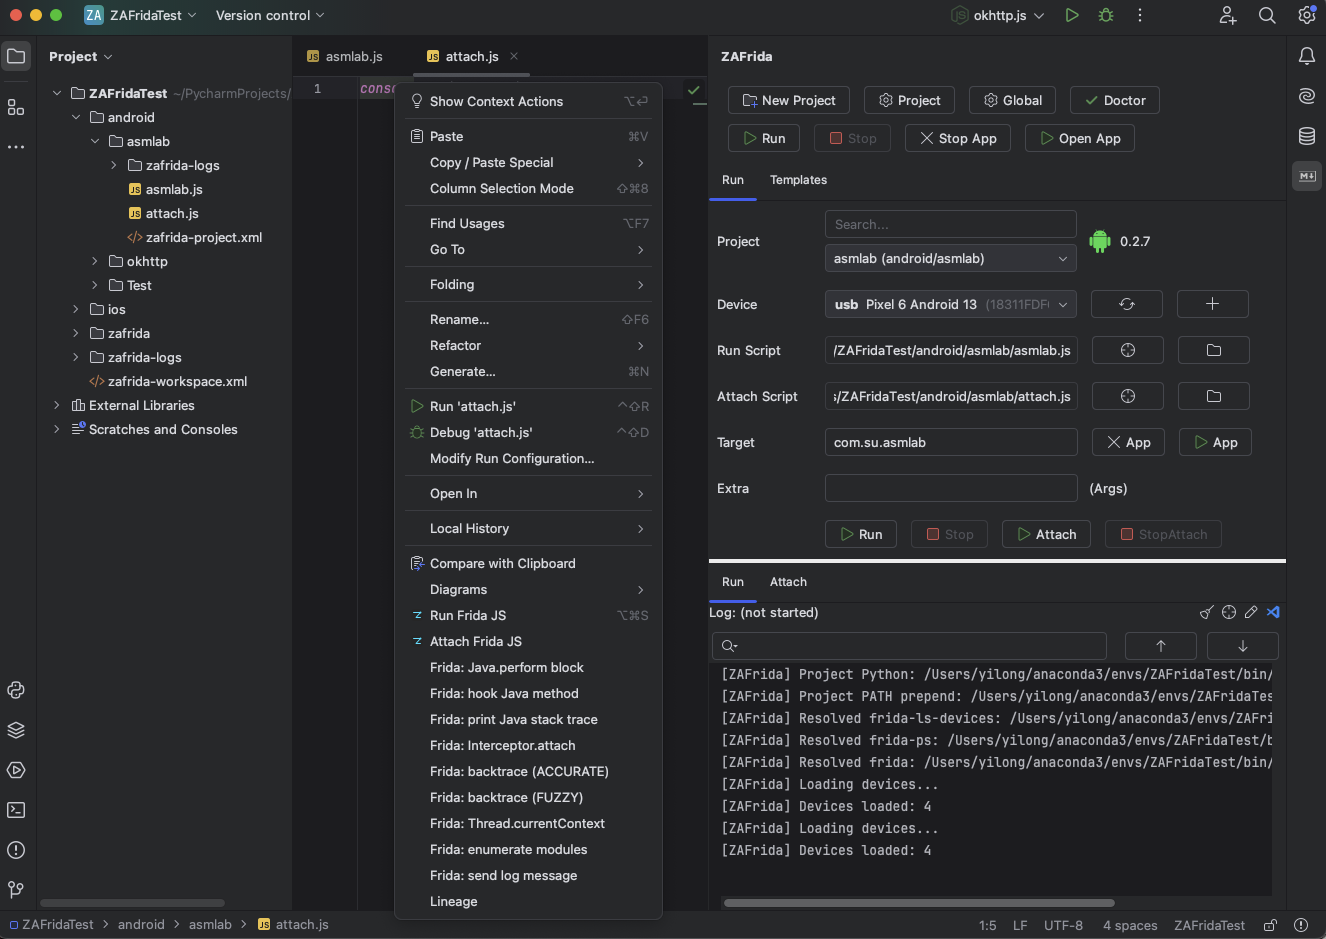 yilongmd/zafrida-ui
A Frida UI tool window inside PyCharm / JetBrains IDEs.
 nccgroup/assethook
LD_PRELOAD magic for Android's AssetManager
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
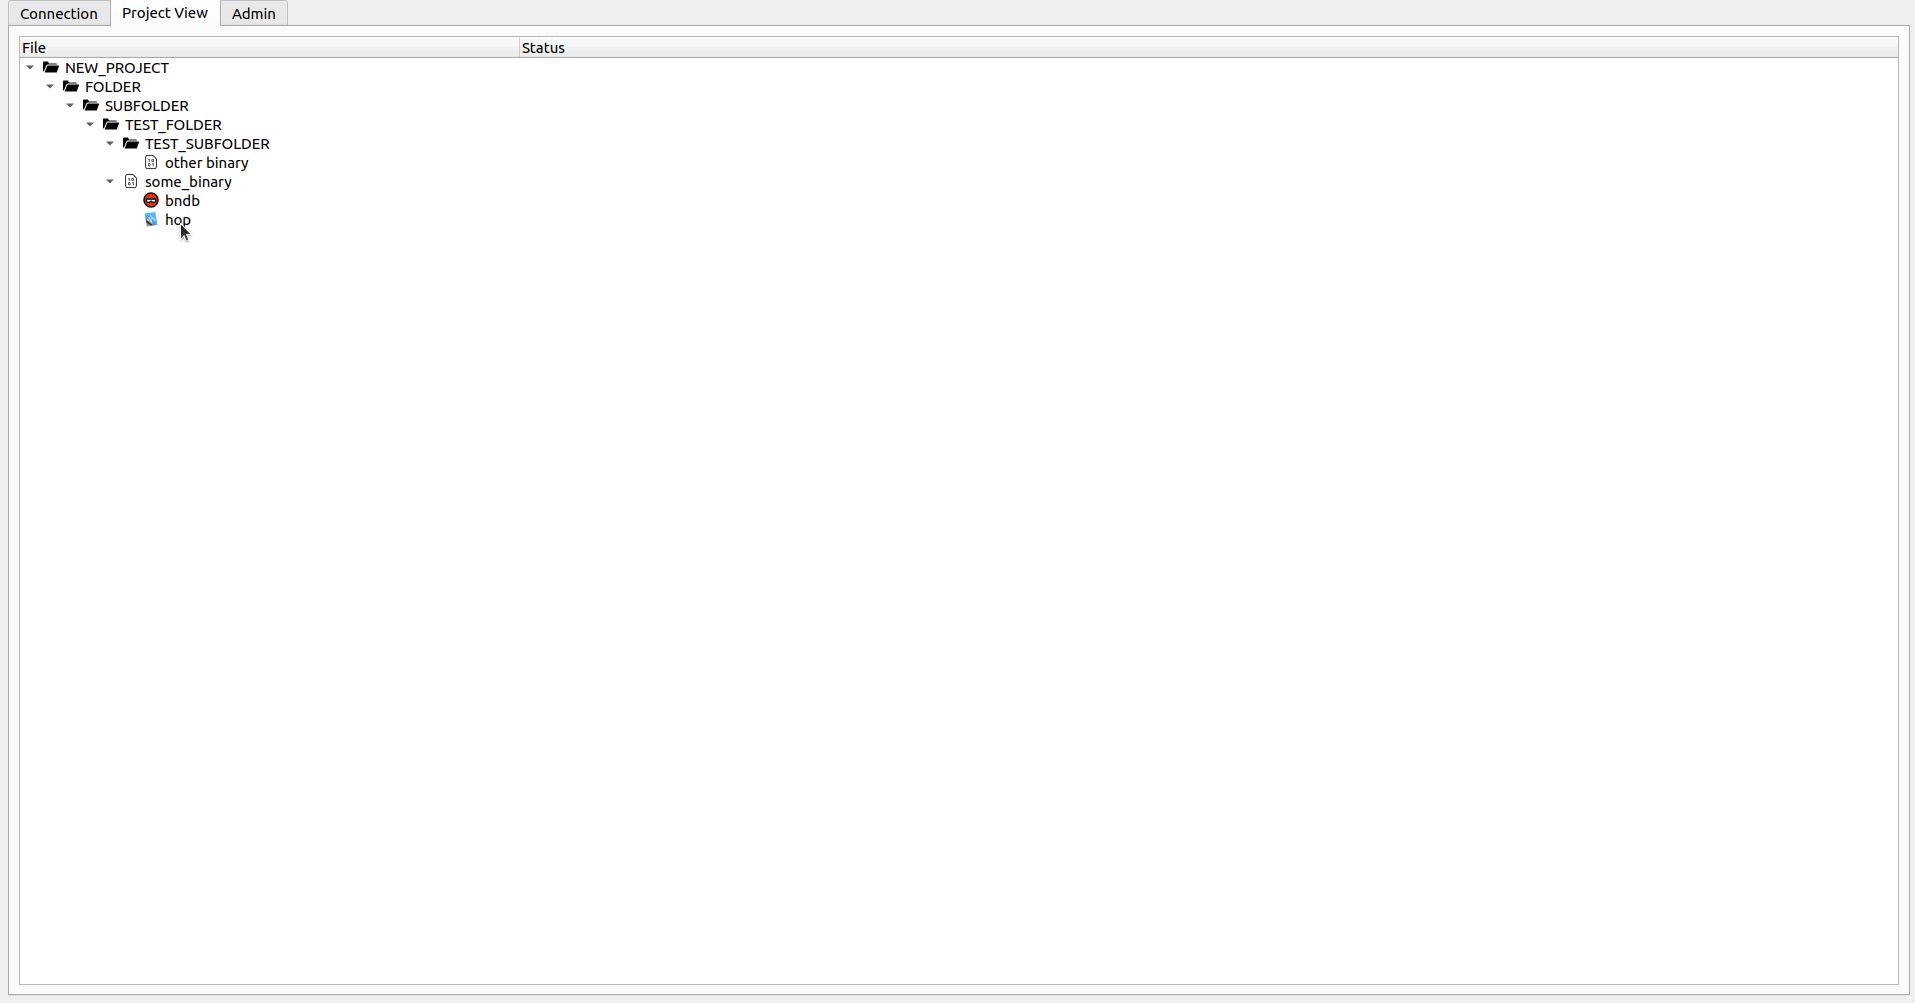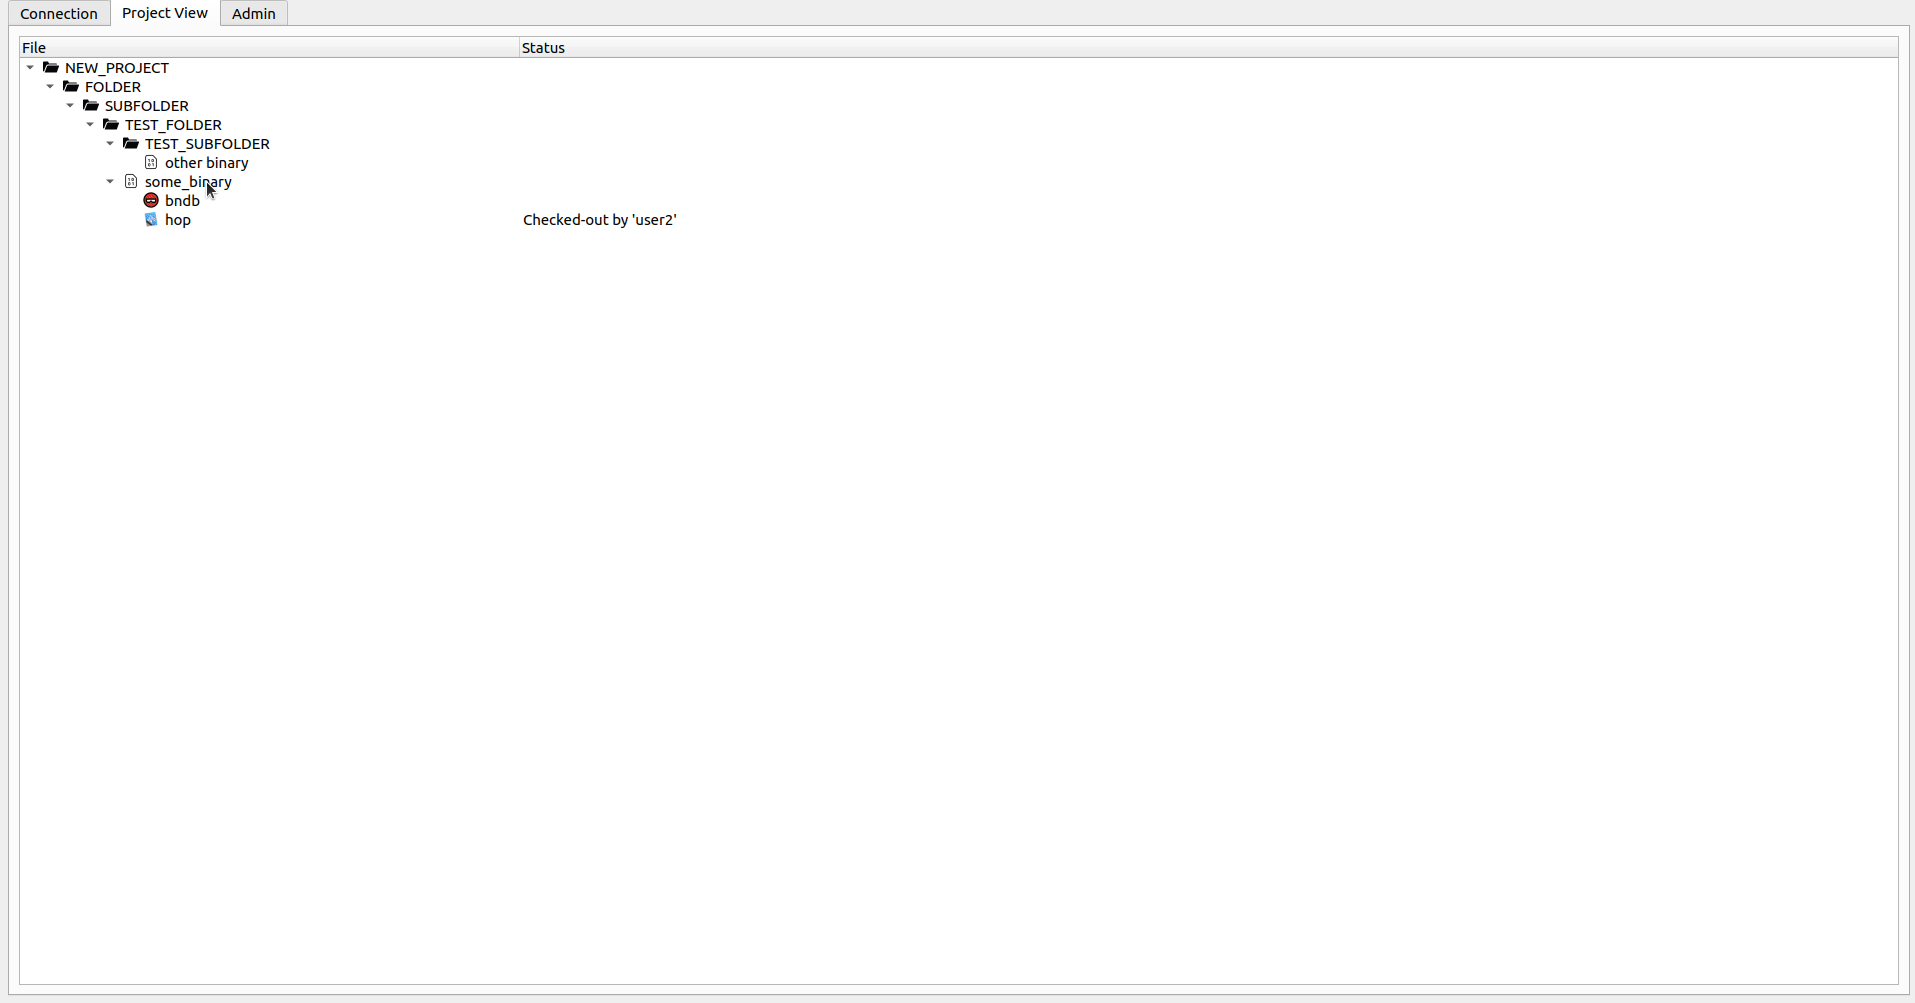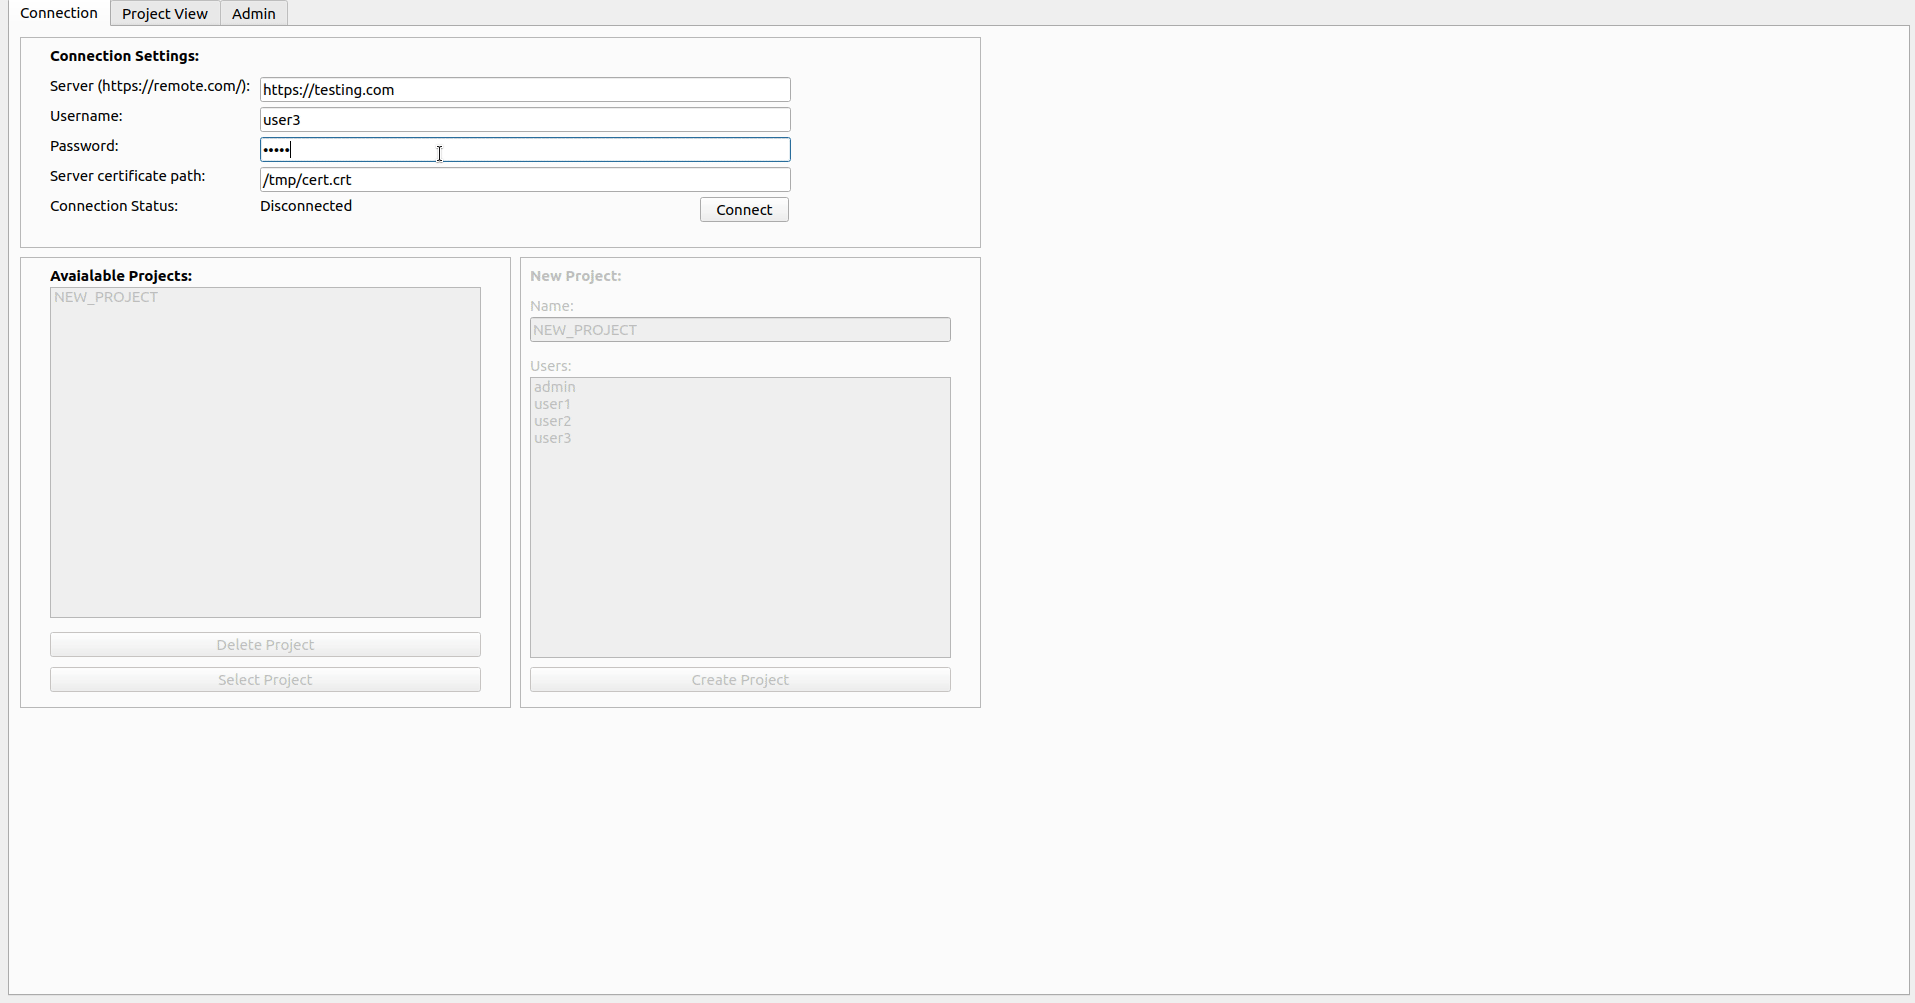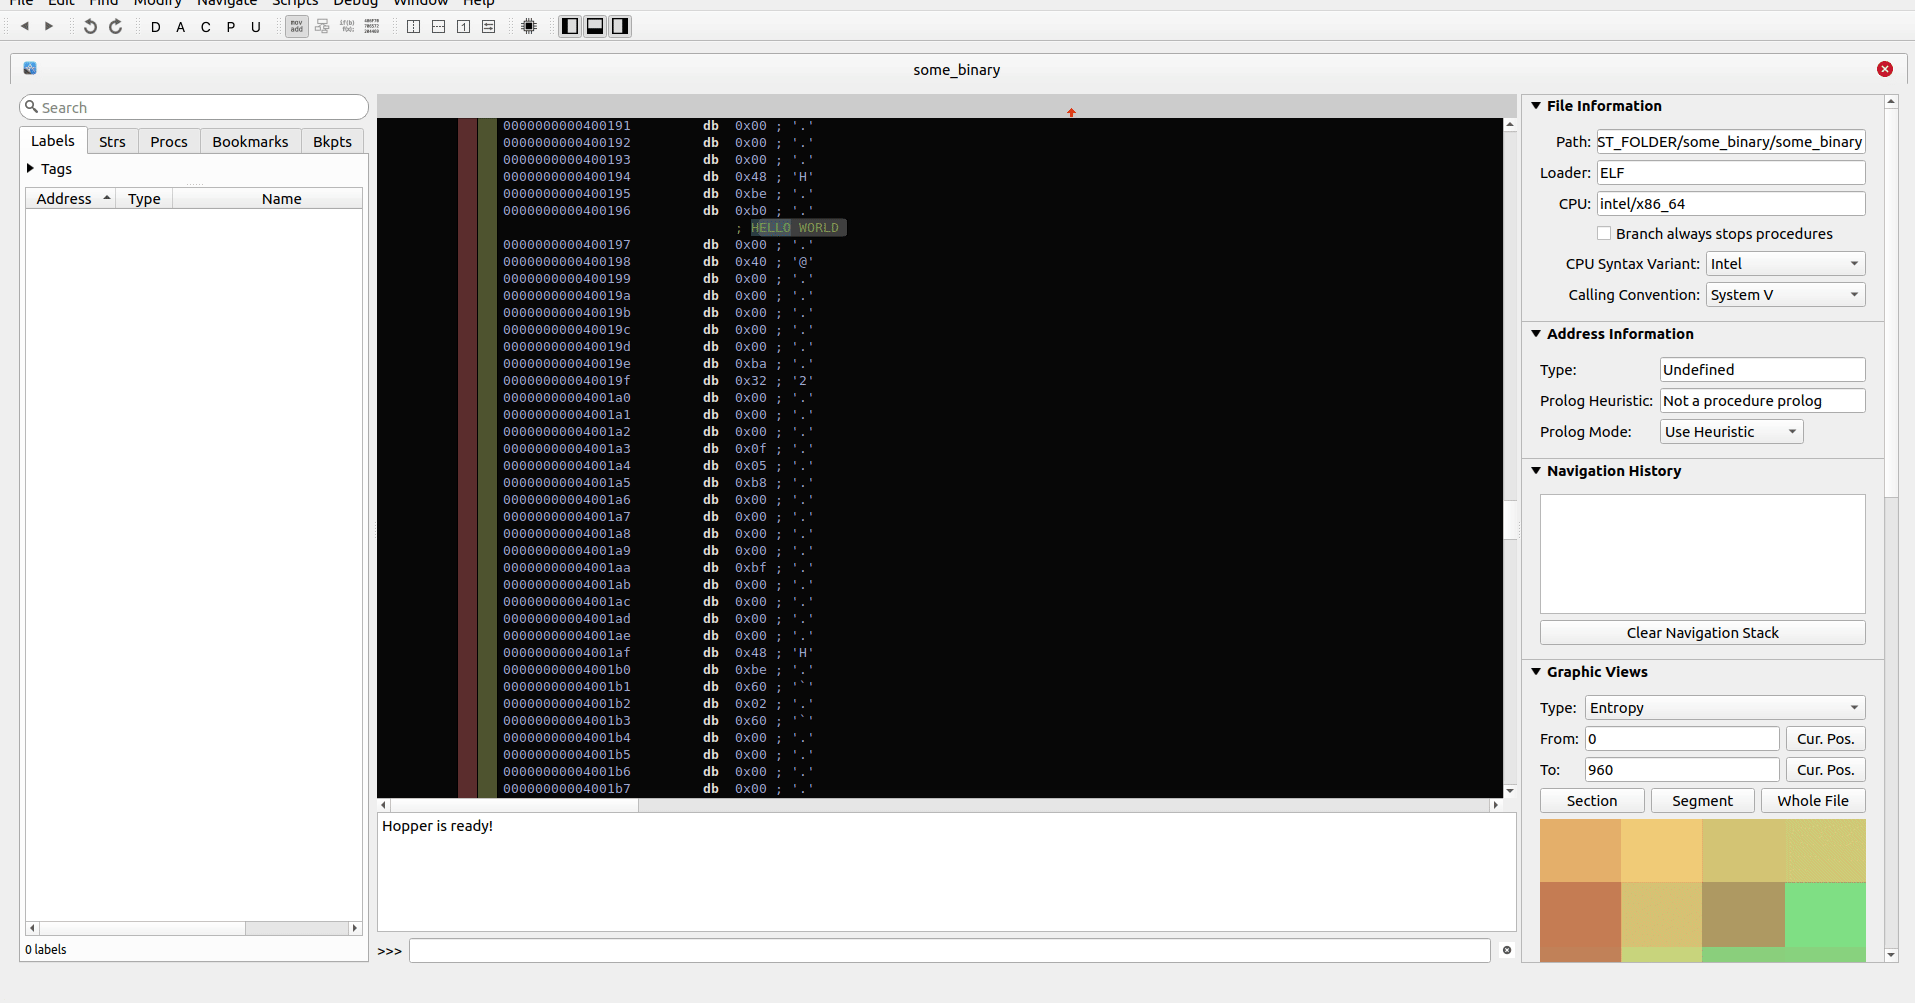 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 theshinigami/mafrida
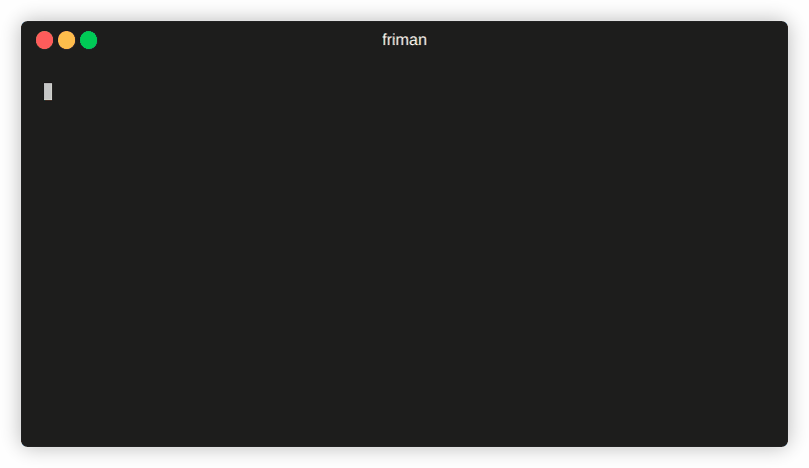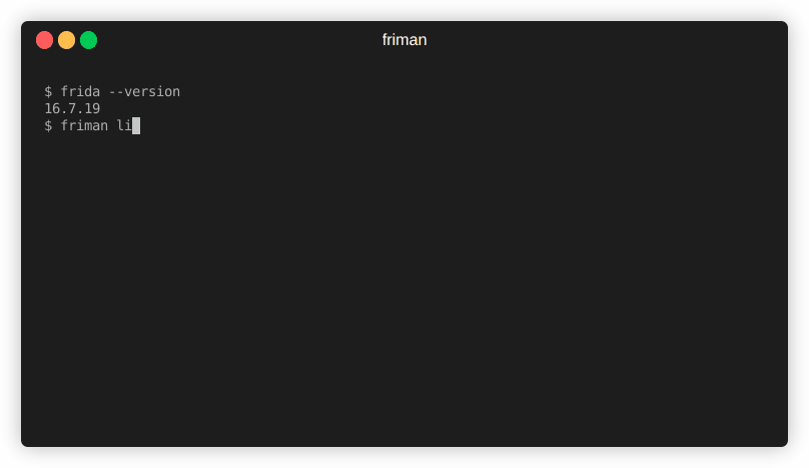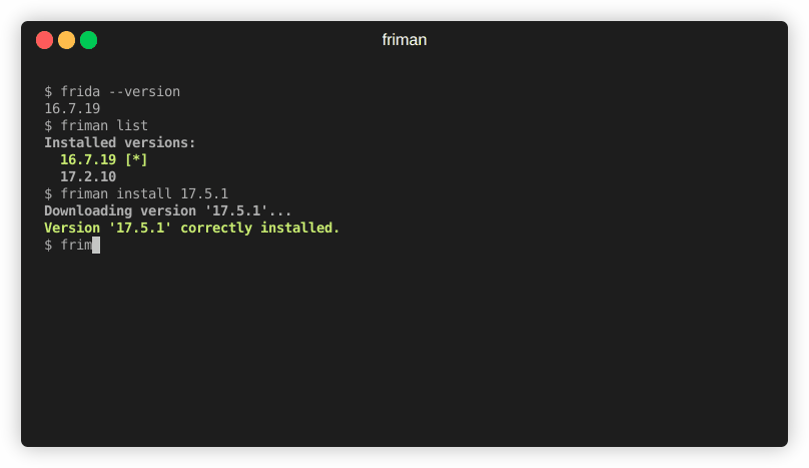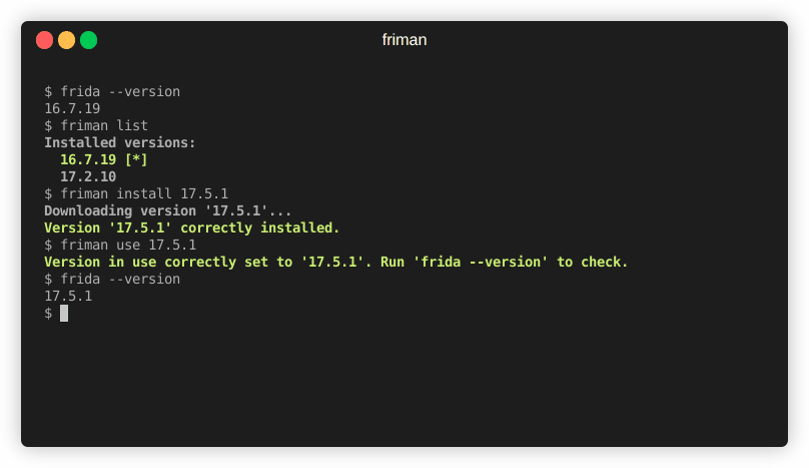
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 e-gleba/world_conqueror_4_ru
Translated strings for World Conqueror 4 (RU)
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.