Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…

Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…

Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…

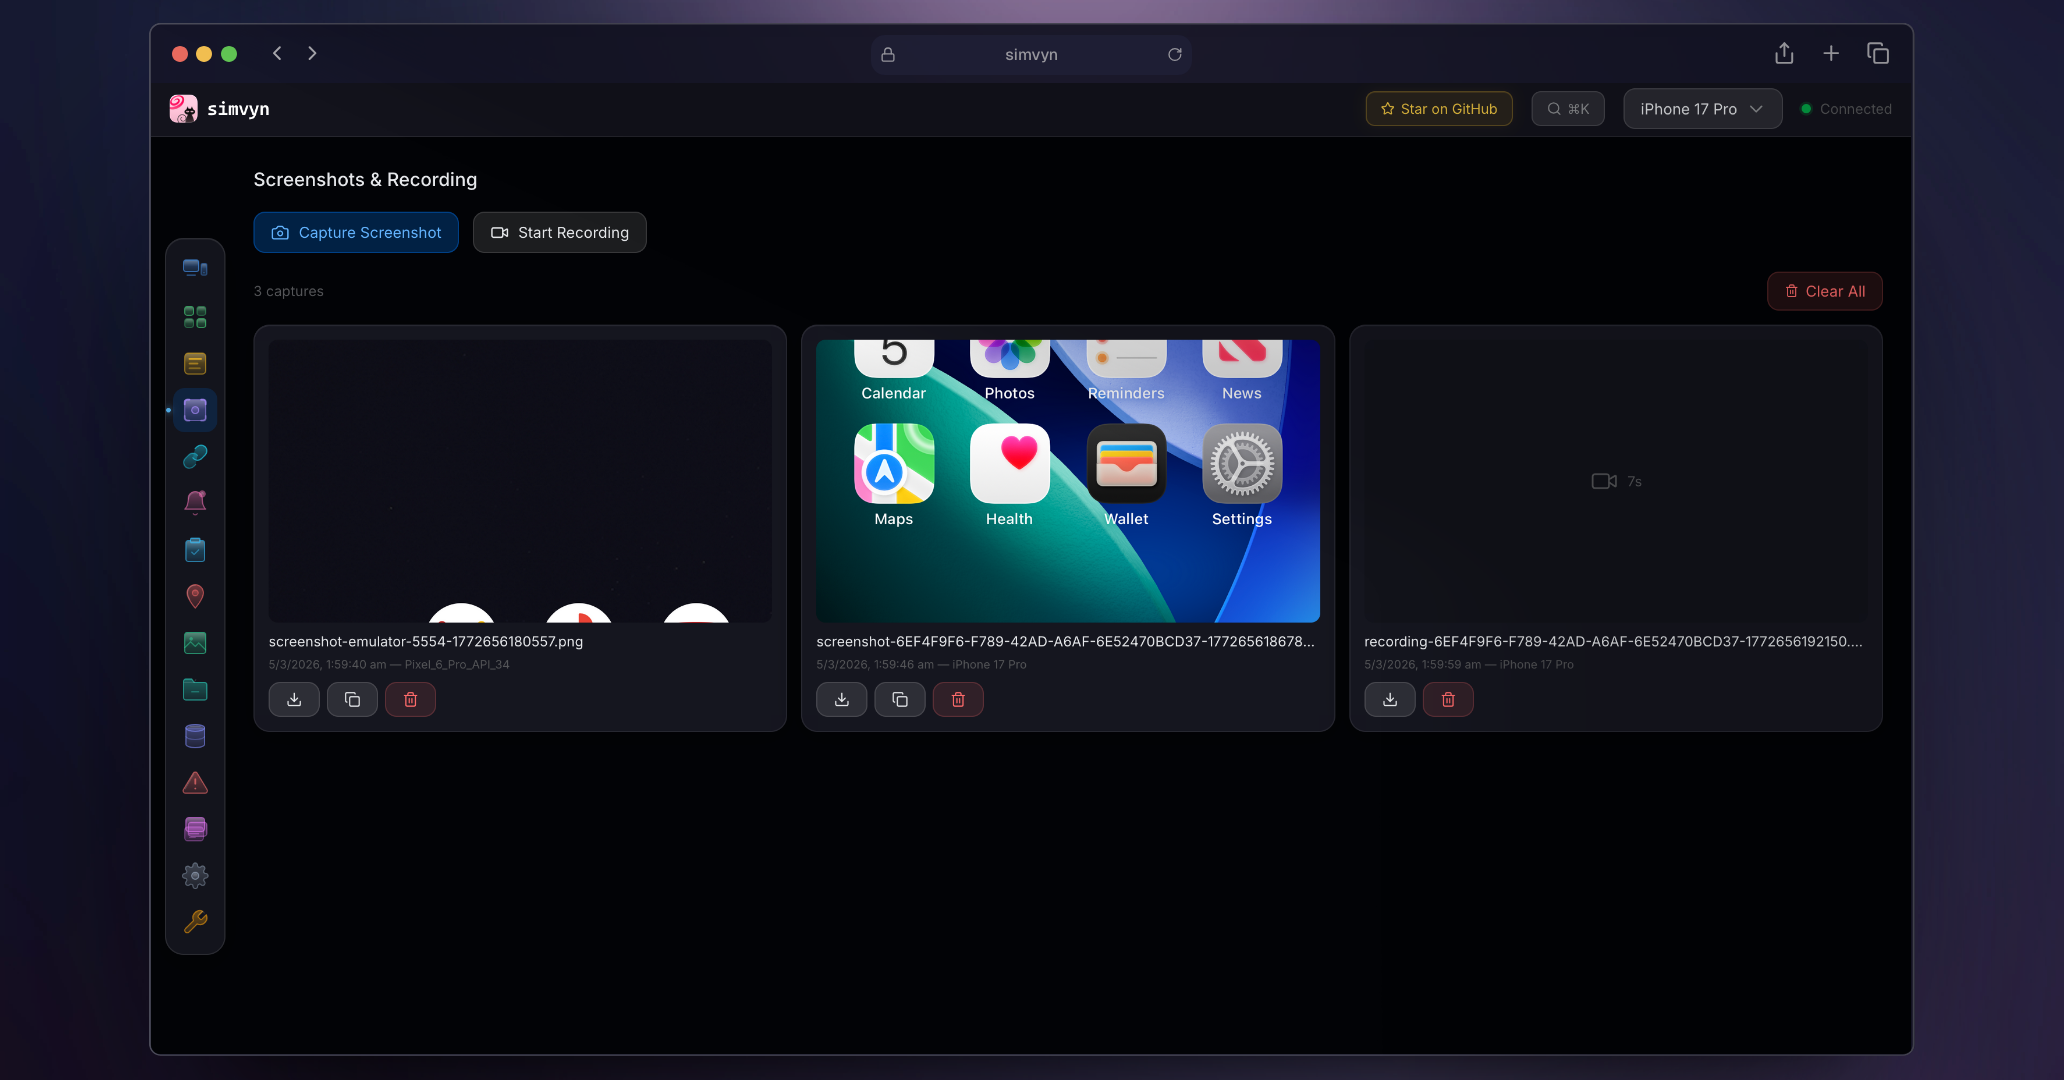
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…

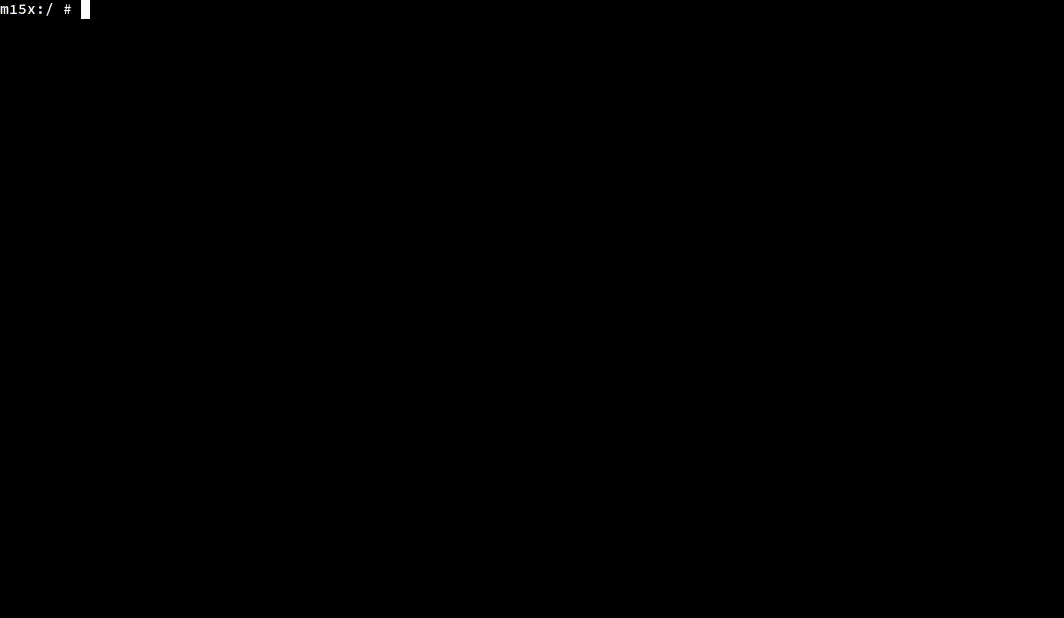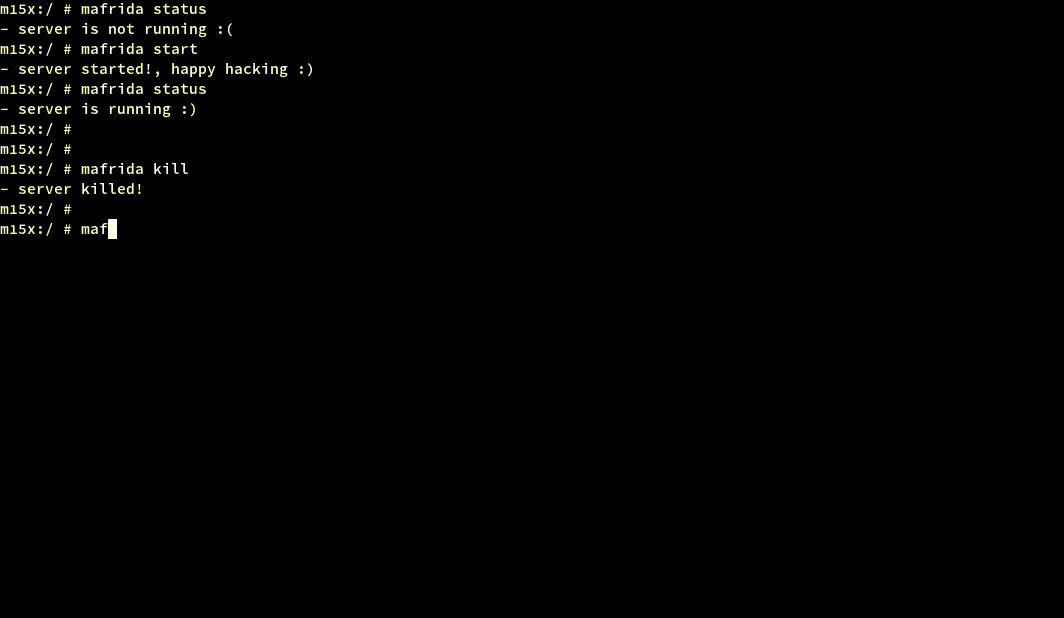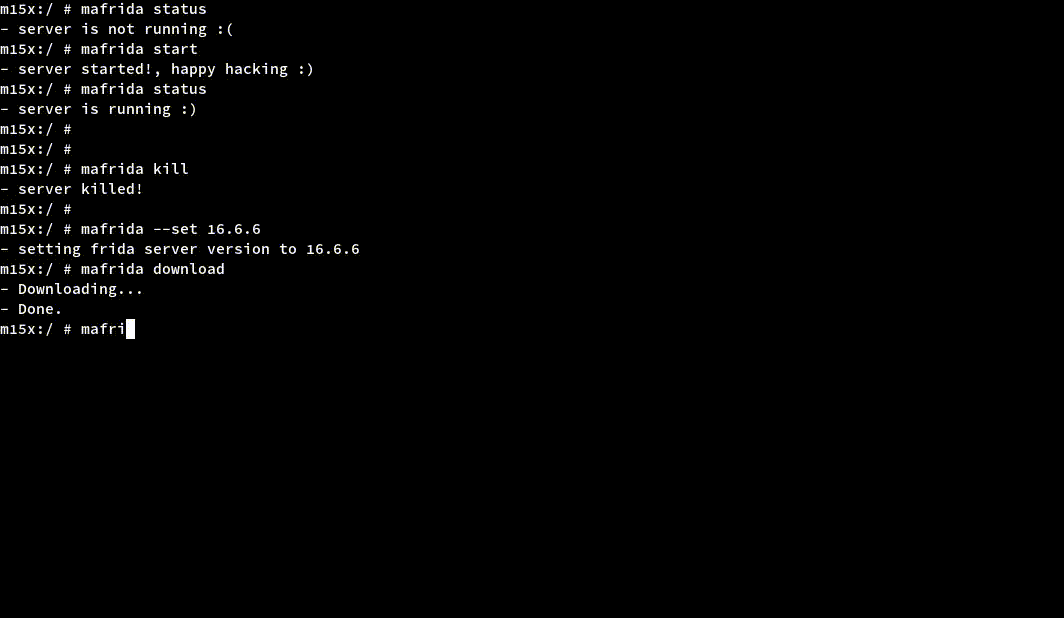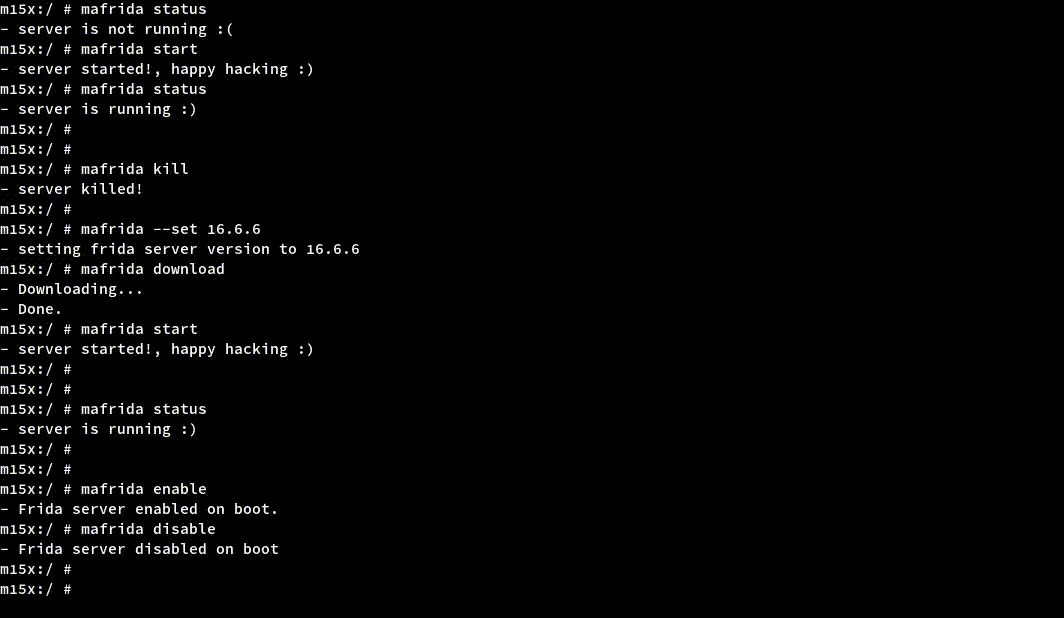
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…

Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.

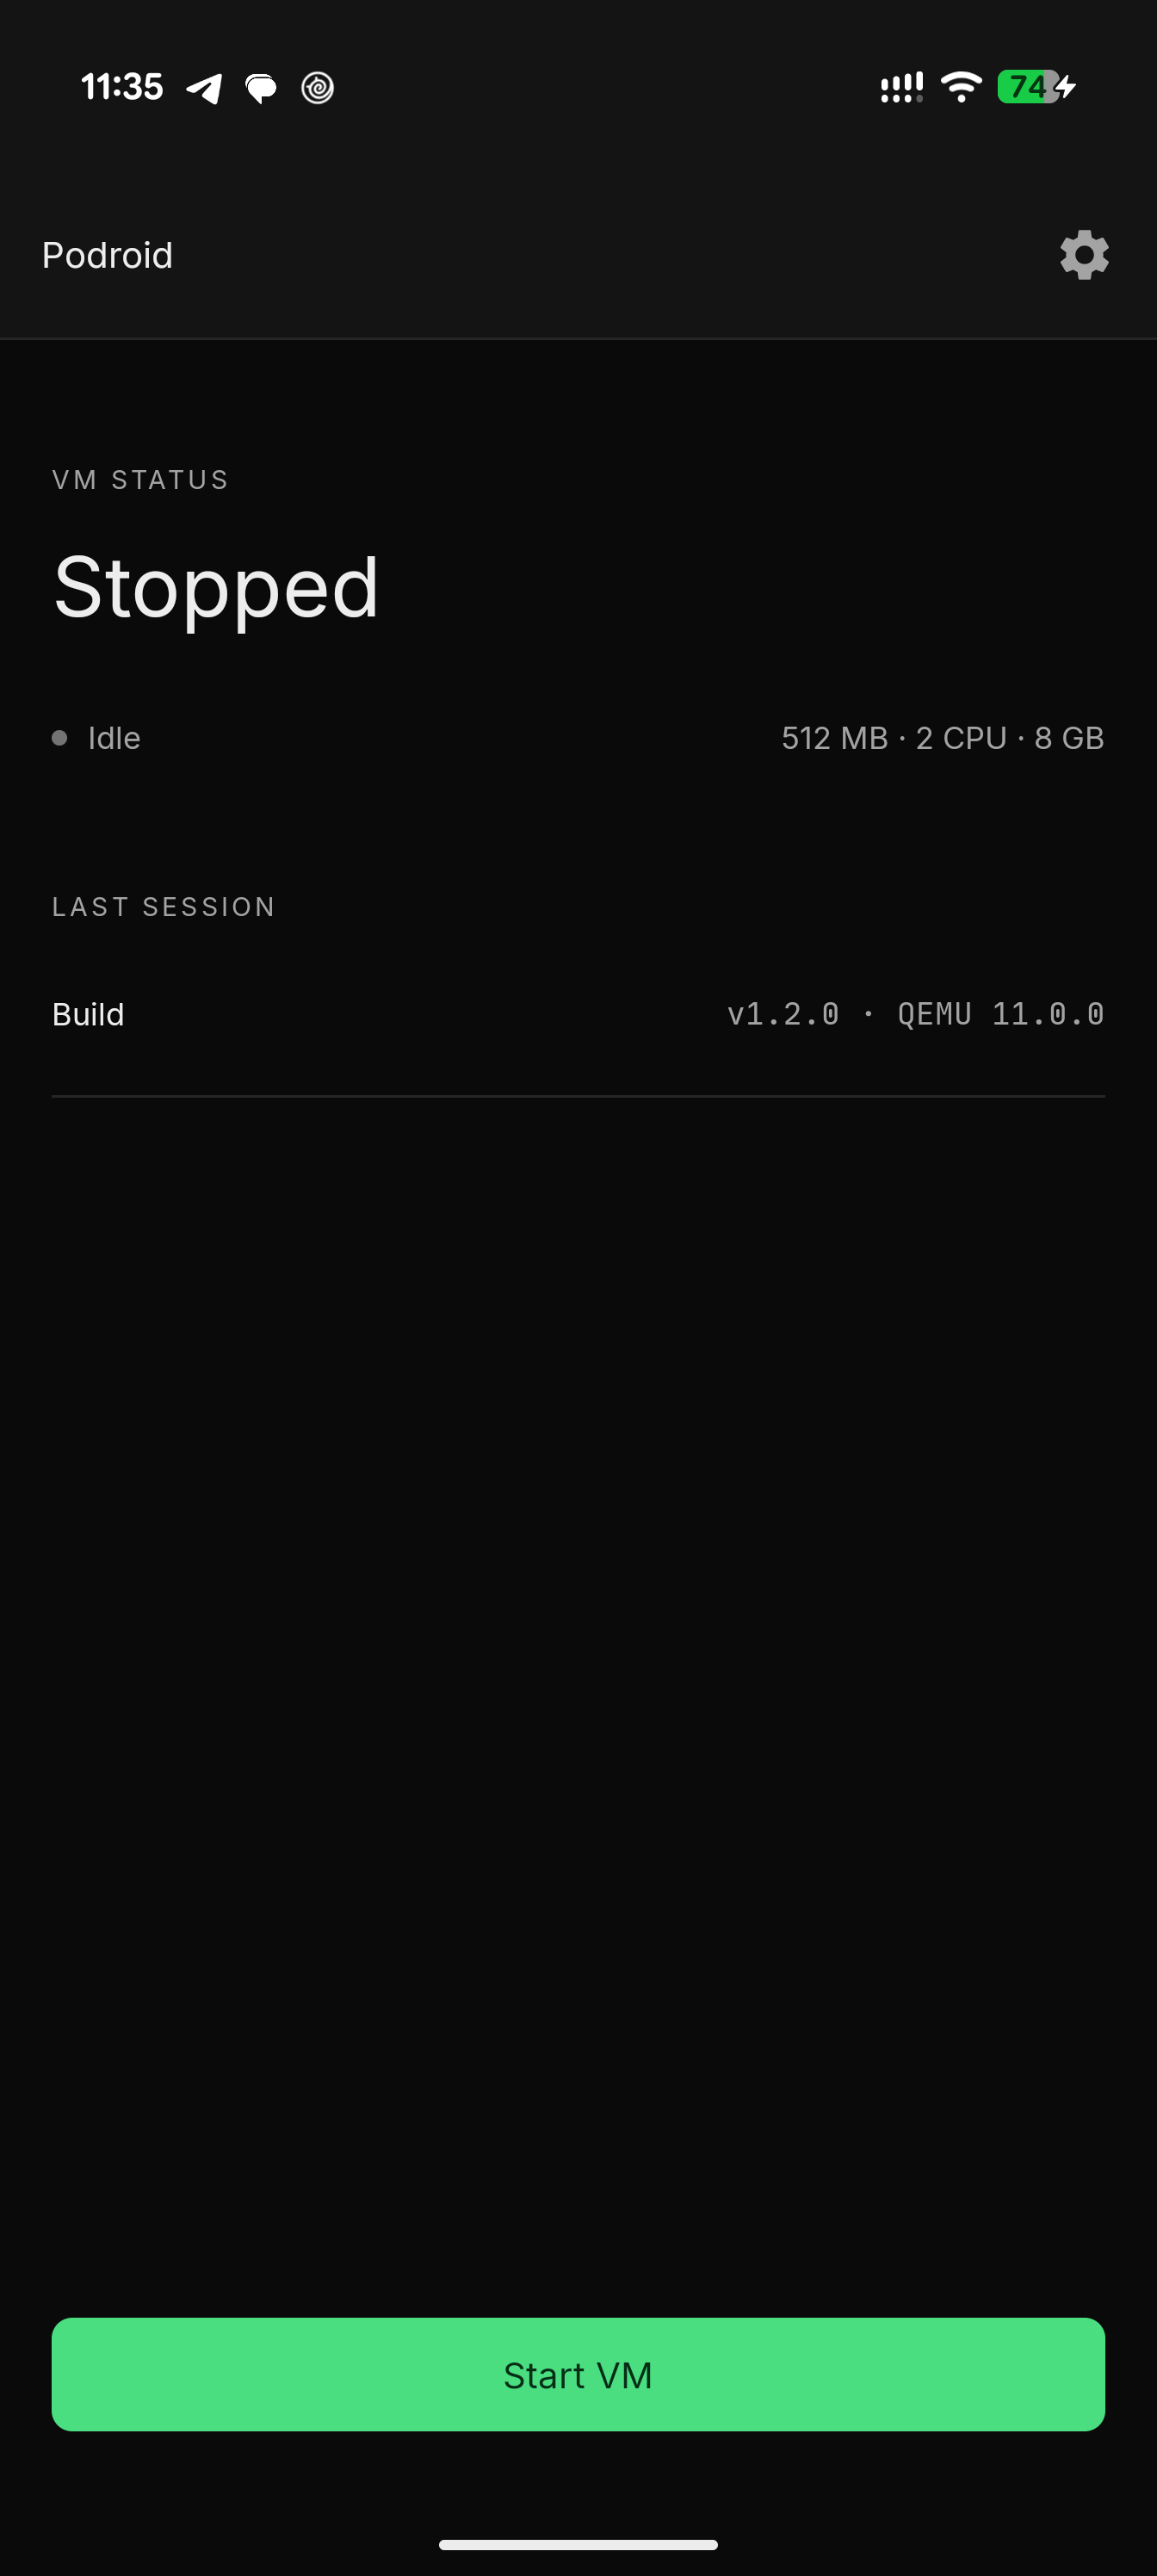
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.

Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…

A native APK and DEX decompiler written in Rust

LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…

Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…

Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…