
cvedb
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
database-securityinformation-gatheringthreat-intelligence+2
25
trailofbits/cvedbCVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 vulnerscom/getsploit
Search and download public exploits from the Vulners database — online, or fully offline from a local SQLite FTS5 index.
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…
 cyberactivity/tyr
Tools collection to explore cyber security data like: * NVD CVE, CVE vendors, Cpe and CpeMatch, * Mitre CWE, CAPEC and Att&ck * Cisa (kev) data
 fan-67/local-mcp
A lightweight stdio-based MCP server for local file system operations — read, write, edit, search, exec for AI assistants. Specially optimized for…
 datasurgeon-ds/ds-cve-plugin
A plugin for DataSurgeon that Extracts CVE Numbers From Text (e.g: CVE-2021-56789)
 dsp-testing/cve-2018-13797
Cross-platform Node.js library to retrieve MAC addresses per network interface on Linux, macOS, and Windows, with async and sync APIs.
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 vpierre/ndaal_public_sbom_auditor
Offline single-binary web app that ingests CycloneDX, SPDX and syft SBOMs, runs an ensemble of CVE scanners, enriches findings with EPSS, CISA-KEV…
 alvm/php2shell-eol-backport
Unofficial fix for CVE-2026-109618 / CVE-2026-109619 (php2shell) for the end-of-life PHP 5.4 / 5.3 packages of RHEL, CentOS and Oracle Linux 7 / 6
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 owasp/cwe-sdk-javascript
A Common Weakness Enumeration (CWE) Node.js SDK compliant with MITRE / CAPEC
 daehee/nvd
Fast, simple library in Go to fetch CVEs from the National Vulnerability Database feeds
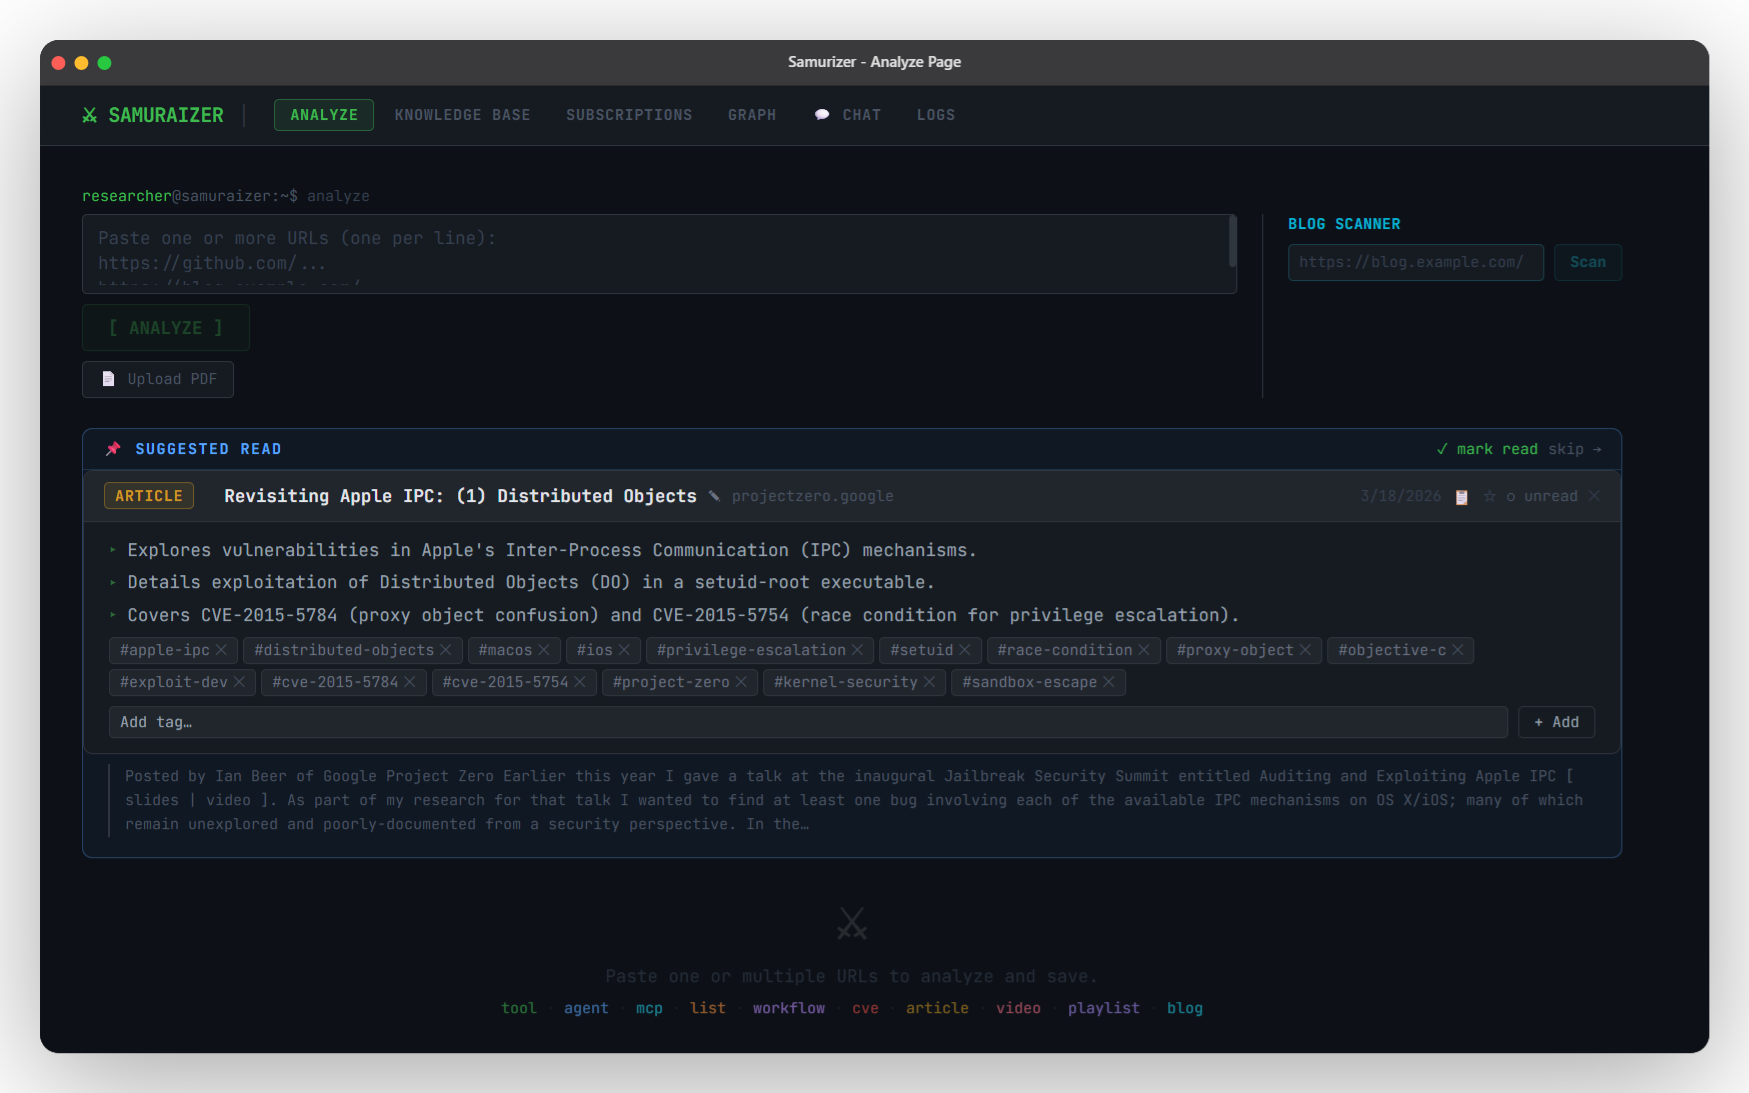 zomry1/samuraizer
NotebookLM on steroids — purpose-built for security researchers.