

HaE
 overspace-labs/hae
Modular Burp Suite extension for fine-grained highlighting and extraction of sensitive data from HTTP and WebSocket traffic, enabling efficient…
information-gatheringutilities-frameworksweb-security
overspace-labs/haeModular Burp Suite extension for fine-grained highlighting and extraction of sensitive data from HTTP and WebSocket traffic, enabling efficient…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
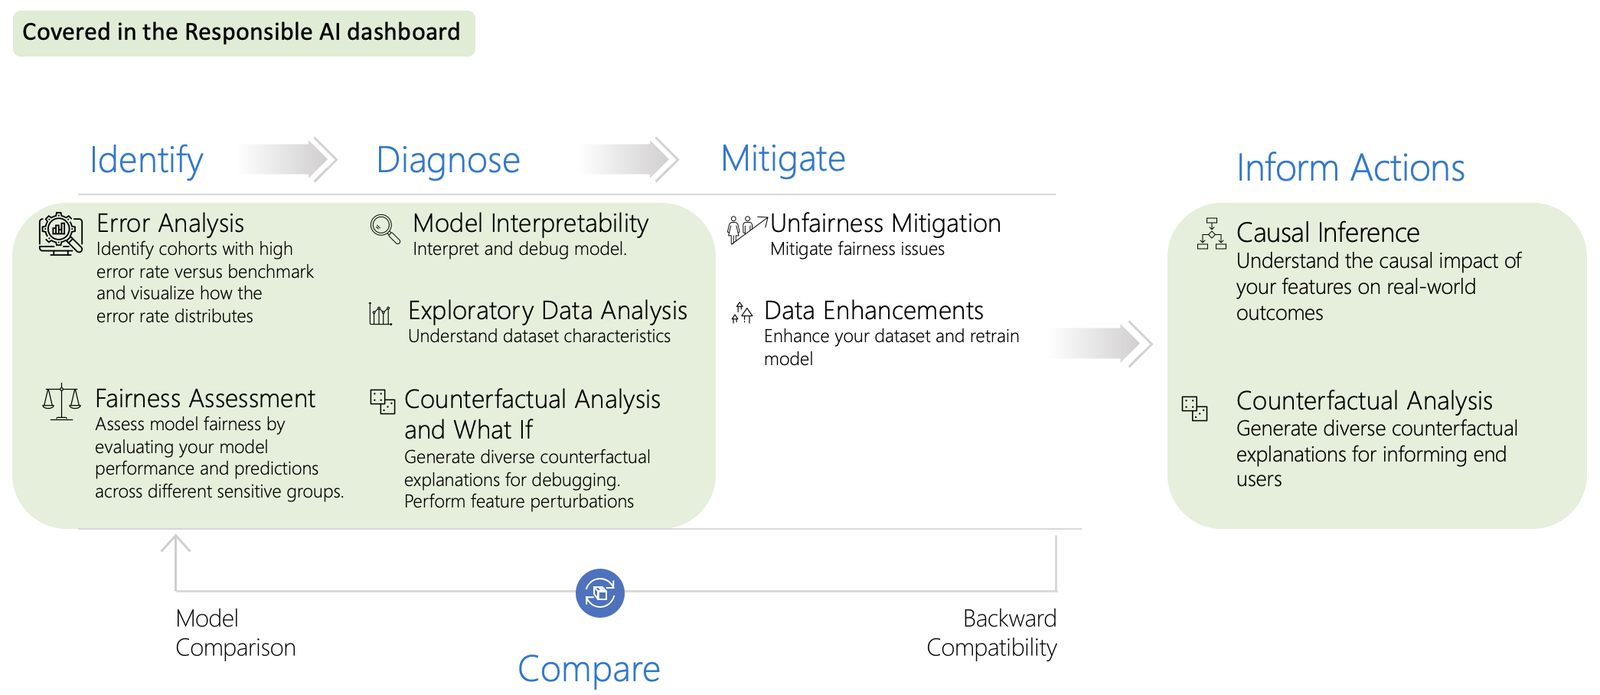 microsoft/responsible-ai-toolbox
Interactive dashboards and libraries for responsible AI model debugging, covering error analysis, fairness, interpretability, counterfactuals, causal…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 iphelix/pack
PACK (Password Analysis and Cracking Kit)
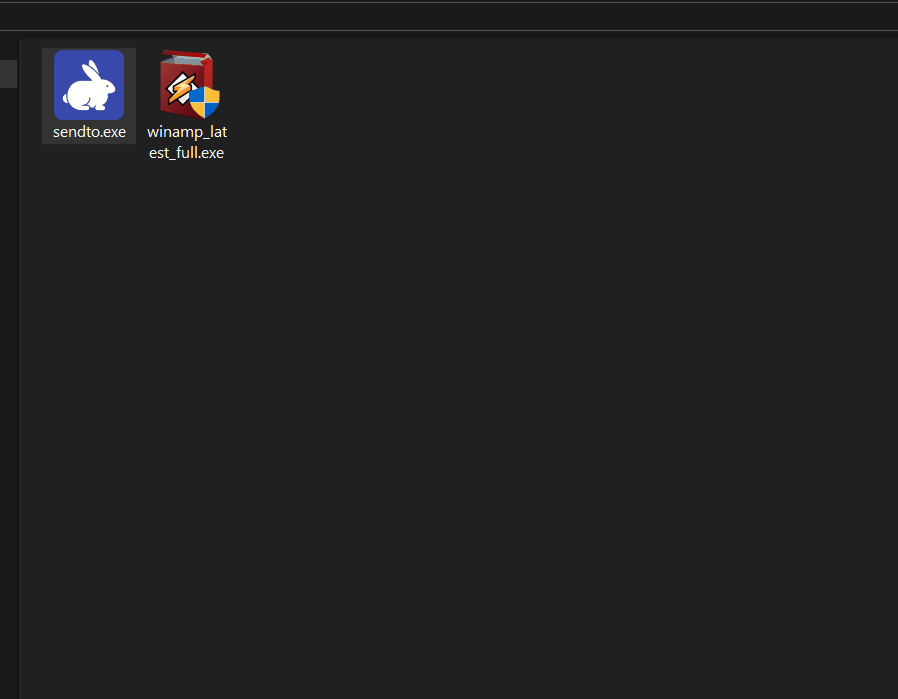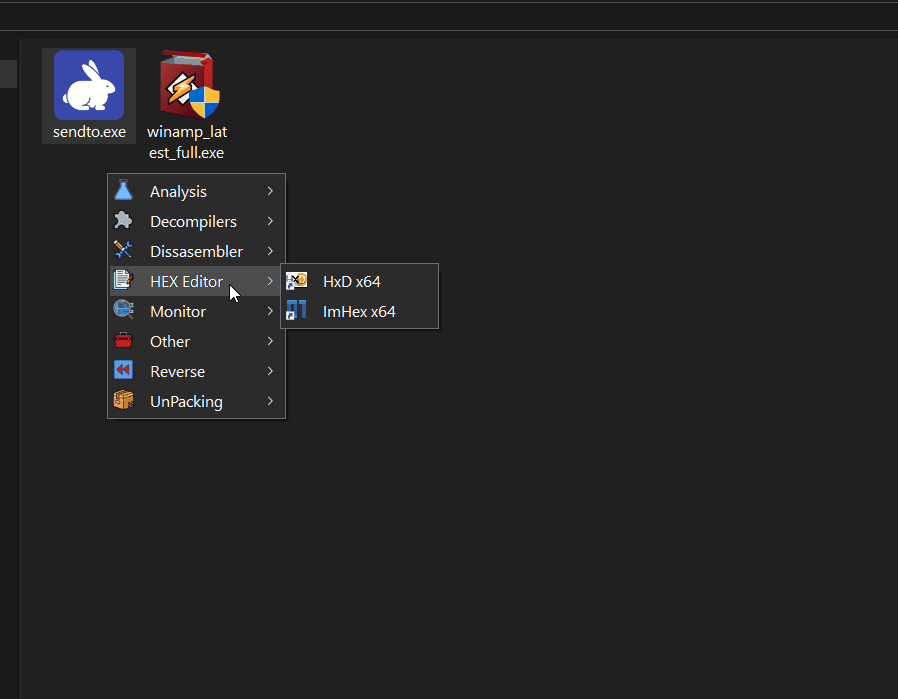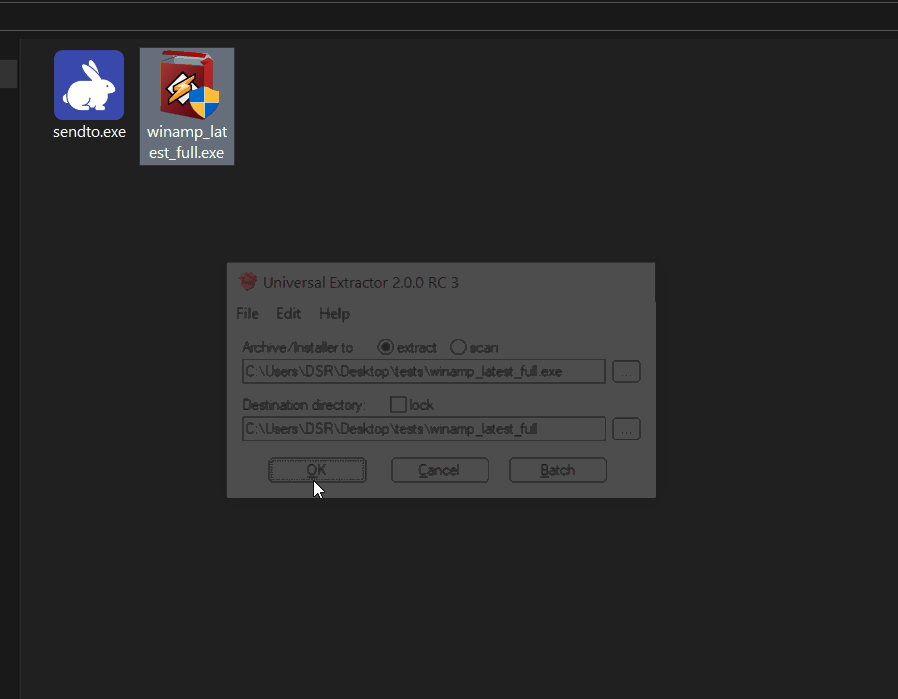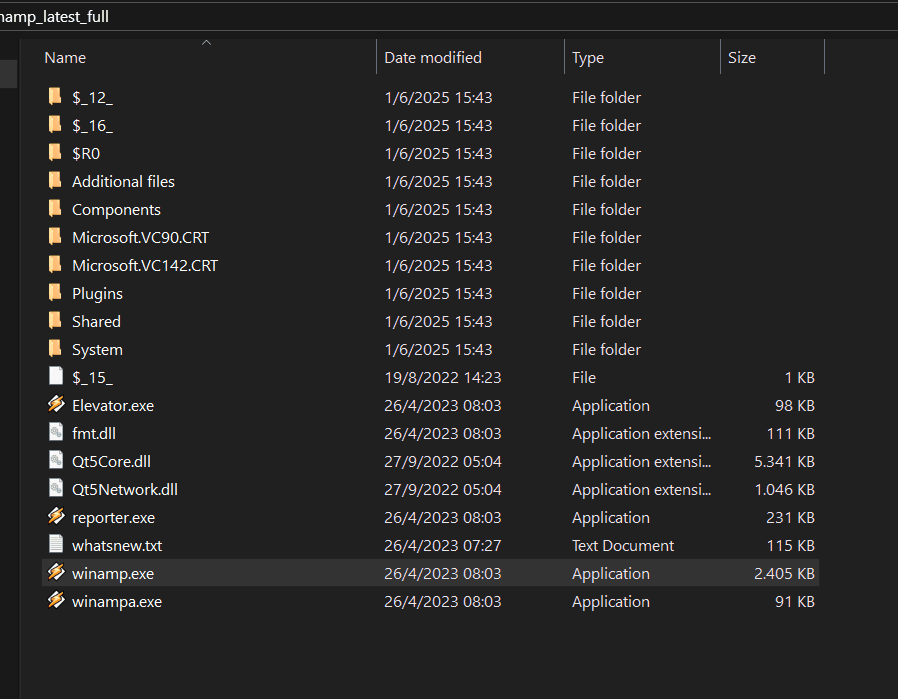 indetectables-net/toolkit
Curated Windows toolkit for reverse engineering, malware analysis, and password cracking. Includes 101 pre-configured tools with automatic updates…
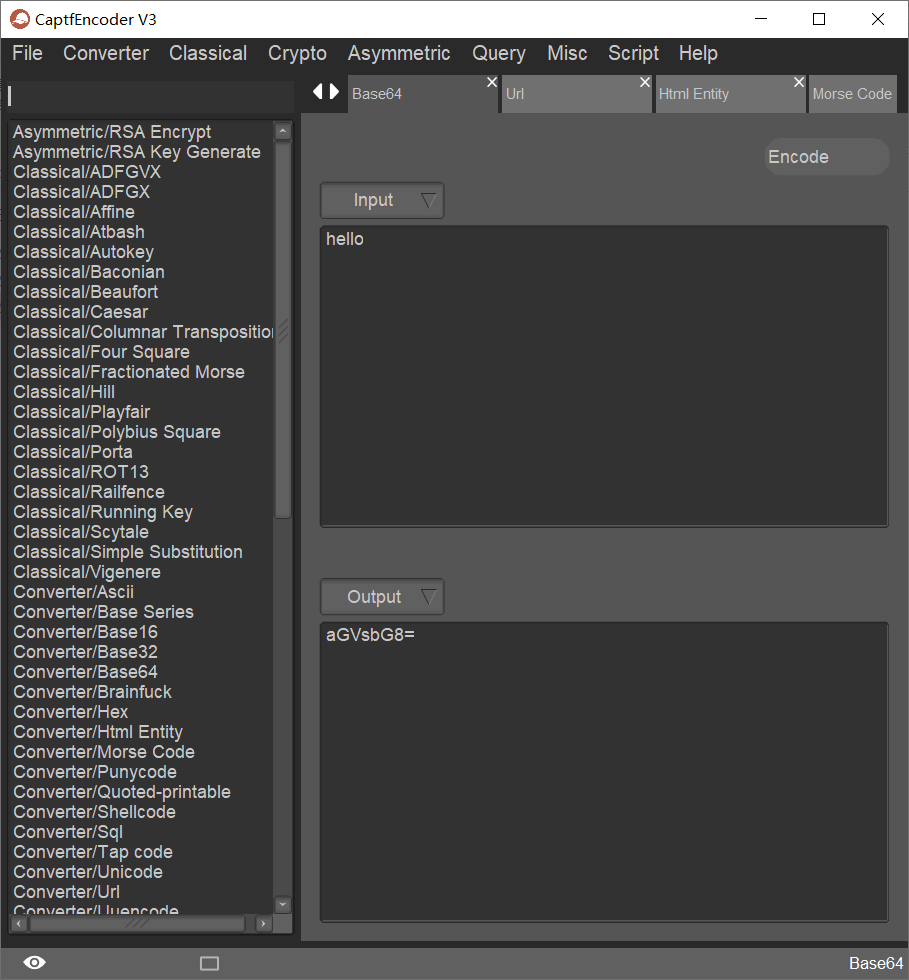 guyoung/captfencoder
Cross-platform security toolkit for encoding, classical and modern cryptography, hash computation, and online reconnaissance queries, designed for…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 therealsaumil/static-arm-bins
Statically compiled ARM binaries for debugging and runtime analysis
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 rosesecurity/scrappy
Python utility that scrapes PDFs to generate targeted wordlists for brute force, forced browsing, and dictionary attacks, with word frequency,…
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
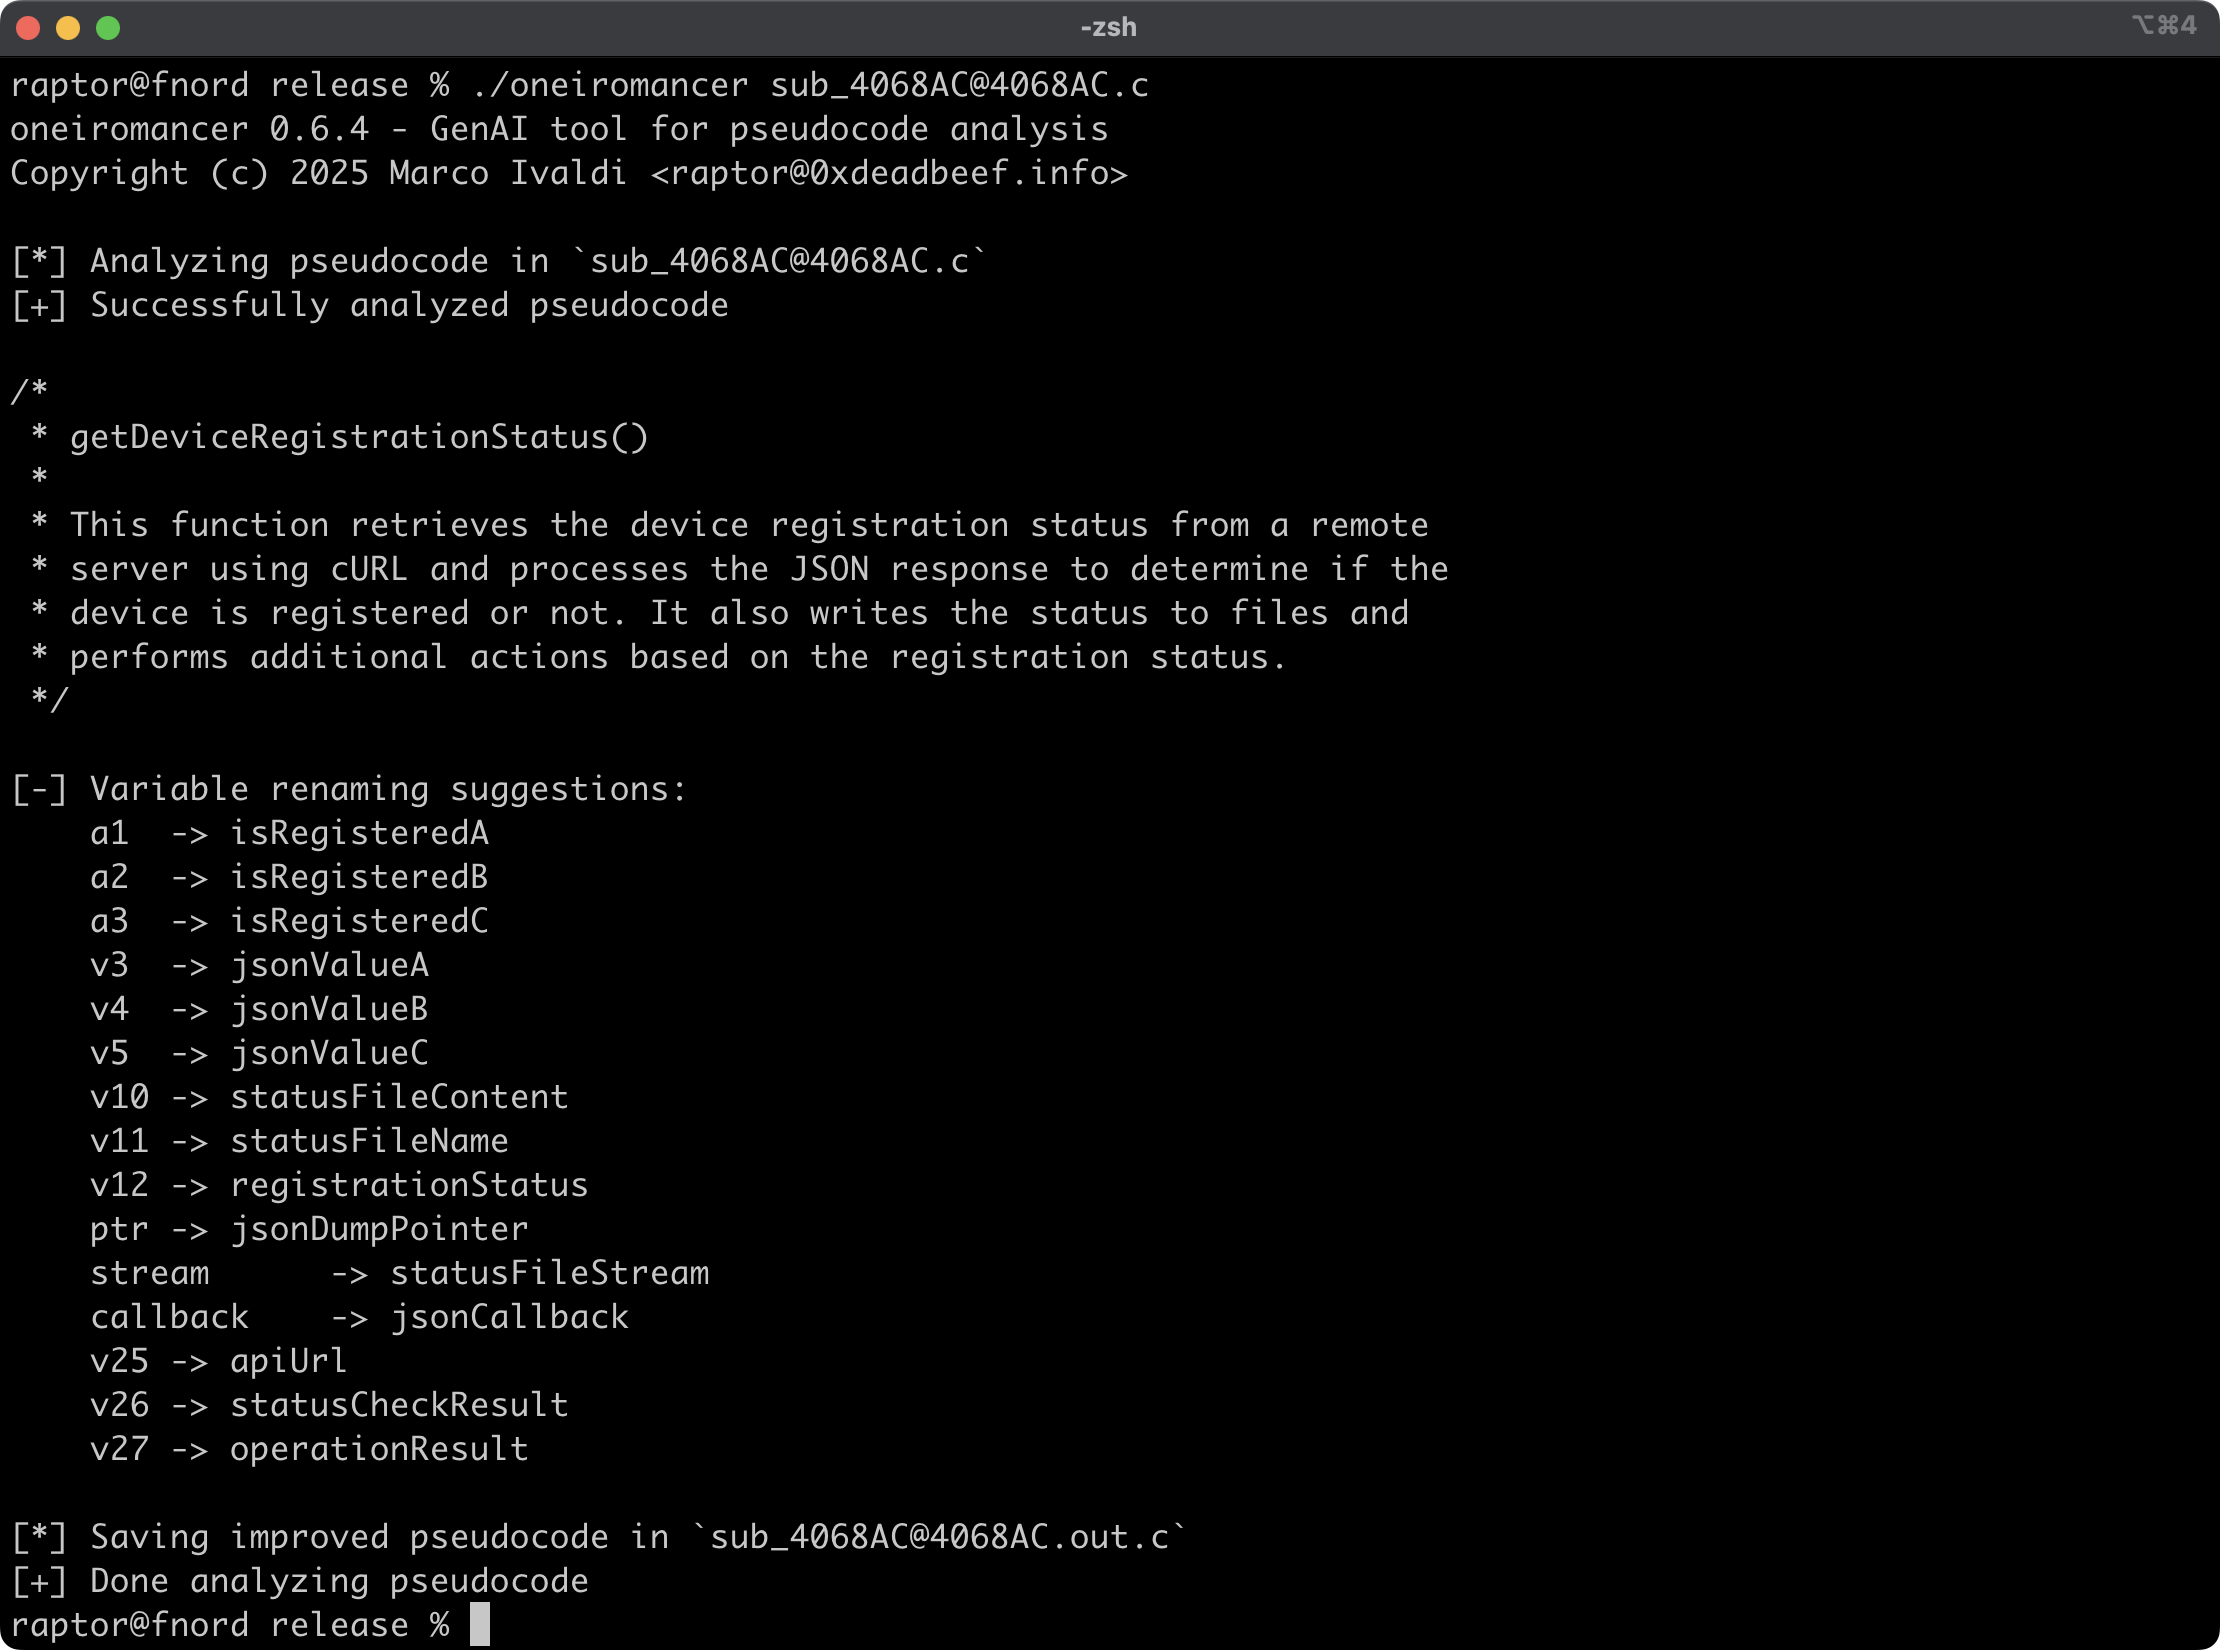 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 llvmparty/striga
Experimental x86-64 to LLVM IR lifter in Python that translates machine code into analyzable IR for reverse engineering, optimization, and VM handler…