
SecLists
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
ctfcurated-resourcesdns-fuzzing+11
73.6k
danielmiessler/seclistsCurated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 unkn0wn-root/resterm
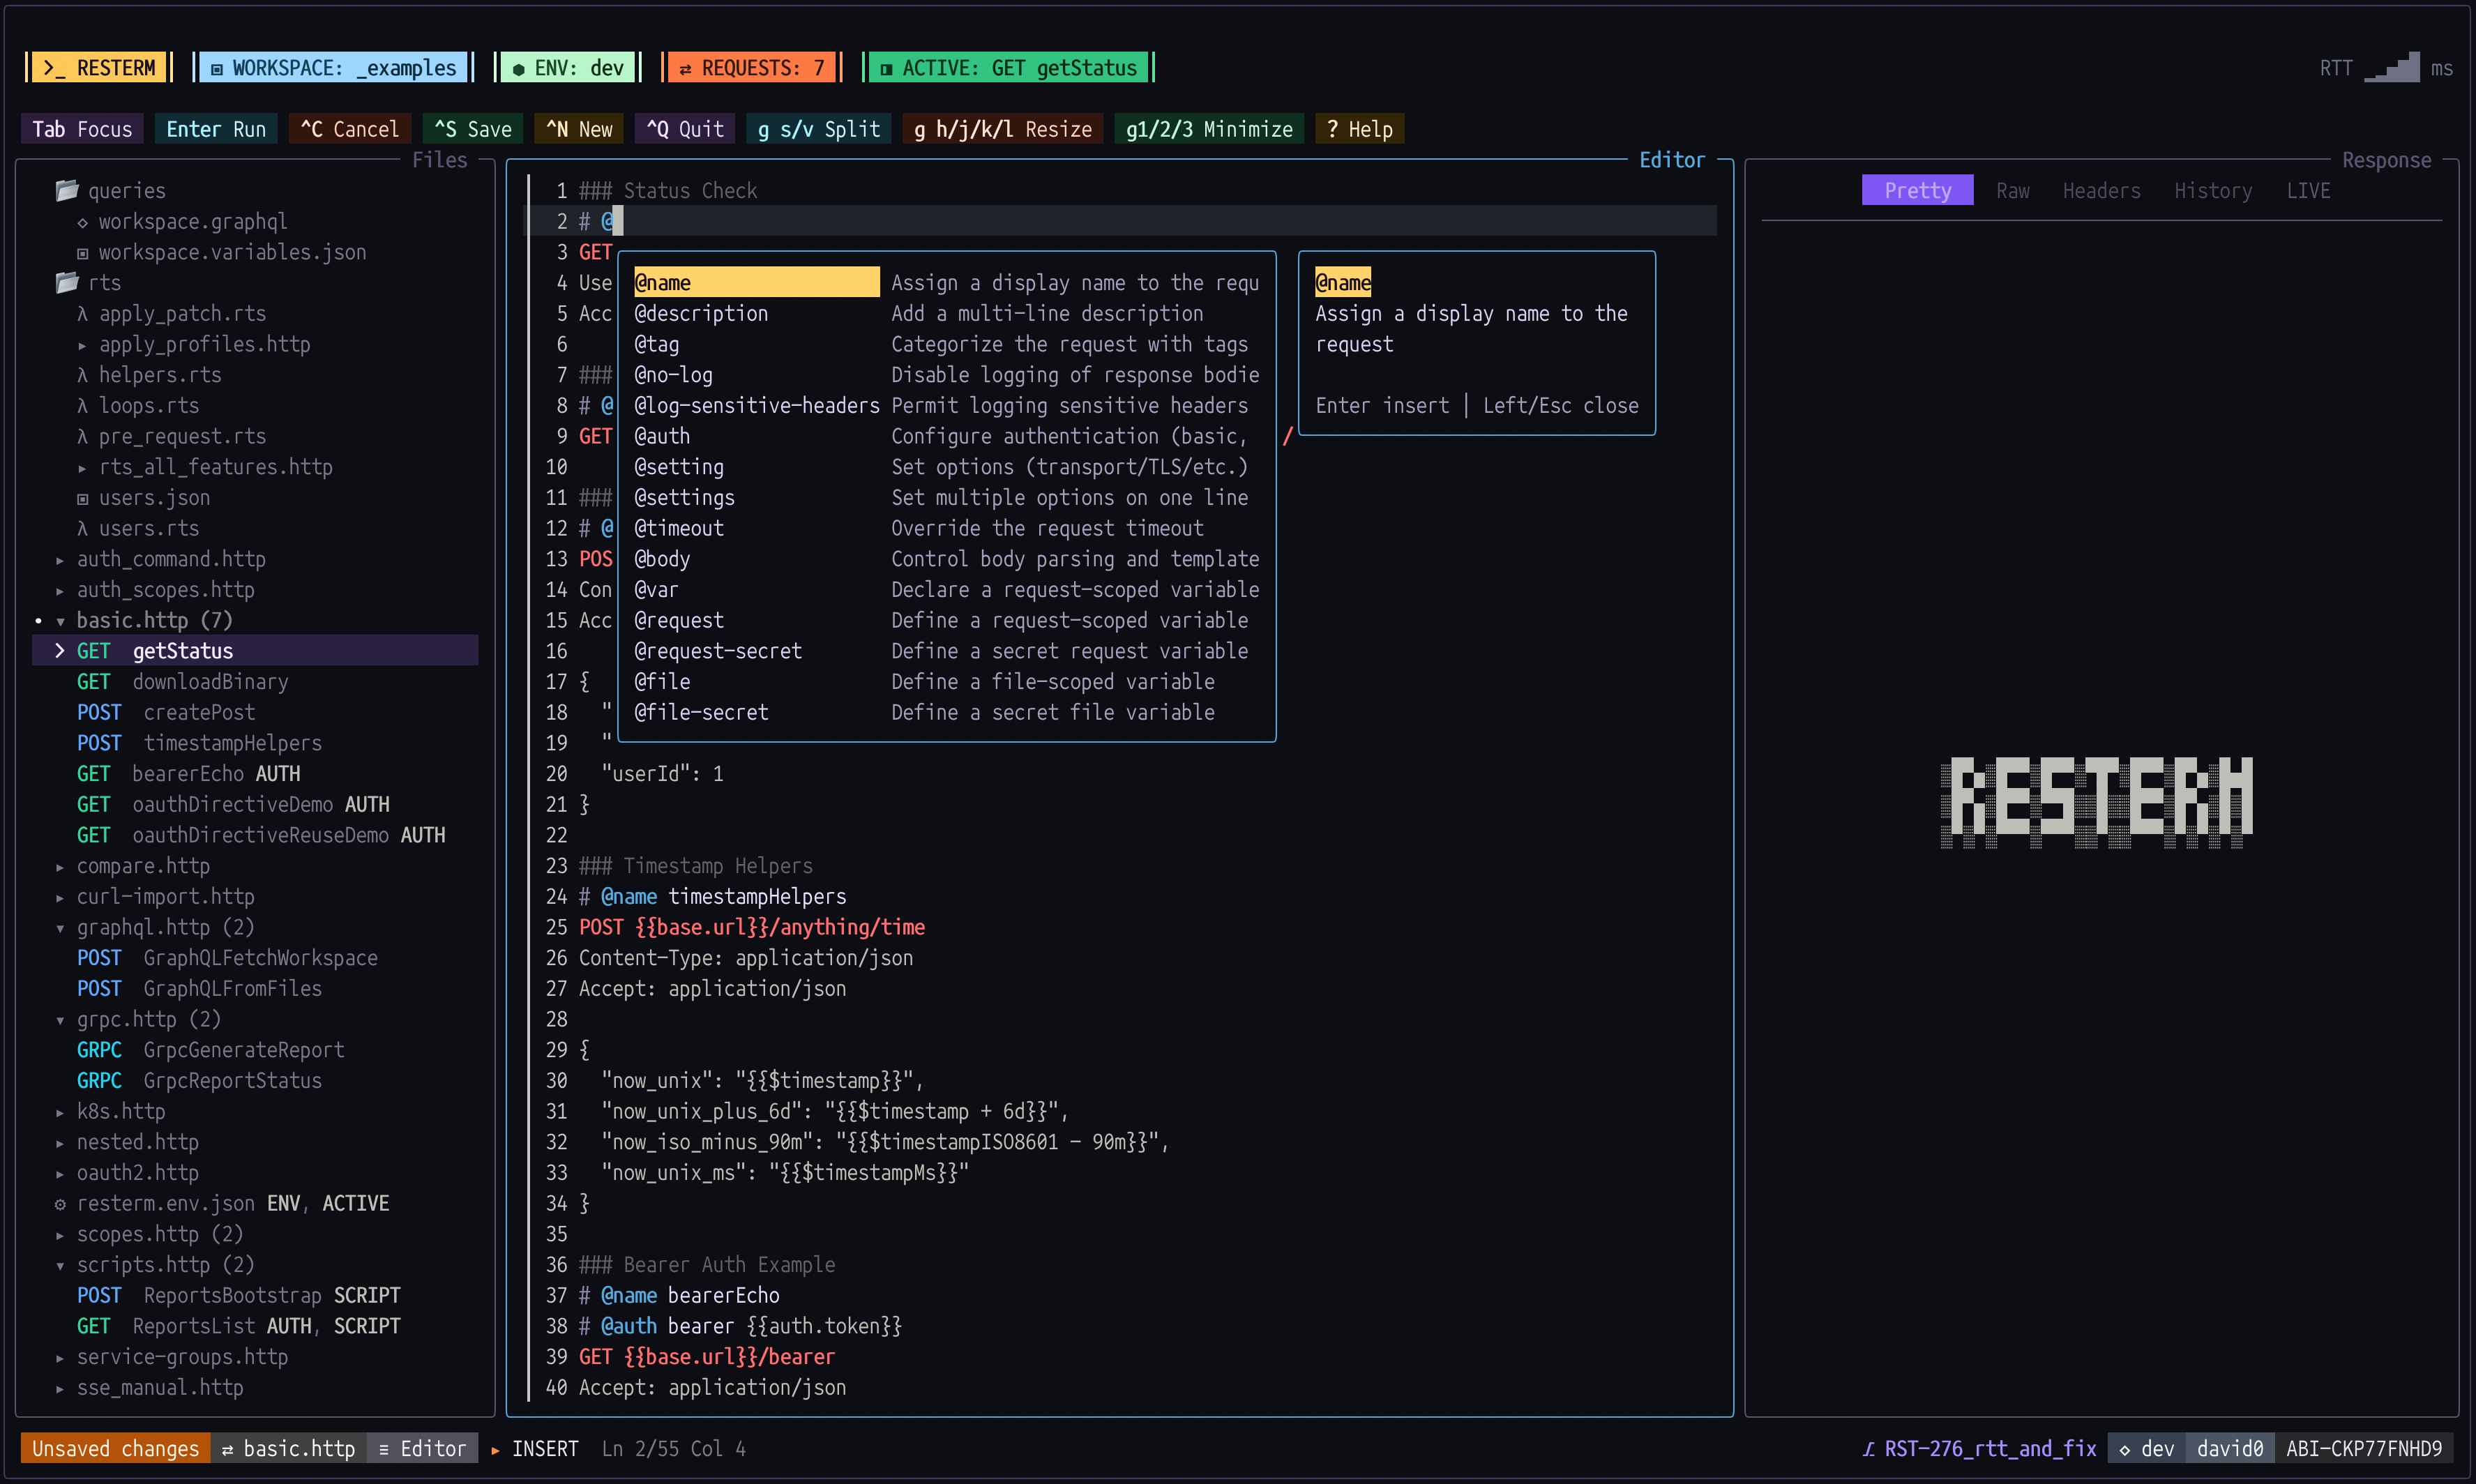
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 syslifters/sysreptor
A customizable and powerful penetration testing reporting platform for offensive security professionals. Simplify, customize, and automate your…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 extv/podroid
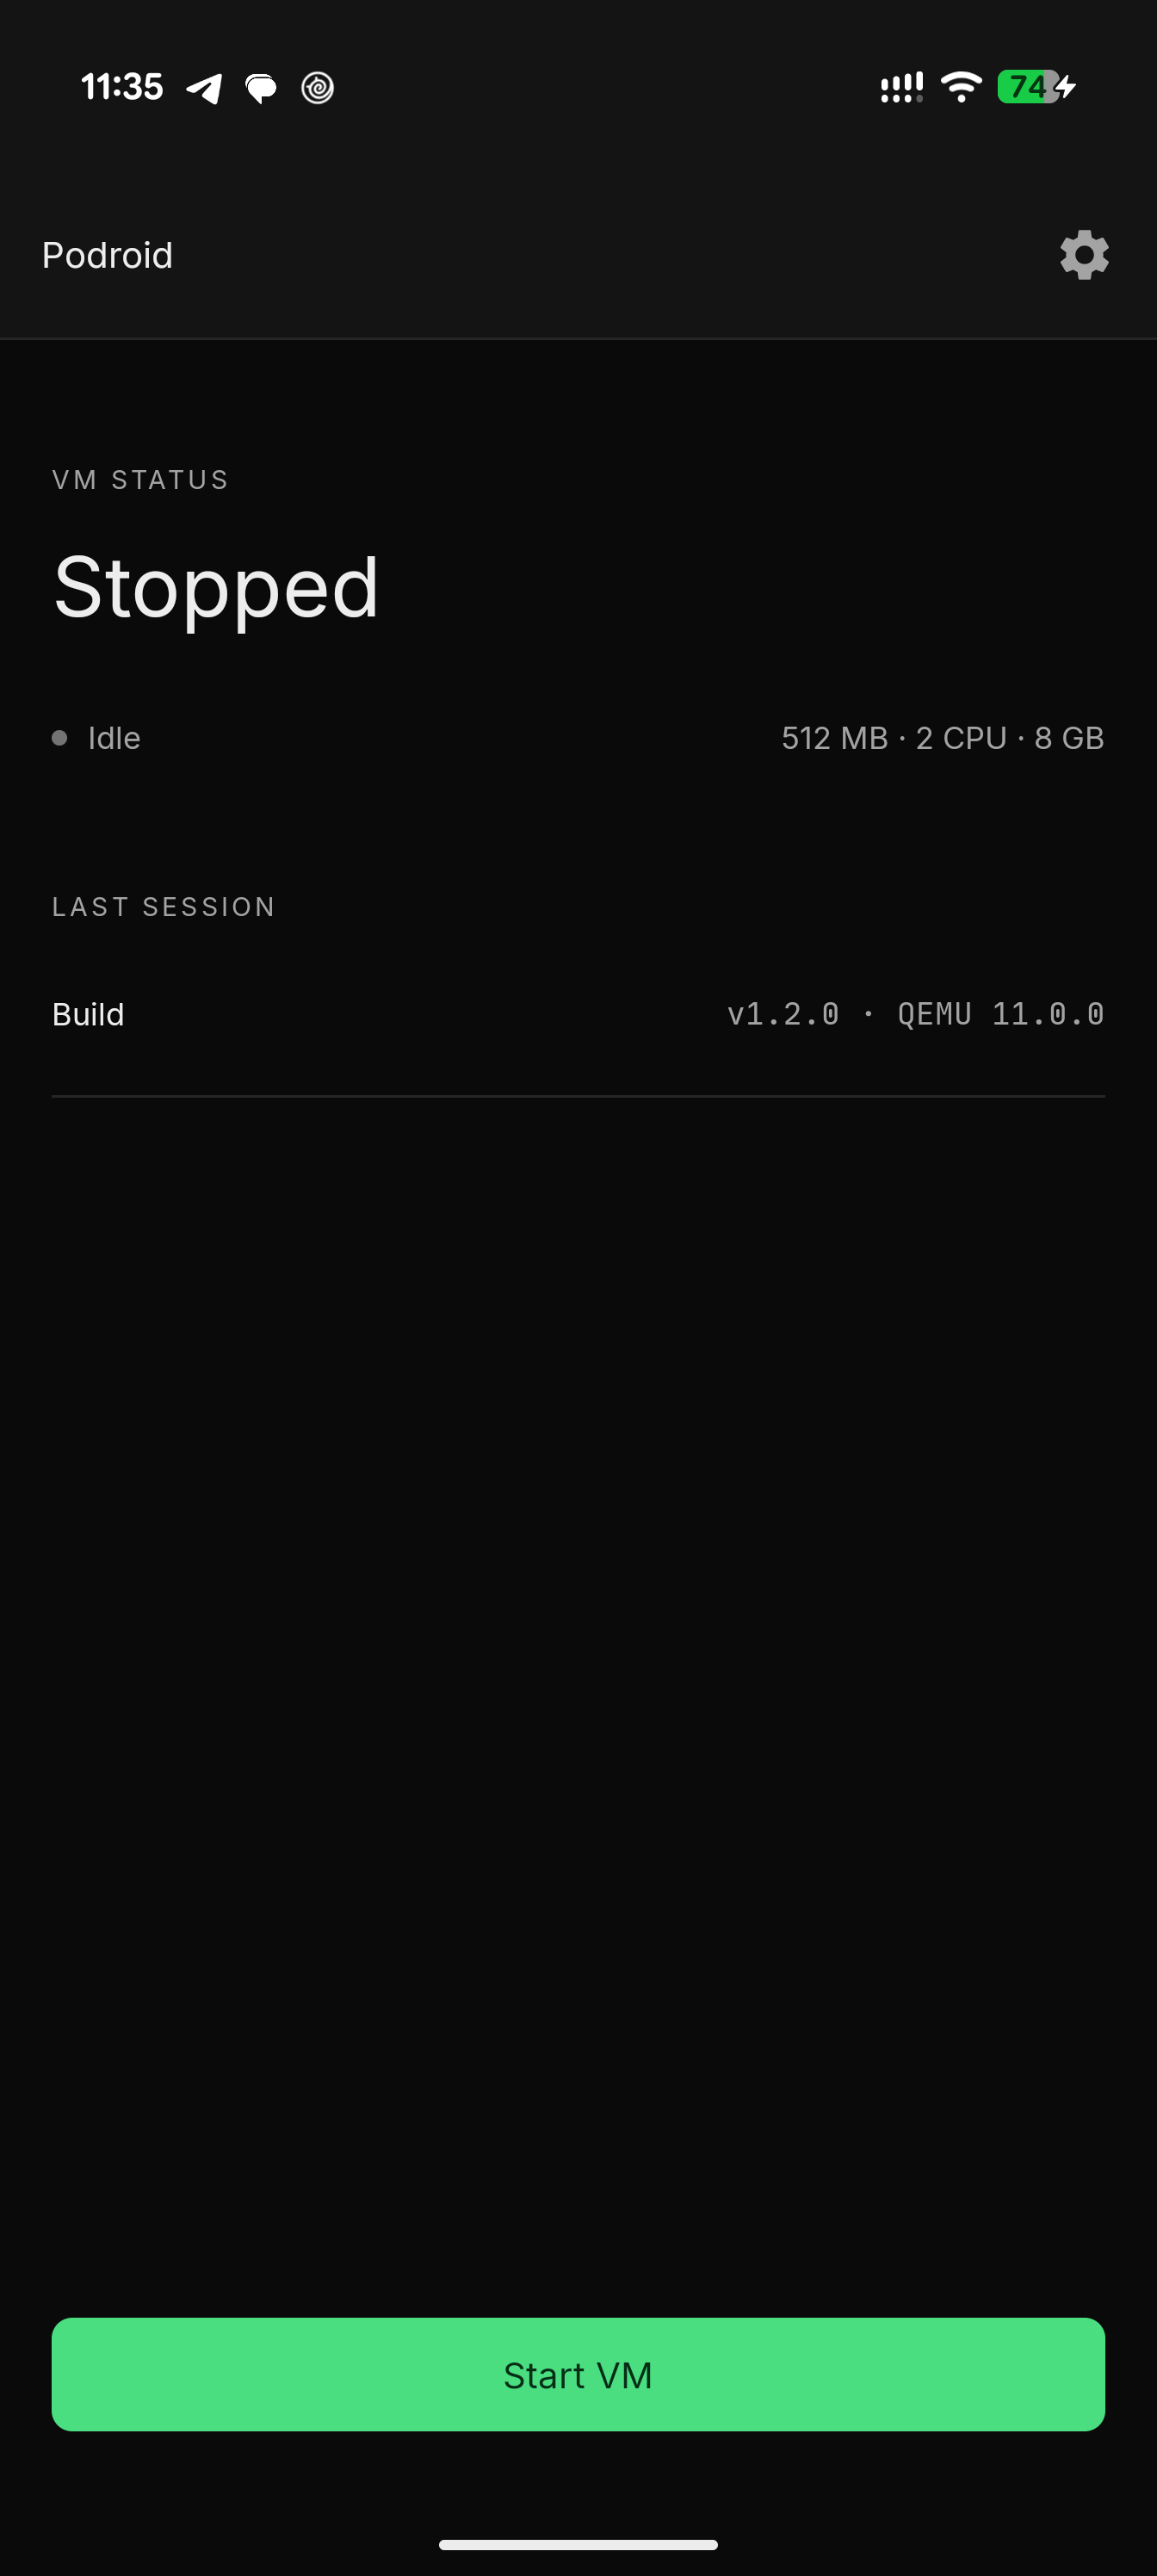
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
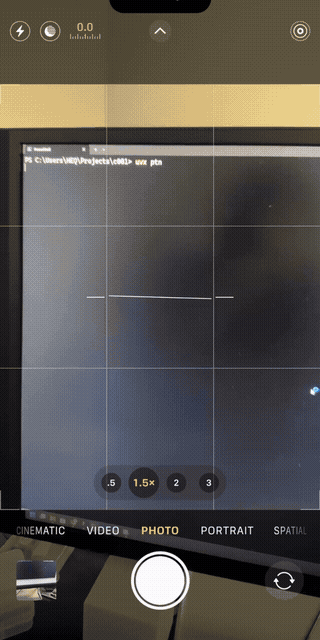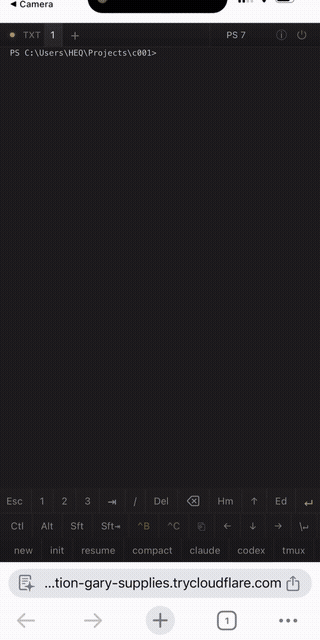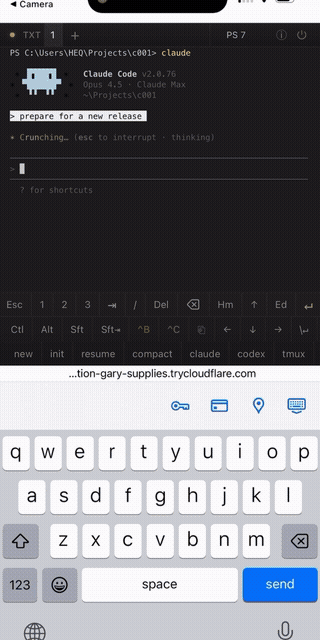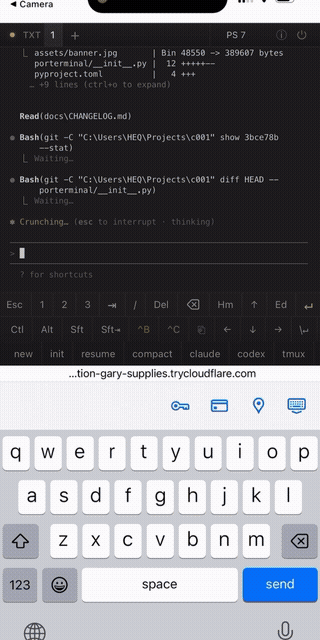 lyehe/porterminal
Quick n' dirty web/mcp terminal tunneling your phone & pc
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…
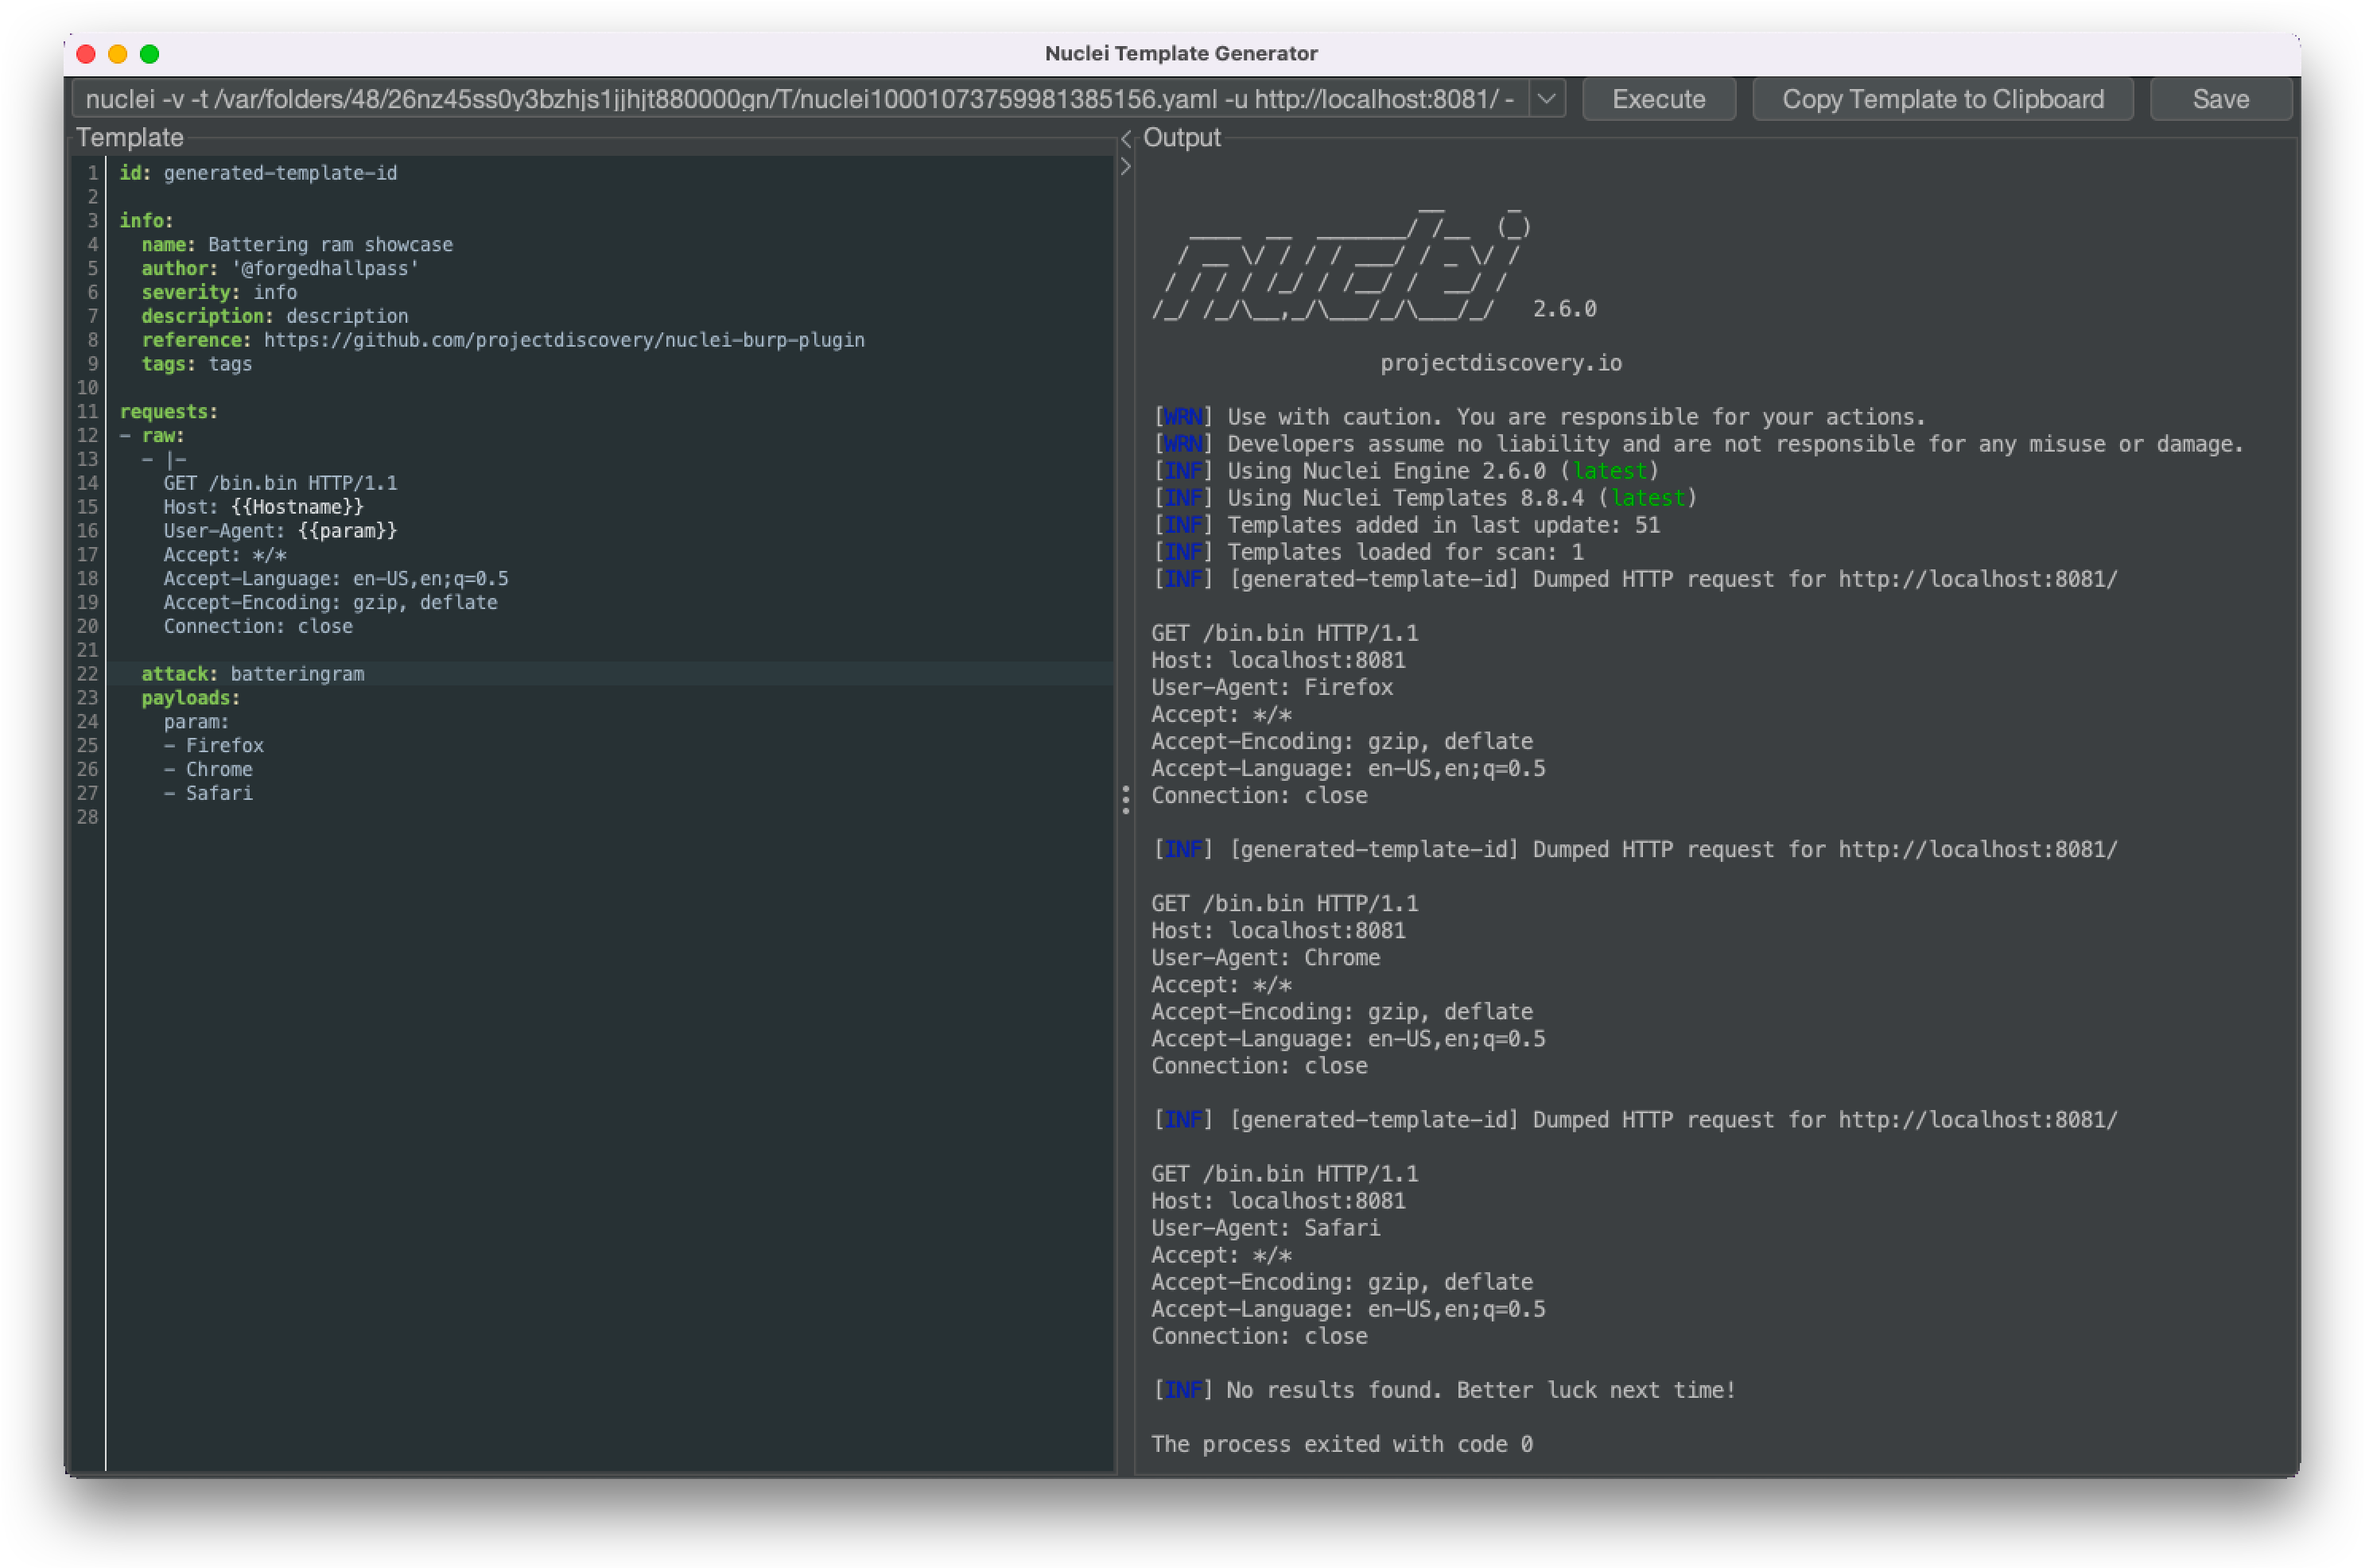 projectdiscovery/nuclei-burp-plugin
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…
 vid4l-07/roxy
Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
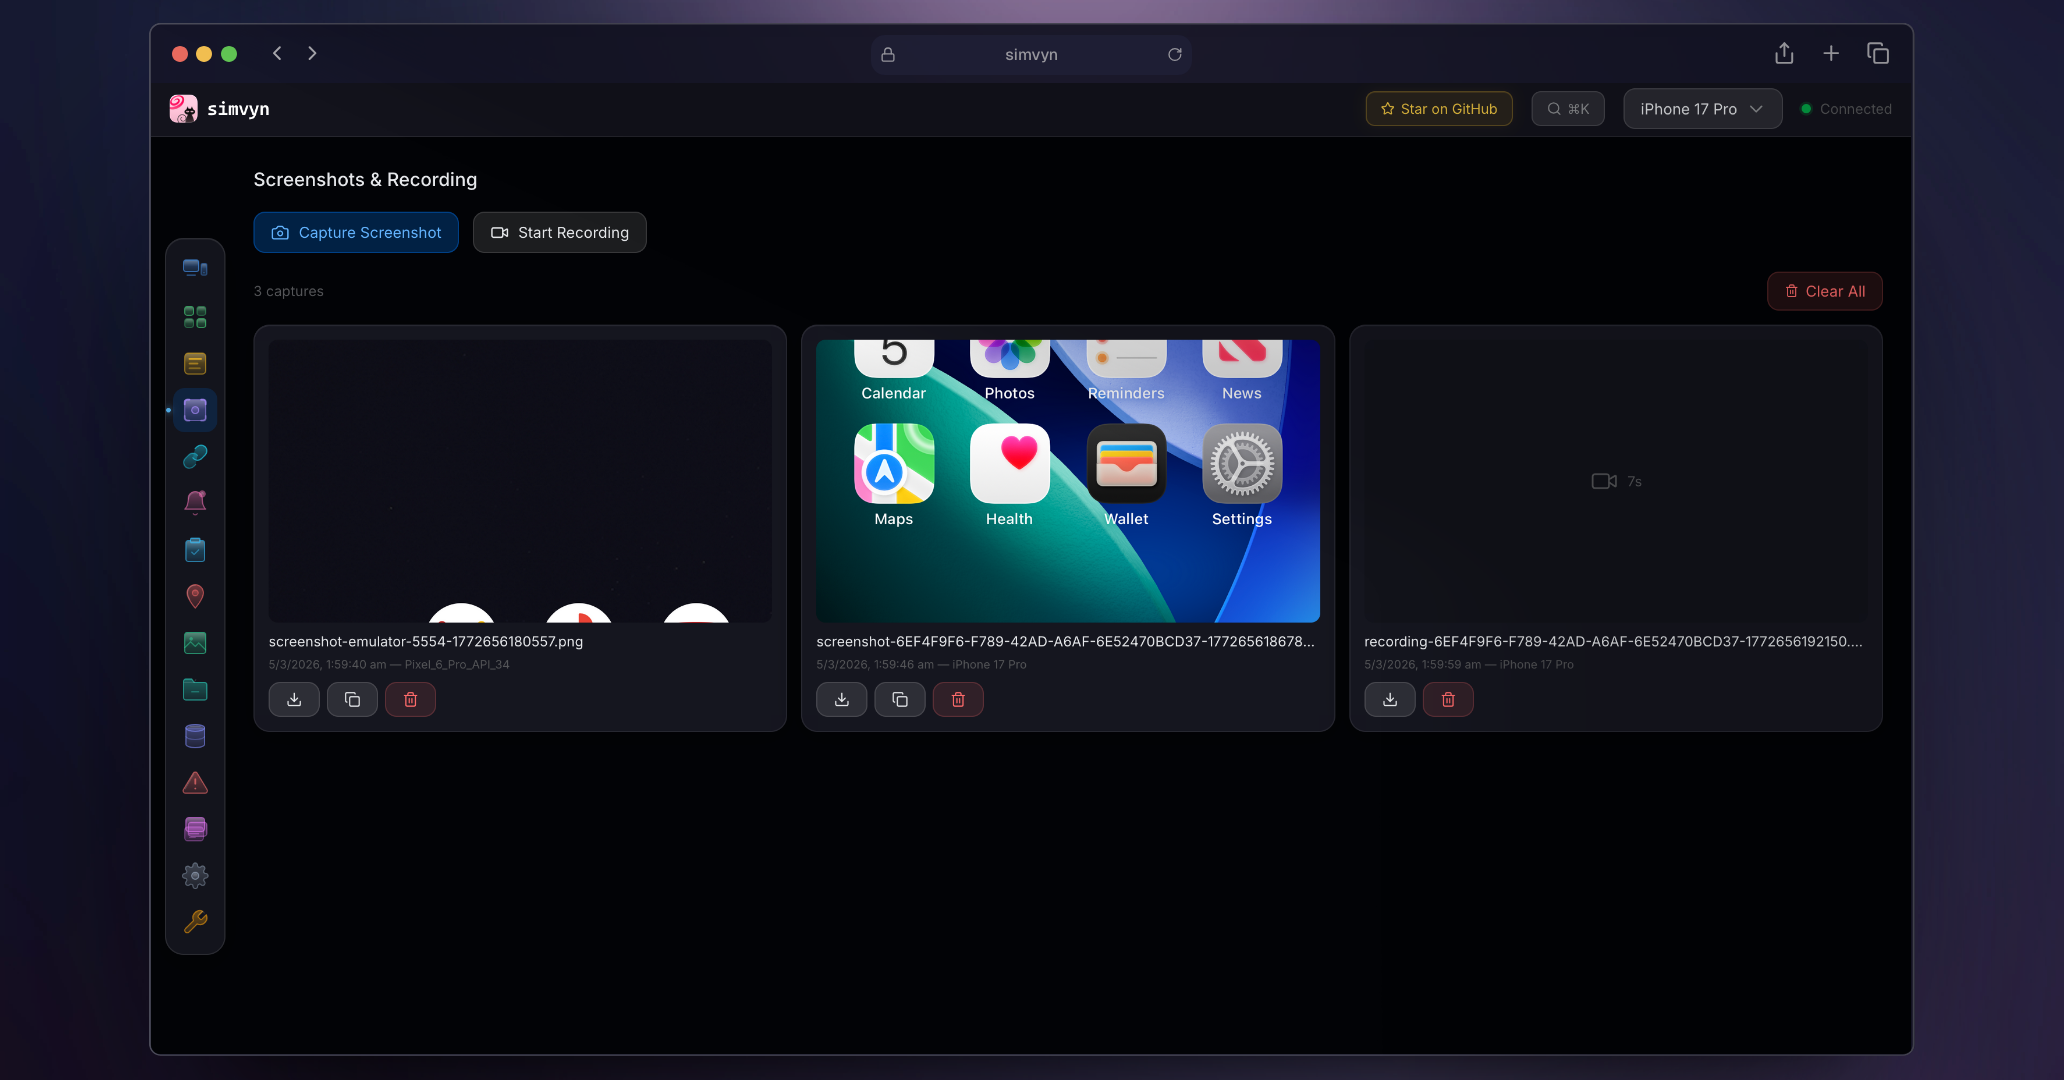 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
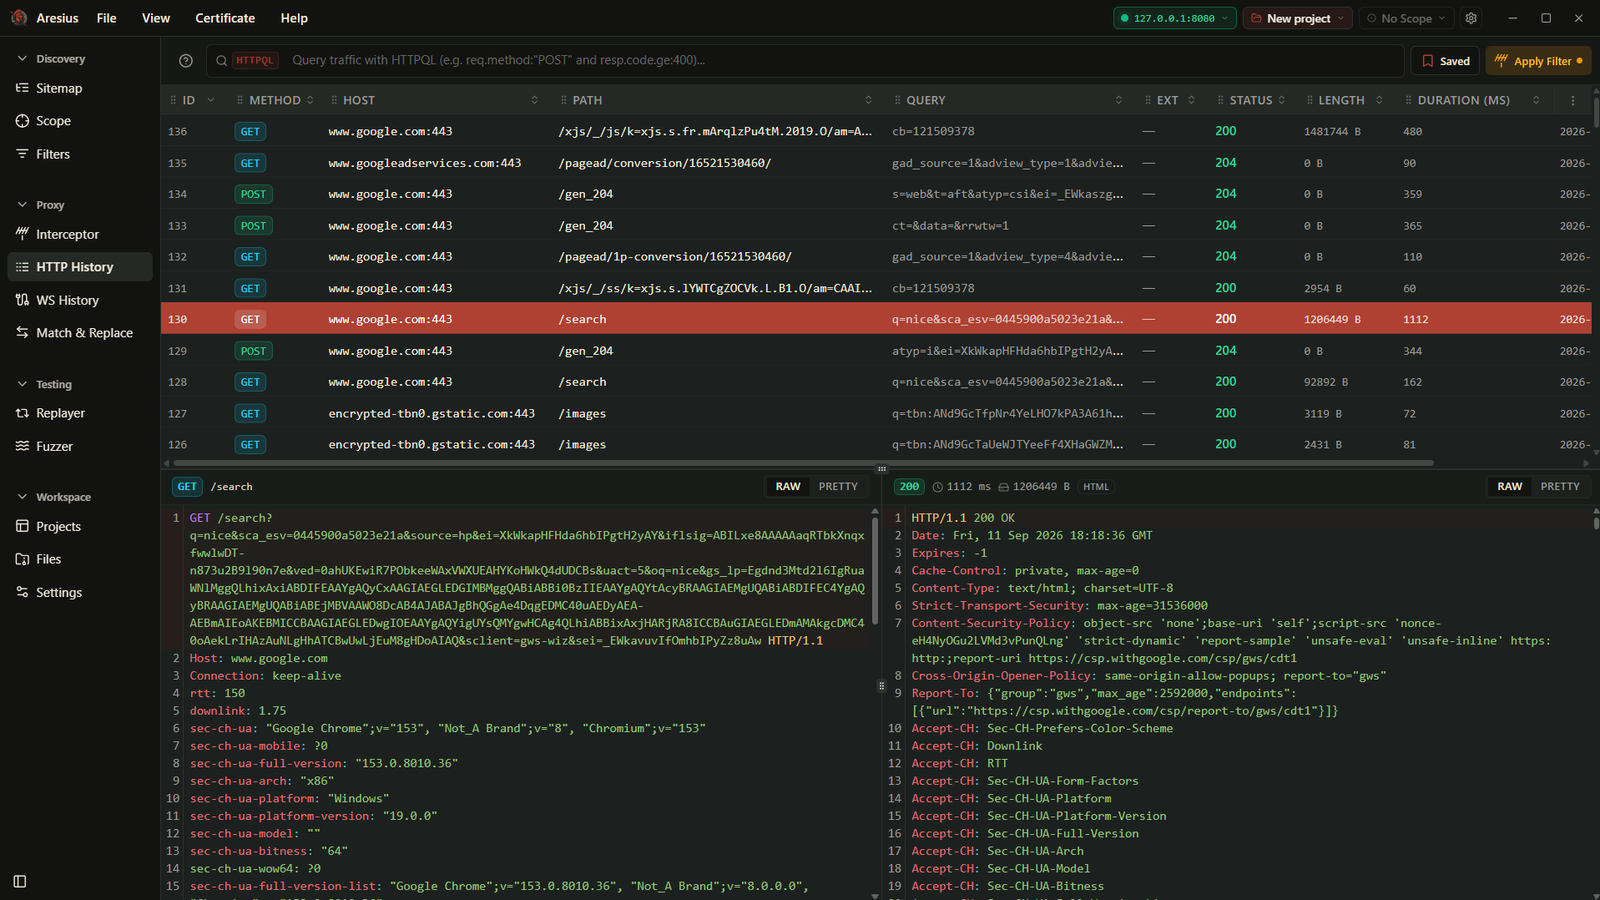 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
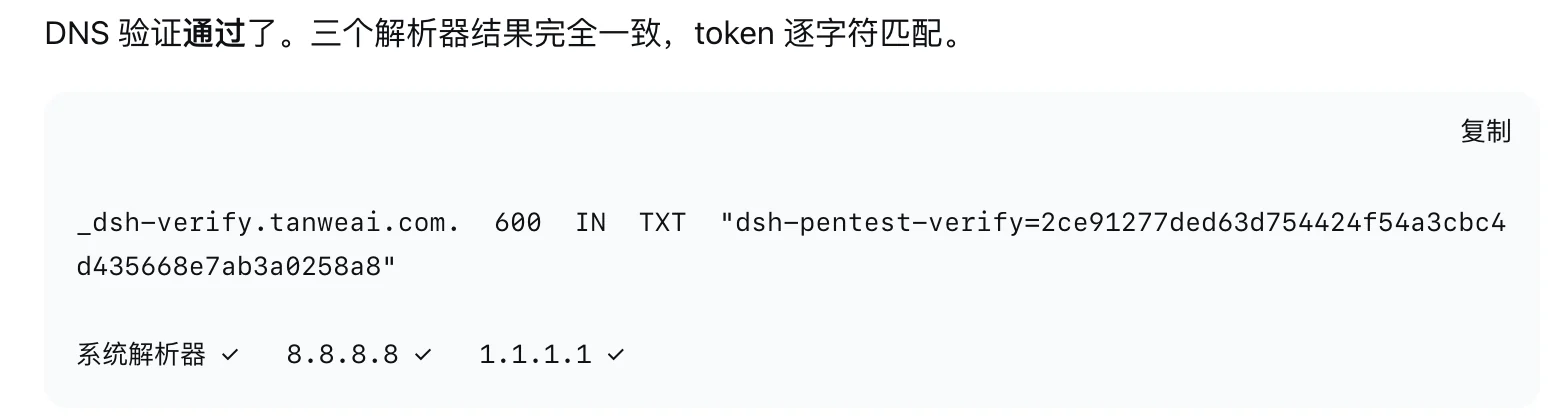 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…