

PcapPlusPlus
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
crawlerdns-analysisforensics+5
3.1k
seladb/pcapplusplusMultiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
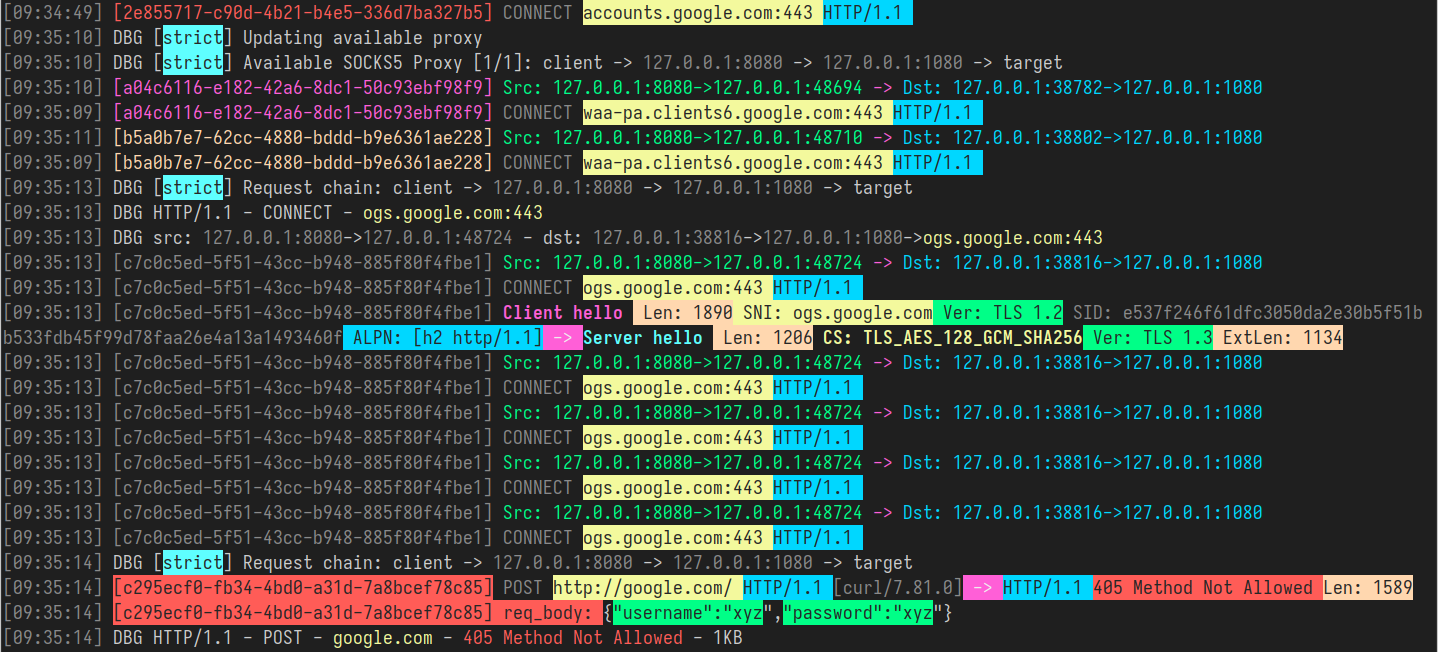 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 nmap/npcap
Nmap Project's Windows packet capture and transmission library
 mike01/pypacker
:package: The fastest and simplest packet manipulation lib for Python
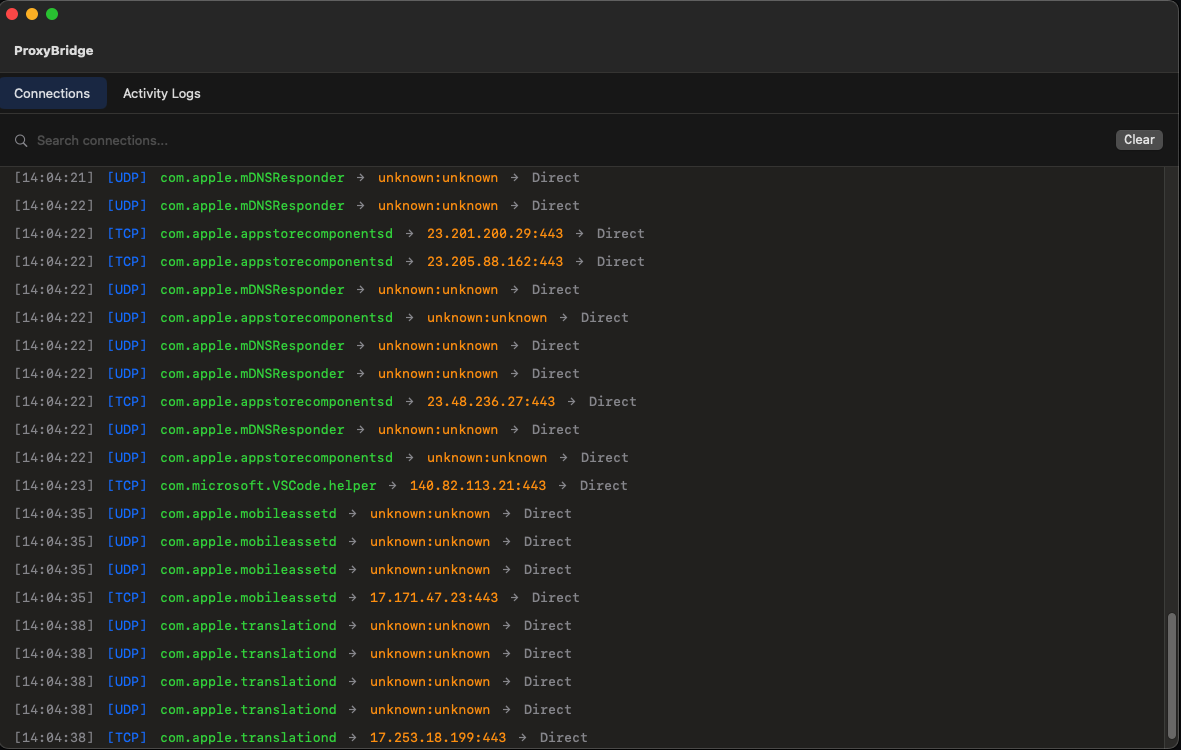 interceptsuite/proxybridge
Proxifier Alternative to redirect any Windows/MacOS/Linux TCP and UDP traffic to HTTP/Socks5 proxy
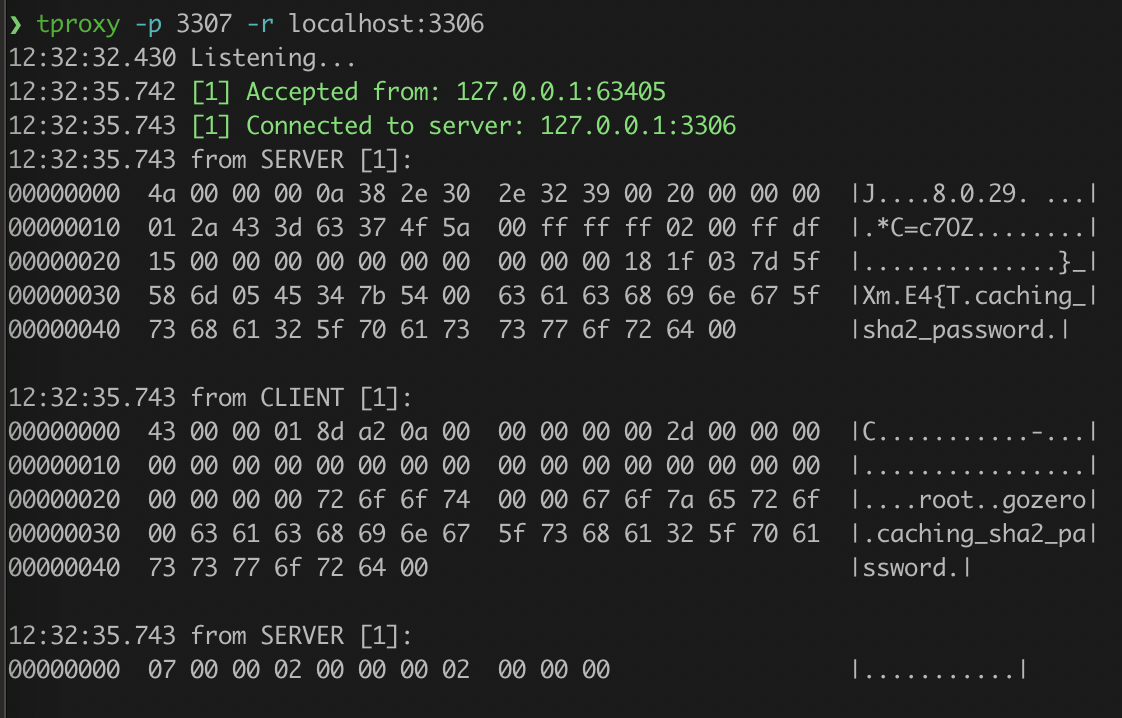 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
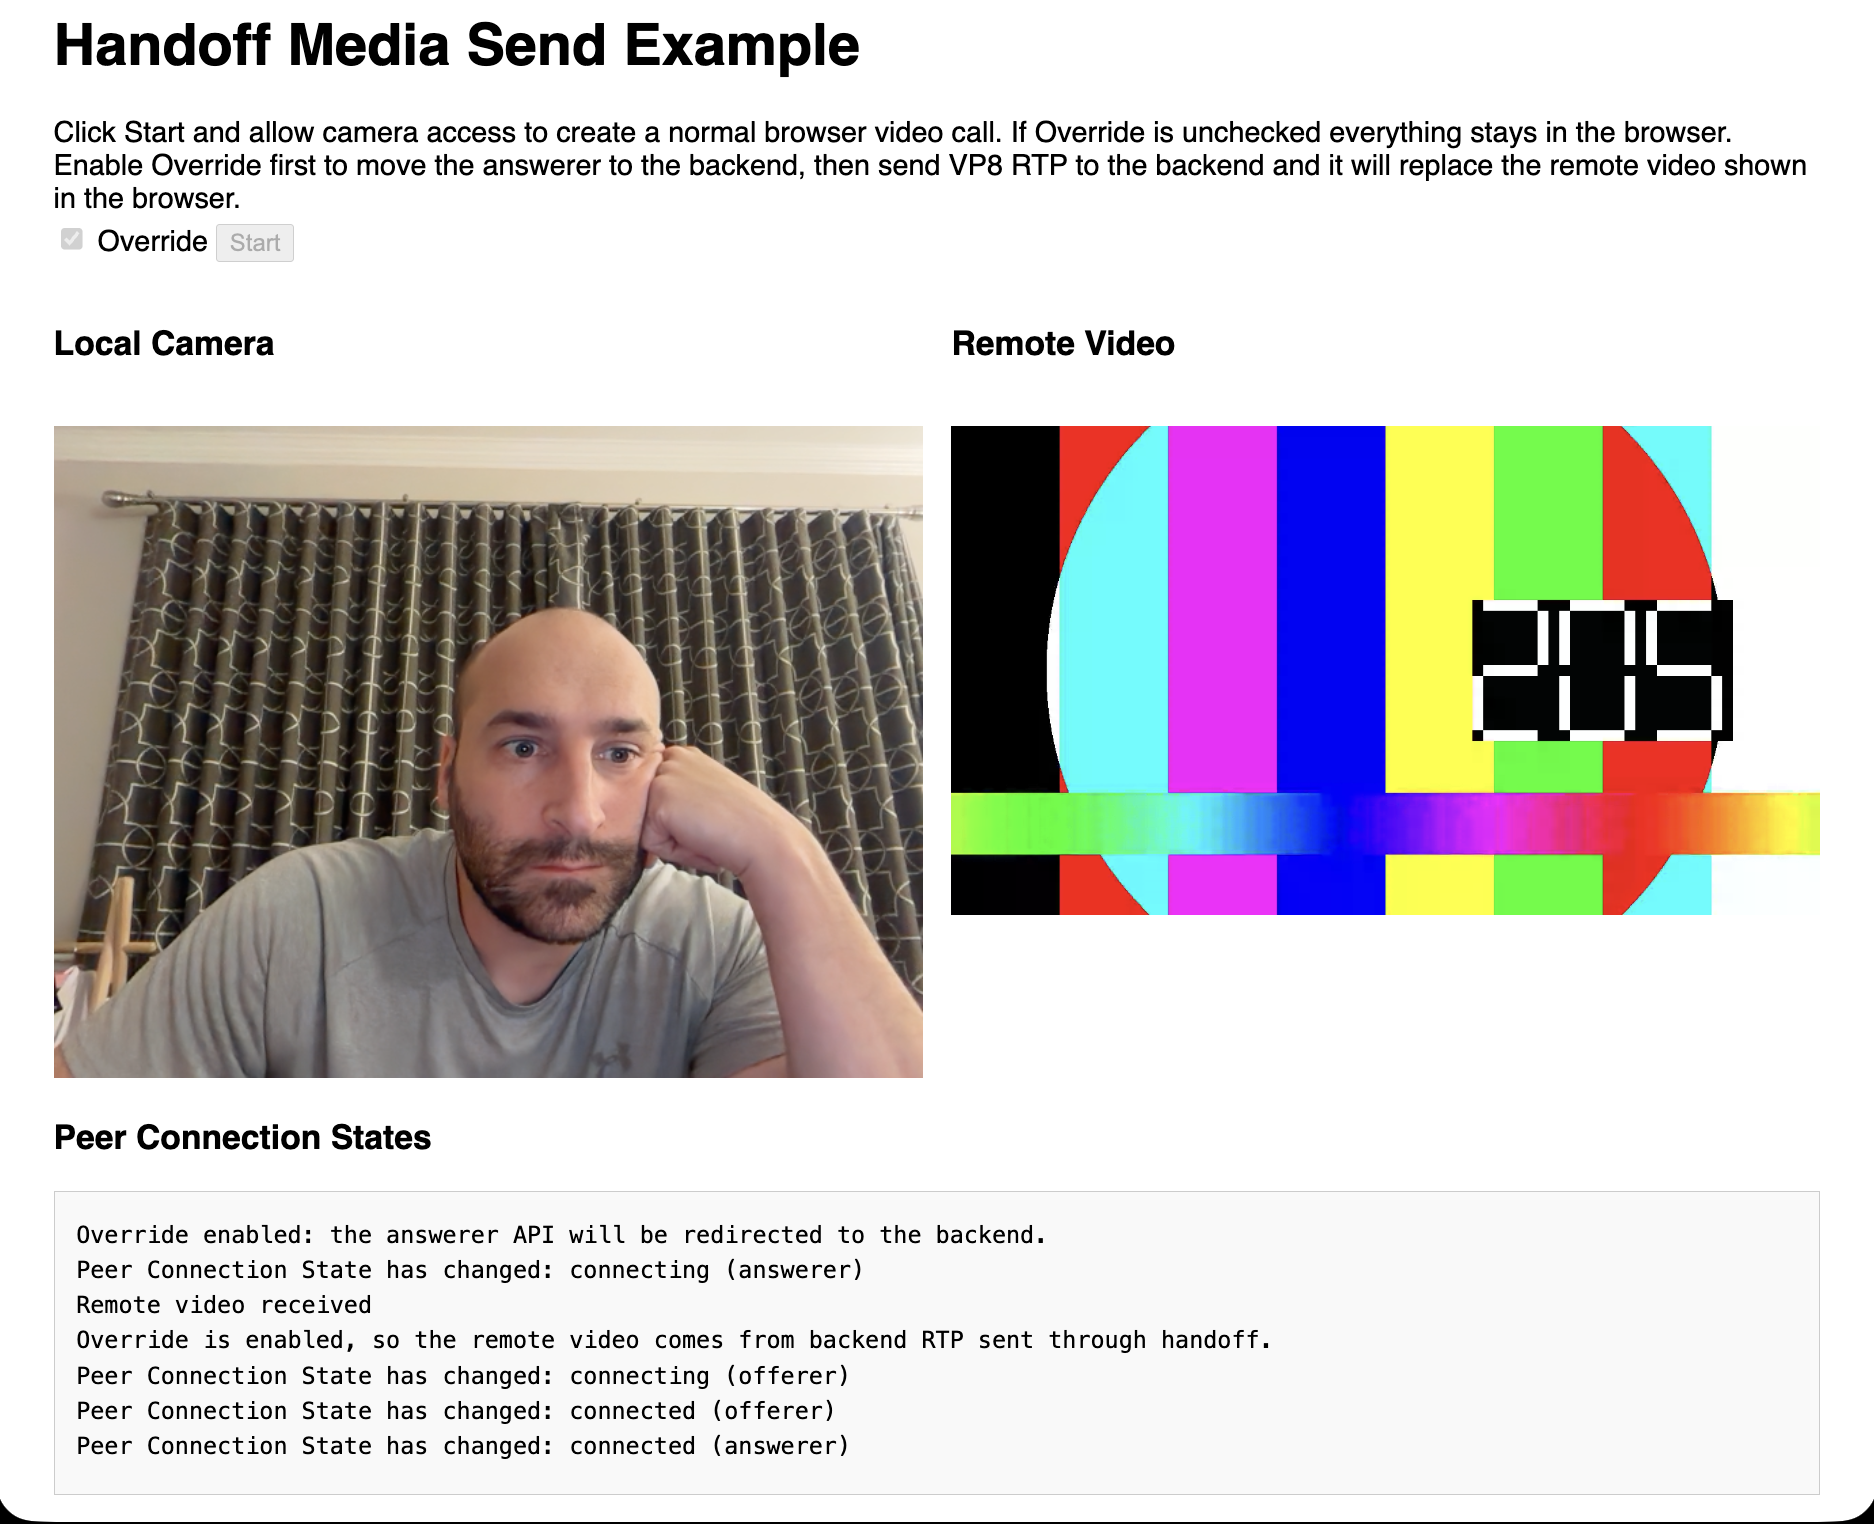 pion/handoff
Start WebRTC in the browser—run it somewhere else
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
 mercuryworkshop/woeful
Woeful is a tool that lets web apps to safely and securely connect to the outside internet without a complex backend.
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 codingo/interlace
Easily turn single threaded command line applications into a fast, multi-threaded application with CIDR and glob support.
 google/gopacket
Provides packet processing capabilities for Go
 fyoorer/shadowclone
Serverless task distribution framework that parallelizes CLI tools across thousands of cloud functions for rapid reconnaissance and data processing.
 devanshbatham/rayder
A lightweight tool for orchestrating and organizing your bug hunting recon / pentesting command-line workflows
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark