
wafmeow
 lu1sdv/wafmeow
wafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
information-gatheringnetwork-securitypenetration-testing+5
67
lu1sdv/wafmeowwafw00f's fingerprints. Go speed. Pipeline-native. WAF detection from live HTTP and offline captures.
 aa22396584/synology-nas-cli
nas: a zero-dependency Python CLI + MCP server for Synology DSM 7. One-command audit and fix for the C3RB3R / .L0CK3D ransomware campaign; hand it to…
 auyer/steganography
Zero-dependency Go library for LSB steganography in images: encode arbitrary files into PNG carriers and decode hidden messages, with message-size…
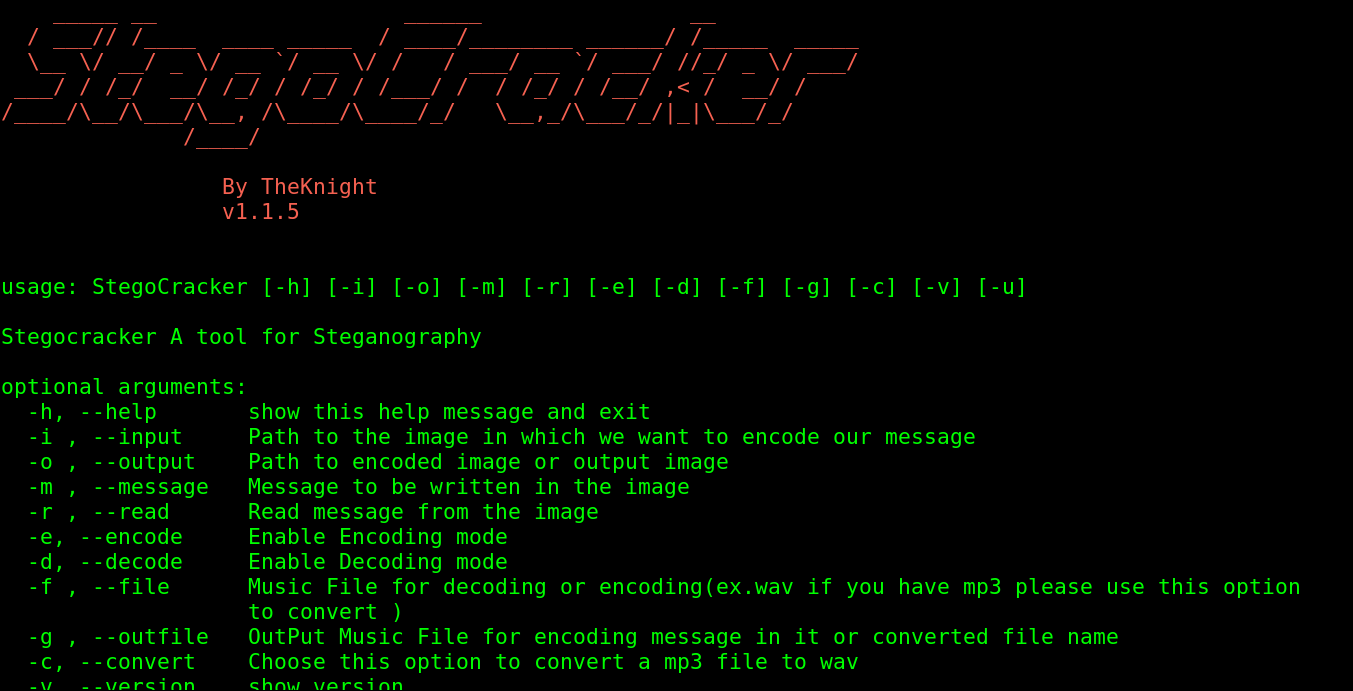 w1ldn16h7/stegocracker
Stego is an open-source and free steganography tool that lets you hide your secret message in an image or audio file. You will not notice any change…
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 ejfkdev/pycdc
Decompile and disassemble Python bytecode (.pyc/.pyo) back to readable source. Supports Python 2.0 - 3.15 (CPython, PyPy and other implementations).…
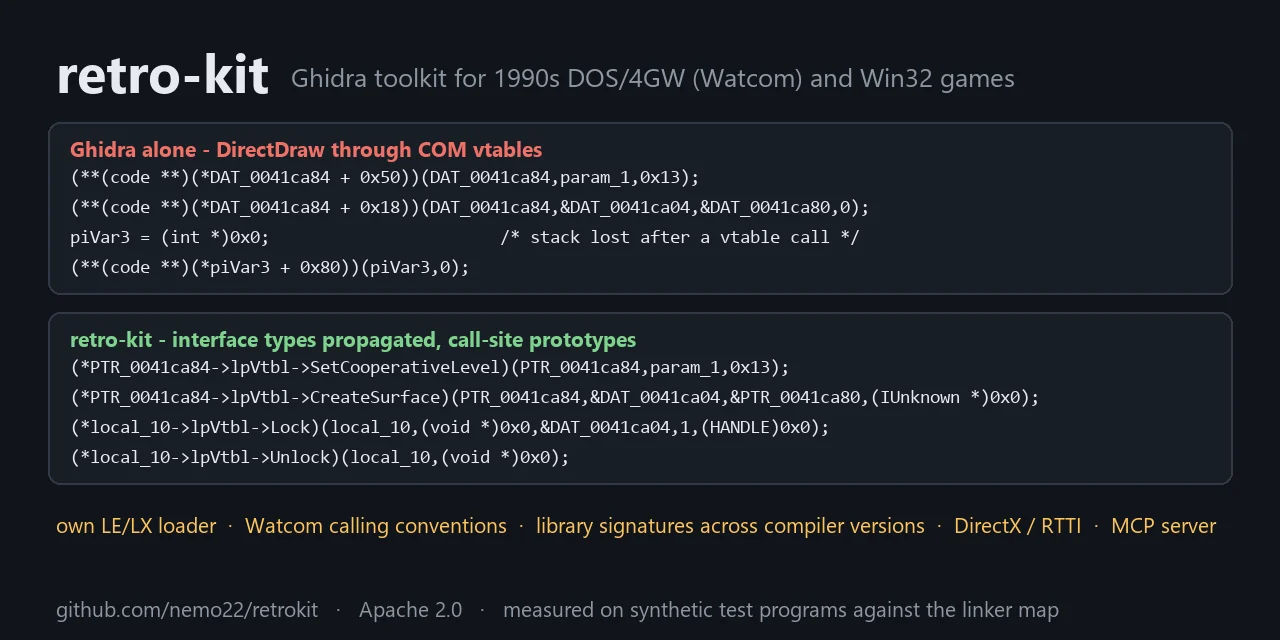 nautilusbits/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
 iana-org/get-trust-anchor
Tool for fetching/refreshing DNS Root Zone trust anchors
 emrekybs/veiled-eye
OSINT identity investigation tool. Pivot from an e-mail, username, phone or wallet across 46 sources into one profile and relationship graph.
 p3ng0s/archlive
Physical access red team live ISO built on Arch Linux
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
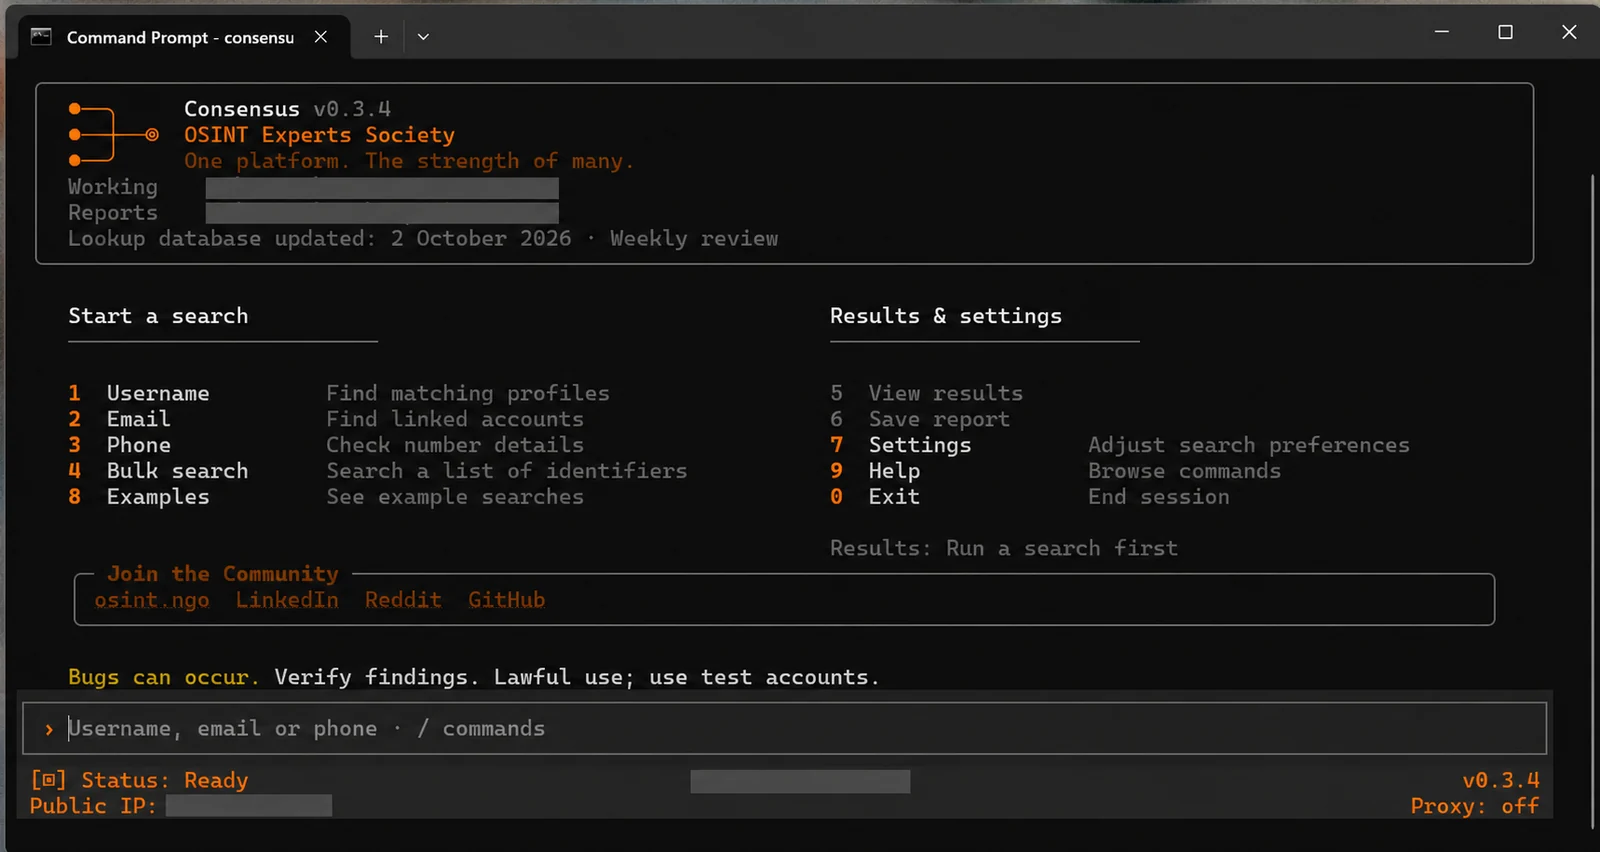 osint-experts-society/consensus-osint
🔎 Username, email & phone OSINT — 9,700+ lookup checks from 19 projects, with profile enrichment, bulk searches, evidence graphs and expert-reviewed…
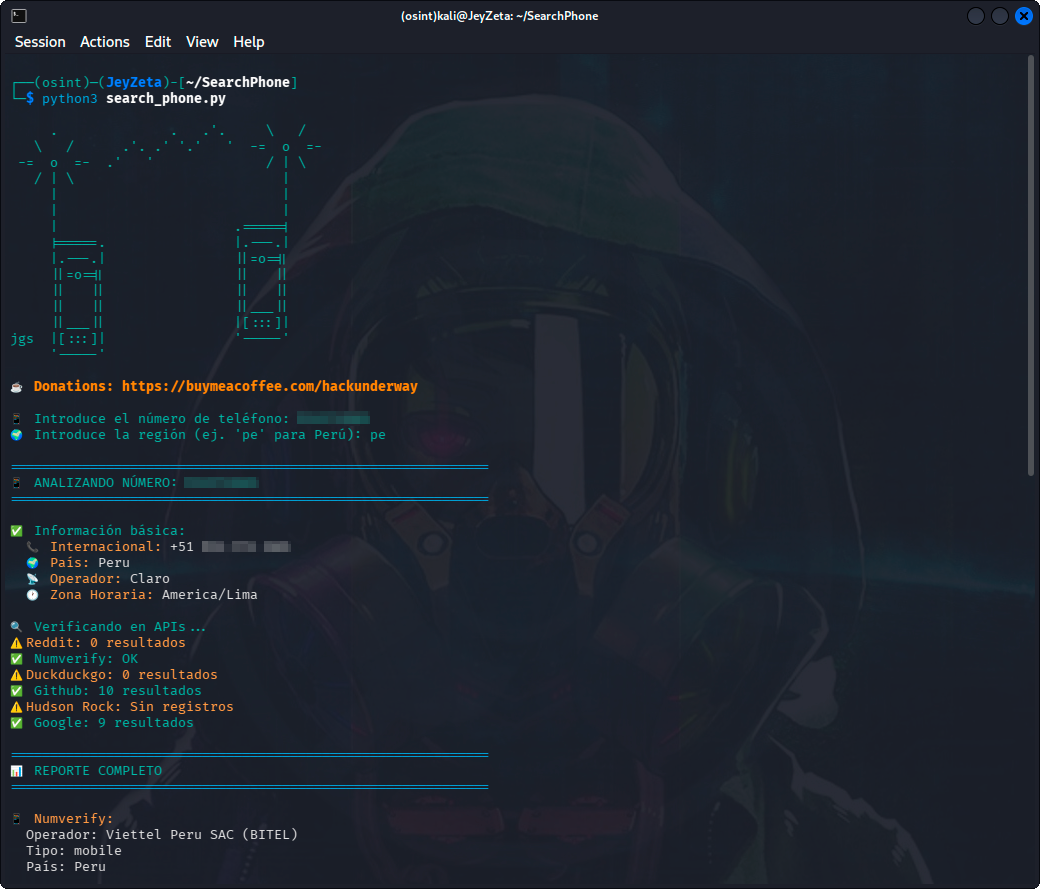 hackunderway/searchphone
Phone number OSINT toolkit with multi-API search (Google, GitHub, Numverify, Reddit, DuckDuckGo), Hudson Rock infostealer intelligence, and automatic…
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks