
dwarf2json
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
binary-analysisdigital-forensicsmemory-forensics+2
161
volatilityfoundation/dwarf2jsonconvert ELF/DWARF symbol and type information into vol3's intermediate JSON
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
 tomnomnom/anew
A tool for adding new lines to files, skipping duplicates
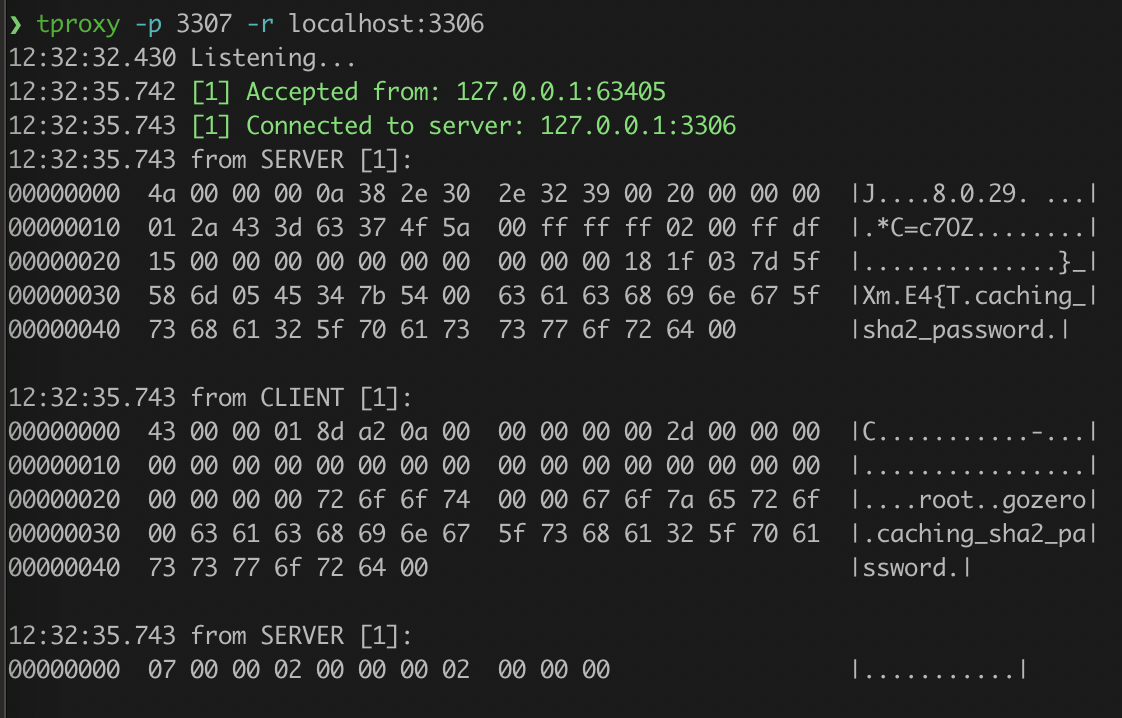 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
 aquasecurity/trivy-java-db
Builds a SQLite database of Maven artifacts (ArtifactID, GroupID, Version, SHA1) for Trivy's Java component vulnerability detection, enabling scans…
 rasta-mouse/pwnlift
Easy peasy file uploads
 buguroo/cuckooautoinstall
Auto Installer Script for Cuckoo Sandbox
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers
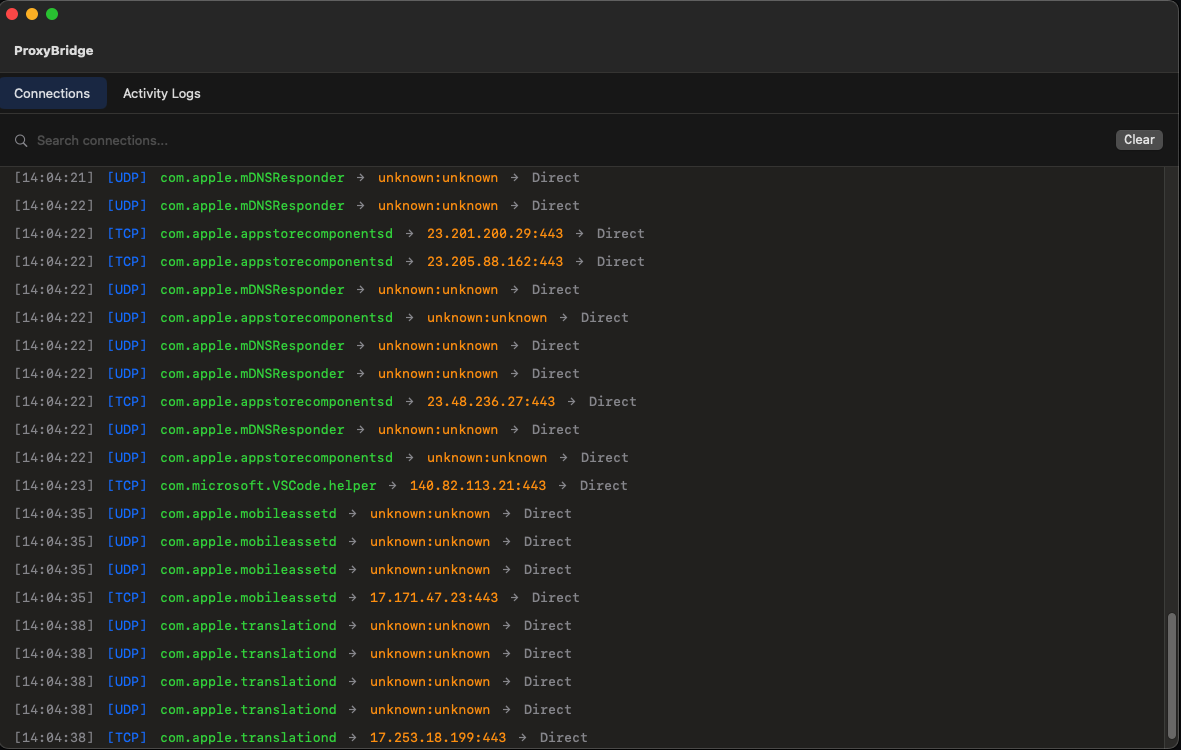 interceptsuite/proxybridge
Proxifier Alternative to redirect any Windows/MacOS/Linux TCP and UDP traffic to HTTP/Socks5 proxy
 mike01/pypacker
:package: The fastest and simplest packet manipulation lib for Python
 fastify/send
Node.js library for streaming files as HTTP responses with support for partial content, conditional requests, and configurable caching headers.…
 mercuryworkshop/woeful
Woeful is a tool that lets web apps to safely and securely connect to the outside internet without a complex backend.
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
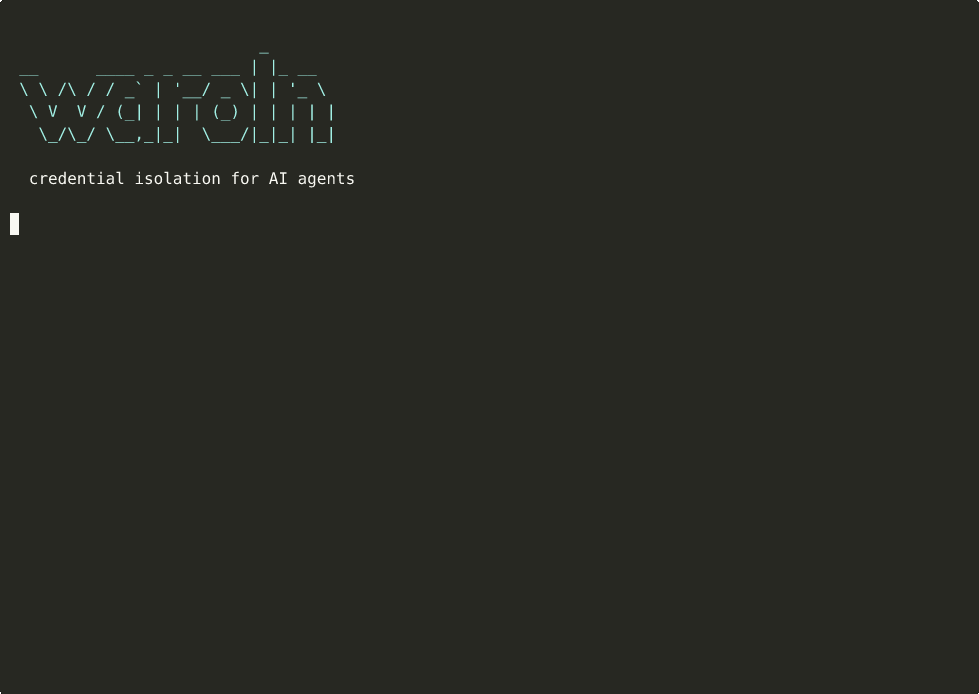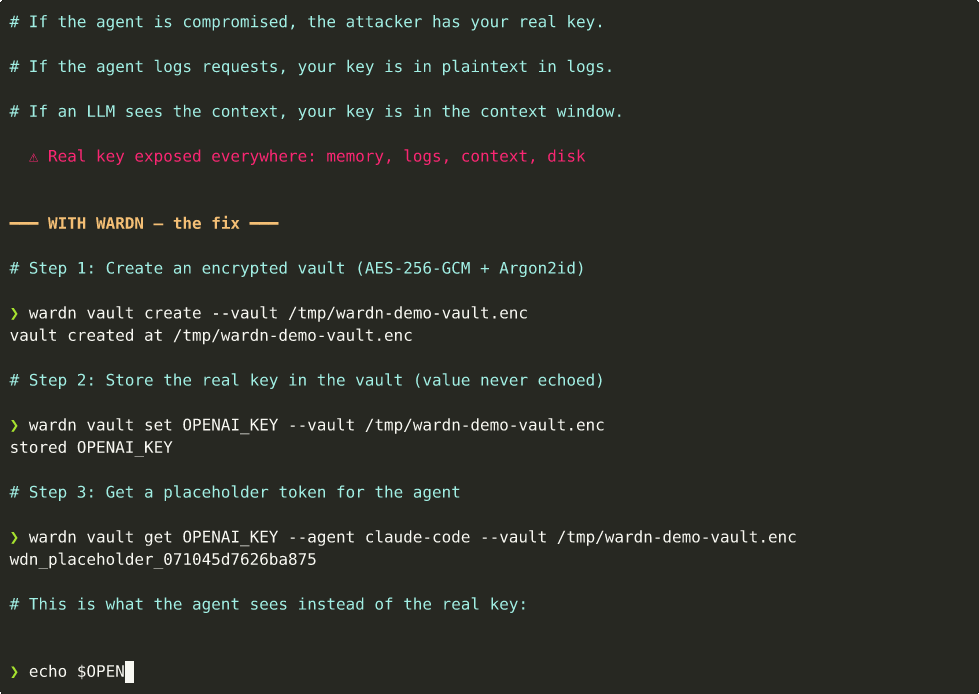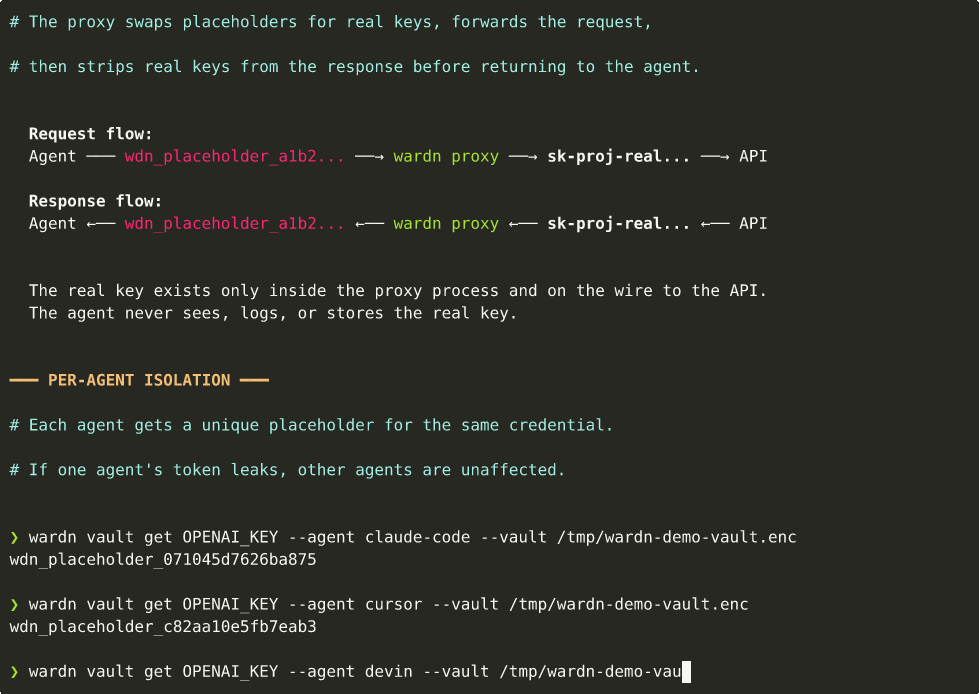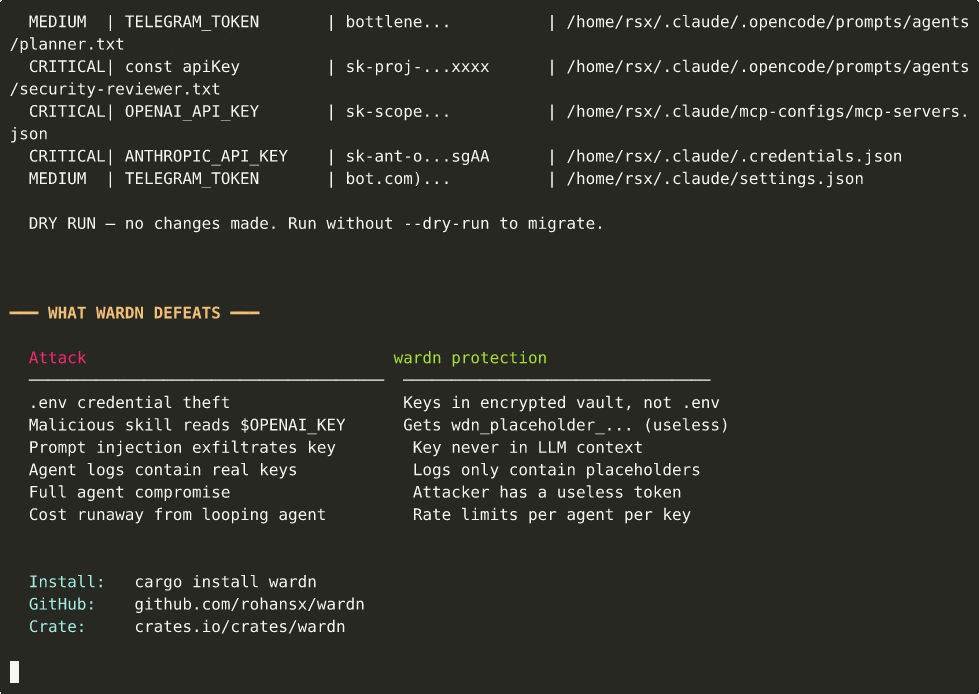 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
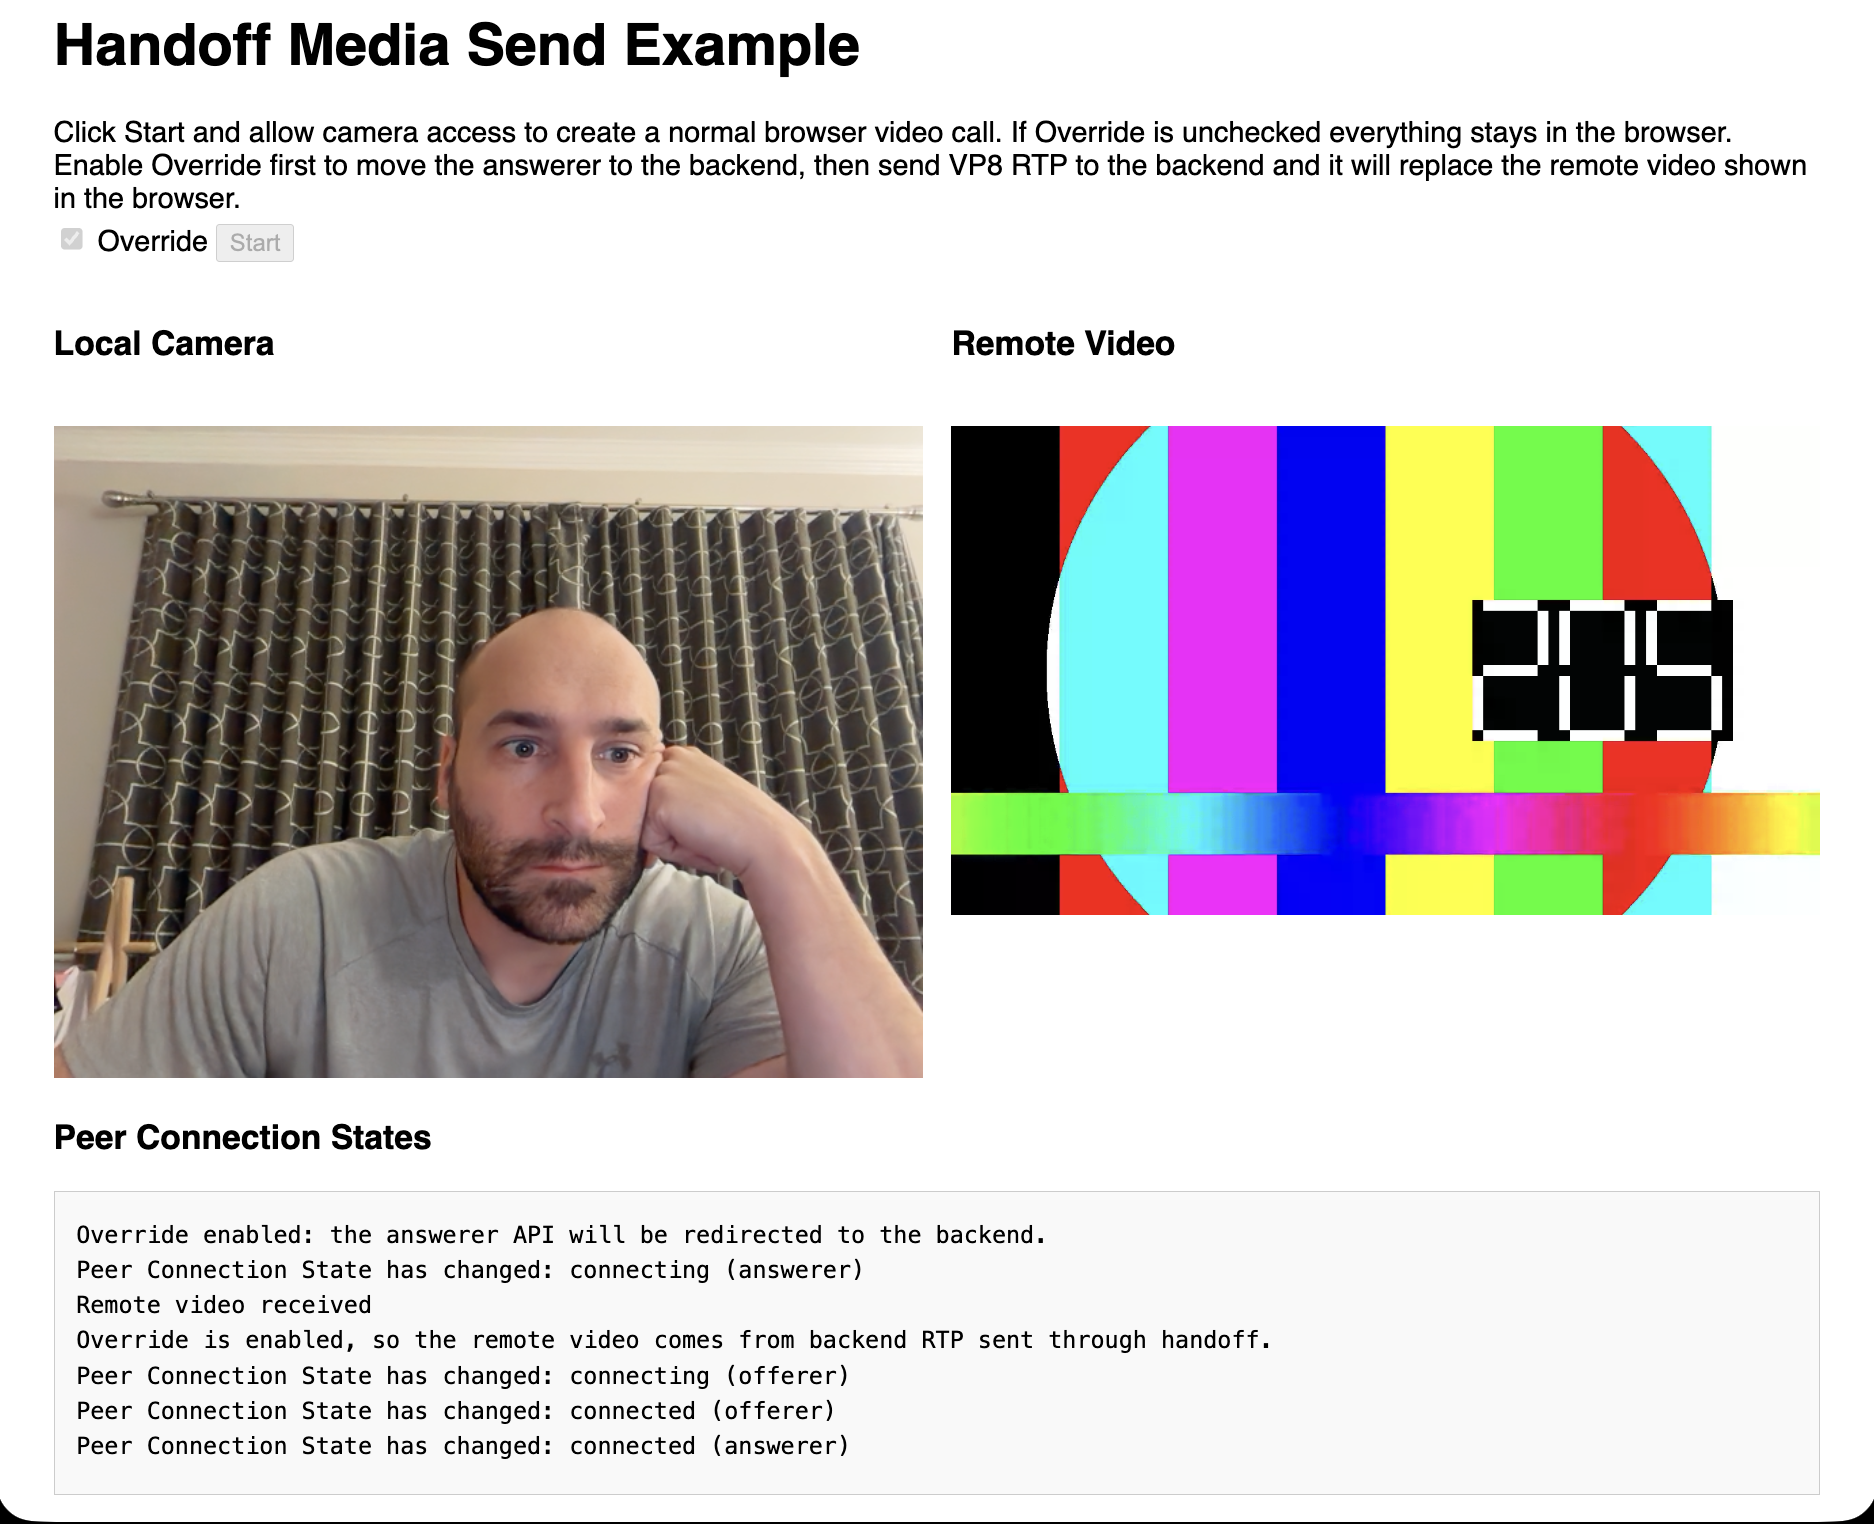 pion/handoff
Start WebRTC in the browser—run it somewhere else
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
 twisteroidambassador/udpack
UDPack is an extensible generic UDP packet obfuscator.