Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
loki preview

loki

GitHubgrafana/loki

Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…

general-purpose-utilitiesincident-responselog-analysis+1
29.1k
11h 17m ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.

digital-forensicsforensicsnetwork-forensics+2
7411 year ago
PcapPlusPlus preview

PcapPlusPlus

GitHubseladb/pcapplusplus

Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…

crawlerdns-analysisforensics+5
3.2k4 days ago
quipu preview

quipu

GitHubcorelight/quipu

A desktop workbench for writing, validating, compiling, and testing YARA rules.

code-analysisdefensive-toolsdigital-forensics+6
13 days ago
GPEWebDefender preview

GPEWebDefender

GitHubgopasteverything/gpewebdefender

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

defensive-toolsincident-responseinformation-gathering+8
52 months ago
fastnetmon preview

fastnetmon

GitHubpavel-odintsov/fastnetmon

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

anomaly-detectionincident-responselog-analysis+5
3.7k1 month ago
iDescriptor preview

iDescriptor

GitHubidescriptor/idescriptor

privacy-first, open-source and free idevice management tool written in Rust and Qt

digital-forensicsforensicsinformation-gathering+6
4.7k21 days ago
DetectTrace preview

DetectTrace

GitHubg0dse11/detecttrace

Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
defensive-toolsdevsecopsincident-response+5
218 days ago
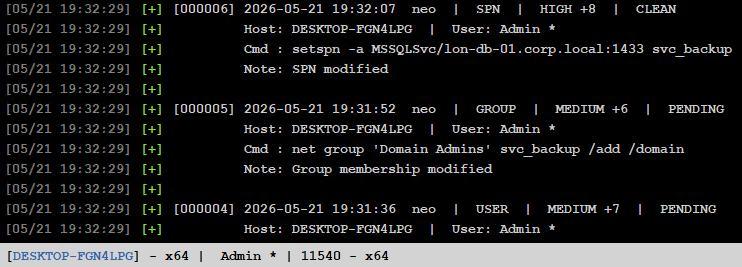
Ledger preview

Ledger

GitHubshellkraft/ledger

An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

command-and-controlincident-responselog-analysis+5
295 months ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

digital-forensicsforensicsincident-response+3
1.5k1 month ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
defensive-toolsdigital-forensicsforensics+8
49024 days ago
thethe preview
Archived

thethe

GitHubelevenpaths/thethe

thethe

incident-responseinformation-gatheringlog-analysis+4
1156 years ago
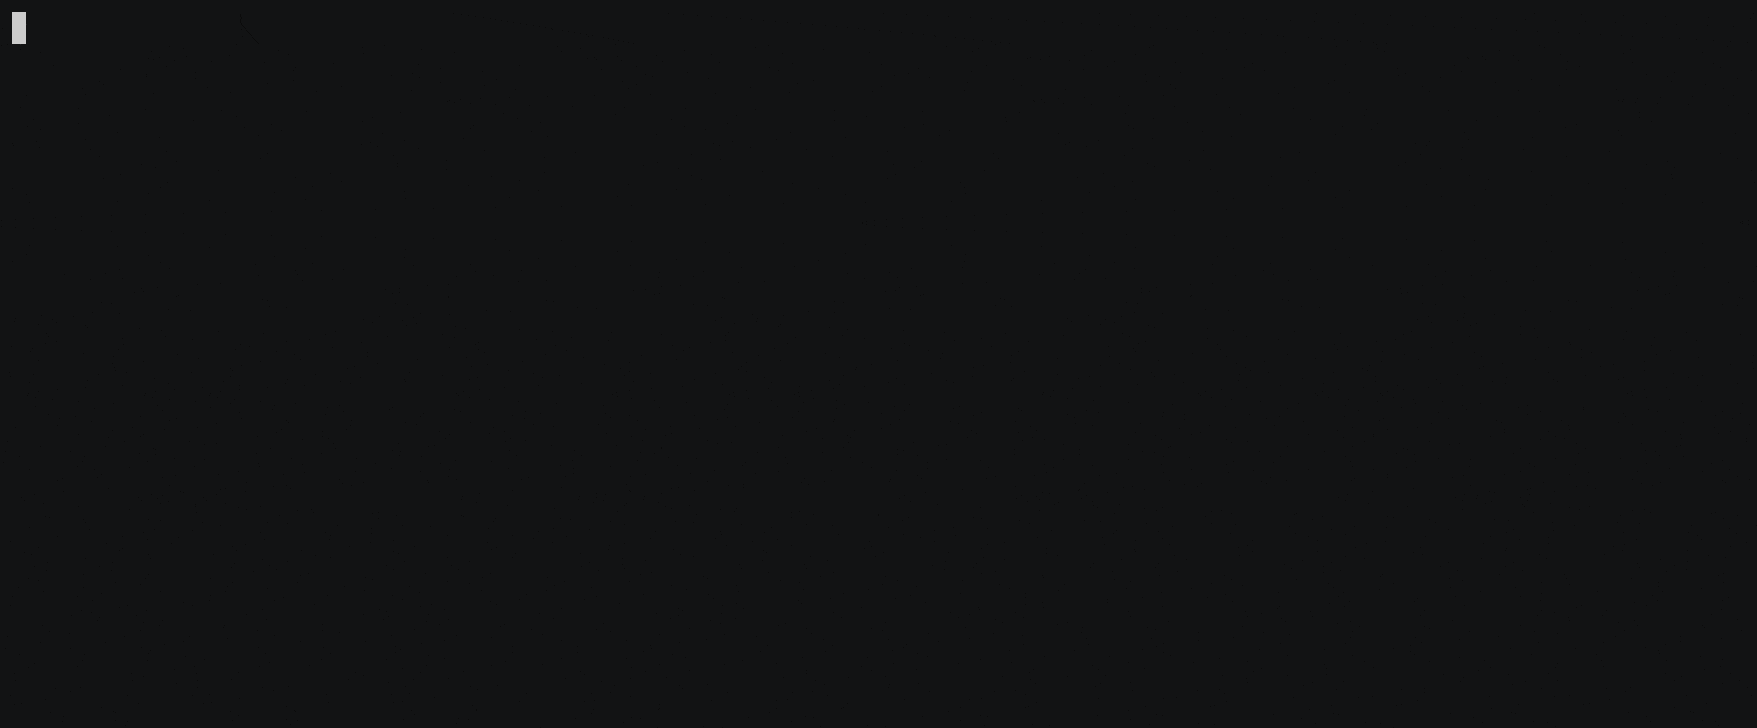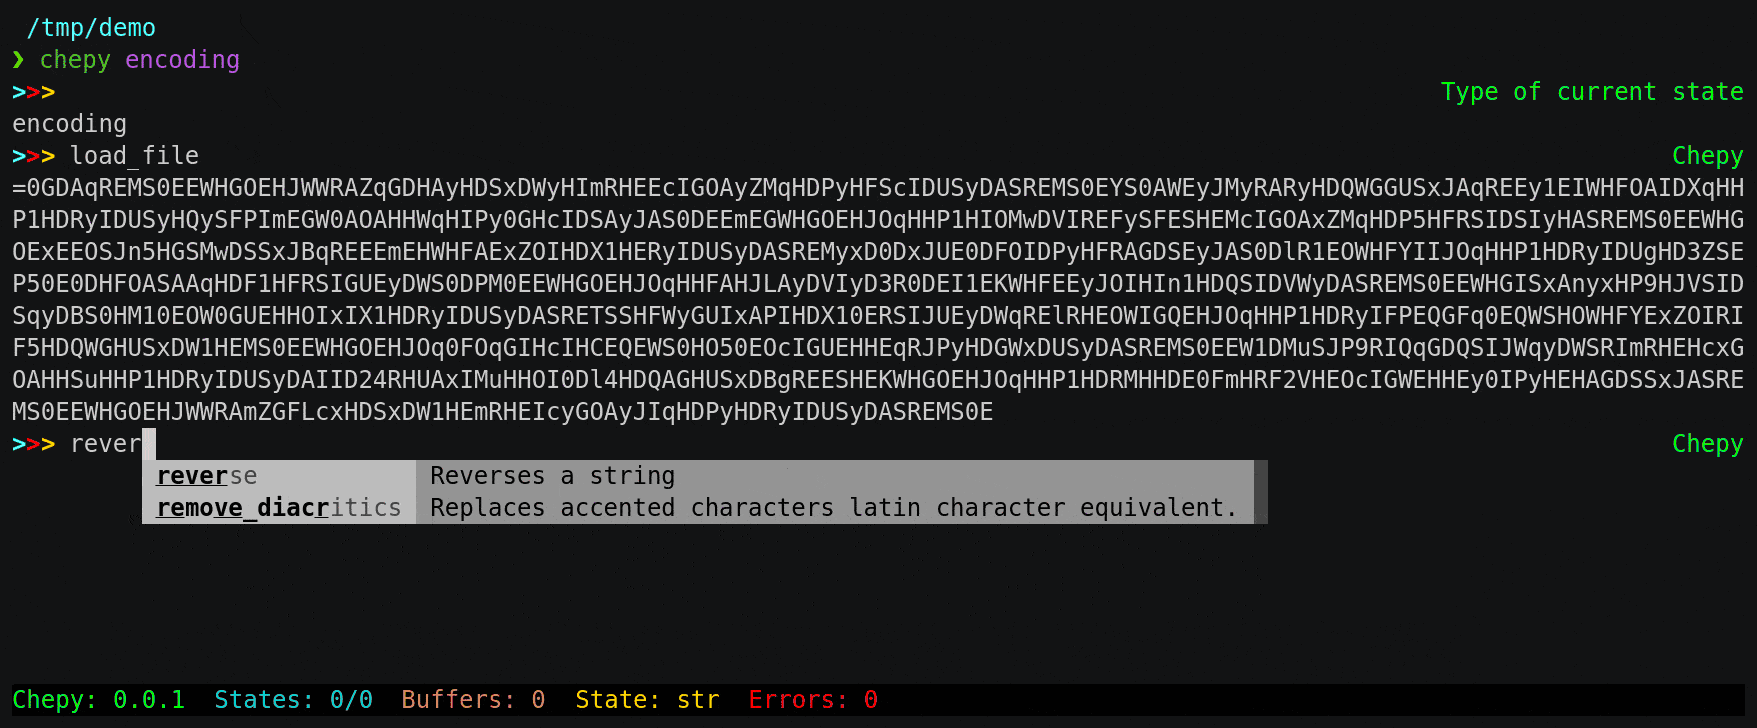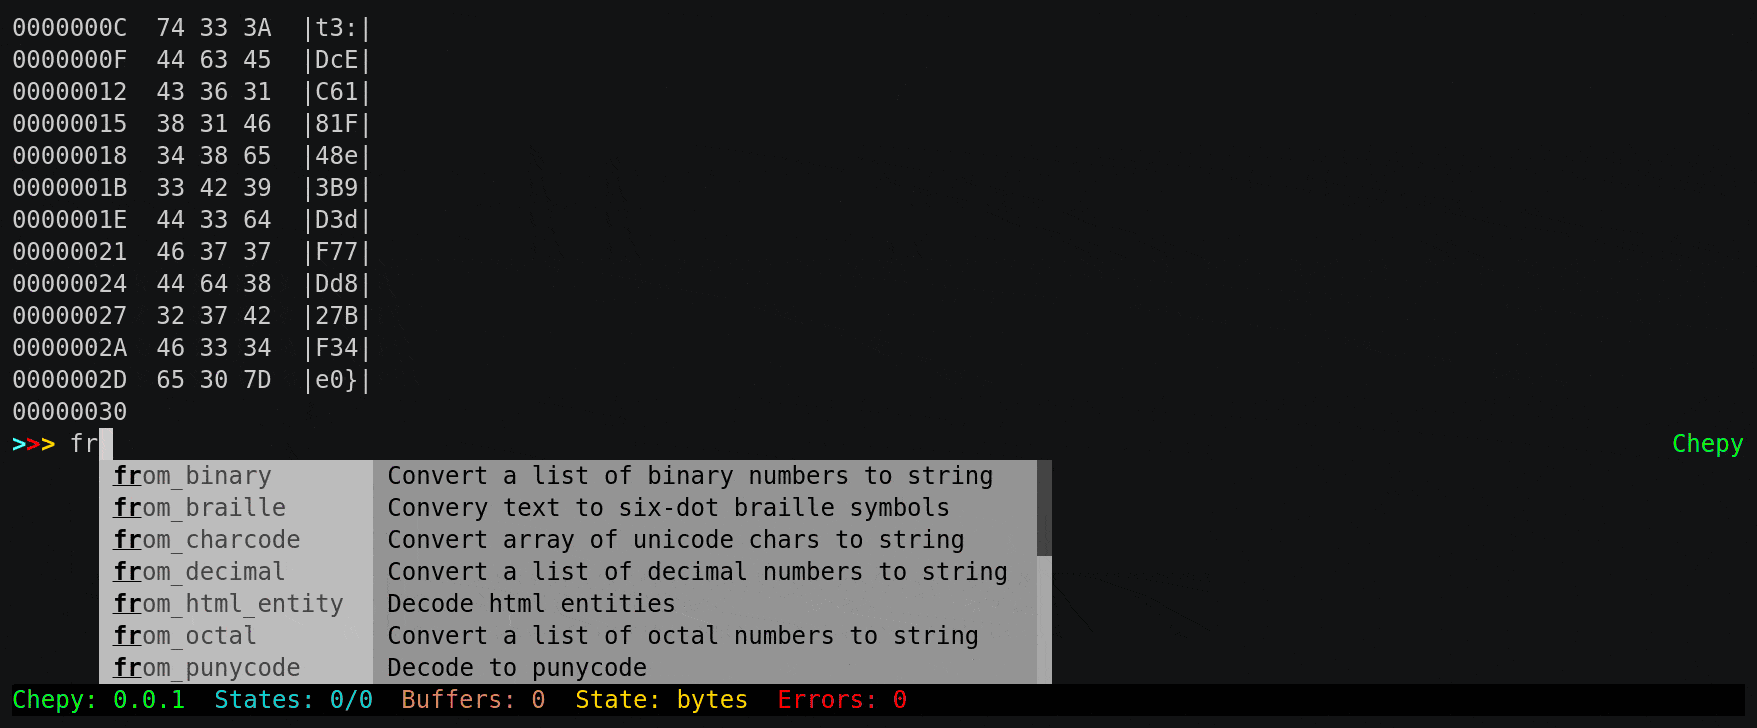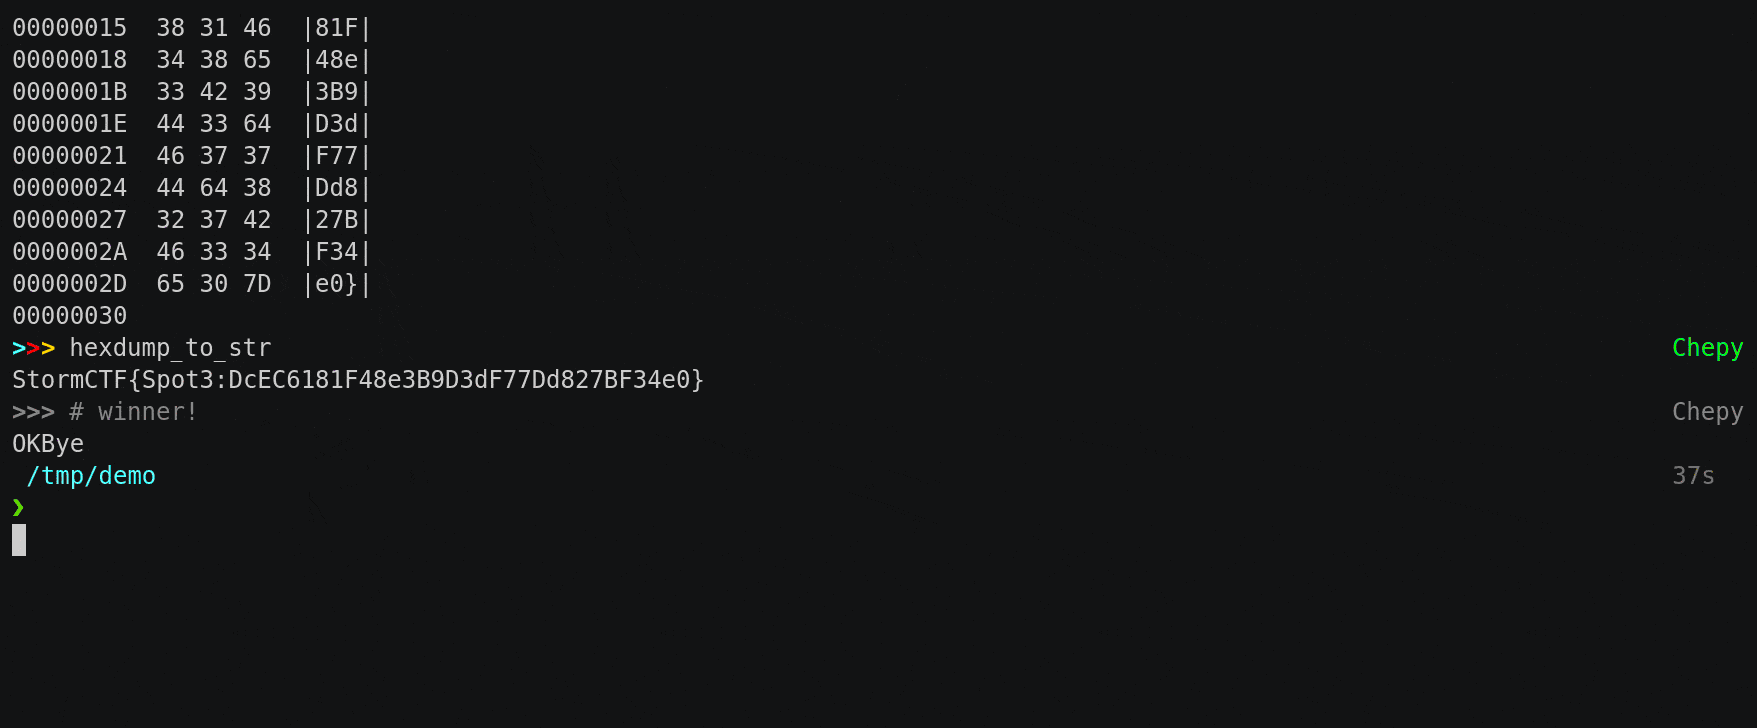
chepy preview

chepy

GitHubsecurisec/chepy

Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
cryptographyctfforensics+2
1.1k5 months ago
securitybot preview
Archived

securitybot

GitHubdropbox/securitybot

Distributed alerting for the masses!
authenticationincident-responselog-analysis+2
9897 years ago
xioc preview

xioc

GitHubassafmo/xioc

Extract indicators of compromise from text, including "escaped" ones.

forensicsinformation-gatheringioc-management+3
1636 years ago
refinery preview

refinery

GitHubbinref/refinery

High Octane Triage Analysis

binary-analysiscryptographyforensics+4
8782h 11m ago
yaml2yara preview

yaml2yara

GitHubnccgroup/yaml2yara

Generate bulk YARA rules from YAML input

digital-forensicsincident-responseintrusion-detection+4
226 years ago
babyshark preview

babyshark

GitHubvignesh07/babyshark

Flows-first PCAP TUI (case files, gorgeous UX). Do do do do.
anomaly-detectiondns-analysisforensics+5
5678 months ago
Previous12Next