
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
731 results
halogen preview
Archived

halogen

GitHubtarget/halogen

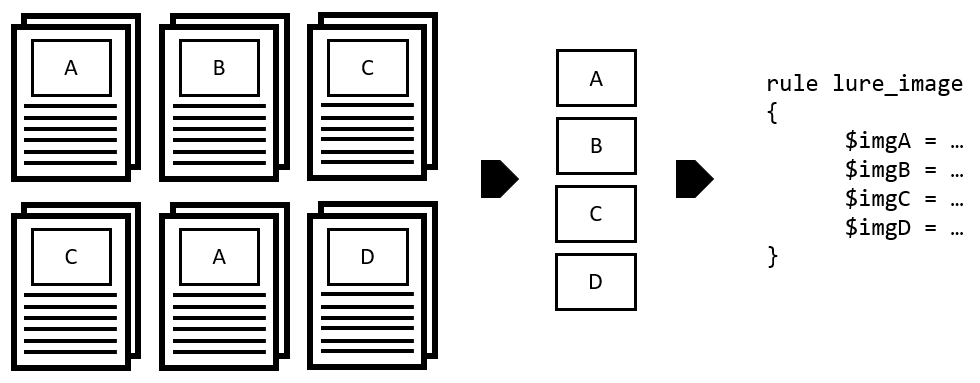
Automatically create YARA rules from malicious documents.

forensicsincident-responsemalware-analysis+2
210
4 years ago
Sooty preview

Sooty

GitHubtheresafewconors/sooty

The SOC Analysts all-in-one CLI tool to automate and speed up workflow.
dns-analysishash-analysisinformation-gathering+5
1.5k1 year ago
Manati preview

Manati

GitHubstratosphereips/manati

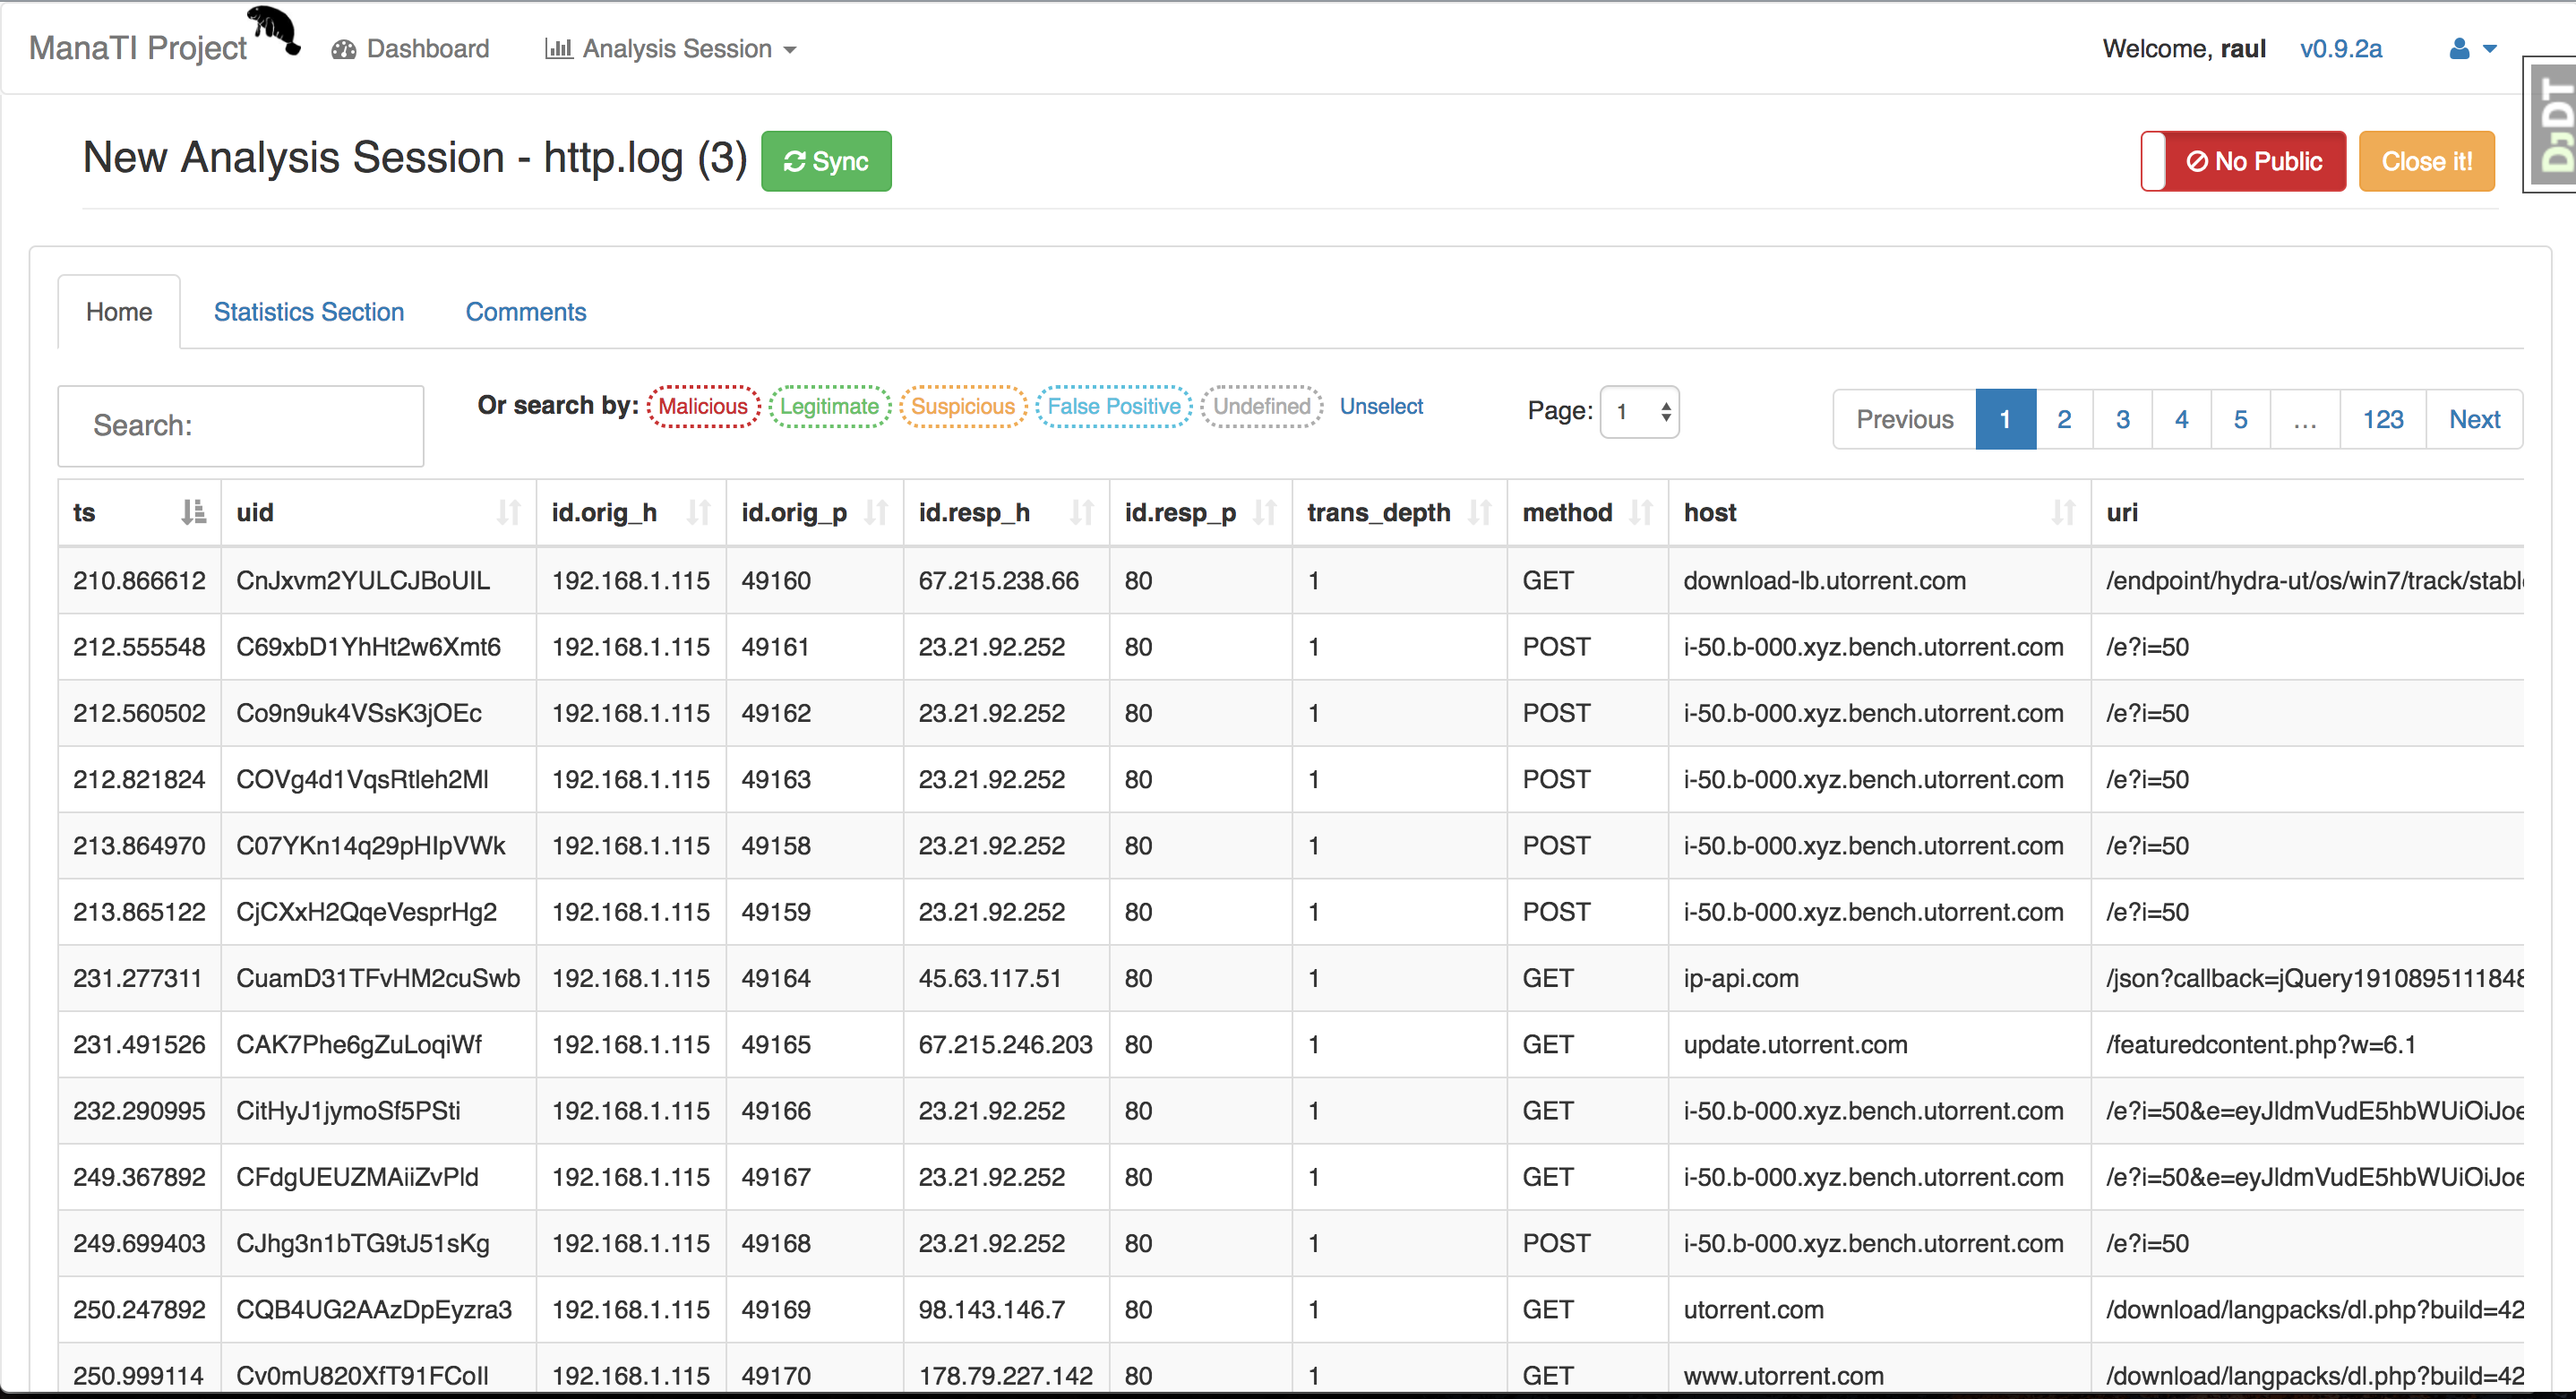
A web-based tool to assist the work of the intuitive threat analysts.

information-gatheringmachine-learningthreat-intelligence
1147 years ago
certReport preview

certReport

GitHubsquiblydoo/certreport

A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.
hash-analysismalware-analysisthreat-intelligence
405 months ago
androidqf preview

androidqf

GitHubmvt-project/androidqf

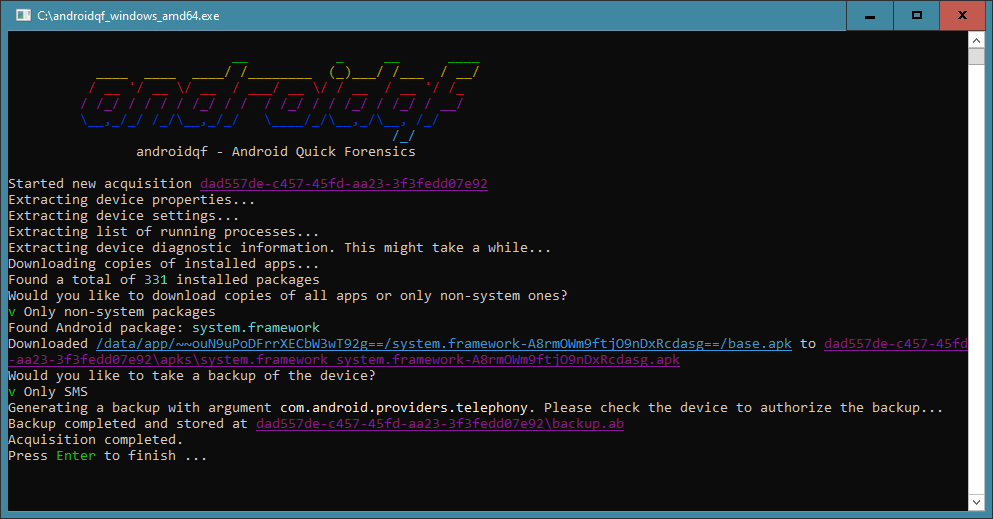
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
27314 days ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
cloud-securitydigital-forensicsincident-response+3
8462 months ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

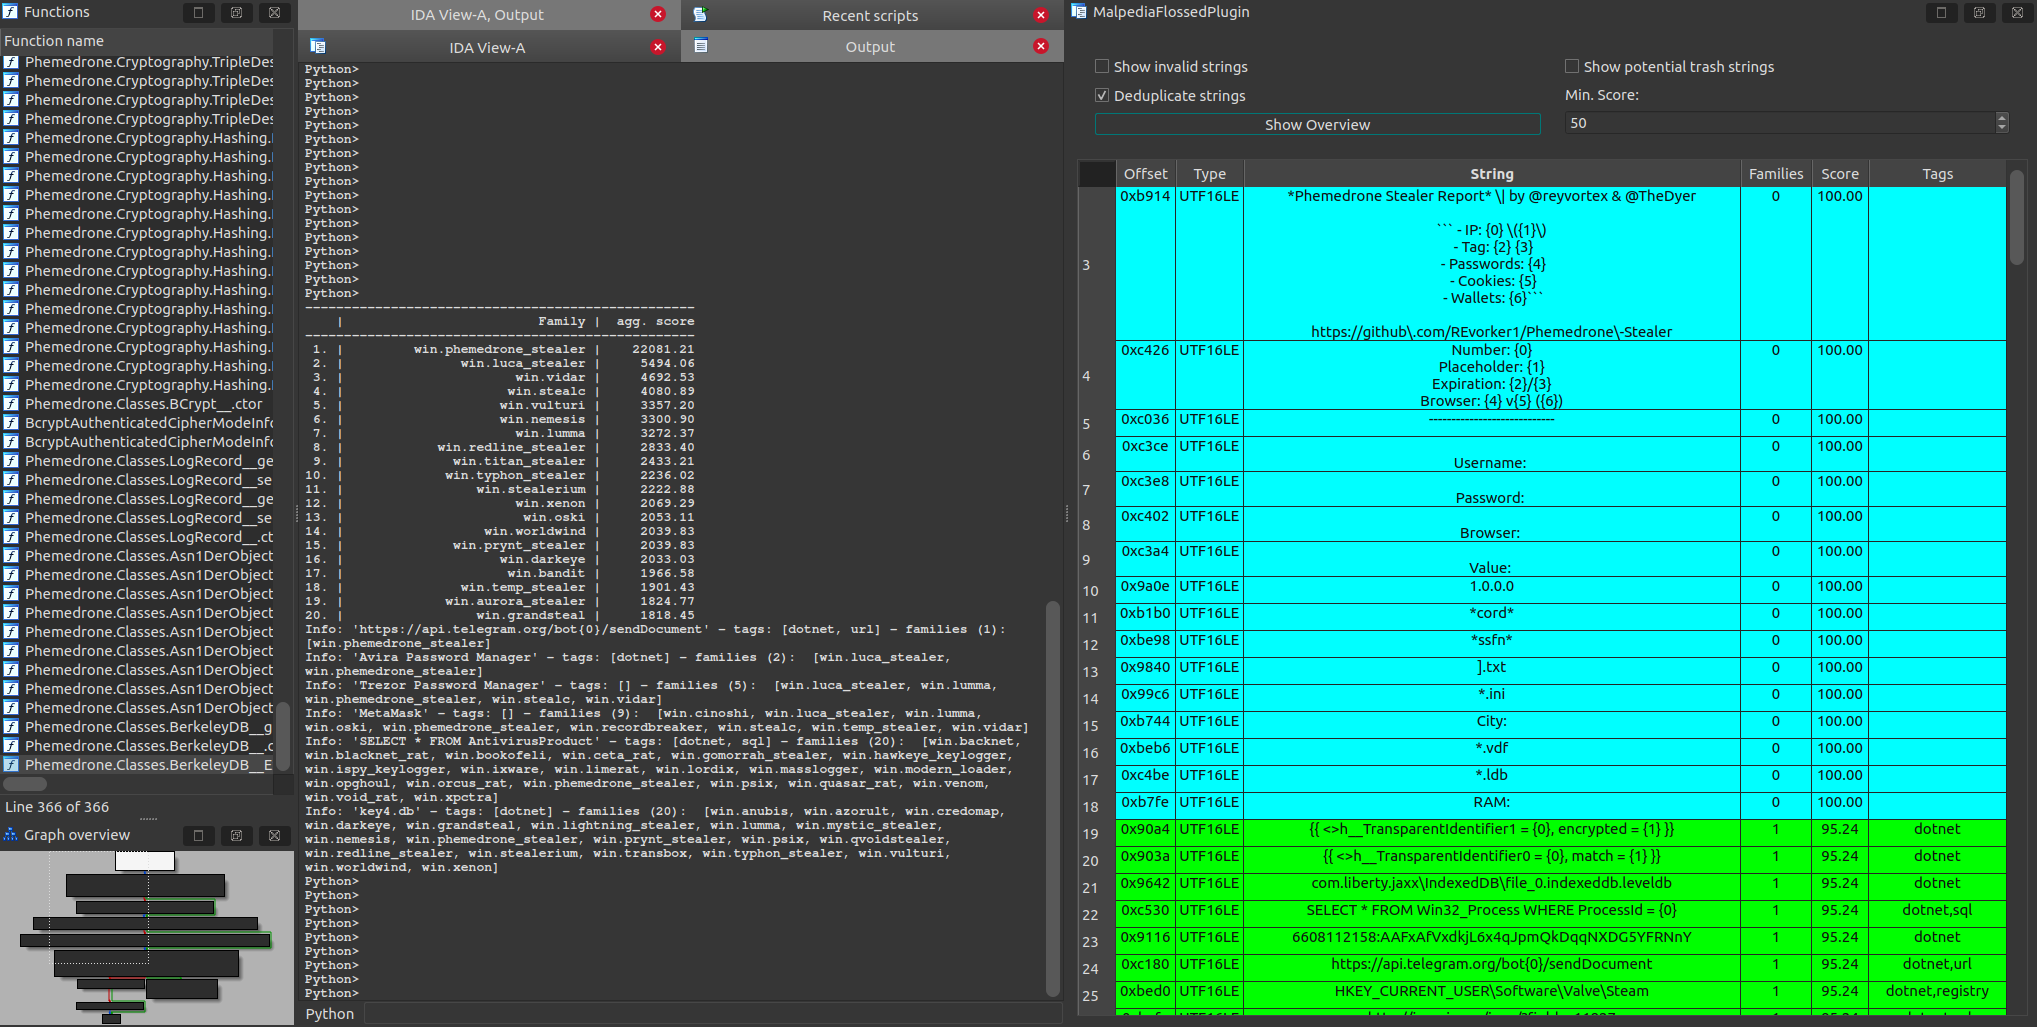
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
838 months ago
SploitScan preview

SploitScan

GitHubxaitax/sploitscan

Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.

exploit-frameworksosintpenetration-testing+2
1.4k24 days ago
chiasmodon preview

chiasmodon

GitHubchiasmod0n/chiasmodon

Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…

dns-subdomain-enumerationemail-harvestinginformation-gathering+5
6981 year ago
mitmengine preview
Archived

mitmengine

GitHubcloudflare/mitmengine

A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
defensive-toolsincident-responsenetwork-security+1
8132 years ago
Threat-Intelligence-Hunter preview

Threat-Intelligence-Hunter

GitHubabhinavbom/threat-intelligence-hunter

TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
information-gatheringioc-managementosint+1
1561 year ago
Search_CVE preview

Search_CVE

GitHubk3ystr0k3r/search_cve

ntroducing Search_CVE: Unleash the Power of CVE Searching Search_CVE is a cutting-edge tool designed to simplify and optimize the process of…
information-gatheringreconnaissancethreat-intelligence+1
33 months ago
buttinsky preview

buttinsky

GitHubmushorg/buttinsky

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
information-gatheringintrusion-detectionmalware-analysis+2
8213 years ago
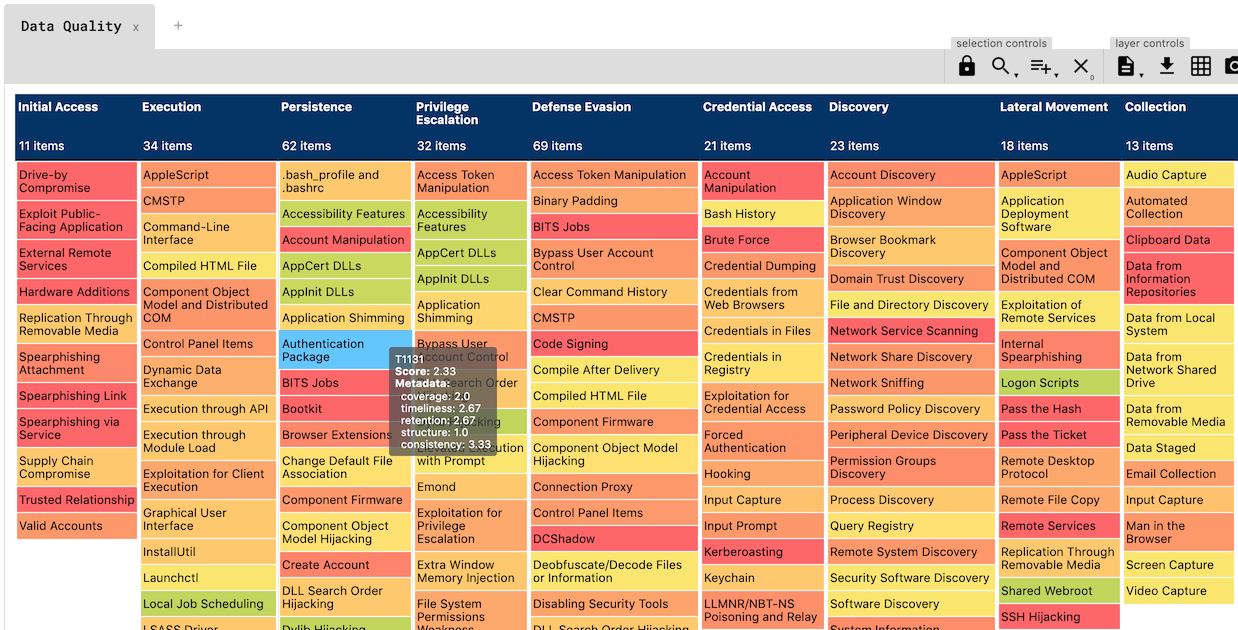
ossem-power-up preview

ossem-power-up

GitHubhxnoyd/ossem-power-up

A tool to assess data quality, built on top of the awesome OSSEM.

curated-resourceseducationlog-analysis+1
795 years ago
theHarvester preview

theHarvester

GitHublaramies/theharvester

E-mails, subdomains and names Harvester - OSINT

dns-analysisdns-subdomain-enumerationemail-harvesting+9
17.4k7 days ago
DDWPasteRecon preview

DDWPasteRecon

GitHubviralmaniar/ddwpasterecon

DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
data-exfiltrationdefensive-toolsincident-response+4
464 years ago
typodetect preview

typodetect

GitHubtelefonicatc2tech/typodetect

Detects active domain mutations to prevent phishing and smishing. Uses IANA TLDs, blockchain DNS validation, and DoH malware reports. Outputs JSON or…
dns-analysisinformation-gatheringosint+2
755 years ago
APT-Hunter preview

APT-Hunter

GitHubahmedkhlief/apt-hunter

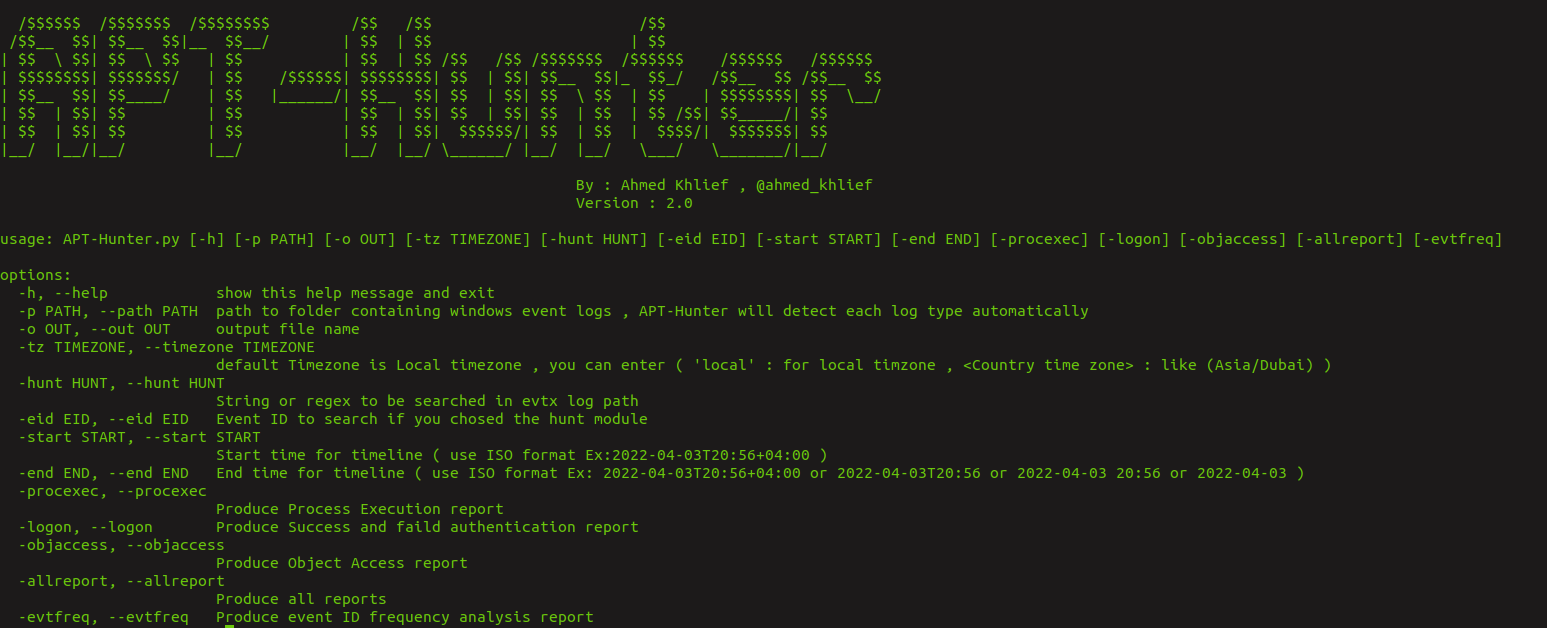
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…

forensicsincident-responselog-analysis+1
1.4k1 year ago
Previous12…41Next