
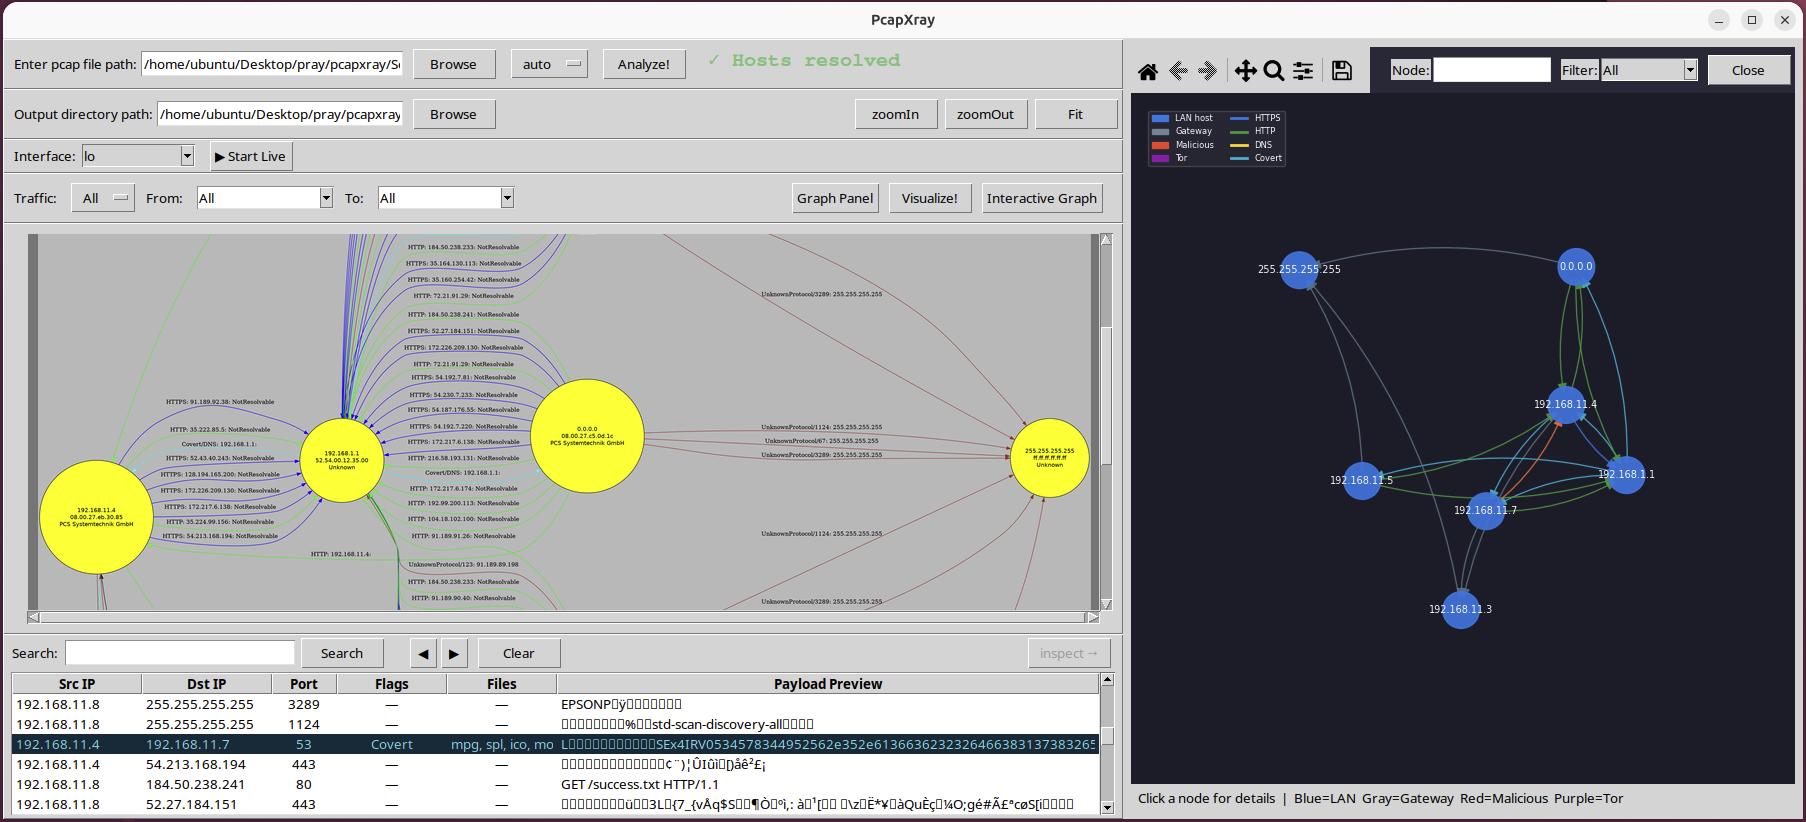
PcapXray
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
ctfdns-analysiseducation+7
1.9k
srixivas/pcapxray❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
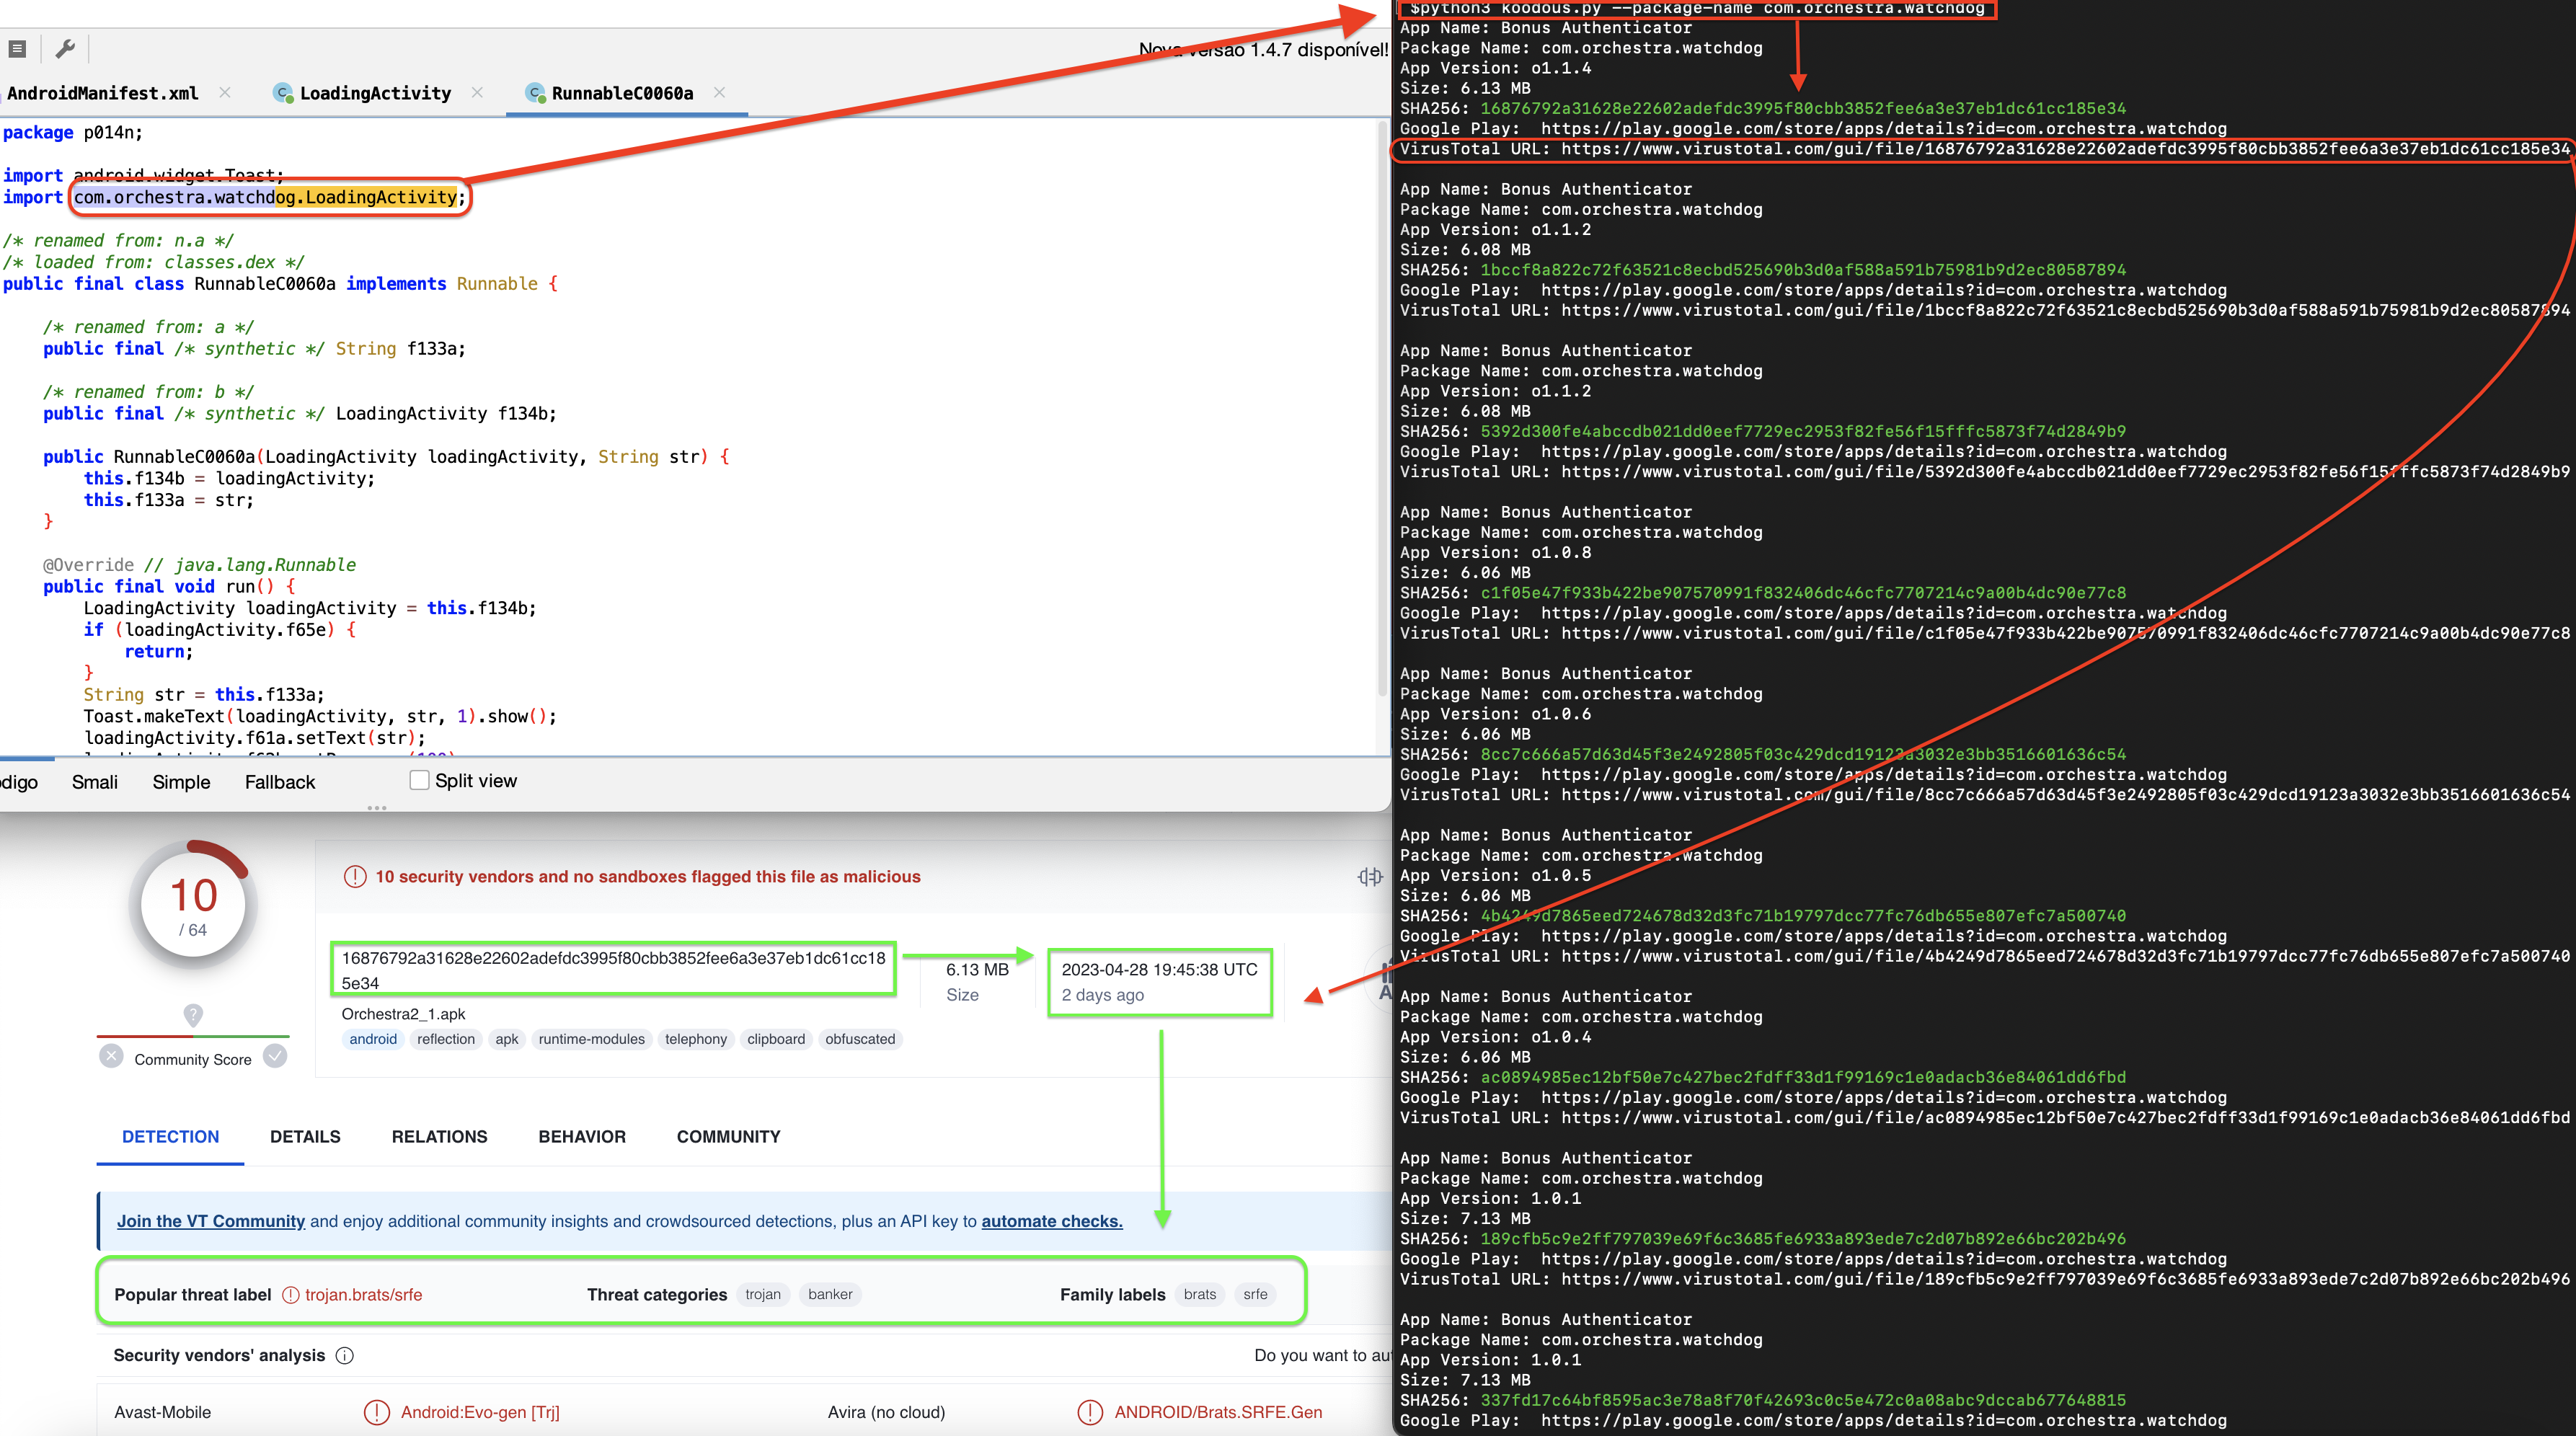 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
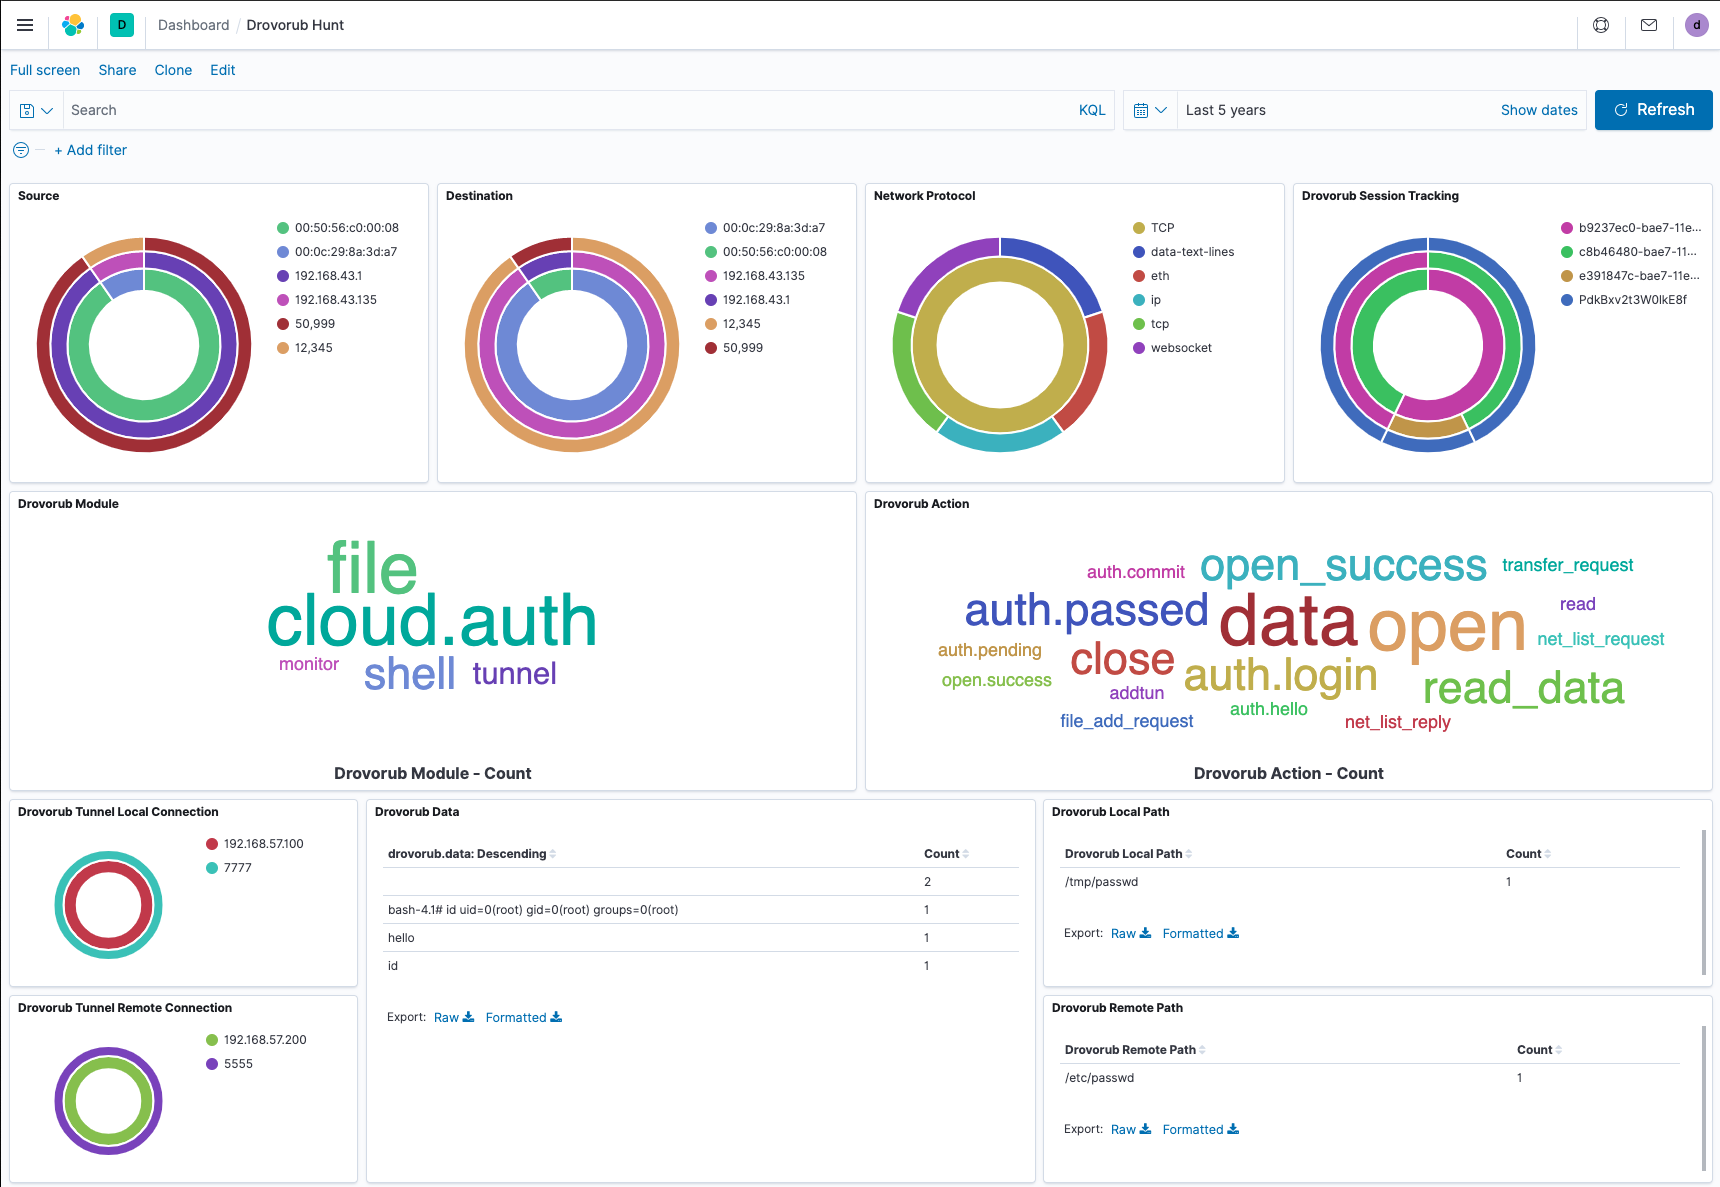 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
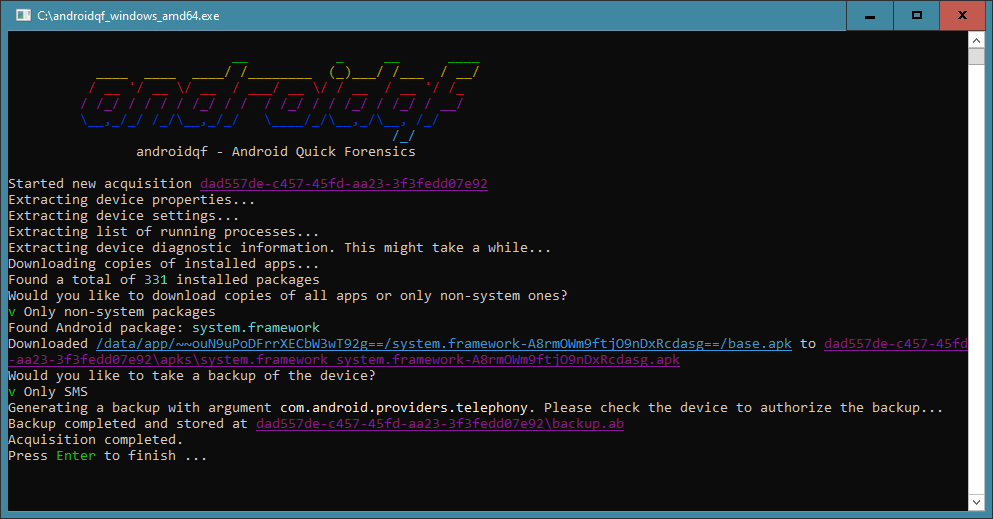 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
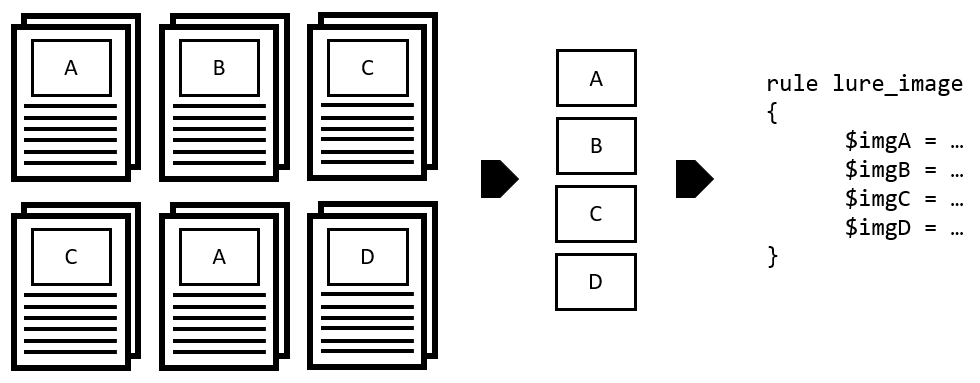 target/halogen
Automatically create YARA rules from malicious documents.
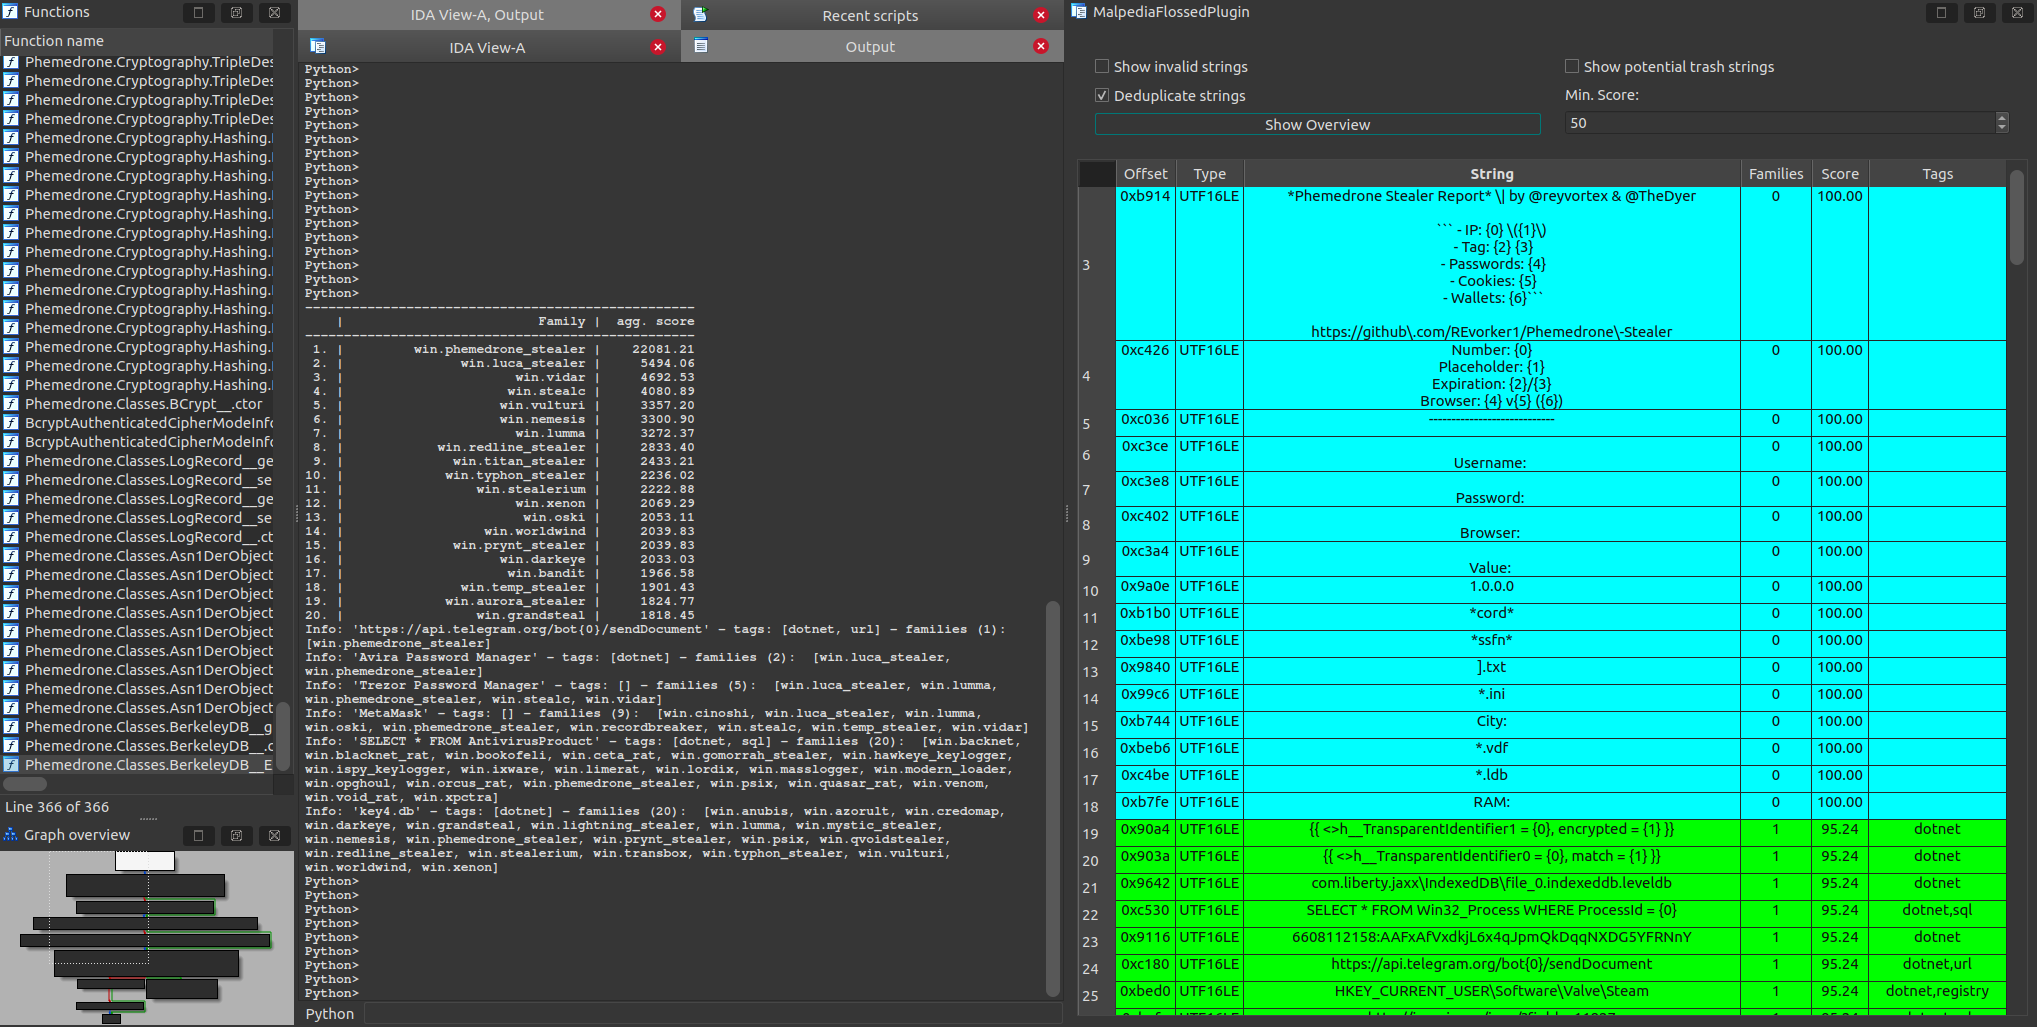 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
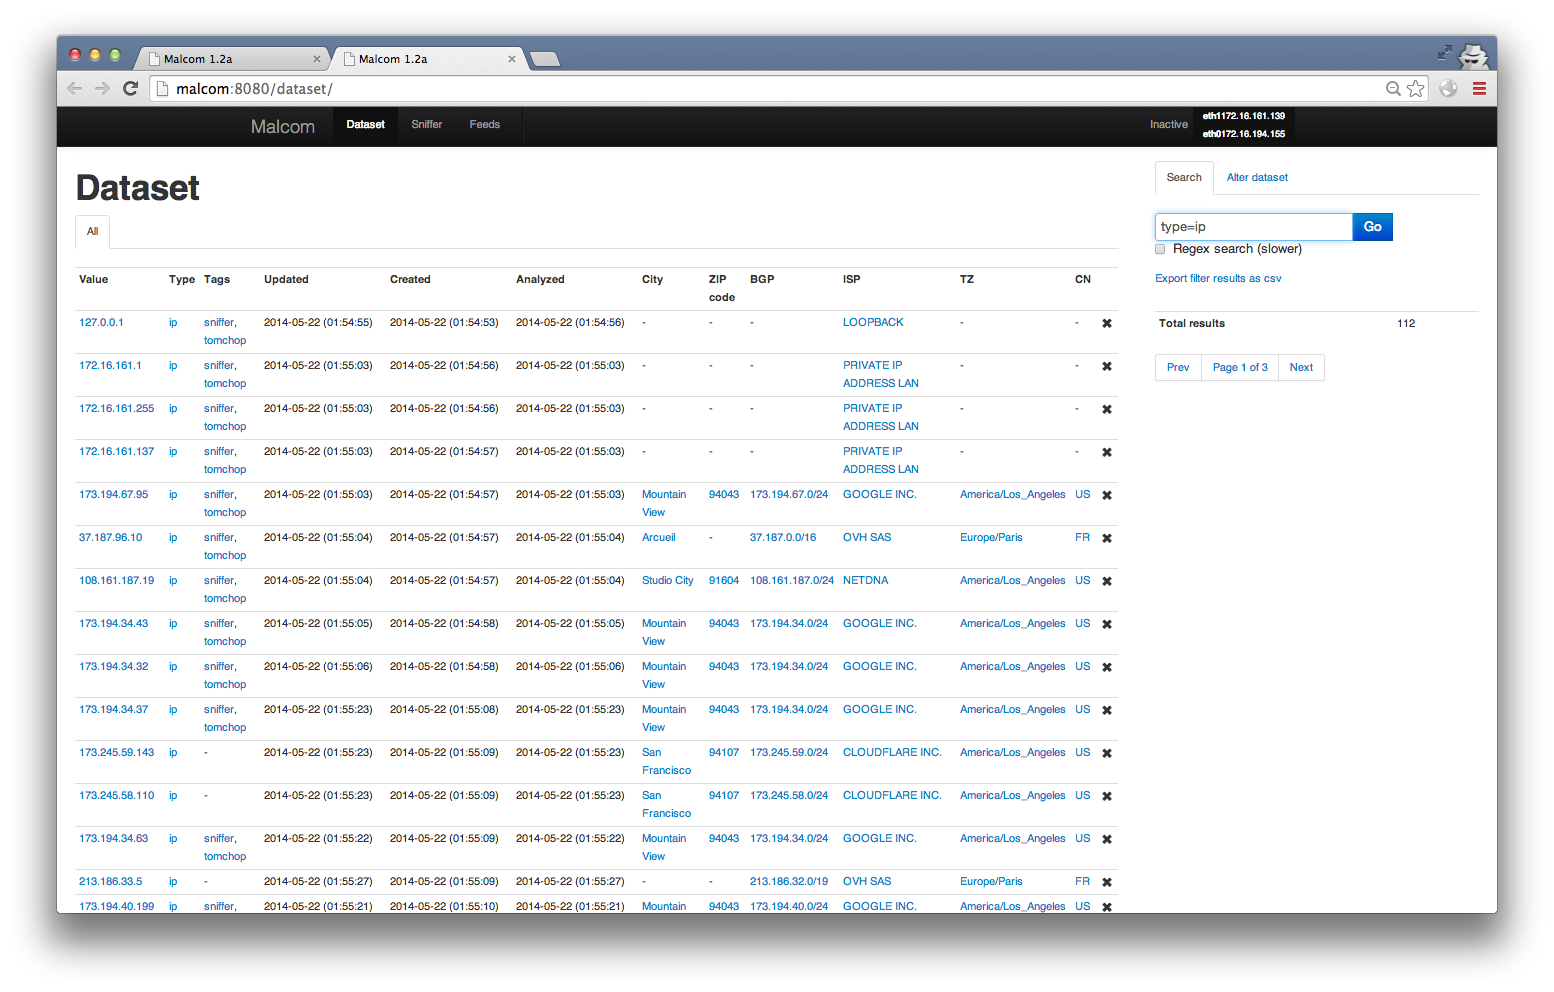 tomchop/malcom
Malcom - Malware Communications Analyzer

 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
 3lp4tr0n/beaconhunter
Detect and respond to Cobalt Strike beacons using ETW.
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
