
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
rengine preview

rengine

GitHubyogeshojha/rengine

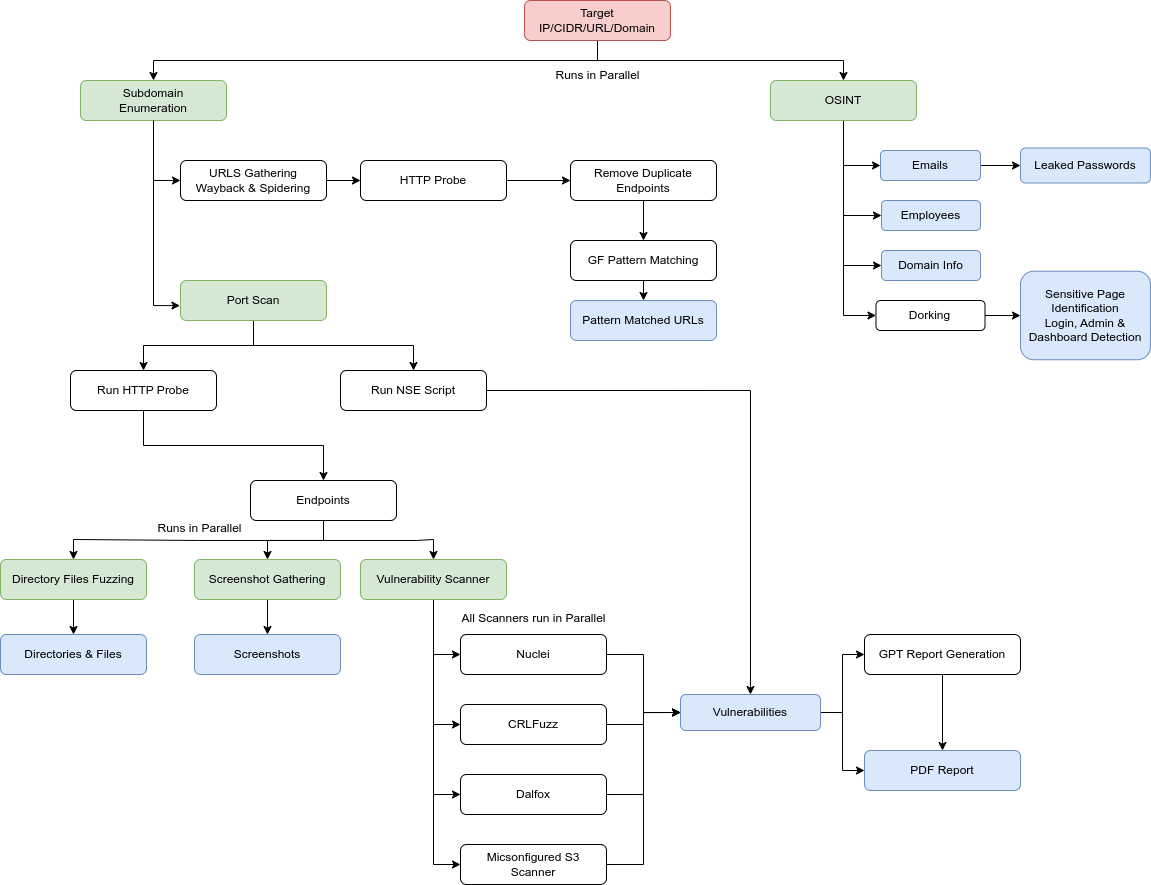
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
crawlerdns-subdomain-enumerationinformation-gathering+9
8.9k
10 months ago
decider preview

decider

GitHubcisagov/decider

A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…

curated-resourceseducationpenetration-testing+1
1.2k1 year ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

anomaly-detectiondigital-forensicsincident-response+5
7381 month ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

digital-forensicsdisk-forensicsforensics+7
37128 days ago
chiasmodon preview

chiasmodon

GitHubchiasmod0n/chiasmodon

Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
dns-subdomain-enumerationemail-harvestinginformation-gathering+5
7031 year ago
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

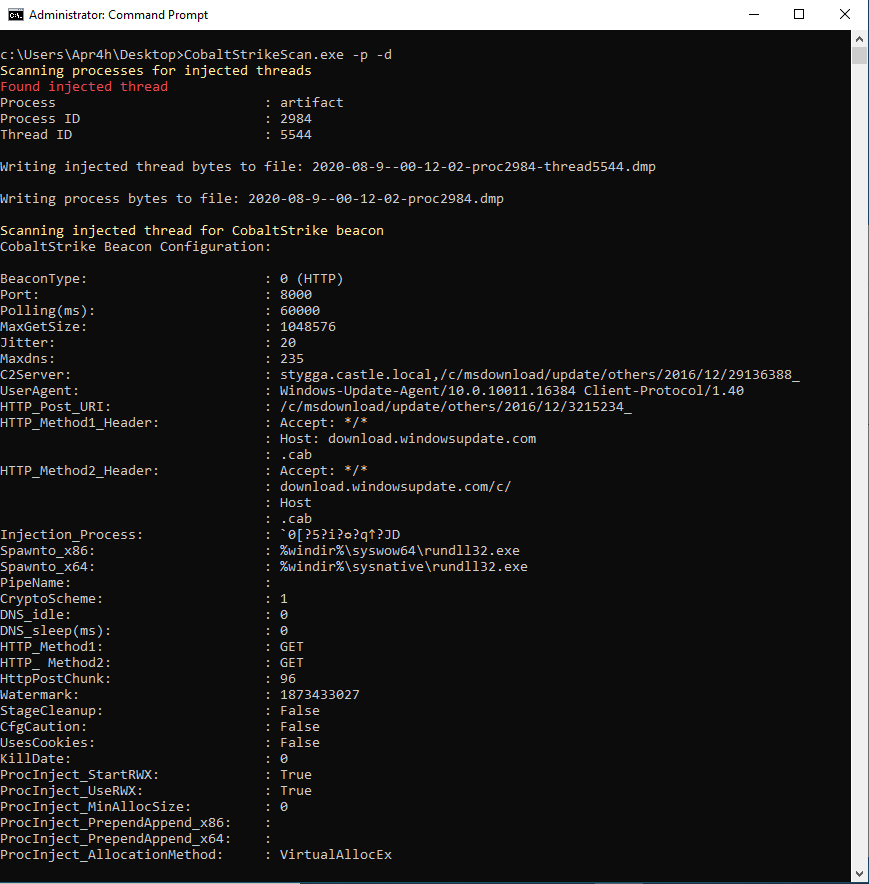
Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9165 years ago
clawdstrike preview

clawdstrike

GitHubbackbay-labs/clawdstrike

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…

ai-securitycloud-securitycontainer-security+5
2958 days ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3912 months ago
Skadi preview

Skadi

GitHuborlikoski/skadi

Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
curated-resourcesdigital-forensicsdisk-forensics+9
5203 years ago
aftermath preview

aftermath

GitHubjamf/aftermath

Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
digital-forensicsforensicsincident-response+3
6001 year ago
priority-intelligence-requirements-dev preview

priority-intelligence-requirements-dev

GitHubredhat-infosec/priority-intelligence-requirements-dev

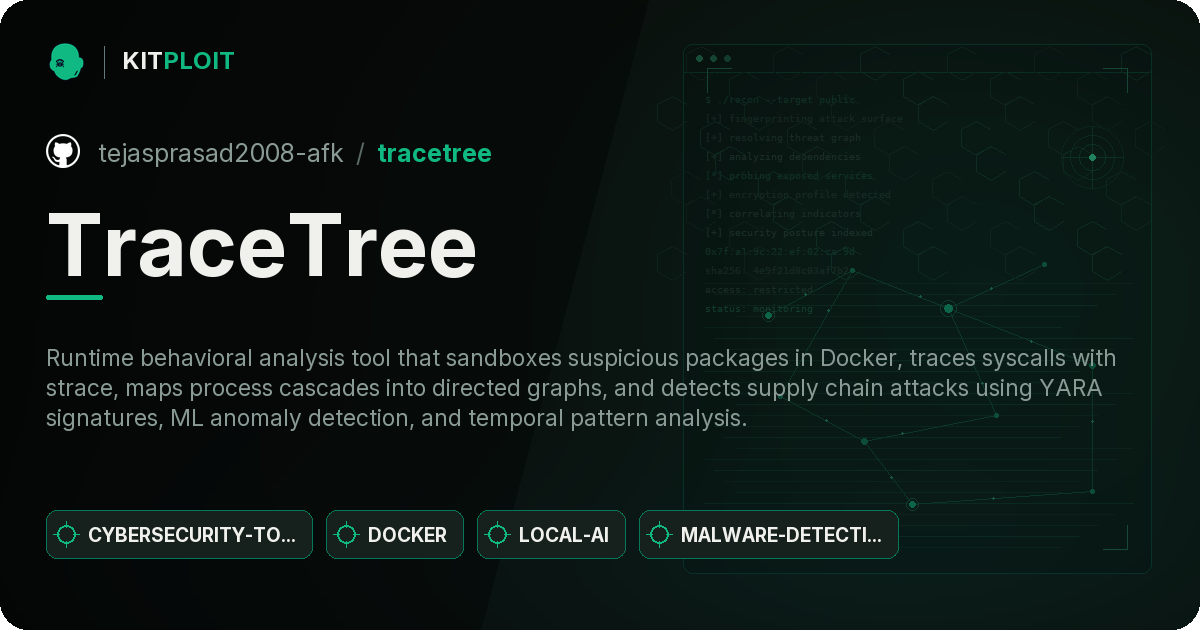
This guide describes a process for developing Cyber Threat Intelligence Priority Intelligence Requirements
educationlearning-paths-coursesthreat-intelligence
1282 years ago
TraceTree preview

TraceTree

GitHubtejasprasad2008-afk/tracetree

Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…

container-securitydevsecopsdynamic-analysis-sandboxing+6
4220 days ago
threat-modeling-playbook preview

threat-modeling-playbook

GitHubowasp/threat-modeling-playbook

Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…

curated-resourcesdevsecopseducation+3
414 years ago
IntelligentProcessLifecycle preview

IntelligentProcessLifecycle

GitHubd3sre/intelligentprocesslifecycle

The Intelligent Process Lifecycle of Active Cyber Defenders
configuration-auditingcurated-resourceseducation+6
343 years ago
BerrySentinel preview

BerrySentinel

GitHubdereeqw/berrysentinel

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
anomaly-detectioncommand-and-controldefensive-tools+8
137 months ago
SOC335---CVE-2024-49138-Exploitation-Detected preview

SOC335---CVE-2024-49138-Exploitation-Detected

GitHubfabianch20/soc335---cve-2024-49138-exploitation-detected

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

digital-forensicseducationincident-response+7
21 days ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
exploitationincident-responselog-analysis+3
84 years ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

binary-analysiseducationforensics+7
32 months ago
Previous123Next