

ICS-Security-Tools
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
curated-resourcesdefensive-toolseducation+4
2.1k
iti/ics-security-toolsTools, tips, tricks, and more for exploring ICS Security.
 wddadk/offensive-osint-tools
Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
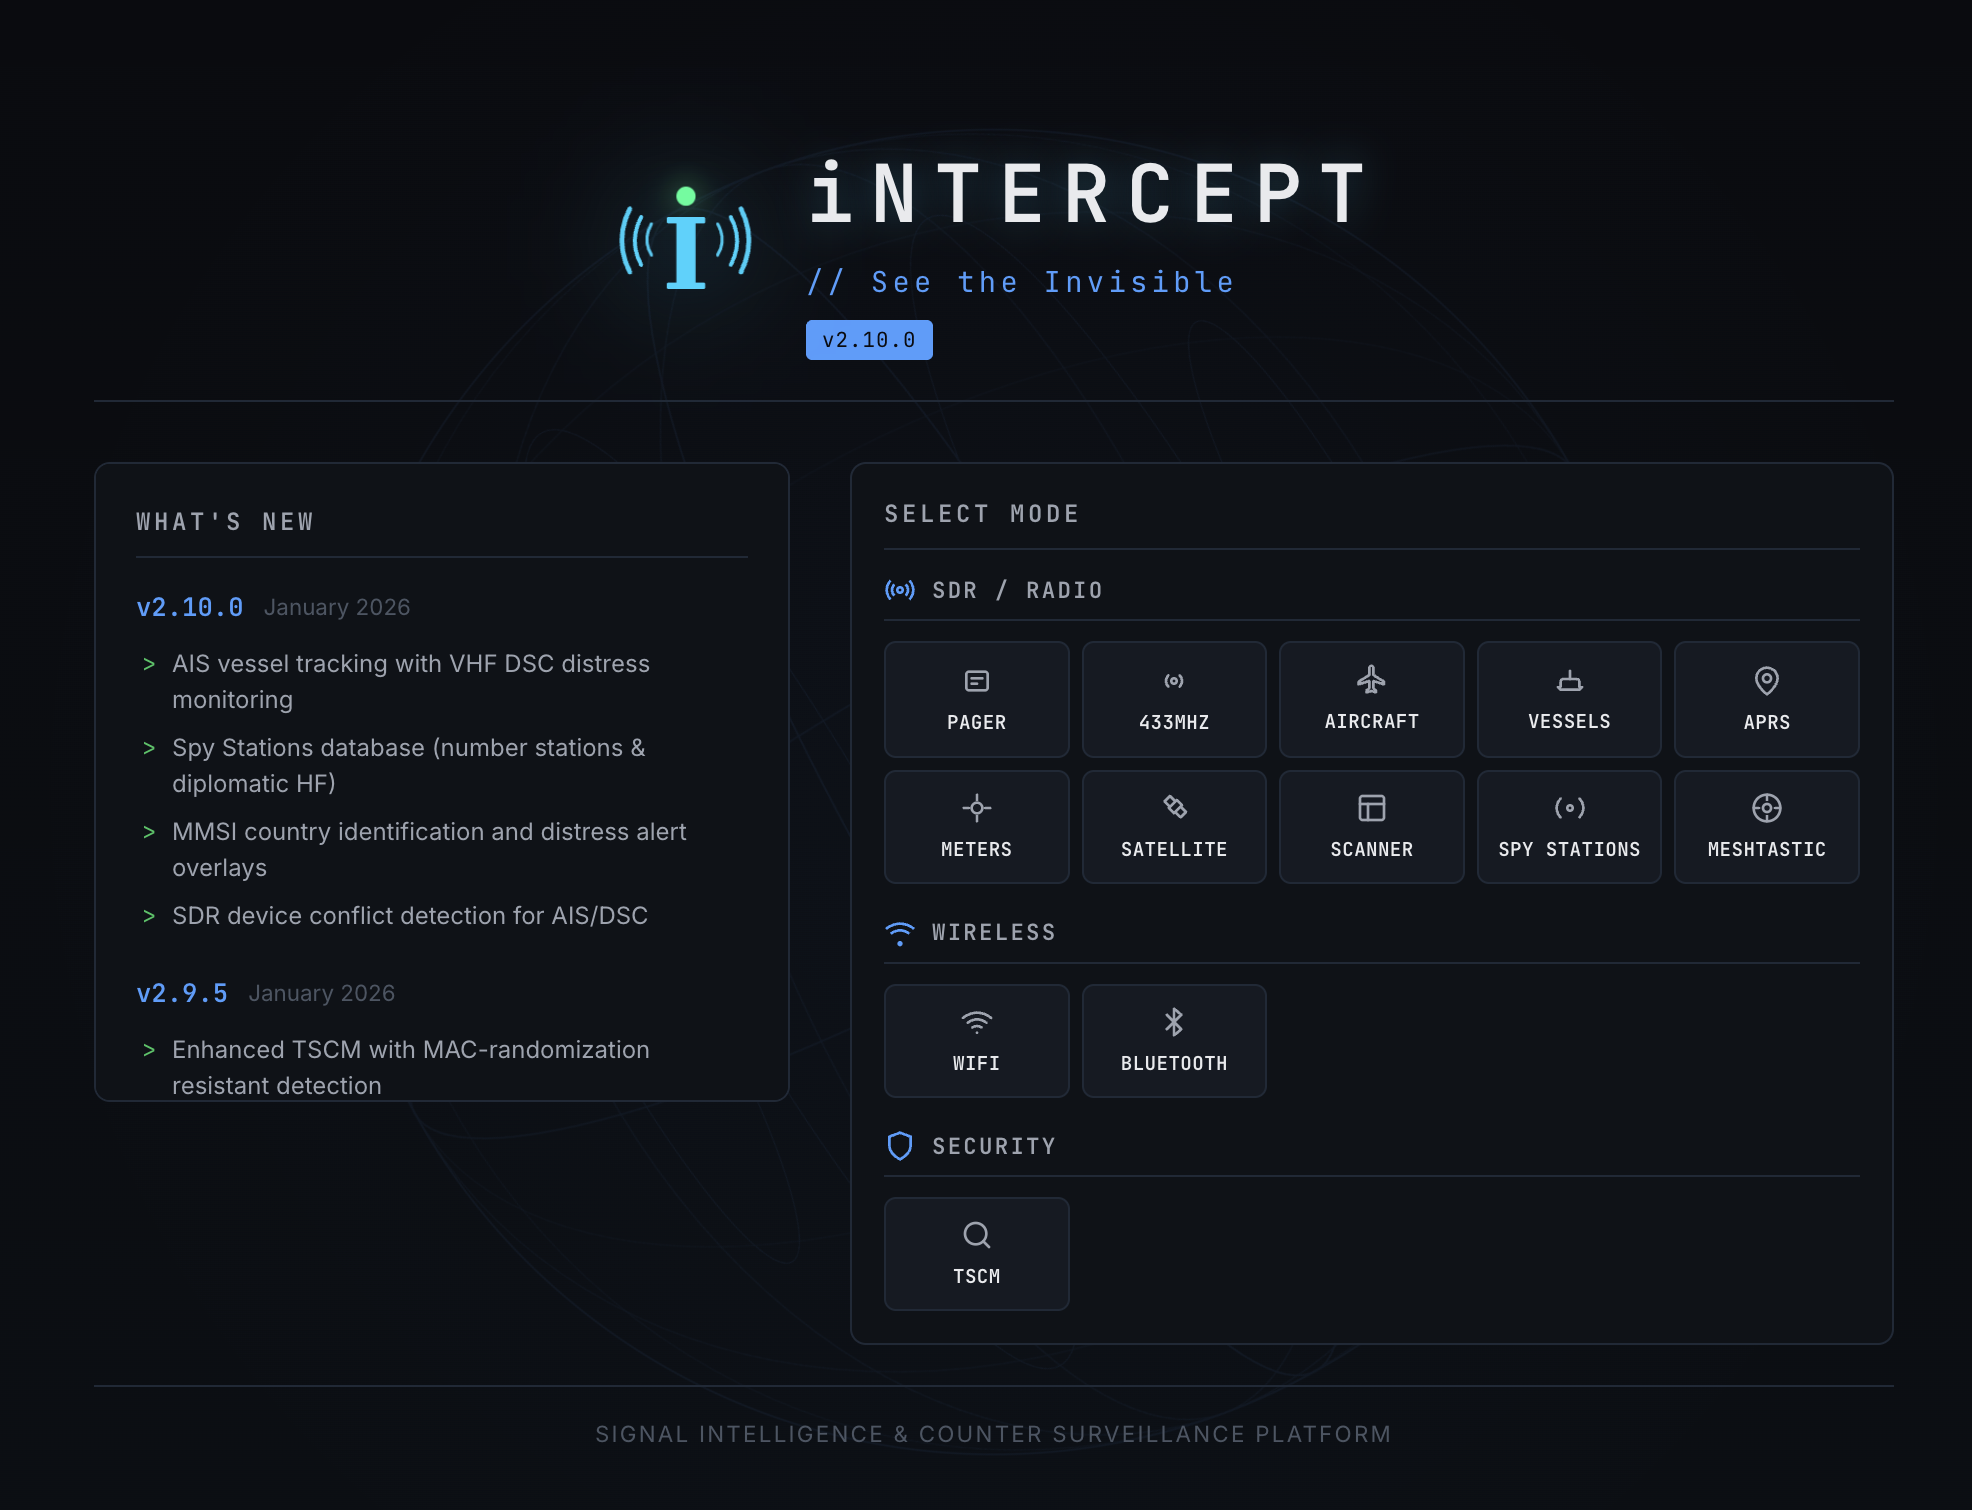 smittix/intercept
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
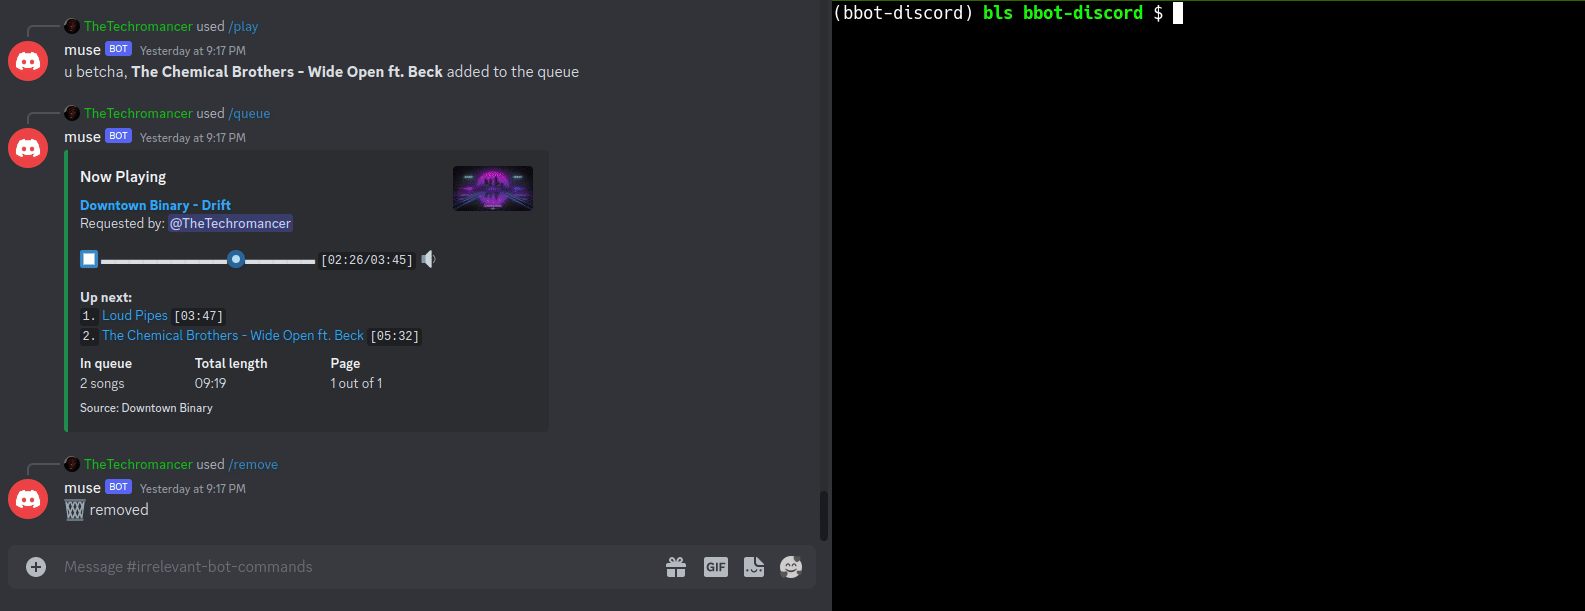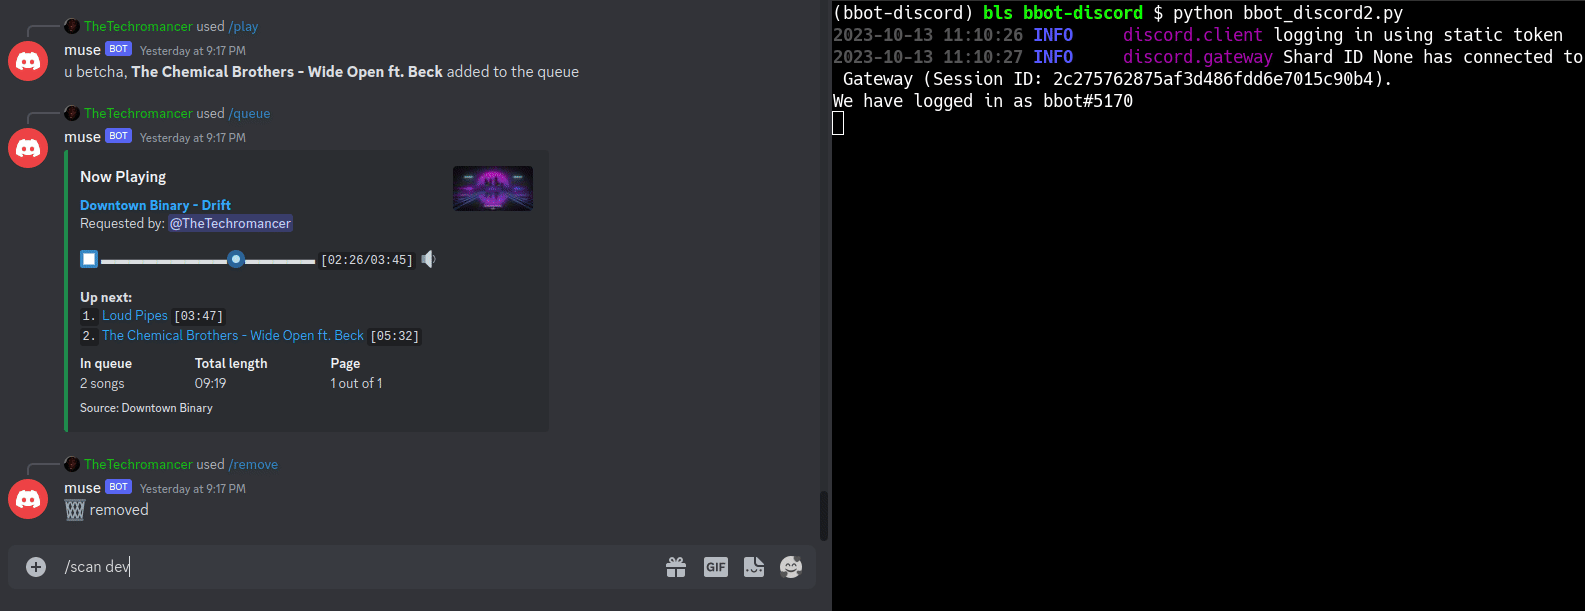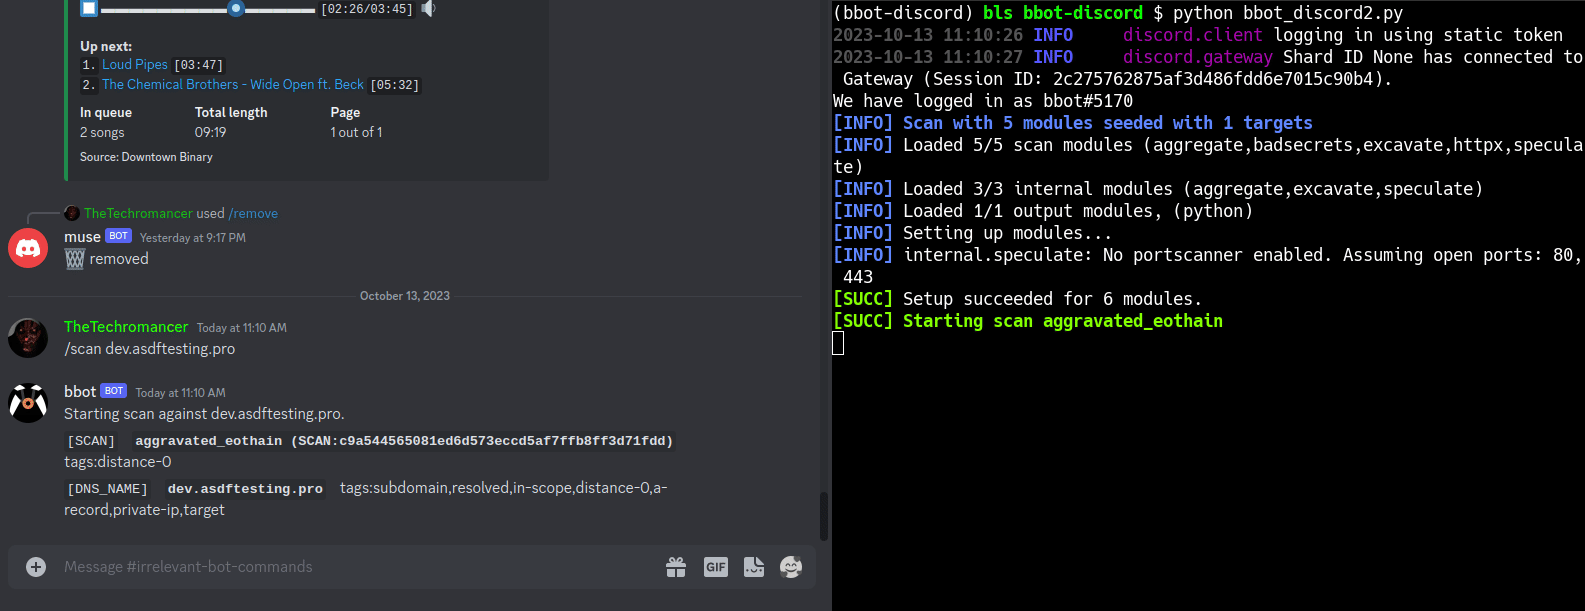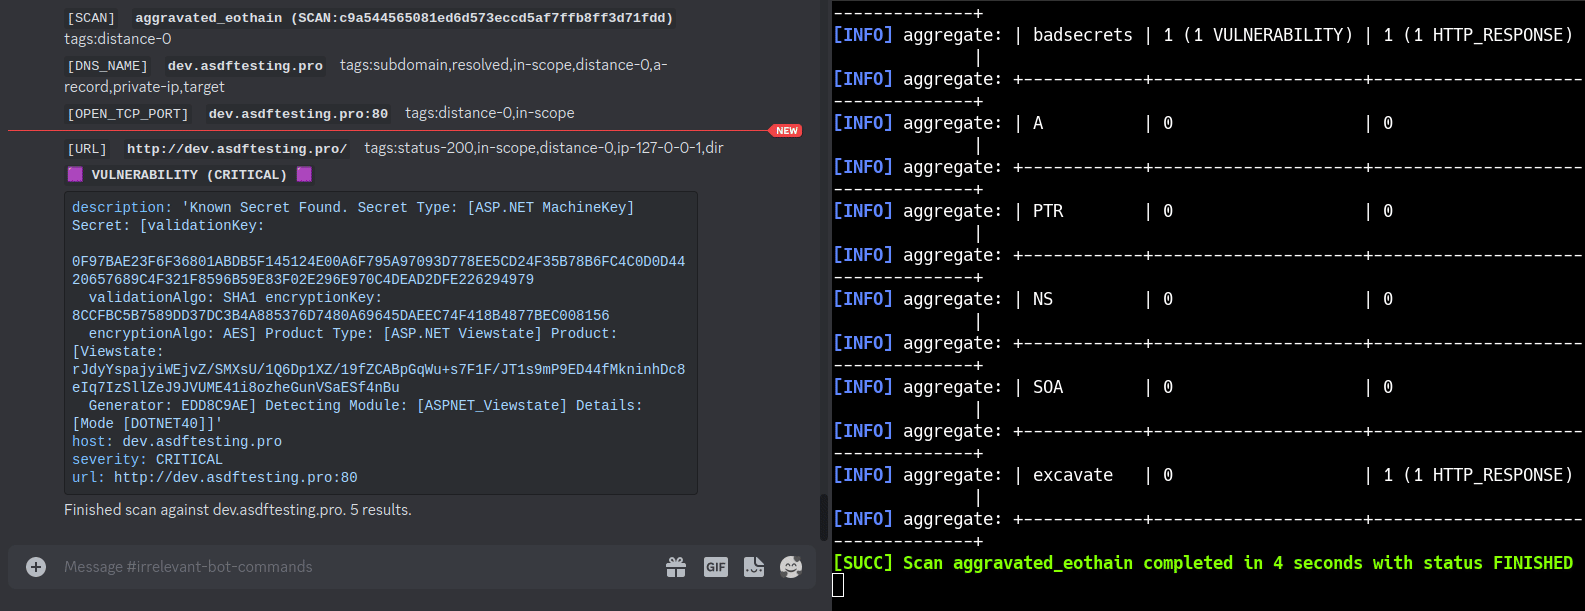 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡
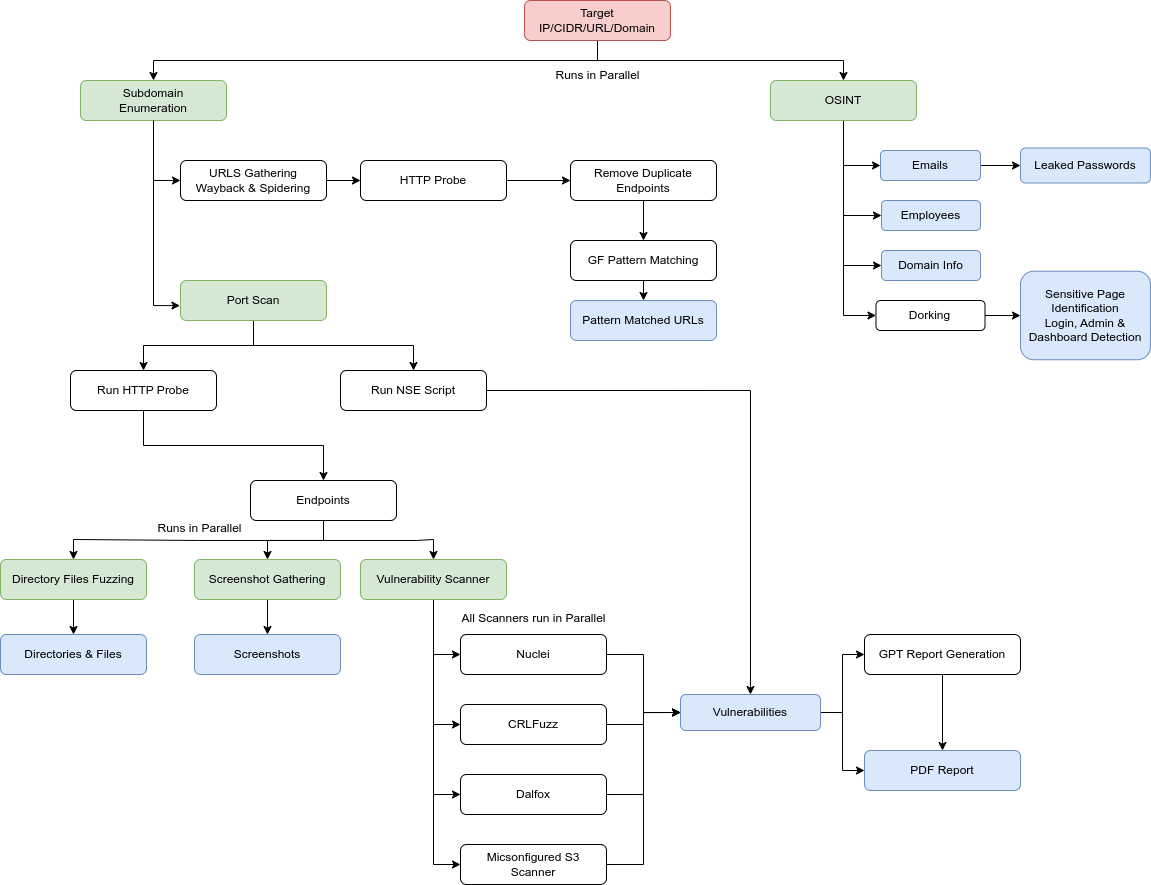 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 khast3x/h8mail
Email OSINT & Password breach hunting tool, locally or using premium services. Supports chasing down related email
 bhavsec/reconspider
🔎 Most Advanced Open Source Intelligence (OSINT) Framework for scanning IP Address, Emails, Websites, Organizations.
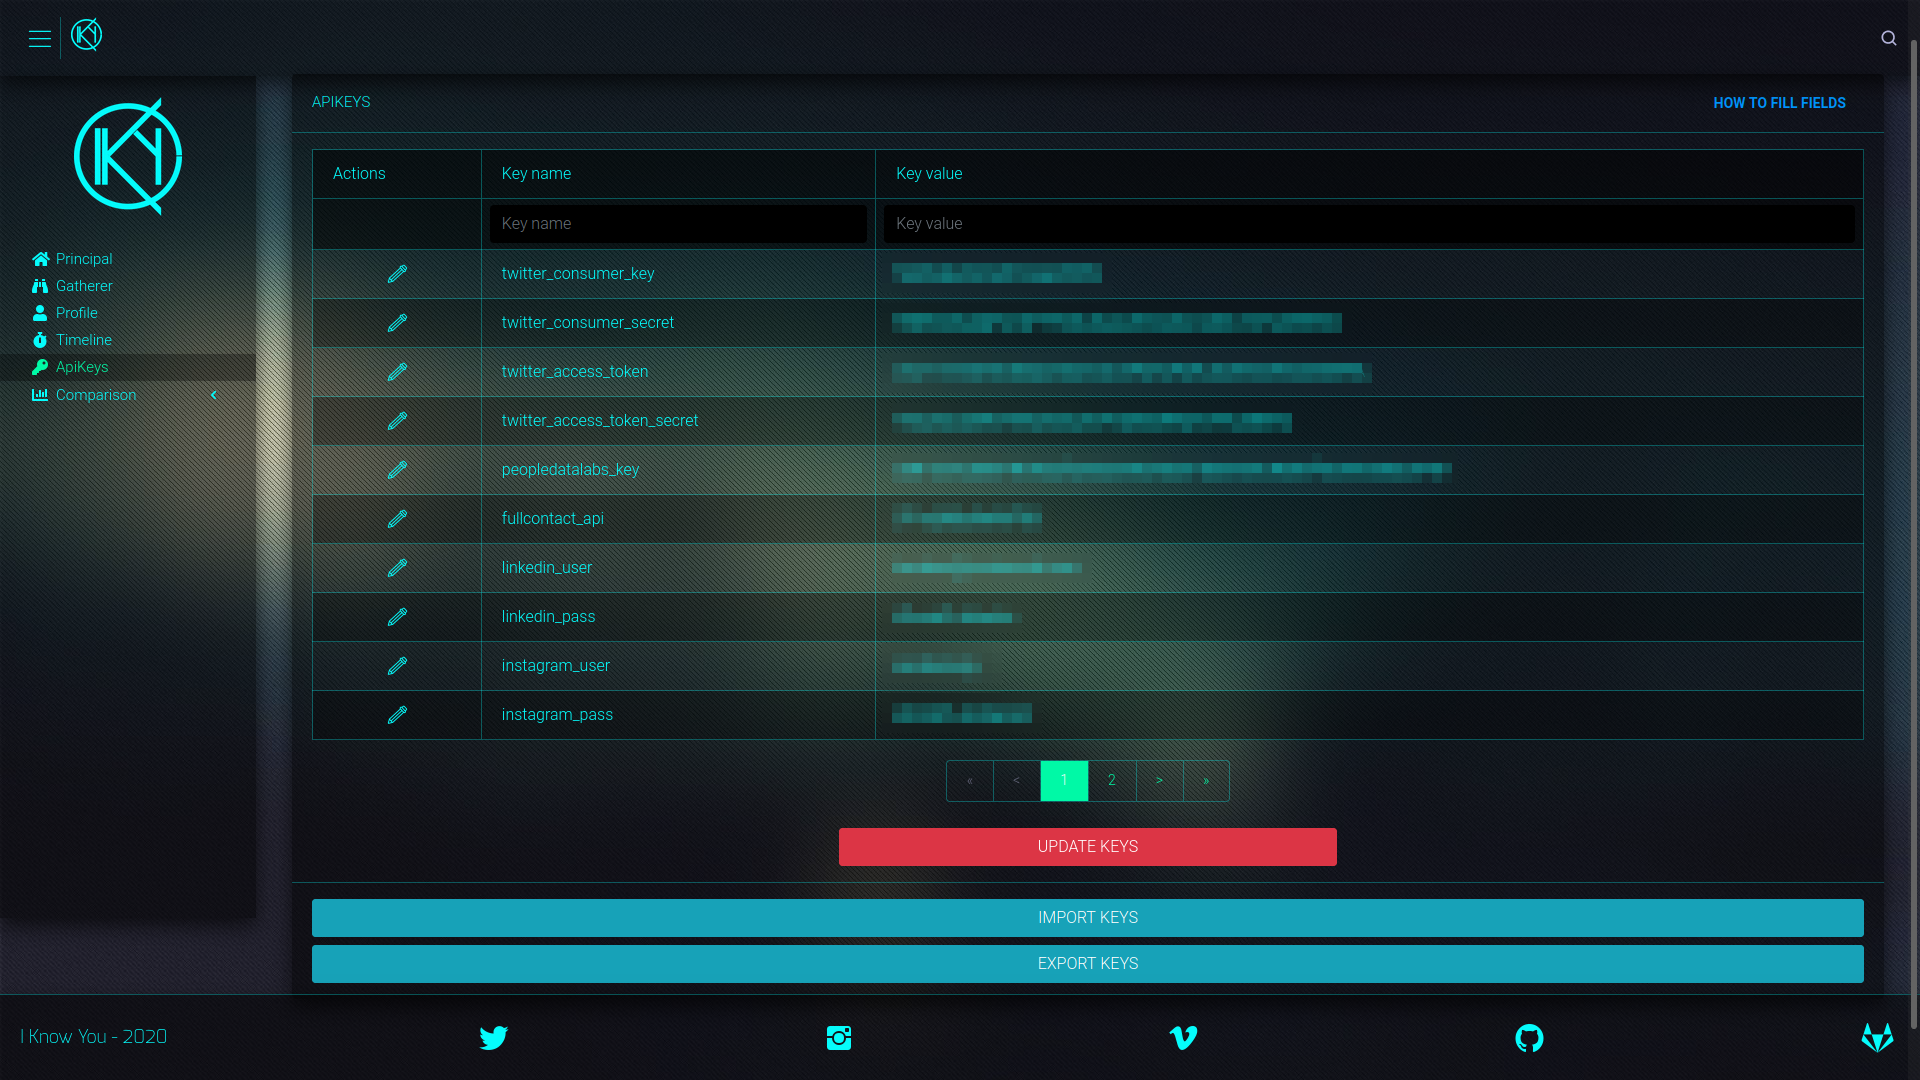 kennbroorg/iky
OSINT Project. Collect information from a mail. Gather. Profile. Timeline.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
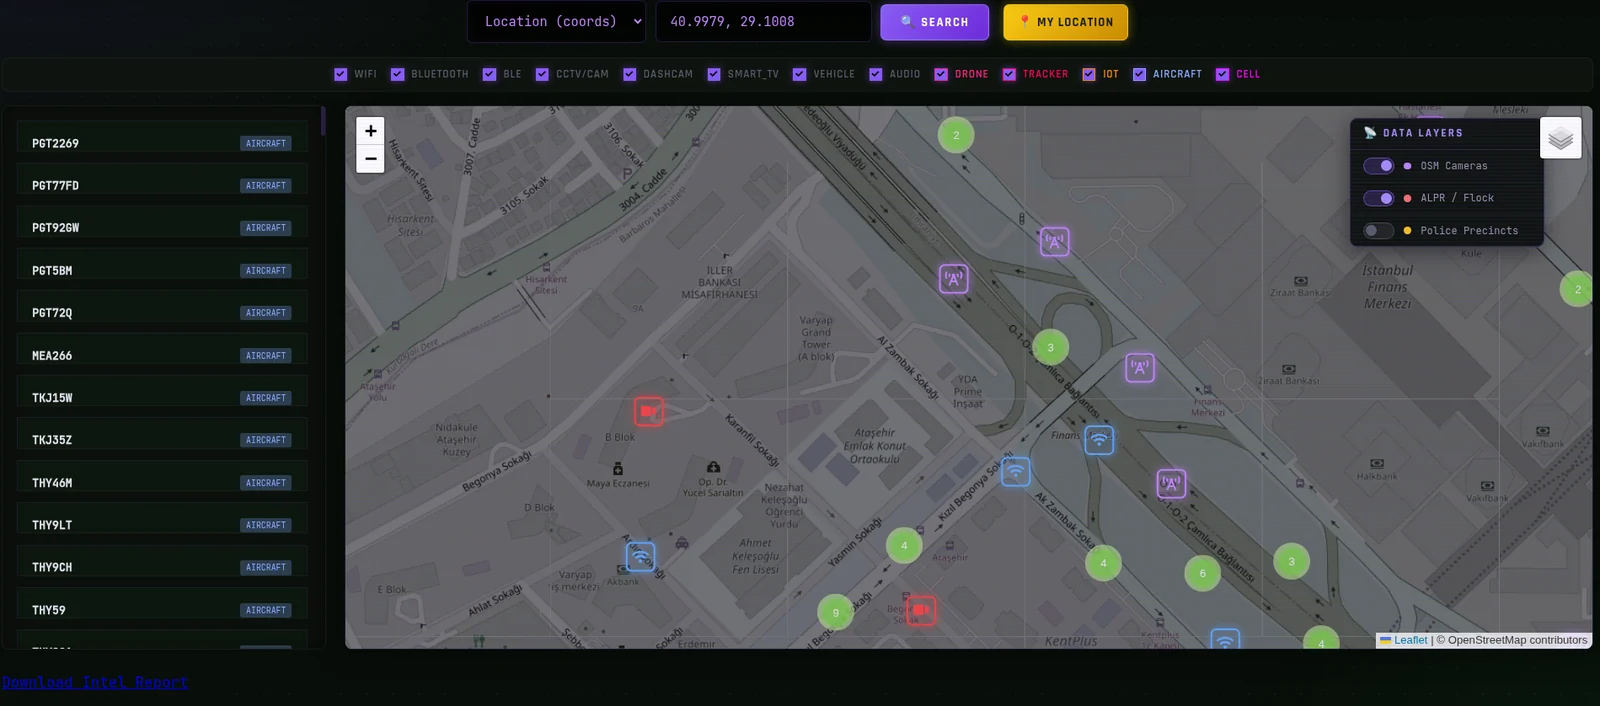 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 s_r_e_e_r_a_j/netspecter
NetSpecter is a lightweight yet powerful asynchronous OSINT and reconnaissance engine built in Python.
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
 pwnedshell/bugs-feed
Bug's feed is a local hosted portal where you can search for the latest news, videos, CVEs, vulnerabilities...
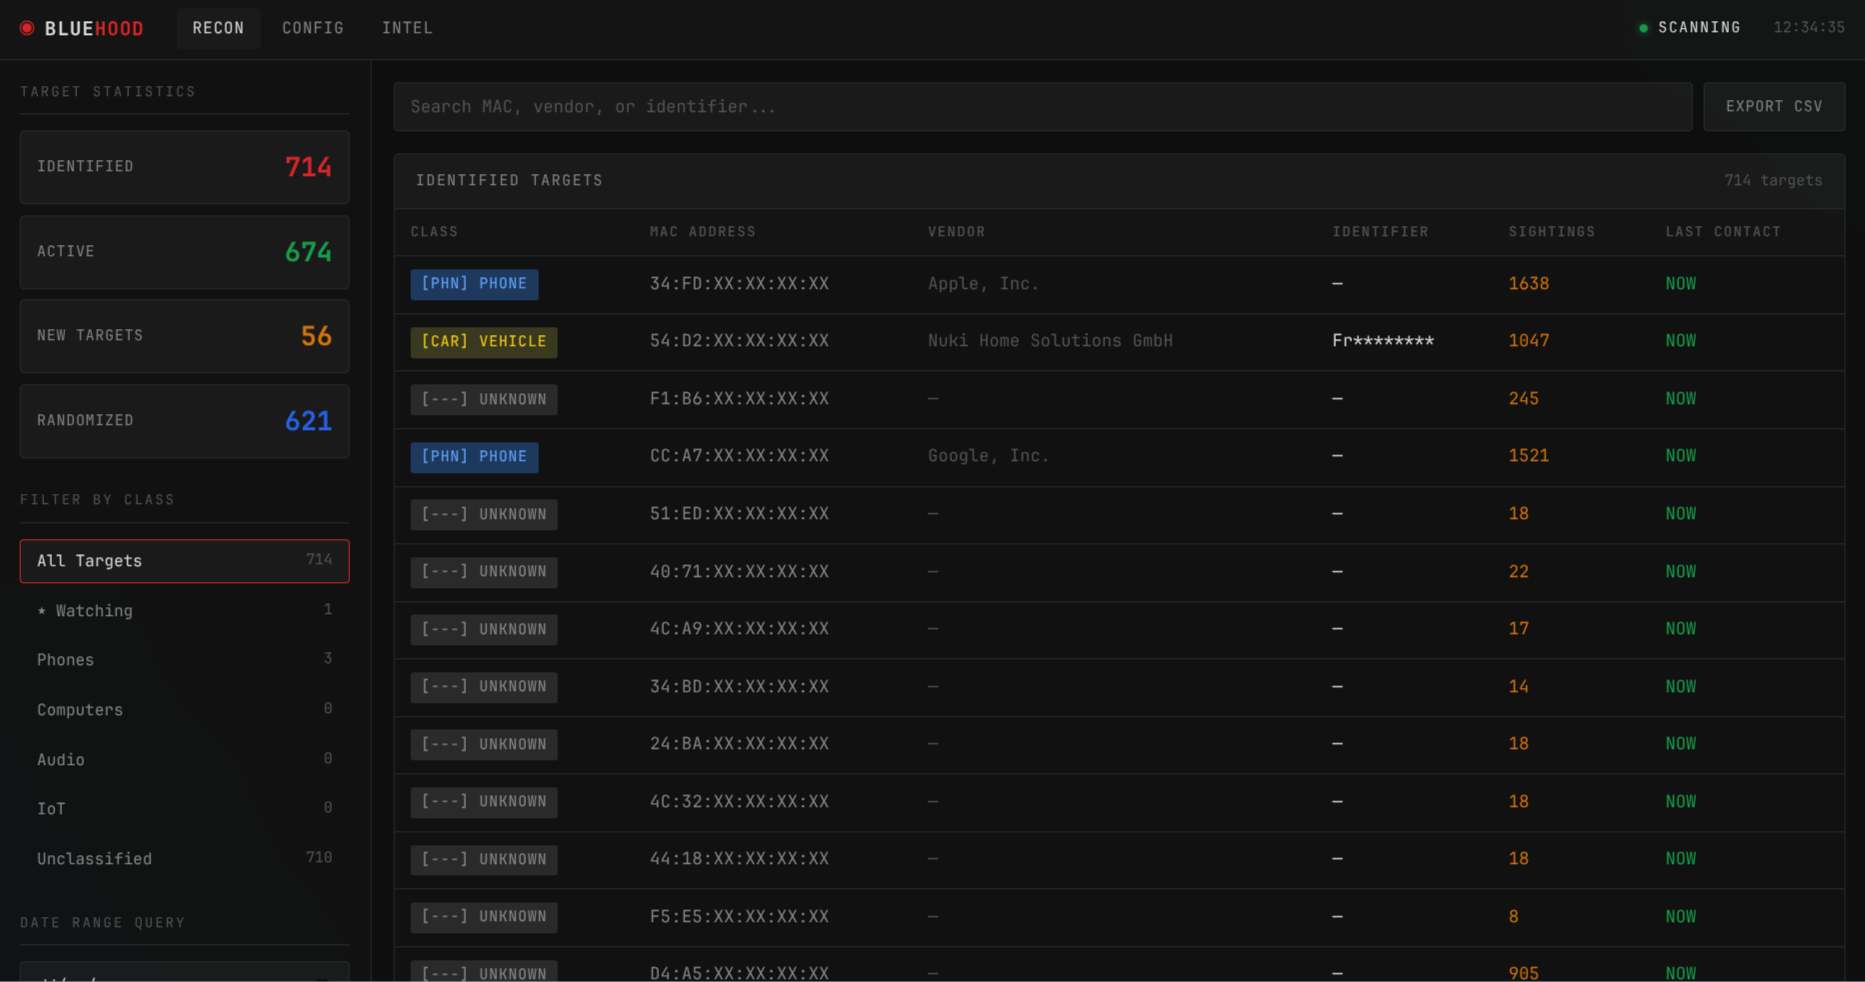 dannymcc/bluehood
Monitor your local neighbourhood's bluetooth activity
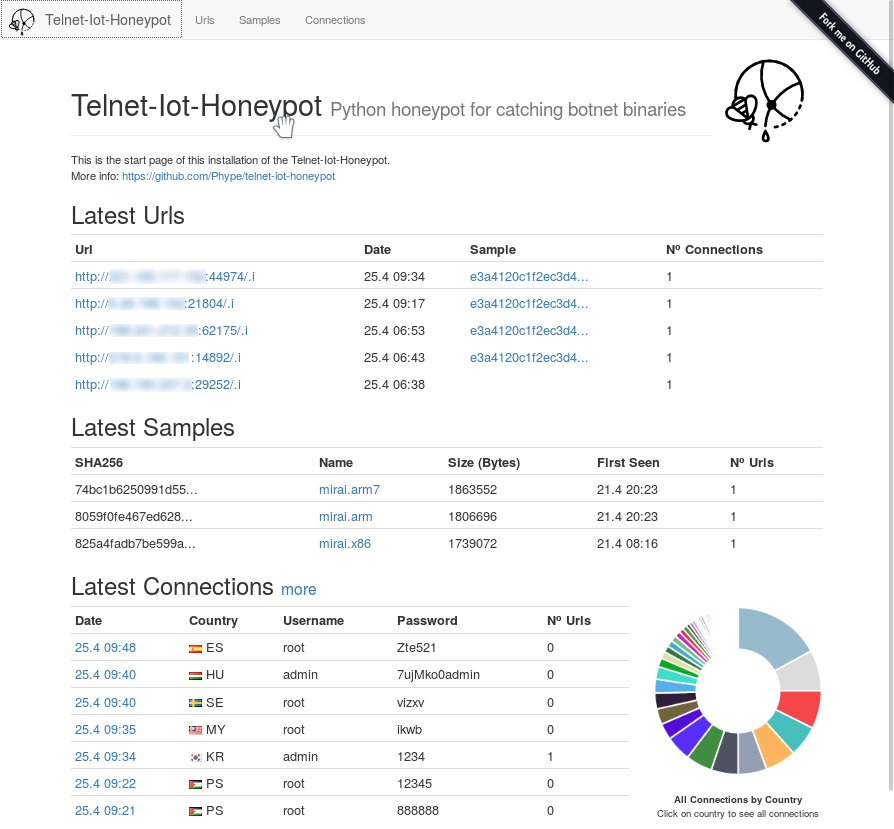 phype/telnet-iot-honeypot
Python telnet honeypot for catching botnet binaries
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.