Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

digital-forensicsdisk-forensicsforensics+6
820
4 months ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…

digital-forensicsforensicsnetwork-forensics+3
1024 years ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

anomaly-detectiondigital-forensicsincident-response+5
32 months ago
opencanary preview

opencanary

GitHubthinkst/opencanary

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…

defensive-toolsincident-responseintrusion-detection+3
3.1k18 days ago
community-id-spec preview

community-id-spec

GitHubcorelight/community-id-spec

An open standard for hashing network flows into identifiers, a.k.a "Community IDs".

digital-forensicsincident-responseintrusion-detection+4
1982 years ago
squidmagic preview

squidmagic

GitHubaws-alchemy/squidmagic

analyze a web-based network traffic 🕶 to detect central command and control servers

command-and-controldns-analysisincident-response+3
818 years ago
FLAIR preview

FLAIR

GitHubwithsecurelabs/flair

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…

digital-forensicsforensicsincident-response+2
165 years ago
CorelightForSplunk preview

CorelightForSplunk

GitHubcorelight/corelightforsplunk

Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.

anomaly-detectionincident-responselog-analysis+4
21 year ago
cve-2026-22557-unifi-detection preview

cve-2026-22557-unifi-detection

GitHubgarethmsheldon/cve-2026-22557-unifi-detection

Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…

intrusion-detectionlog-analysisthreat-intelligence+1
6 months ago
thelightscope preview

thelightscope

GitHubthelightscope/thelightscope

TheLightScope

defensive-toolsincident-responseintrusion-detection+5
706h 1m ago
ACF preview

ACF

GitHubcyberhatcoil/acf

Android Connections Forensics

digital-forensicsmobile-forensicsnetwork-forensics+2
3310 years ago
BlueTeam-Tools preview

BlueTeam-Tools

GitHuba-poc/blueteam-tools

Tools and Techniques for Blue Team / Incident Response

curated-resourcesdata-recoverydefensive-tools+8
4.5k1 month ago
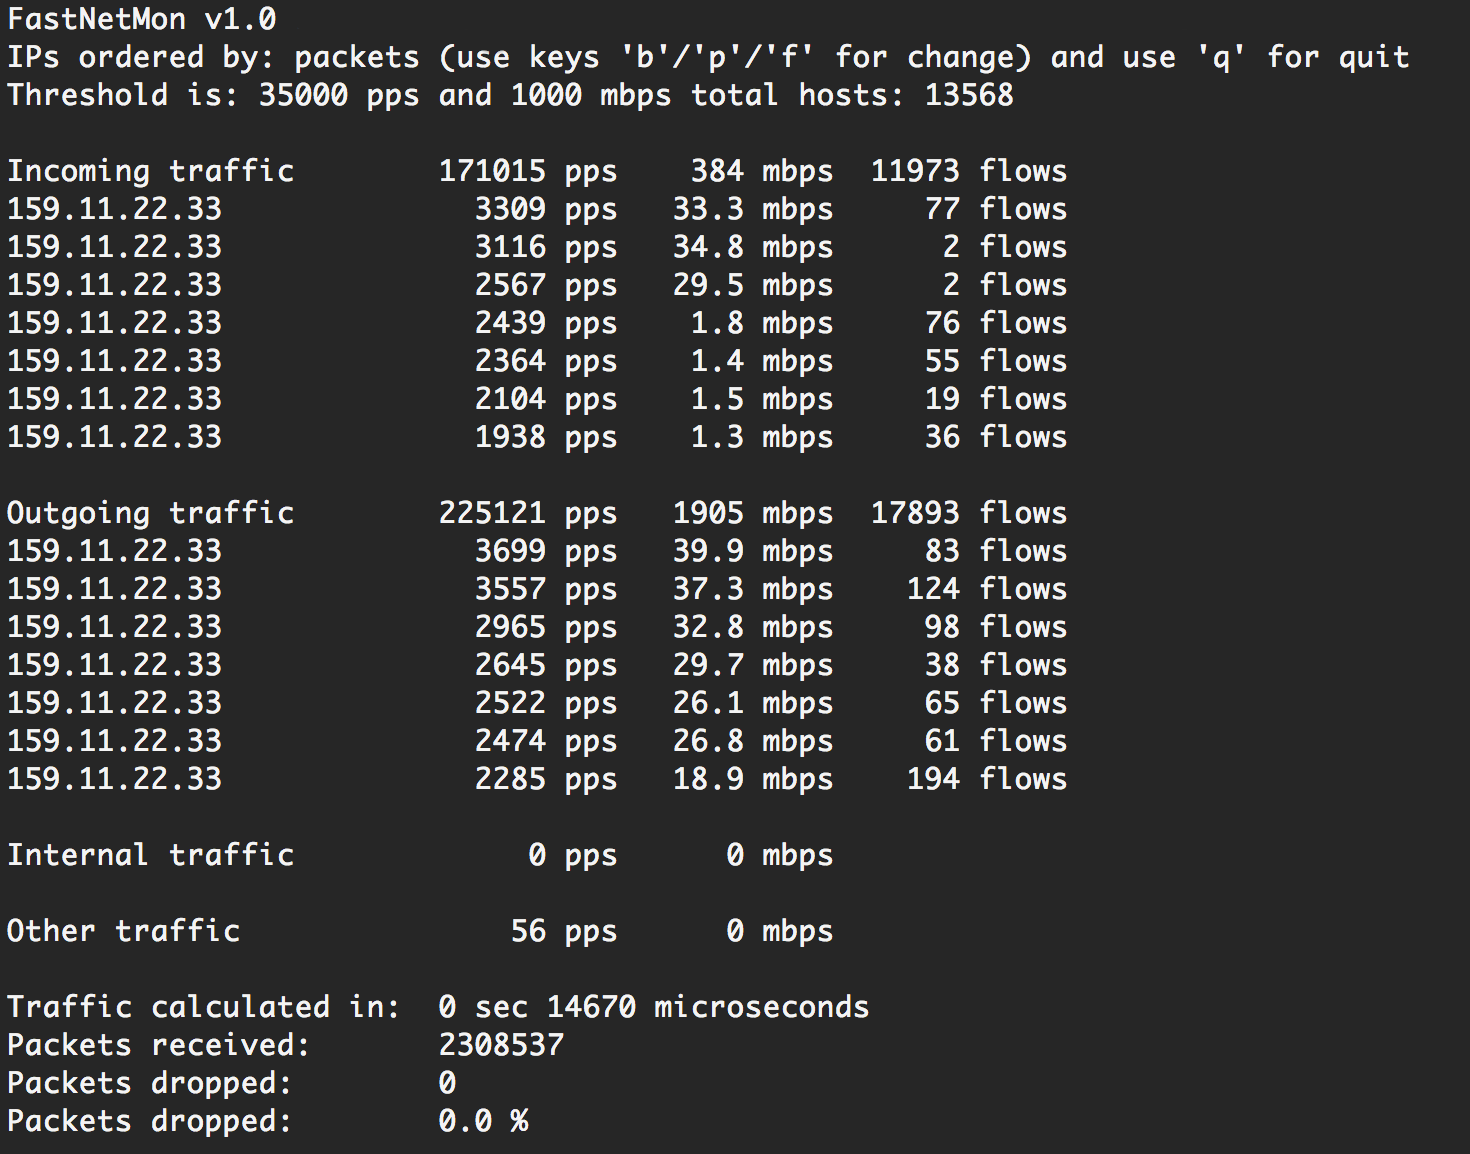
fastnetmon preview

fastnetmon

GitHubpavel-odintsov/fastnetmon

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

anomaly-detectionincident-responselog-analysis+5
3.7k1 month ago
DeTTECT preview

DeTTECT

GitHubrabobank-cdc/dettect

Detect Tactics, Techniques & Combat Threats

defensive-toolsincident-responseintrusion-detection+4
2.3k25 days ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k18h 53m ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:

data-recoverydigital-forensicsdisk-forensics+9
1.4k1 month ago
tenzir preview

tenzir

GitHubtenzir/tenzir

Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…

incident-responselog-analysisnetwork-security+1
7629h 50m ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

anomaly-detectiondigital-forensicsincident-response+5
7381 month ago
Previous1234Next