
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
814 results
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
6854 years ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1034 years ago
misp-wireshark preview

misp-wireshark

GitHubmisp/misp-wireshark

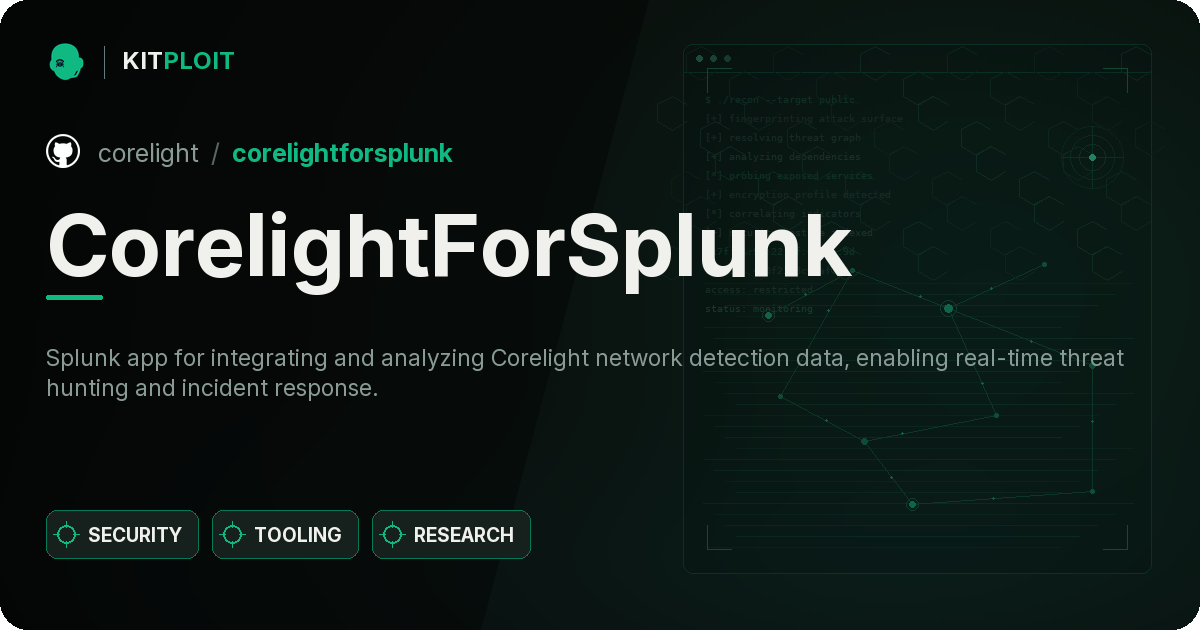
Lua plugin to extract data from Wireshark and convert it into MISP format
digital-forensicsforensicsnetwork-forensics+2
503 years ago
CorelightForSplunk preview

CorelightForSplunk

GitHubcorelight/corelightforsplunk

Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
anomaly-detectionincident-responselog-analysis+4
21 year ago
malcom preview

malcom

GitHubtomchop/malcom

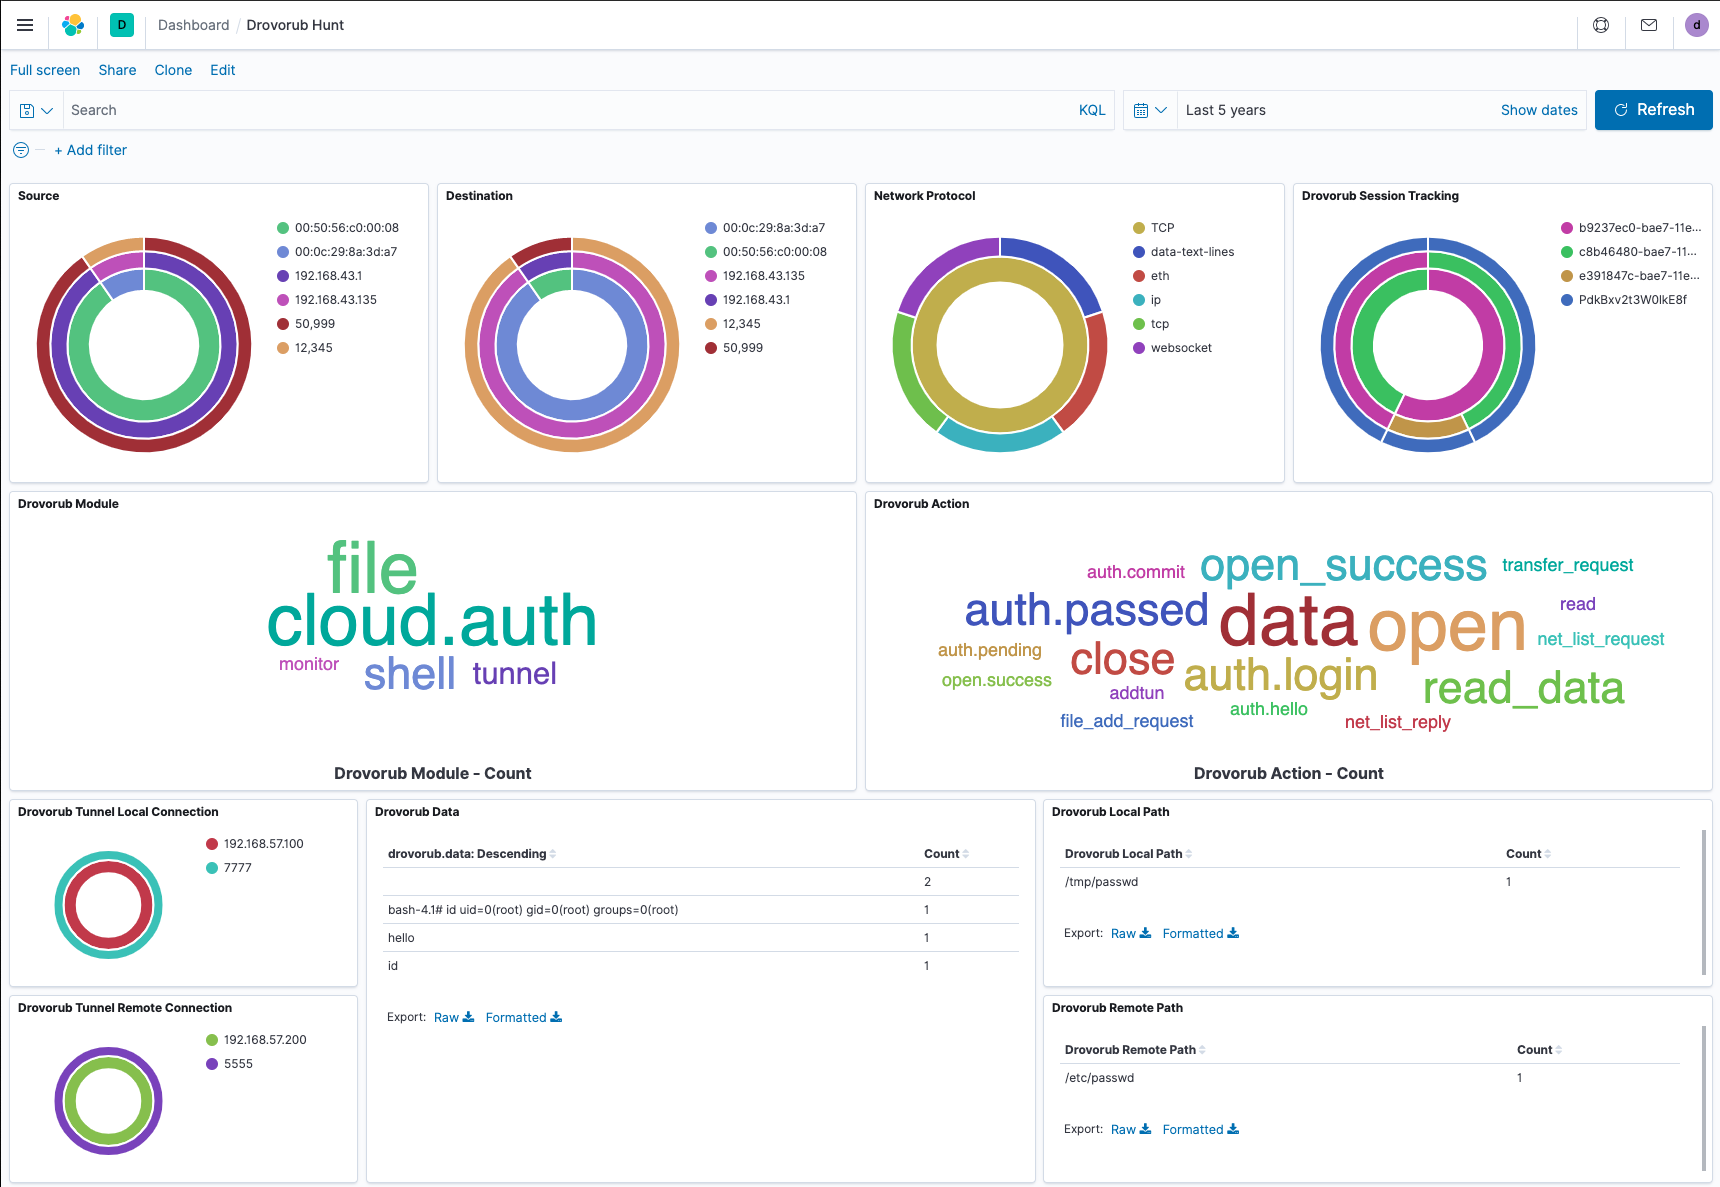
Malcom - Malware Communications Analyzer
malware-analysisnetwork-forensicsthreat-intelligence
1.2k8 years ago
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

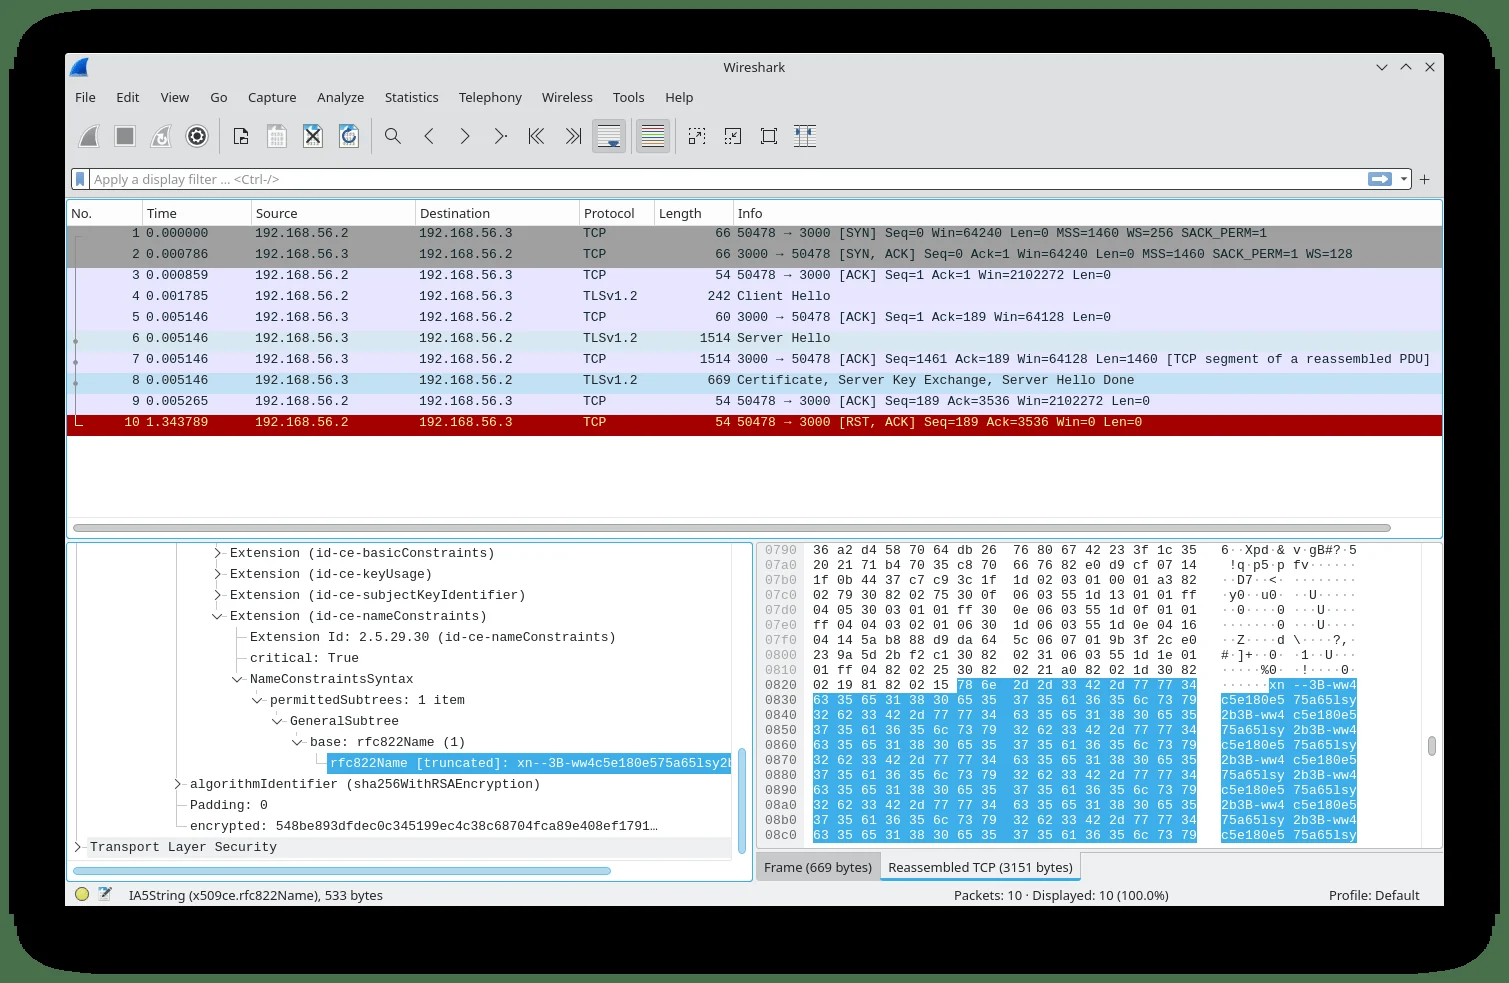
A tool to assist with network-based hunting for GRU's Drovorub malware c2
incident-responseintrusion-detectionmalware-analysis+3
256 years ago
spookyssl-pcaps preview

spookyssl-pcaps

GitHubfox-it/spookyssl-pcaps

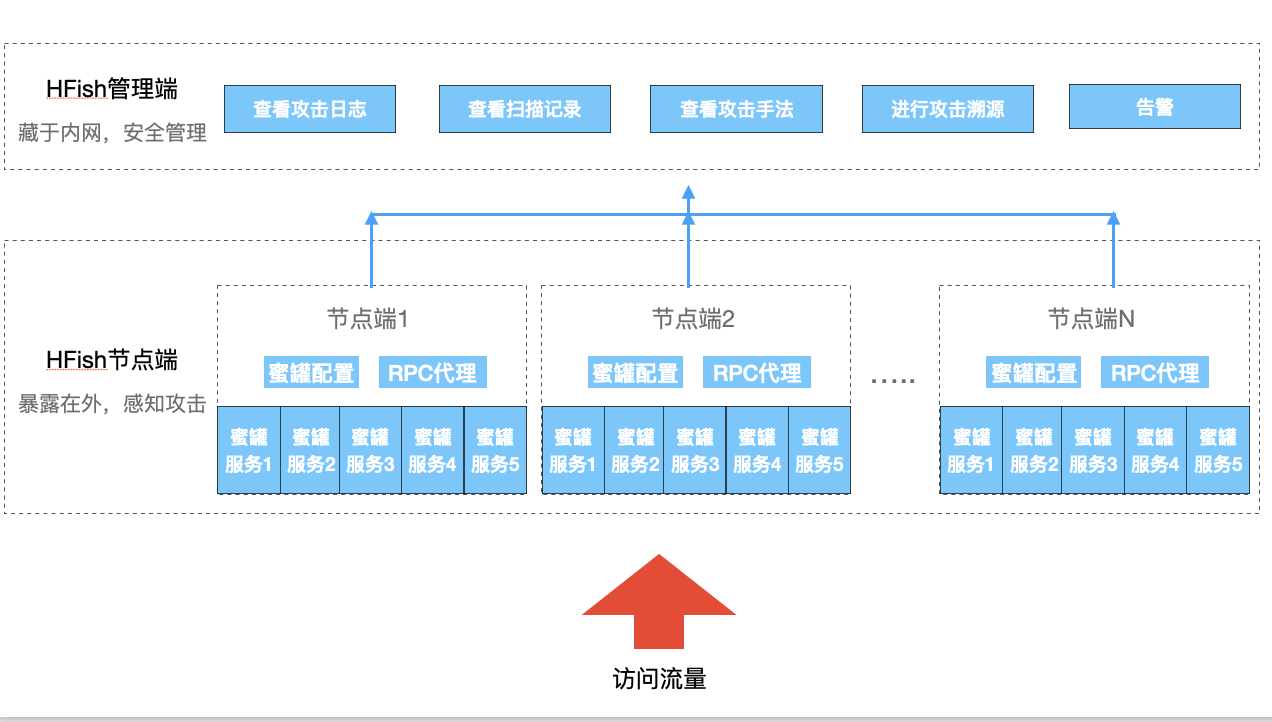
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
intrusion-detectionnetwork-securitypacket-sniffing-analysis+2
103 years ago
HFish preview

HFish

GitHubhacklcx/hfish

Enterprise-grade honeypot system for detecting internal network breaches, external threats, and producing threat intelligence with 90+ service…
defensive-toolsintrusion-detectionnetwork-security+1
4.6k7 months ago
tenzir preview

tenzir

GitHubtenzir/tenzir

Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…

incident-responselog-analysisnetwork-security+1
76920h 6m ago
Zeek-Intelligence-Feeds preview

Zeek-Intelligence-Feeds

GitHubcriticalpathsecurity/zeek-intelligence-feeds

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
command-and-controlintrusion-detectionnetwork-security+3
4068h 53m ago
dionaea preview

dionaea

GitHubdinotools/dionaea

Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
defensive-toolsintrusion-detectionmalware-analysis+2
8205 years ago
scirius preview

scirius

GitHubstamusnetworks/scirius

Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
defensive-toolsintrusion-detectionnetwork-security+3
6851 year ago
SentryPeer preview

SentryPeer

GitHubsentrypeer/sentrypeer

Distributed SIP honeypot that detects and shares fraud data on VoIP attacks. Collects bad actor IPs and phone numbers via peer-to-peer network, with…
api-securitynetwork-securitythreat-intelligence
2125 days ago
HASH preview

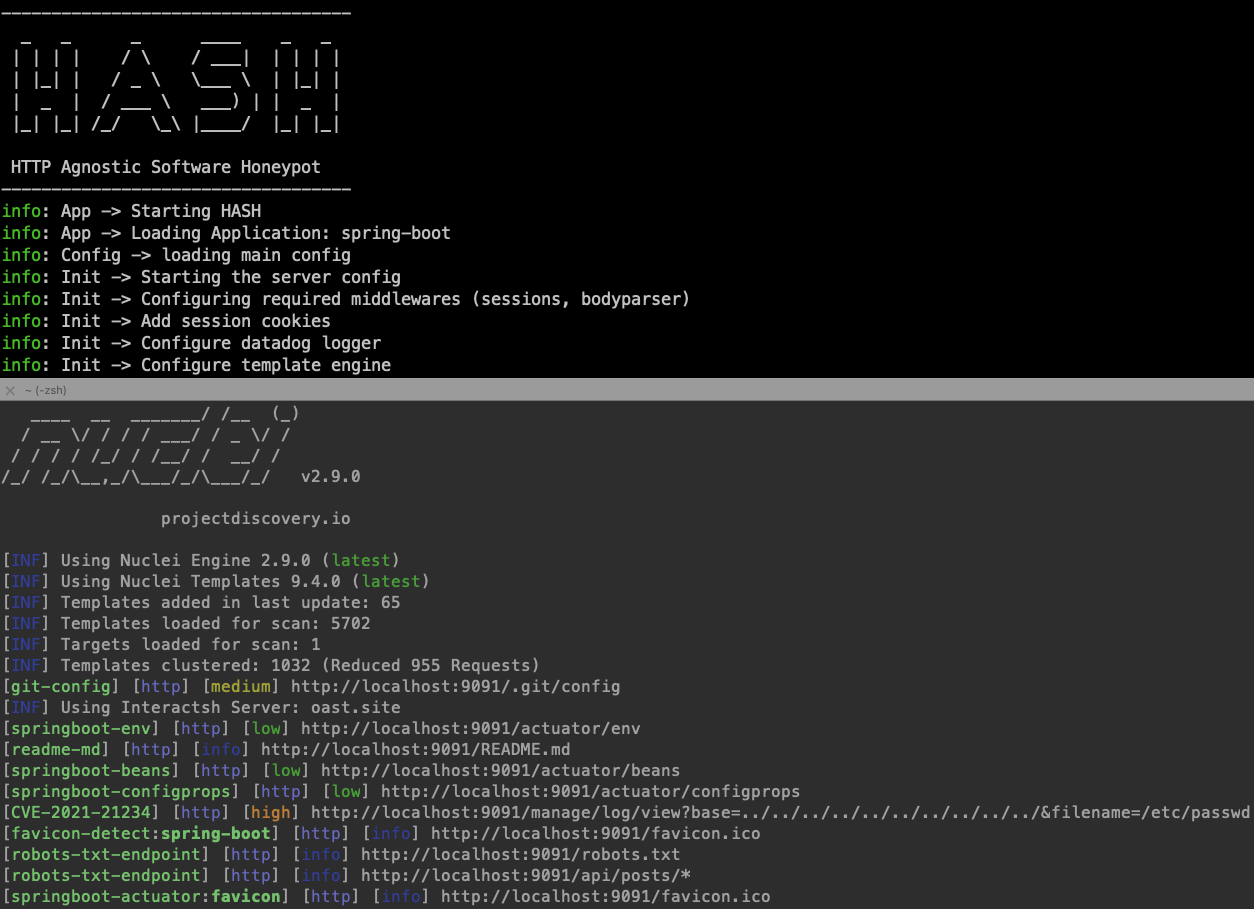
HASH

GitHubdatadog/hash

YAML-configurable low-interactive honeypot framework for deploying HTTP/HTTPS-based deception servers with built-in honeytraps and Datadog log…
defensive-toolsnetwork-securitythreat-intelligence+1
14218h 36m ago
log4j-honeypot-flask preview

log4j-honeypot-flask

GitHubbinarydefense/log4j-honeypot-flask

Internal network honeypot for detecting if an attacker or insider threat scans your network for log4j CVE-2021-44228
defensive-toolsintrusion-detectionnetwork-security+2
1494 years ago
fastfluxanalysis preview

fastfluxanalysis

GitHubstaaldraad/fastfluxanalysis

Scripts to detect Fast-Flux and DGA using DNS query responses
dns-analysisnetwork-securityosint+2
459 years ago
ciscoasa_honeypot preview

ciscoasa_honeypot

GitHubcymmetria/ciscoasa_honeypot

A low interaction honeypot for the Cisco ASA component capable of detecting CVE-2018-0101, a DoS and remote code execution vulnerability.

defensive-toolsintrusion-detectionnetwork-security+2
557 years ago
threat-finder preview

threat-finder

GitHuboffseq/threat-finder

Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.

devsecopsnetwork-securitythreat-intelligence+2
612 months ago
Previous12…46Next