
Manati
 stratosphereips/manati
A web-based tool to assist the work of the intuitive threat analysts.
information-gatheringmachine-learningthreat-intelligence
stratosphereips/manatiA web-based tool to assist the work of the intuitive threat analysts.
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 michenriksen/gitrob
Reconnaissance tool for GitHub organizations
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 cloudflare/mitmengine
A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
 moloch--/leakdb
Web-Scale NoSQL Idempotent Cloud-Native Big-Data Serverless Plaintext Credential Search
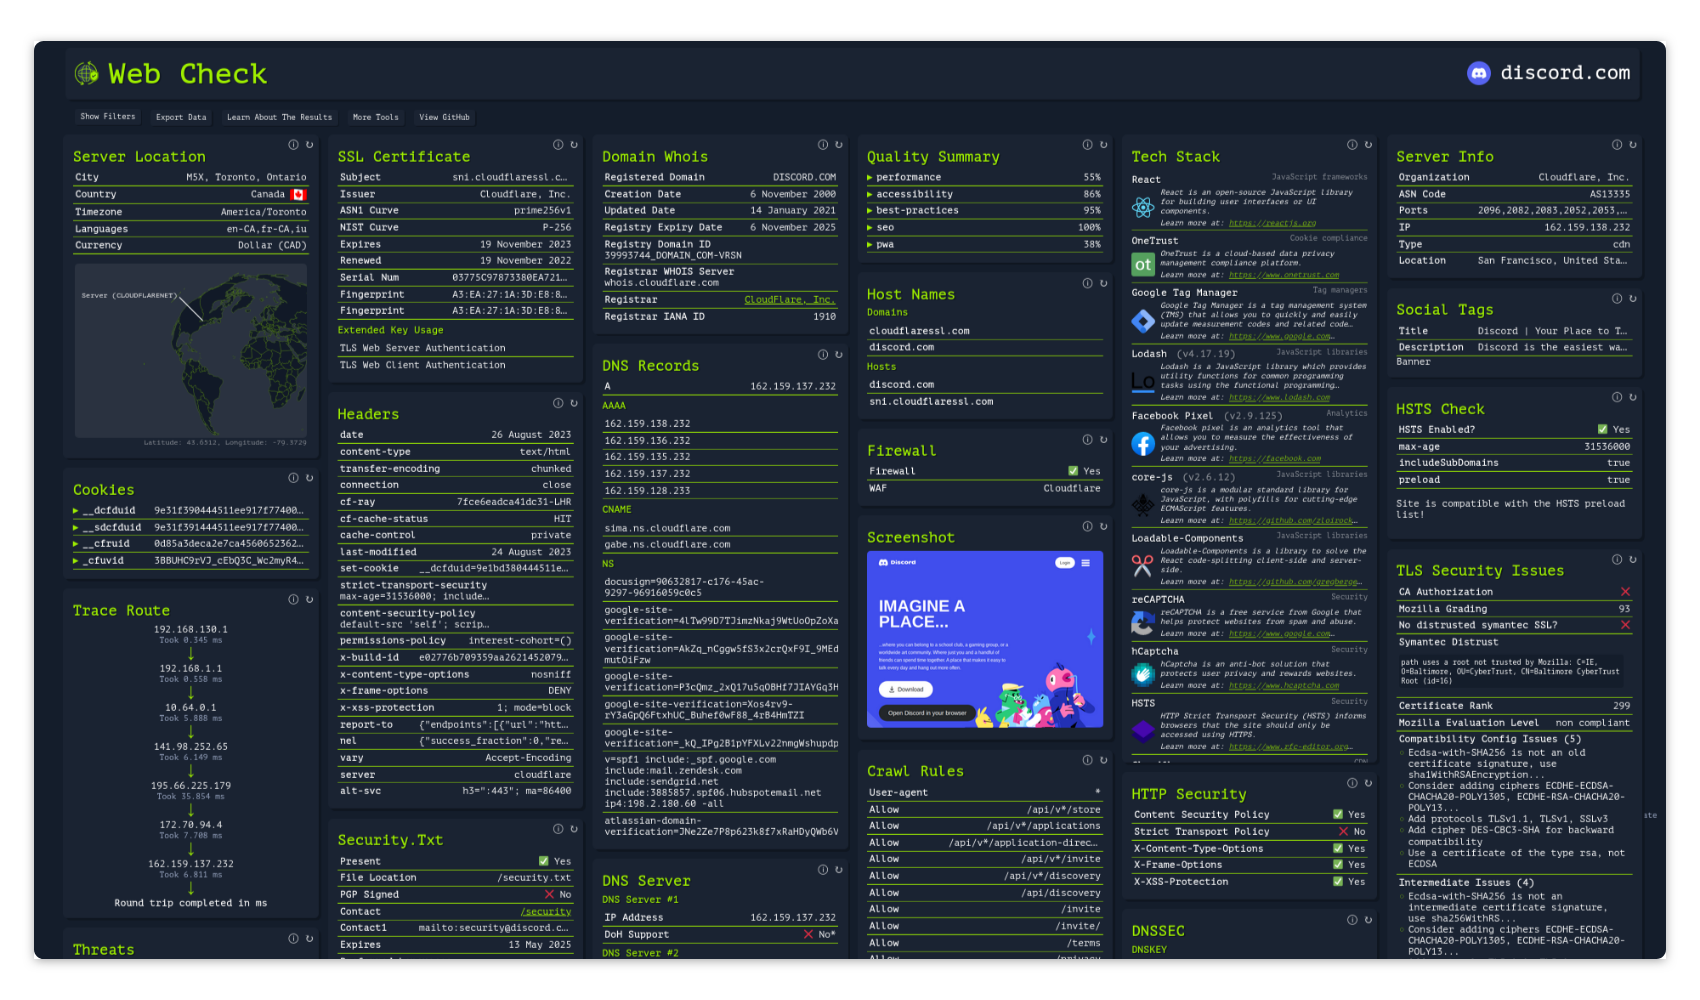 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 daehee/nvd
Fast, simple library in Go to fetch CVEs from the National Vulnerability Database feeds
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 vulncheck-oss/go-exploit-cache
A utility for producing an HTTP cache database to use with go-exploit
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 alvin-tosh/malware-exhibit
🚀🚀 This is a 🎇🔥 REAL WORLD🔥 🎇 Malware Collection I have Compiled & analysed by researchers🔥 to understand more about Malware threats😈,…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.