
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
73 results
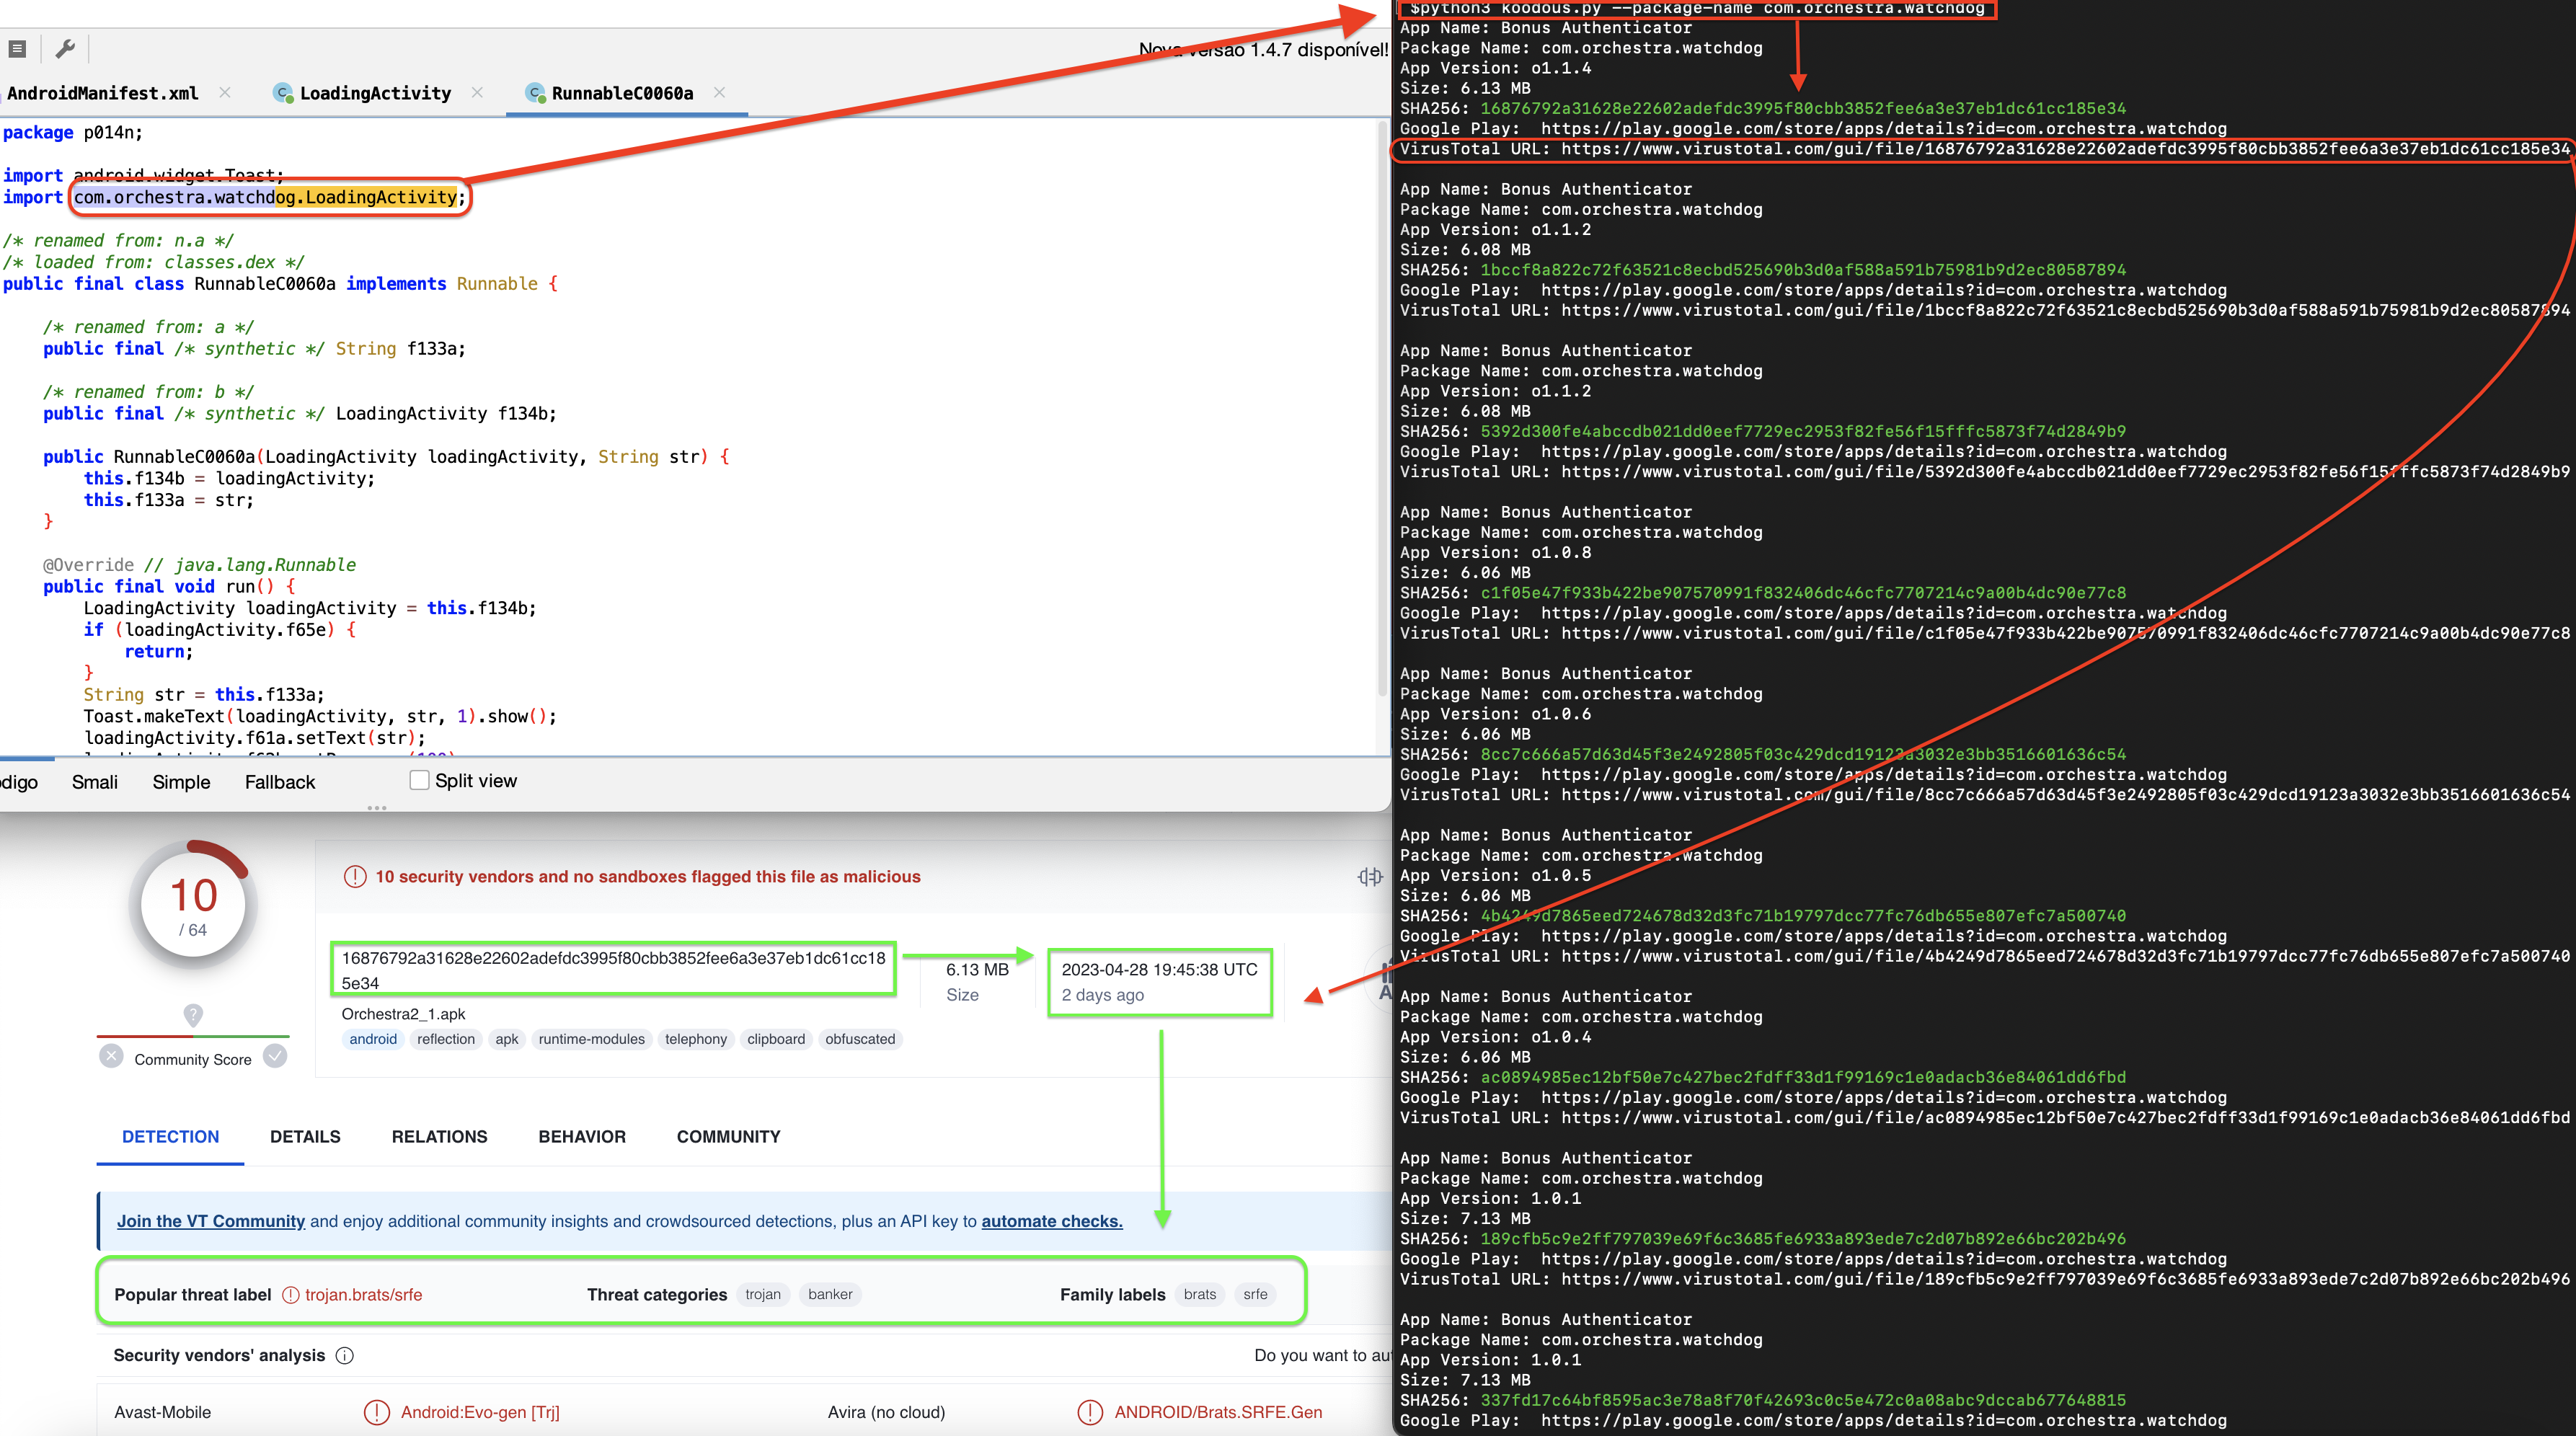
KoodousFinder preview

KoodousFinder

GitHubhuntdownproject/koodousfinder

A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
android-securitymalware-analysisosint+2
89
2 years ago
react-cve-2025-55182 preview

react-cve-2025-55182

GitHubstonelinks/react-cve-2025-55182

Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
command-and-controldata-exfiltrationforensics+6
9 months ago
AIDebug preview

AIDebug

GitHubanpa1200/aidebug

Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging

ai-securitybinary-analysisdebuggers+7
1210h 15m ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

android-securitydigital-forensicsdisk-forensics+7
15.1k1 day ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k23 days ago
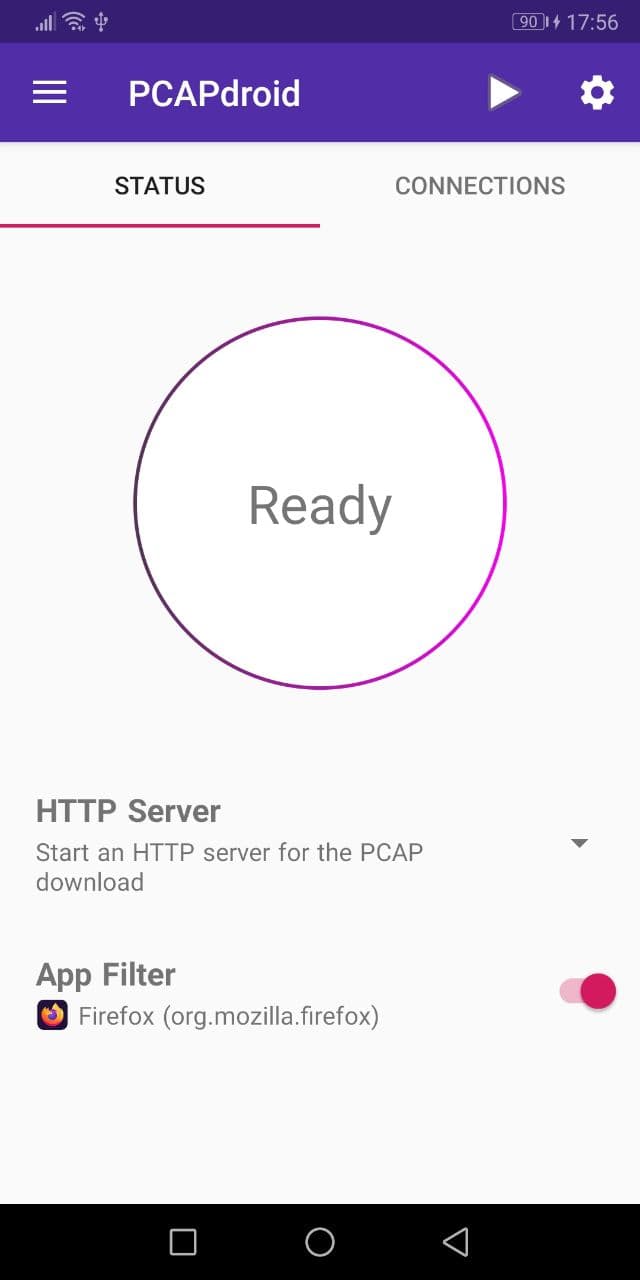
PCAPdroid preview

PCAPdroid

GitHubemanuele-f/pcapdroid

No-root network monitor, firewall and PCAP dumper for Android

android-securitydns-analysiseducation+8
4.8k5 days ago
malwoverview preview

malwoverview

GitHubalexandreborges/malwoverview

Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…

android-securityinformation-gatheringioc-management+4
4.1k9 days ago
drakvuf-sandbox preview

drakvuf-sandbox

GitHubcert-polska/drakvuf-sandbox

Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
dynamic-analysis-sandboxingforensicsmalware-analysis+2
1.4k1 month ago
flare-learning-hub preview

flare-learning-hub

GitHubmandiant/flare-learning-hub

Free educational content on reverse engineering and malware analysis from the FLARE team
binary-analysisdebuggerseducation+4
1.5k6 months ago
CAPE preview

CAPE

GitHubctxis/cape

Malware Configuration And Payload Extraction

debuggersdynamic-analysis-sandboxingmalware-analysis+2
7615 years ago
Malware-Bible preview

Malware-Bible

GitHubperkins-fund/malware-bible

Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…

digital-forensicseducationincident-response+4
6121 month ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3911 month ago
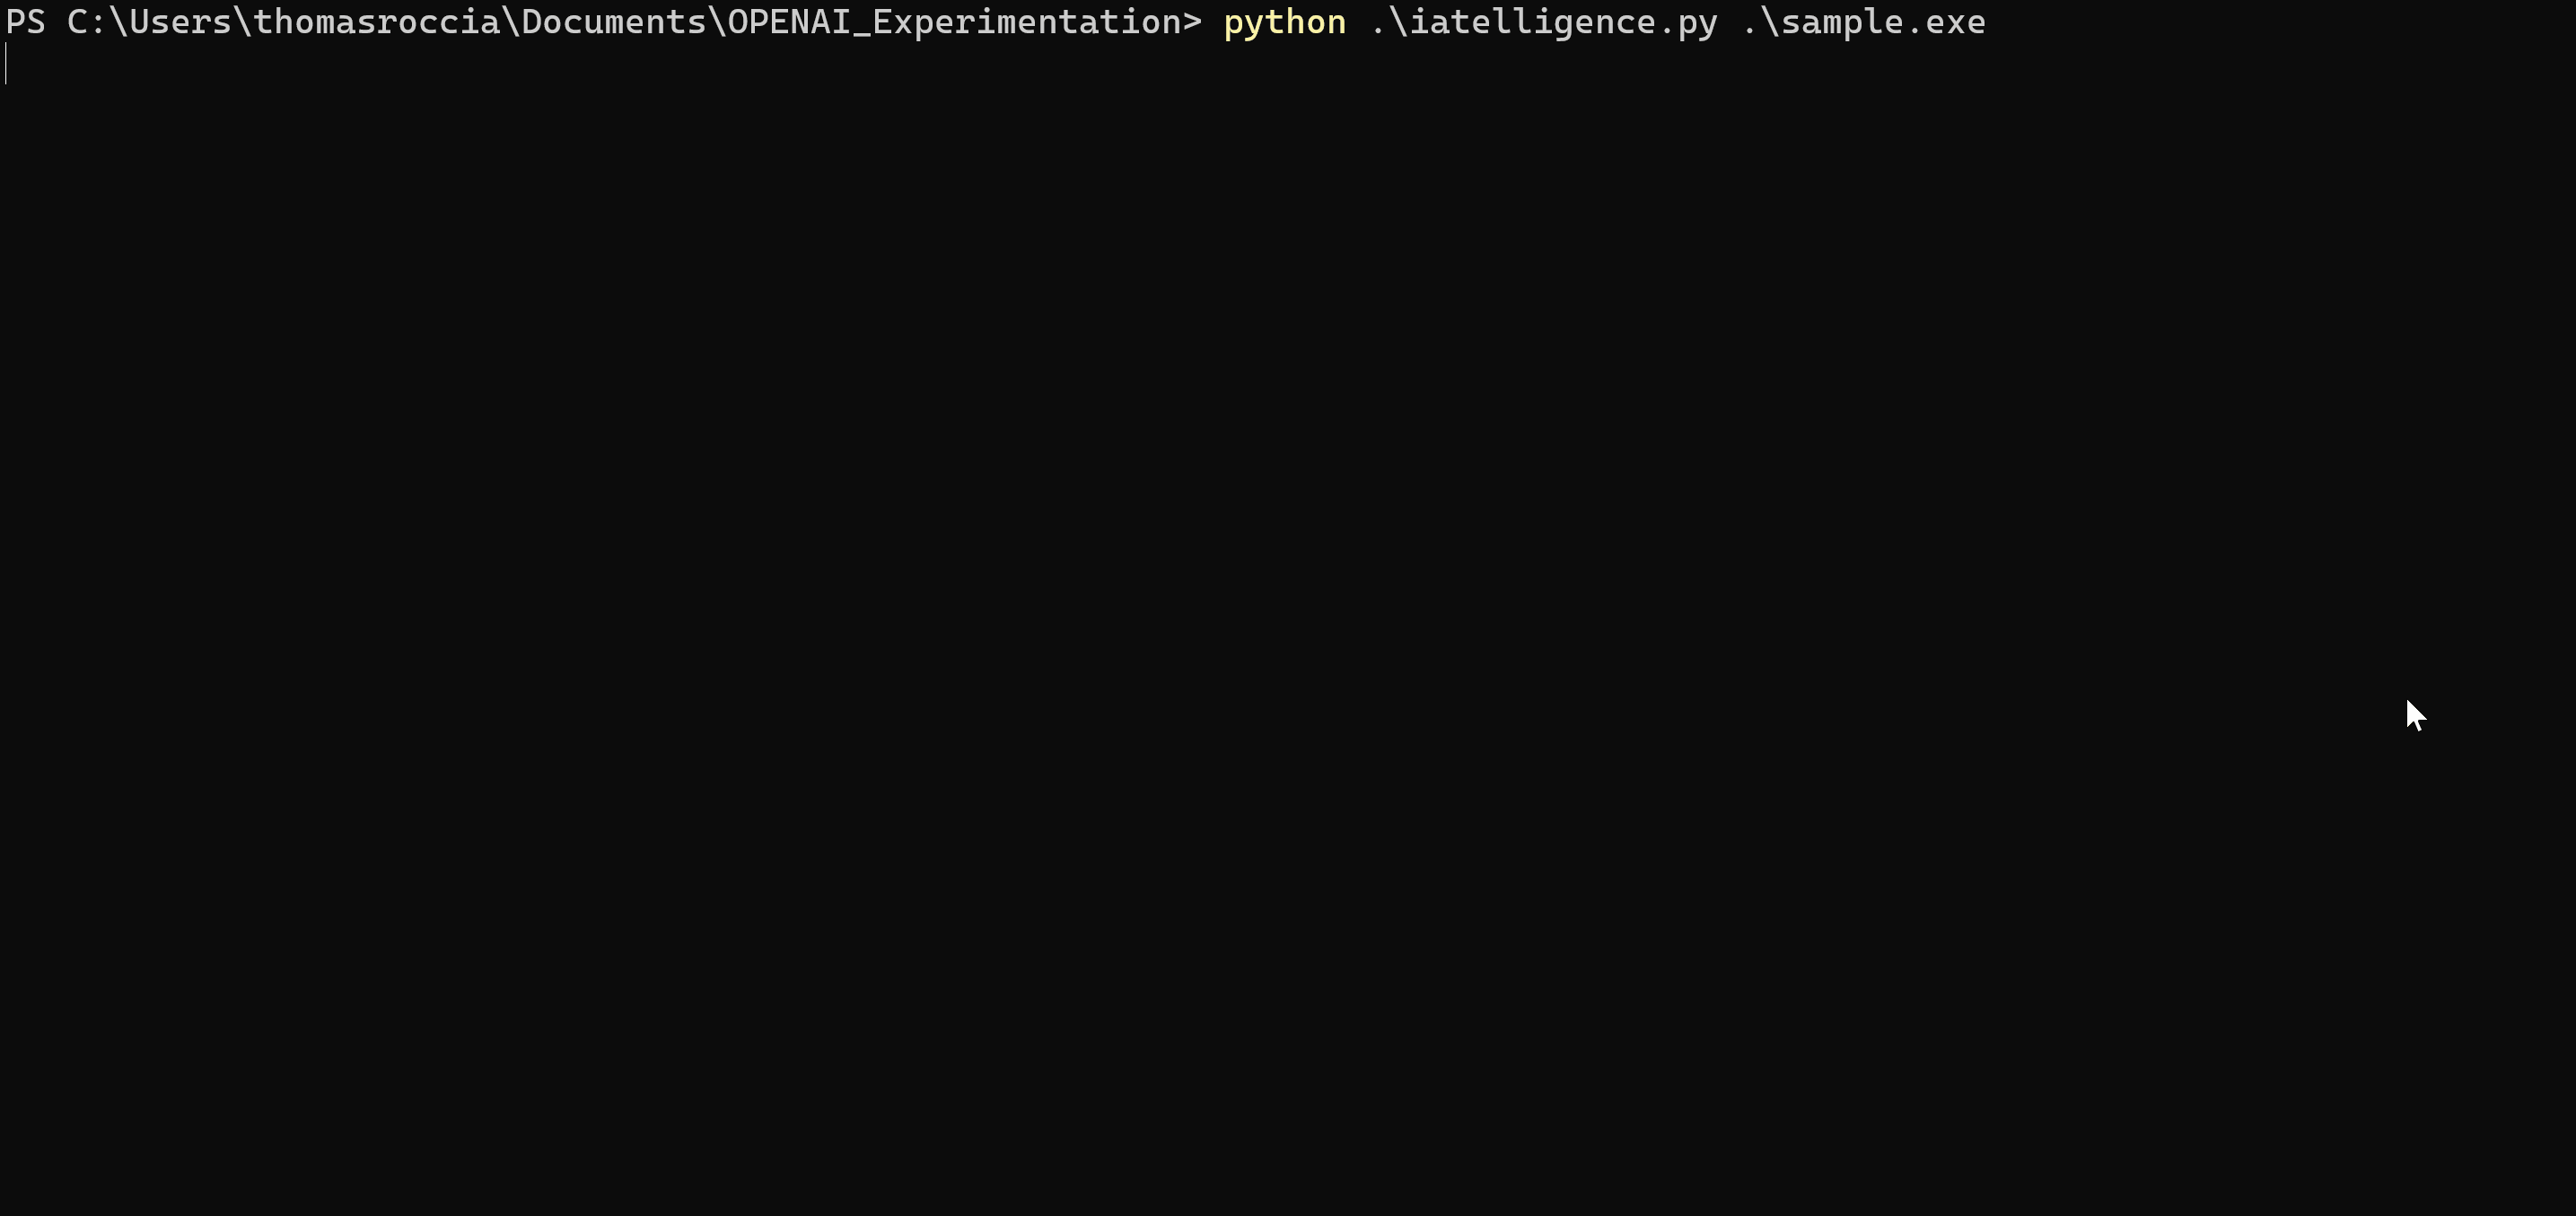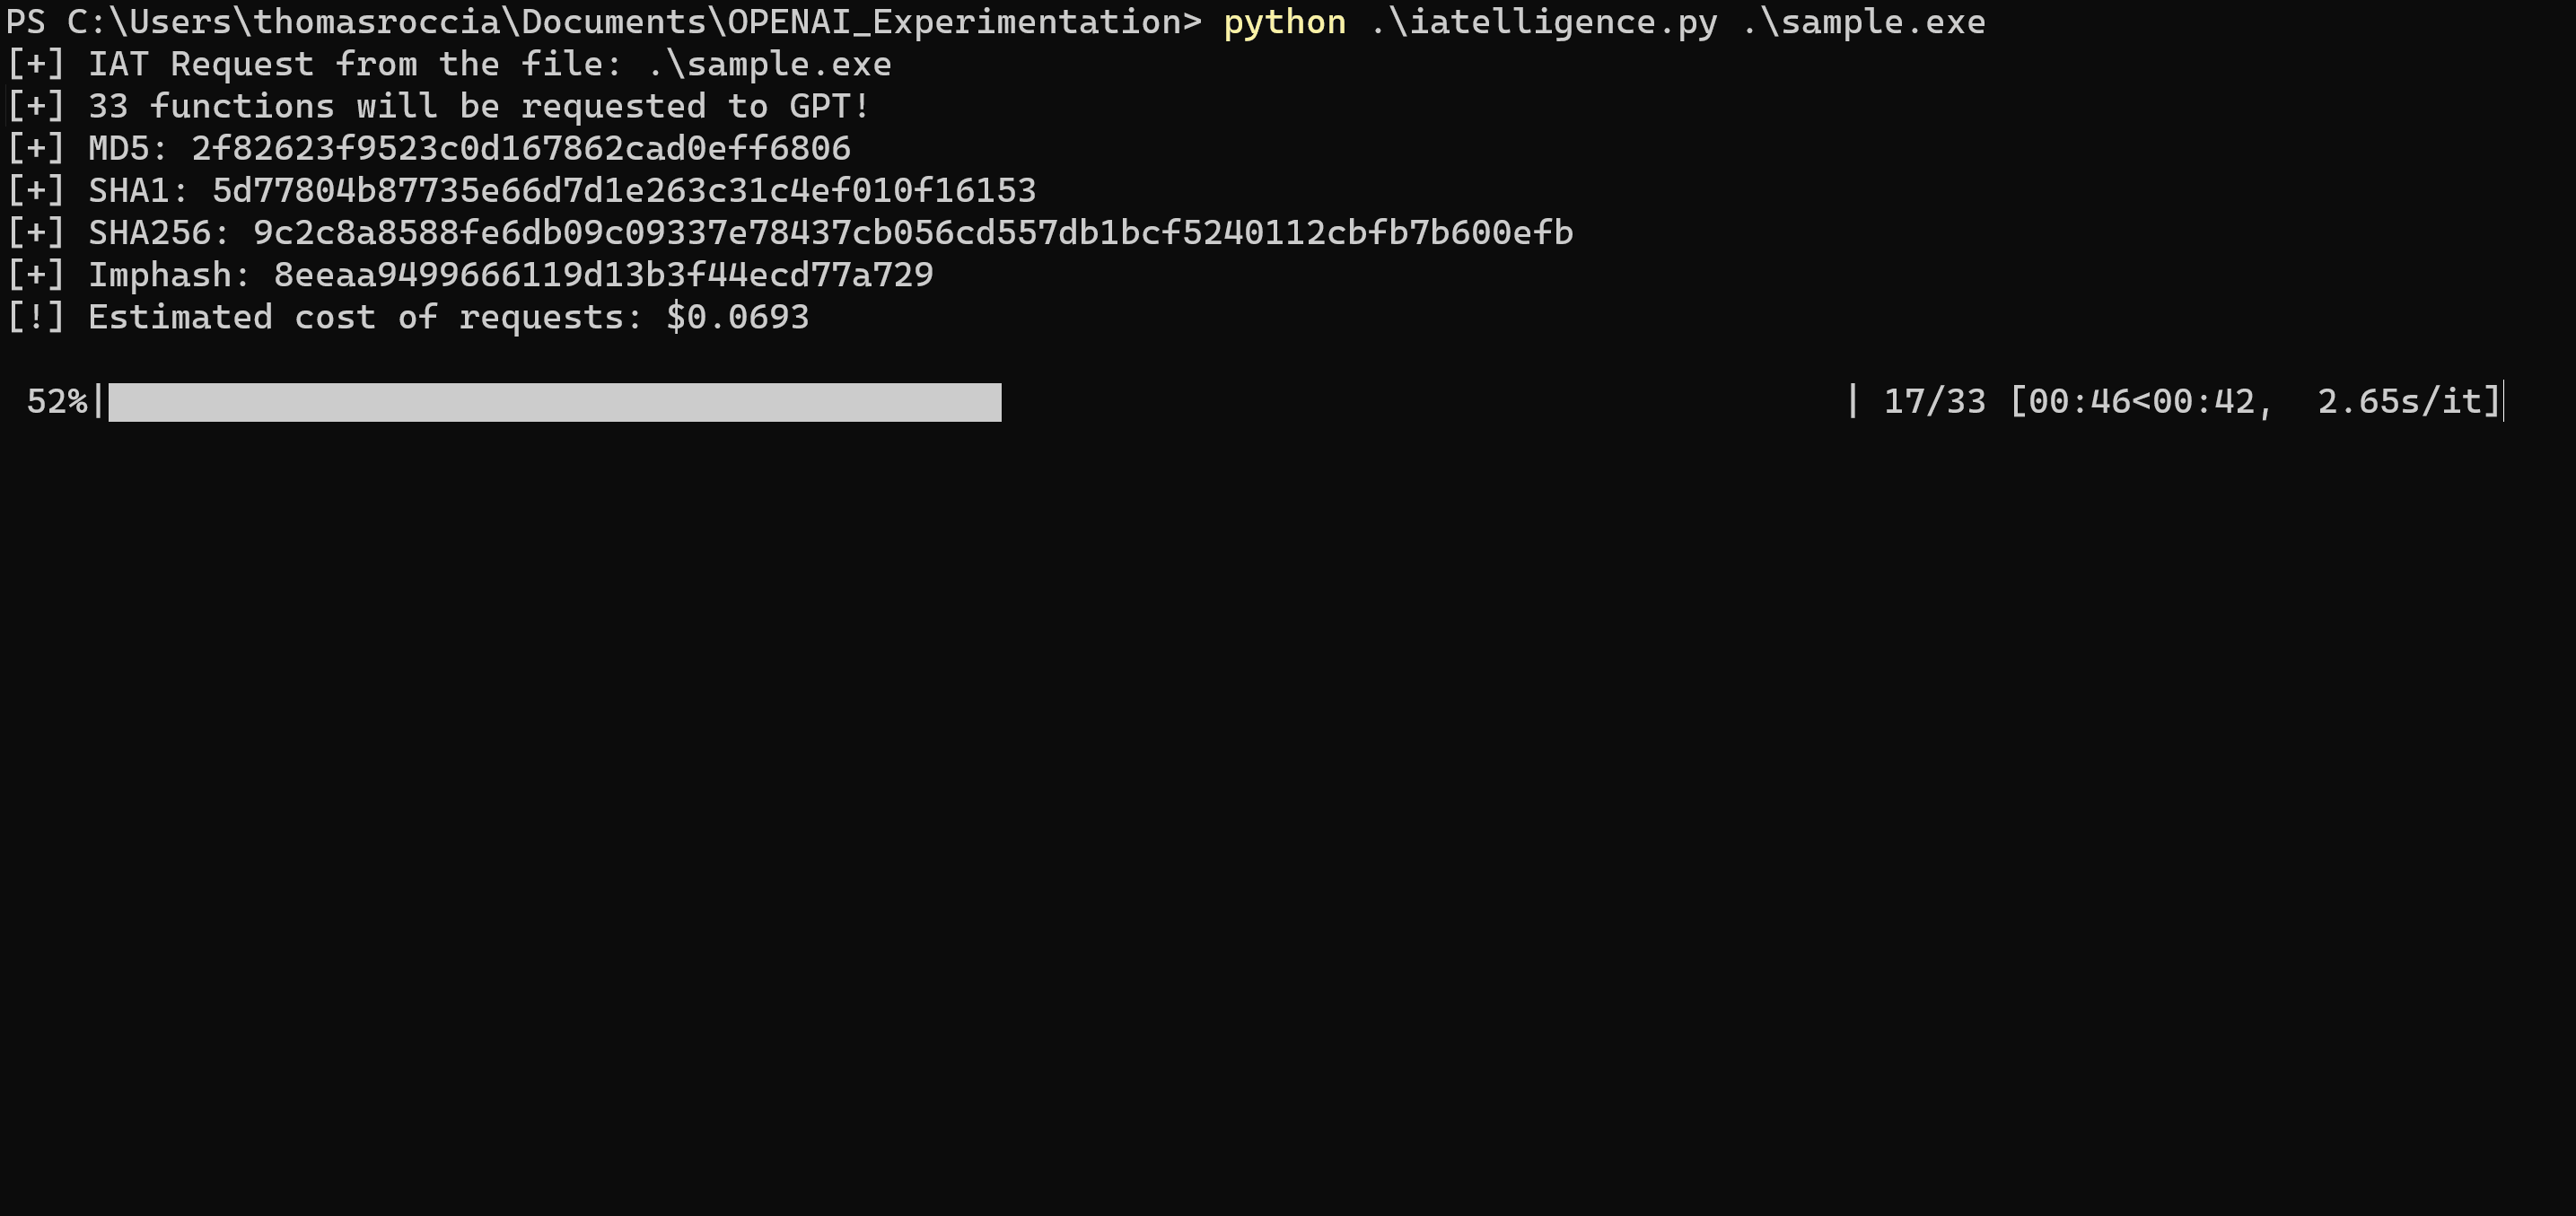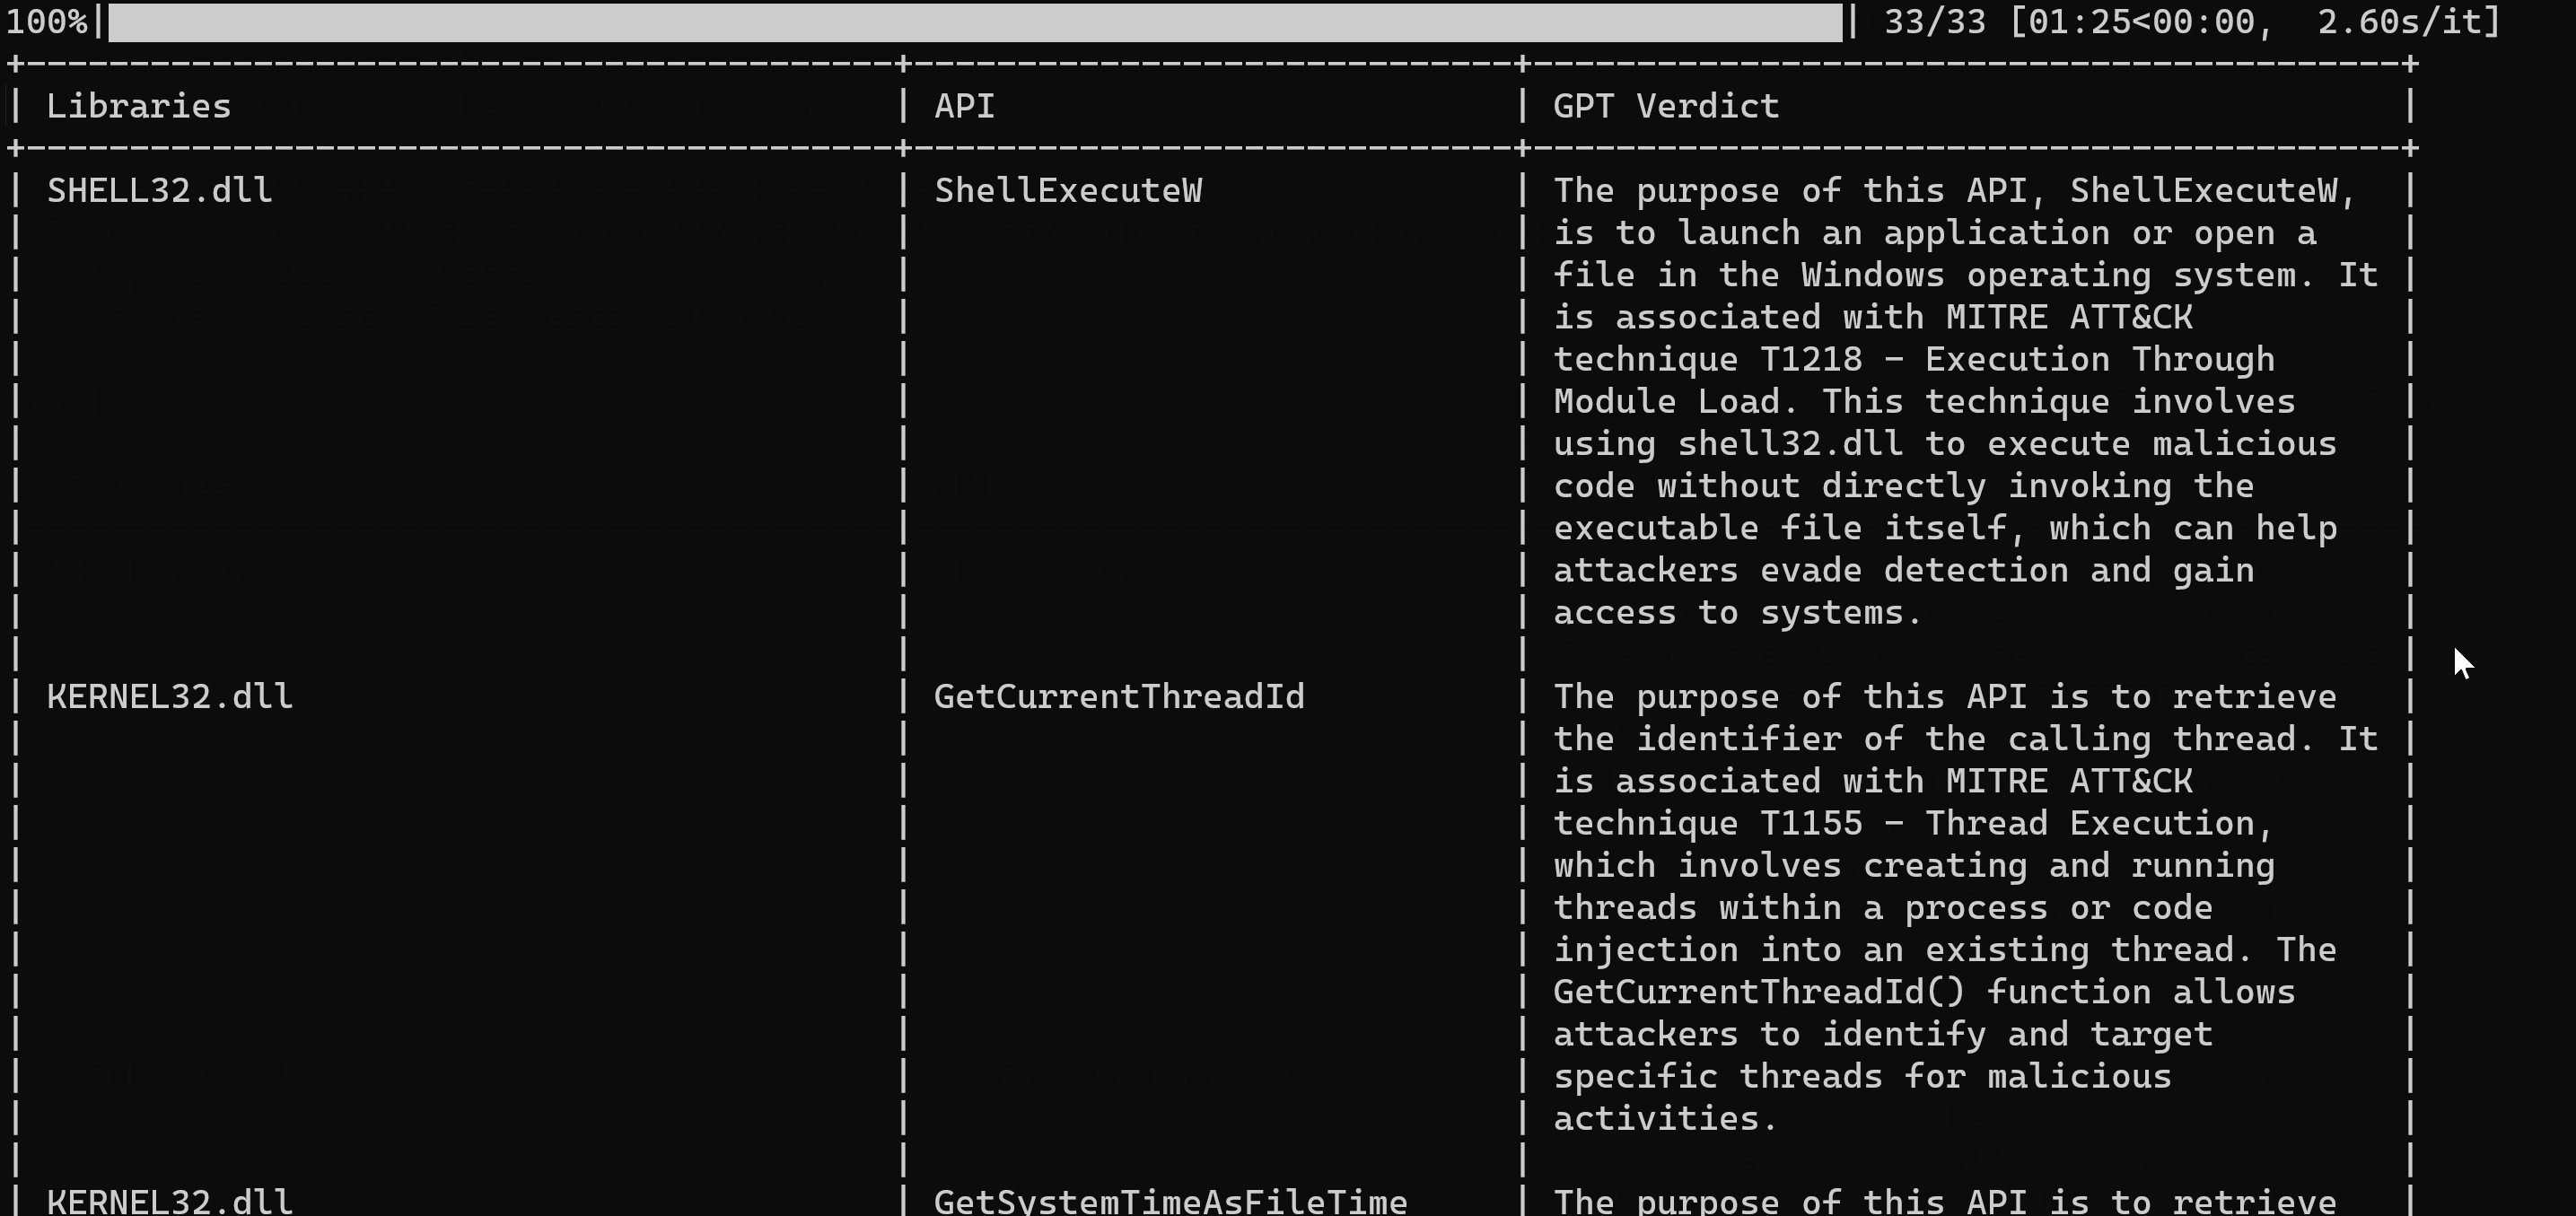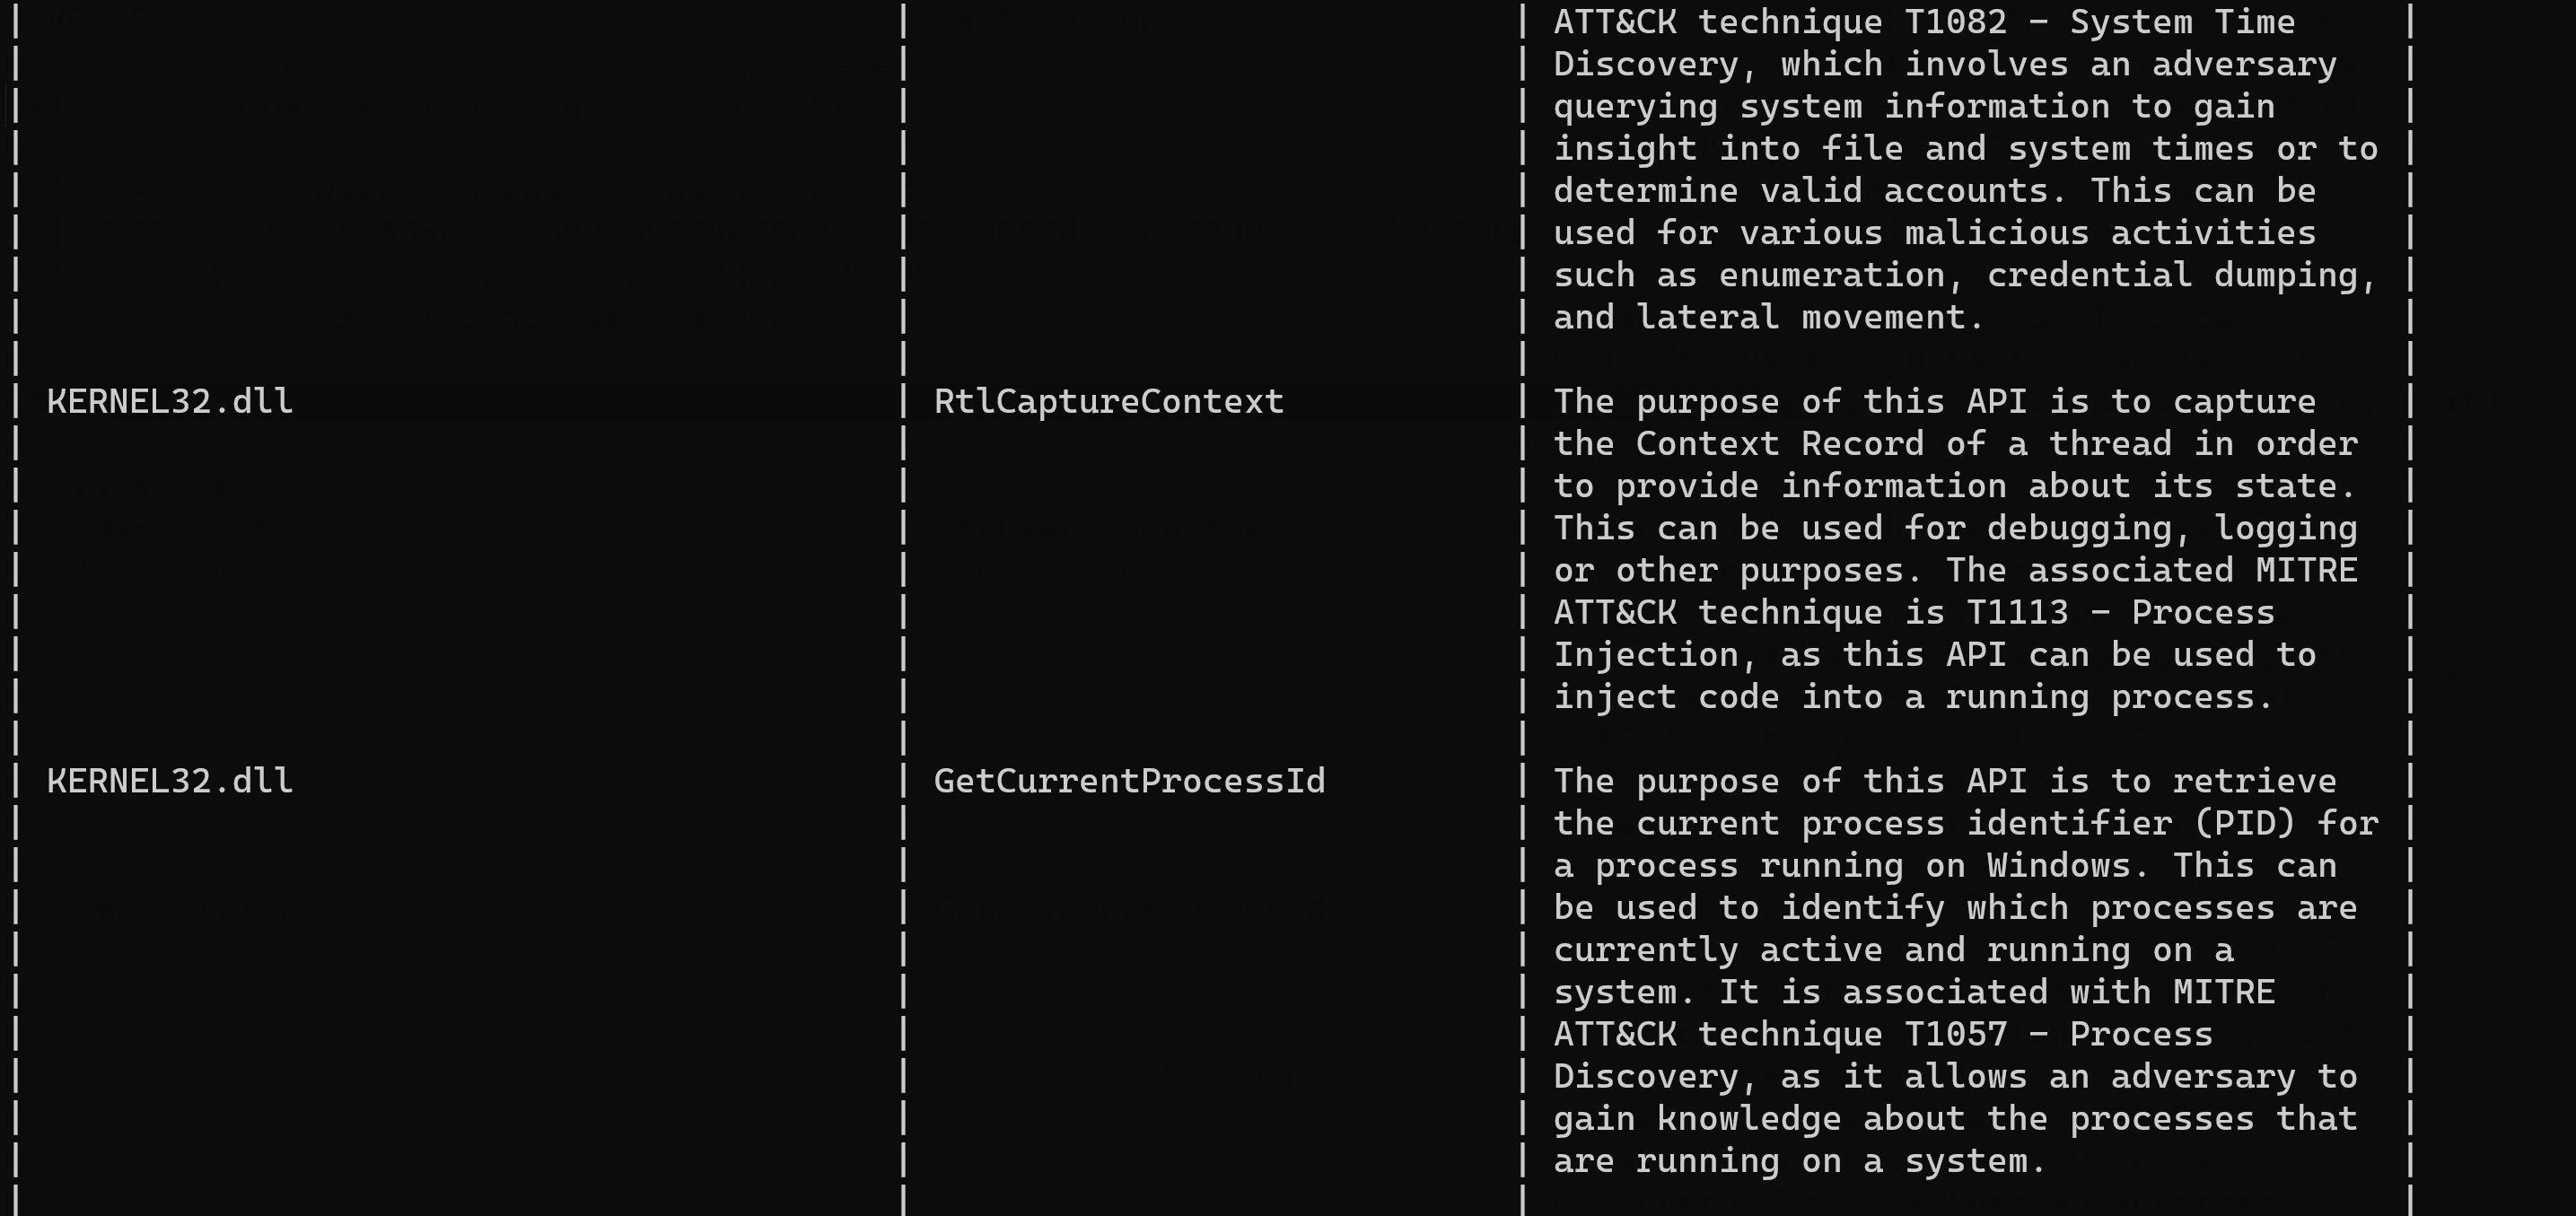
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

ai-assisted-reversingbinary-analysismalware-analysis+3
3863 years ago
freki preview

freki

GitHubcristianzsh/freki

Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
binary-analysismalware-analysisreverse-engineering+2
4452 years ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
18625 days ago
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
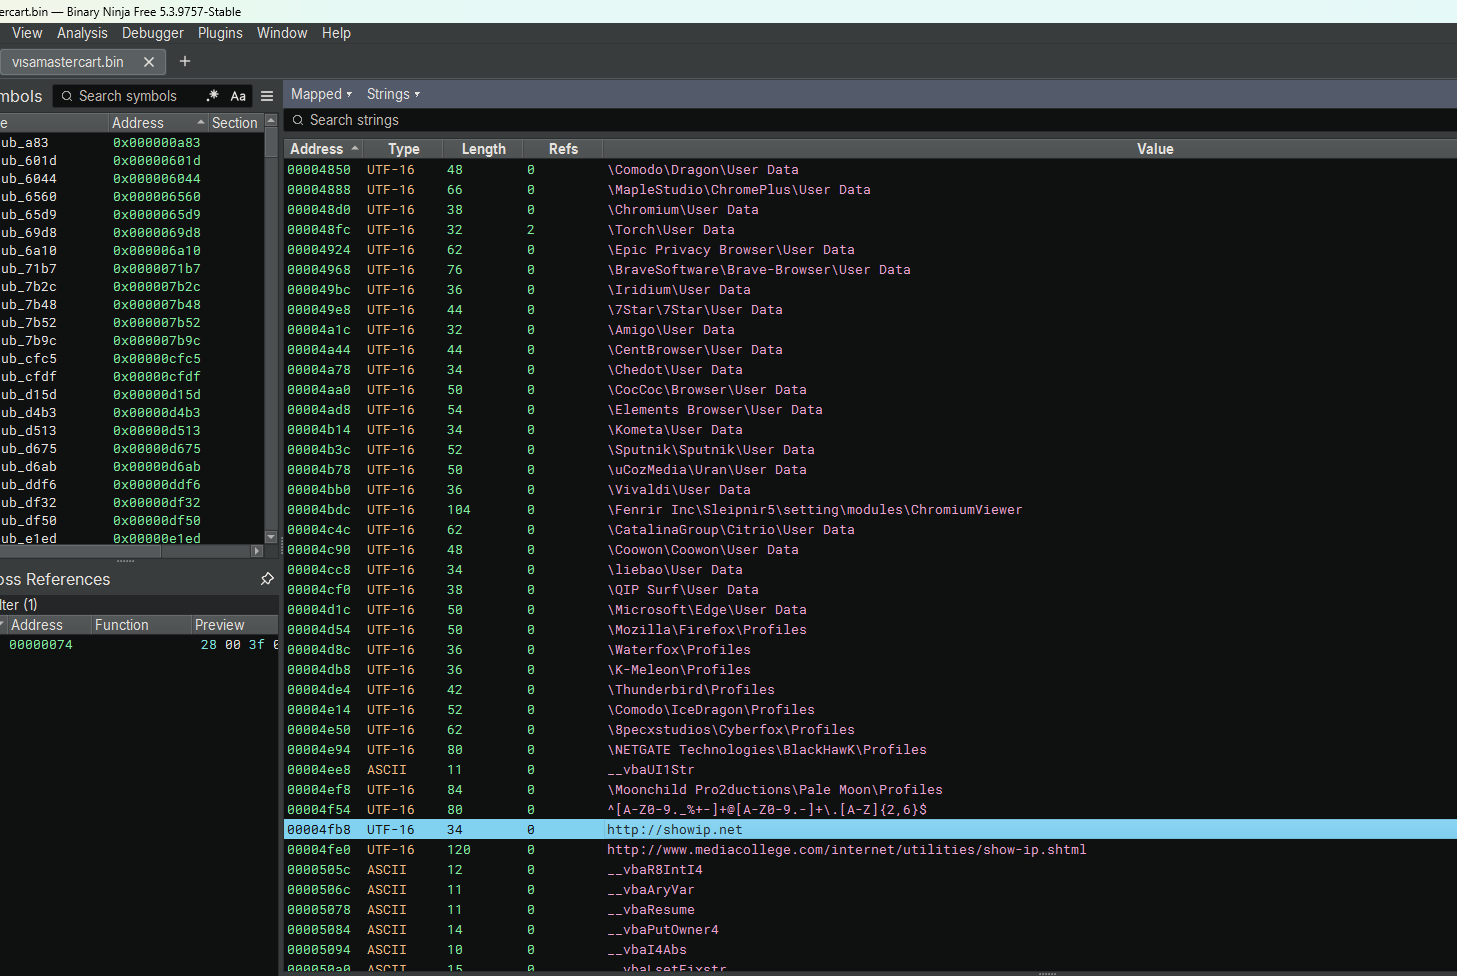
binary-analysisbinary-exploitationctf+8
945 days ago
DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis preview

DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

GitHubkaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis

Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
command-and-controldata-exfiltrationdigital-forensics+4
4726 days ago
CAPEsolo preview

CAPEsolo

GitHubcapesandbox/capesolo

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

defensive-toolsdynamic-analysis-sandboxingforensics+7
6011h 5m ago
Previous12345Next