
redtail-ioc
 lukeslp/redtail-ioc
IOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
curated-resourcesdigital-forensicseducation+6
2
lukeslp/redtail-iocIOCs and a read-only triage checklist from a real Linux root compromise: RedTail miner, XorDDoS persistence, MoneroOcean miner, DirtyFrag LPE…
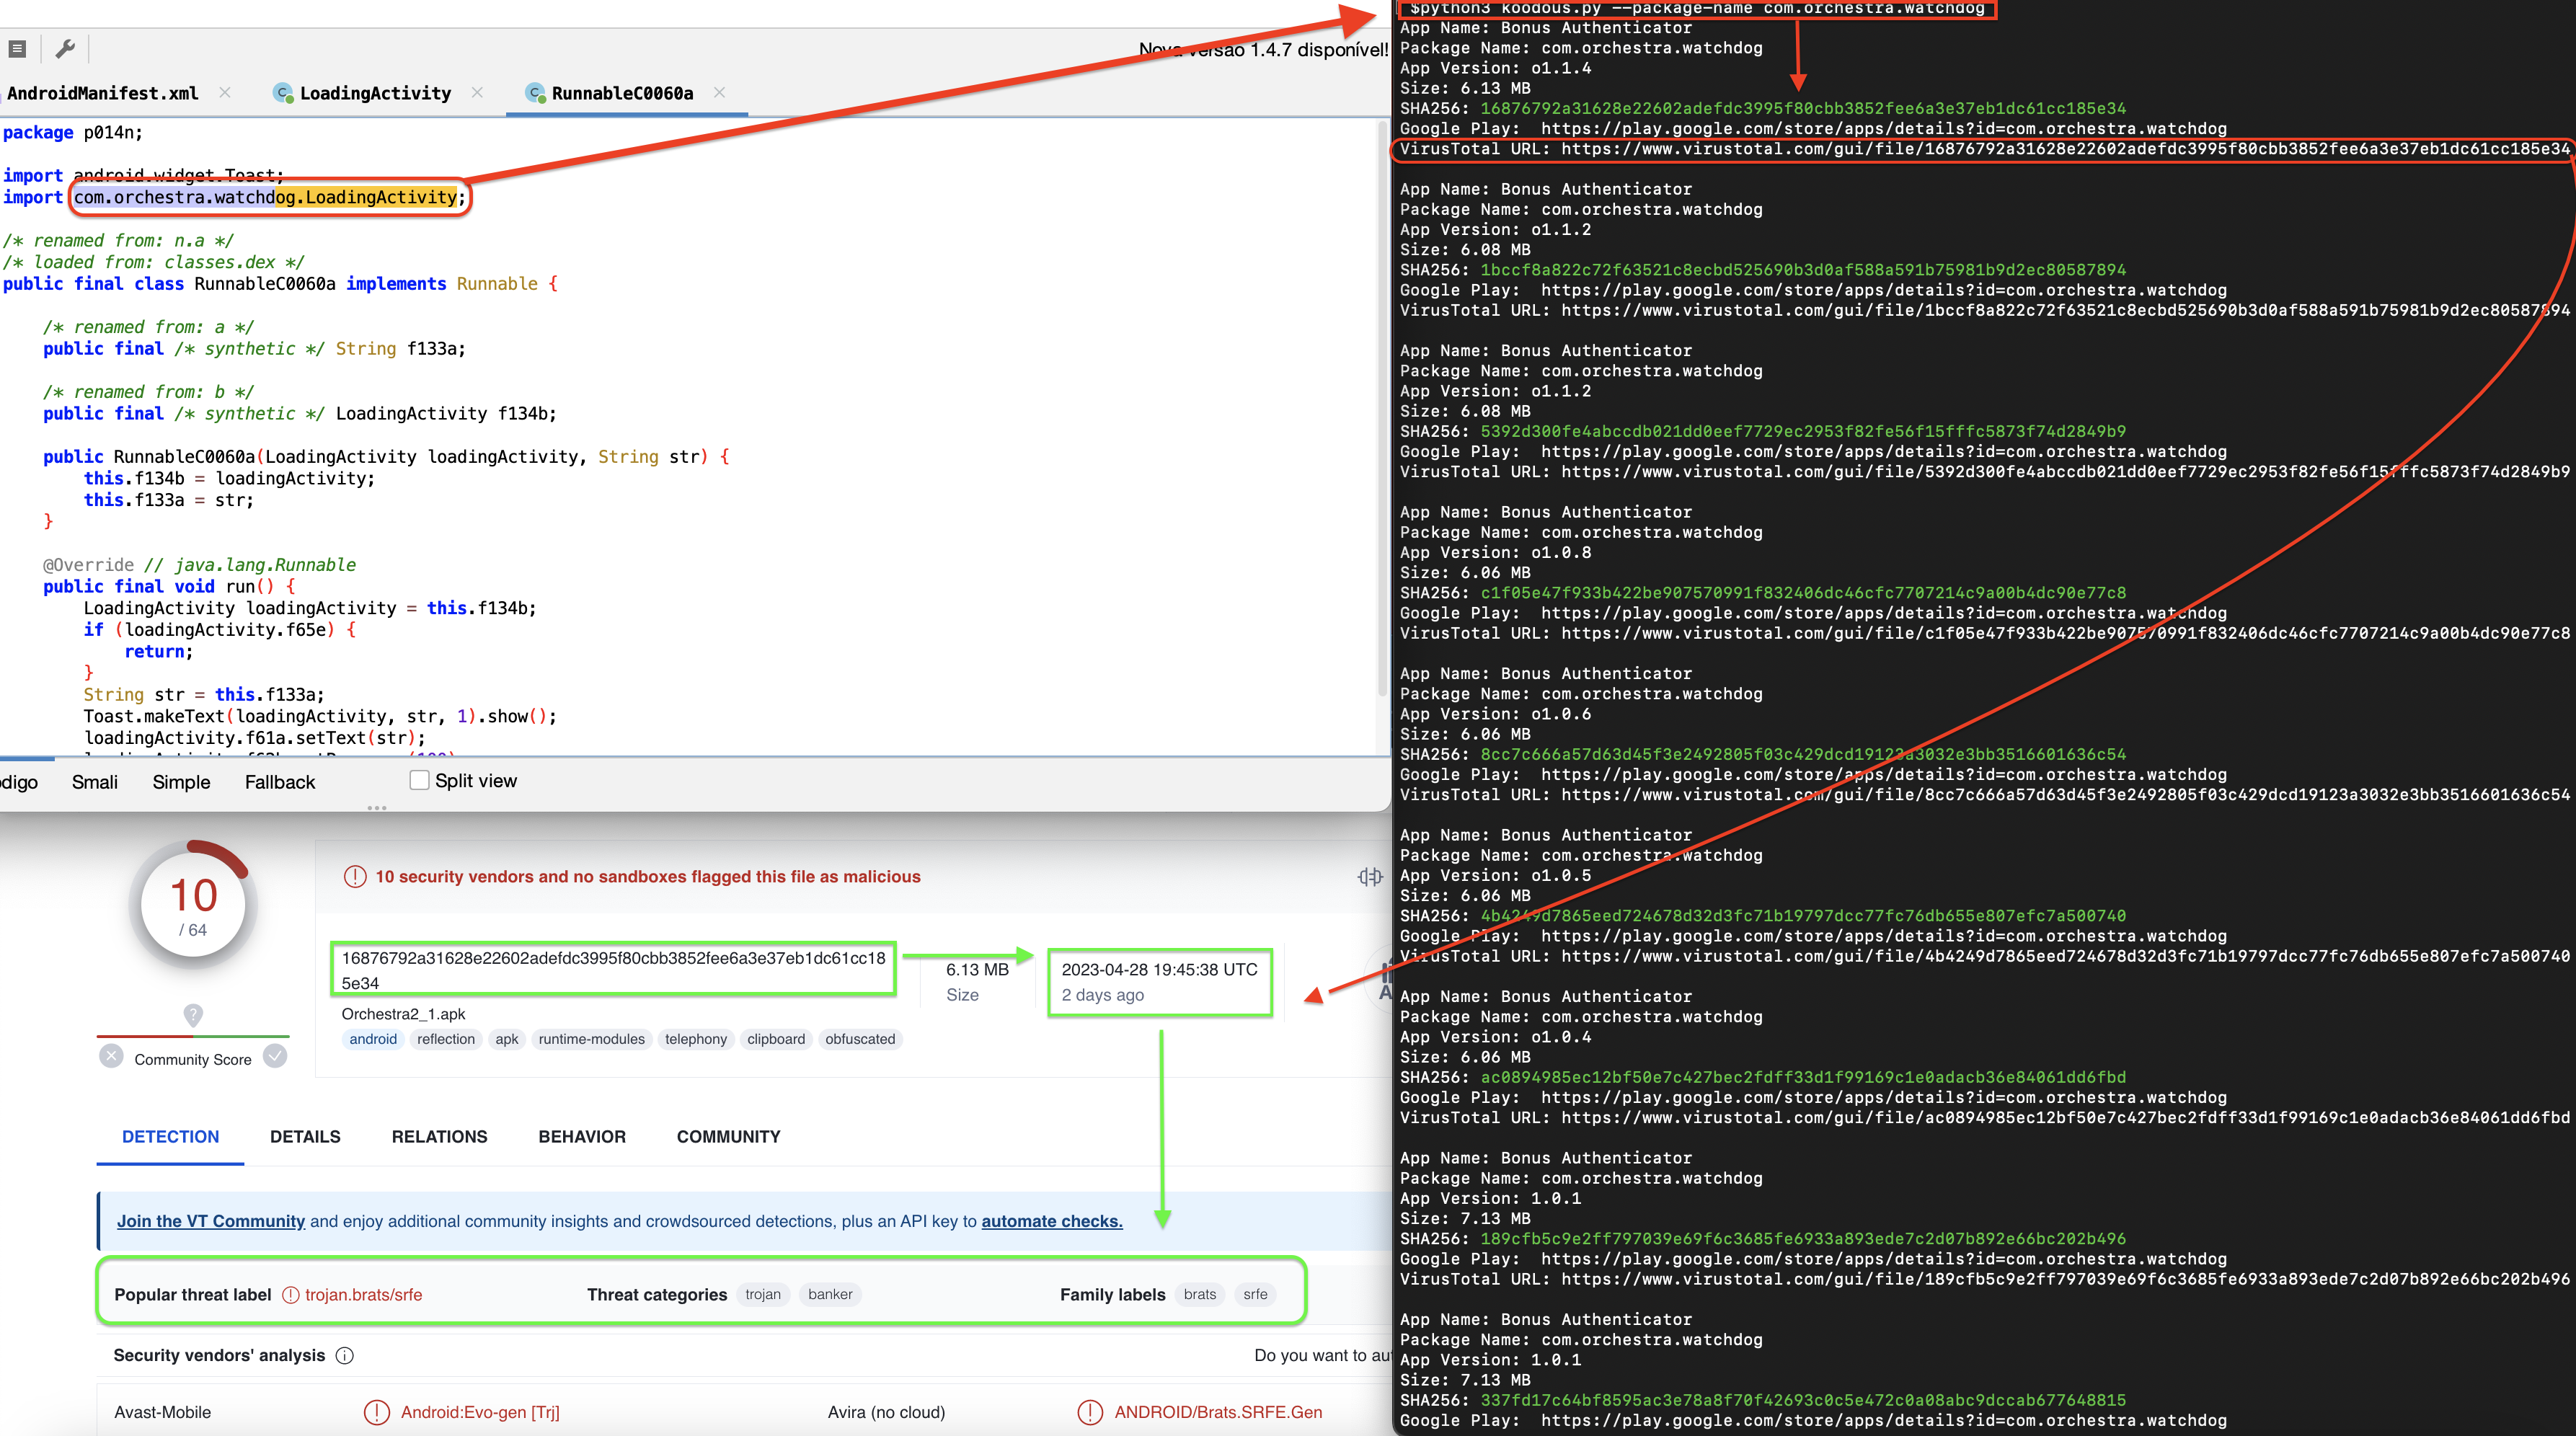 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
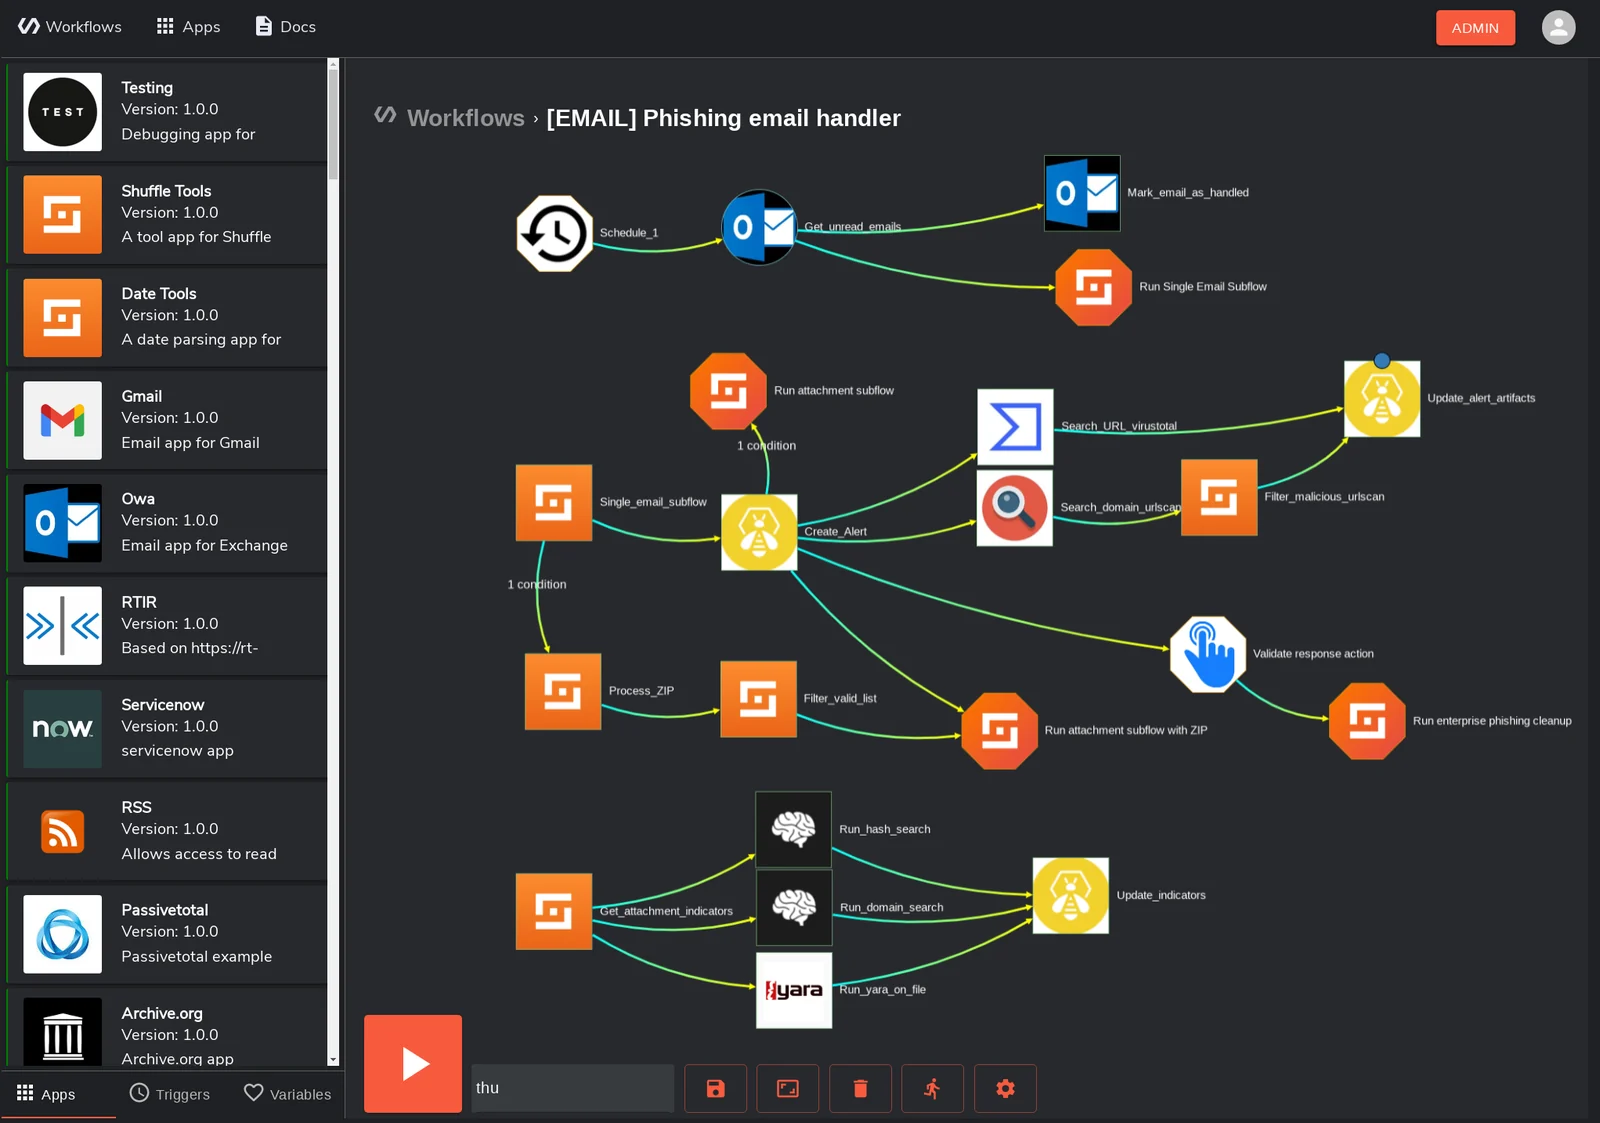 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
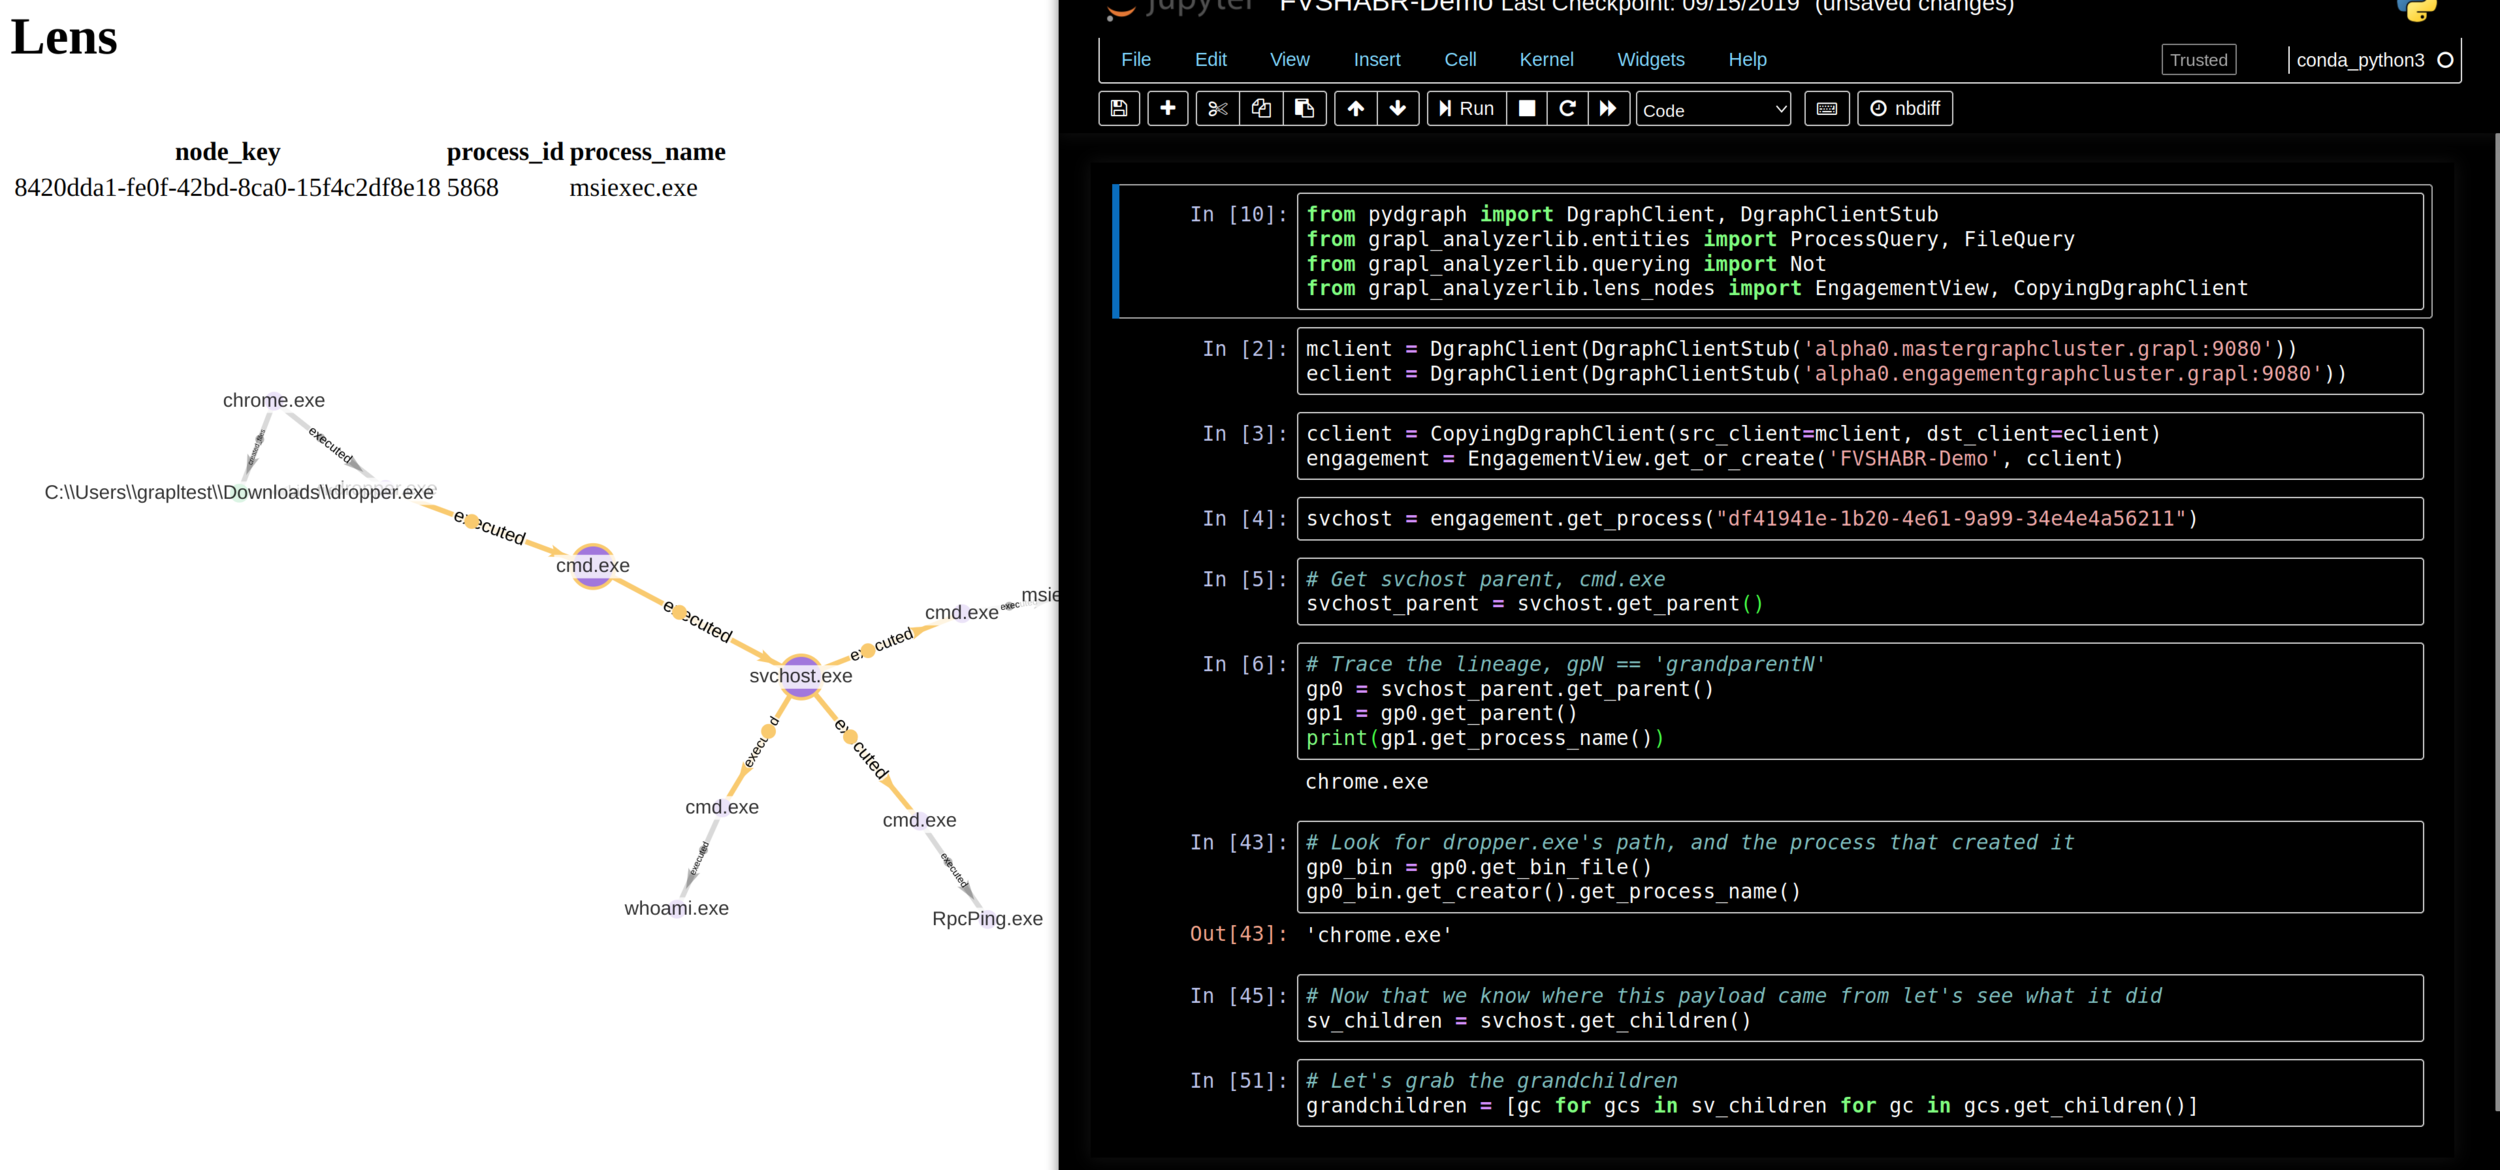 grapl-security/grapl
Graph platform for Detection and Response
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
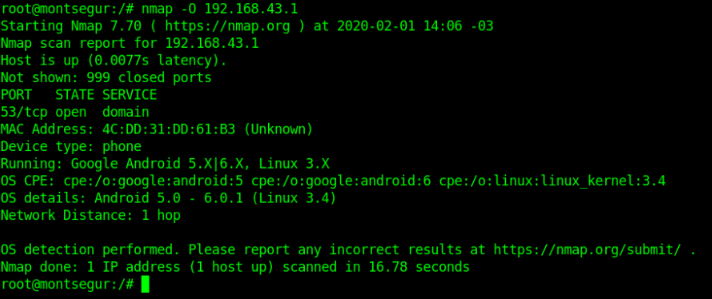 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 kaifcodec/user-scanner
Multi-platform OSINT scanner for email and username reconnaissance across 295+ vectors. Extracts profile metadata, checks account registrations, and…
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 iti/ics-security-tools
Tools, tips, tricks, and more for exploring ICS Security.
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
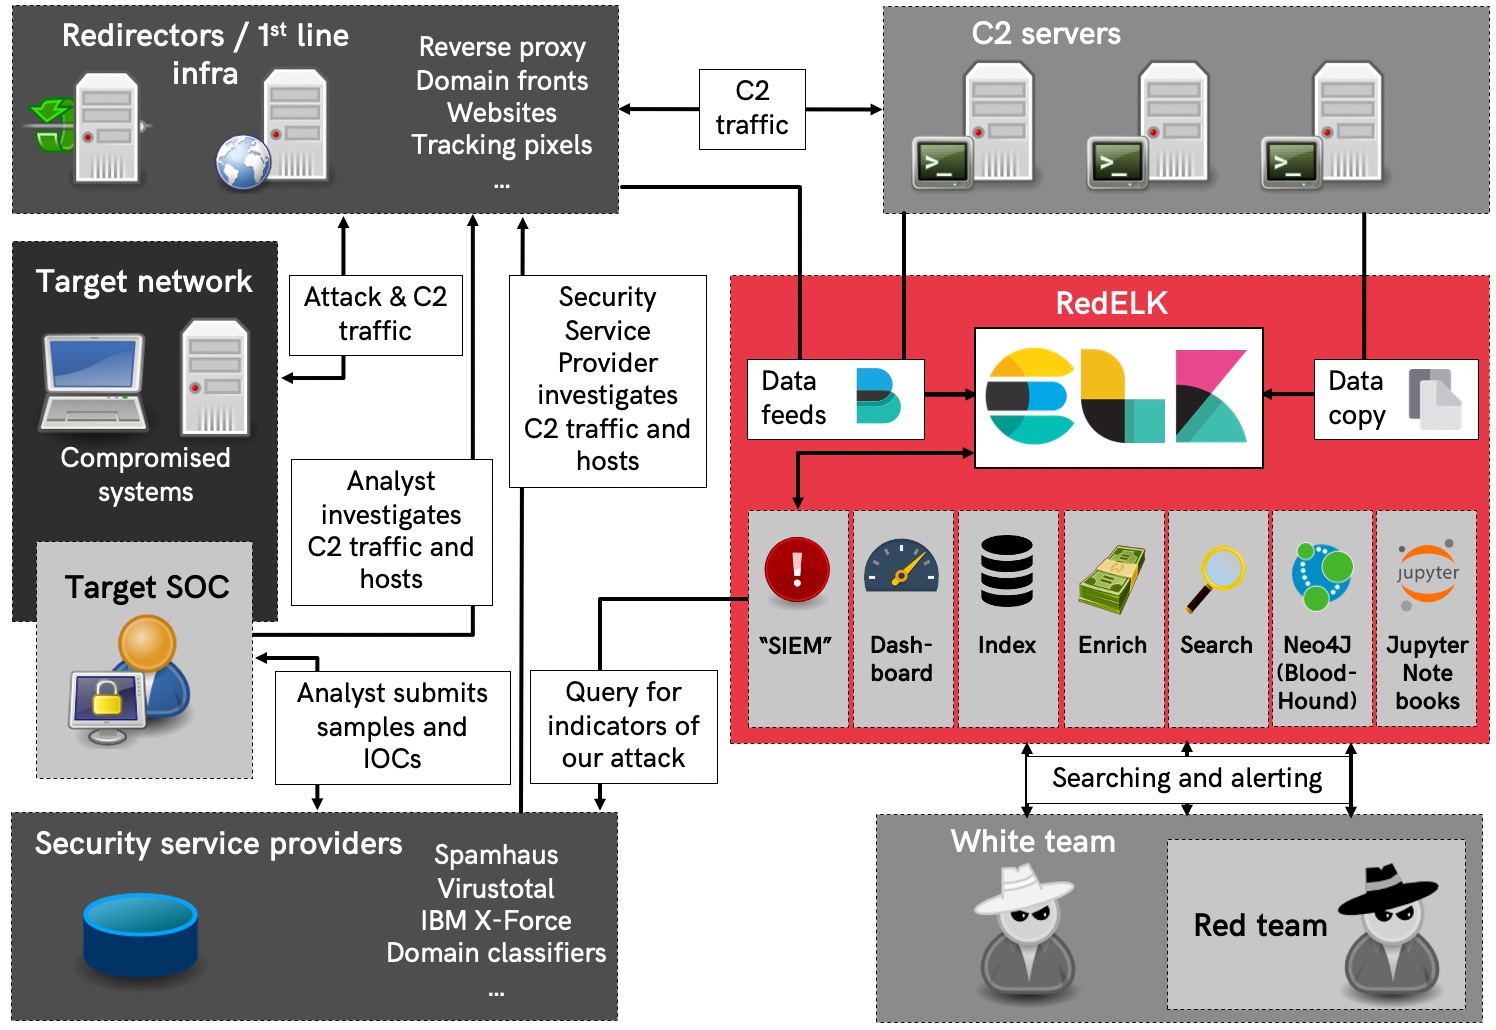 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
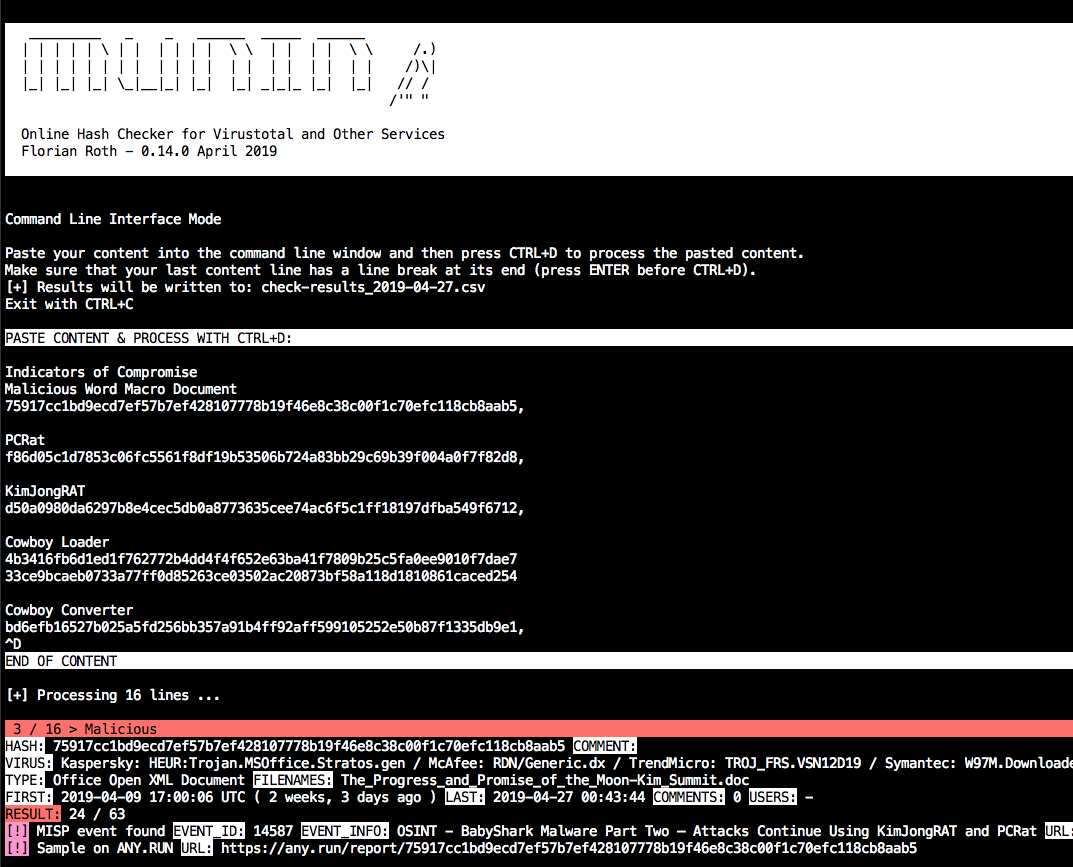 neo23x0/munin
Online hash checker for Virustotal and other services
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…