
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
69 results
SecFlow preview

SecFlow

GitHubaradhyacp/secflow

AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
ai-securityforensicsincident-response+6
22
6 months ago
cve-lfi-lab preview

cve-lfi-lab

GitHubthecyberfairy/cve-lfi-lab

A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…

ctfeducationincident-response+5
1 year ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
5 days ago
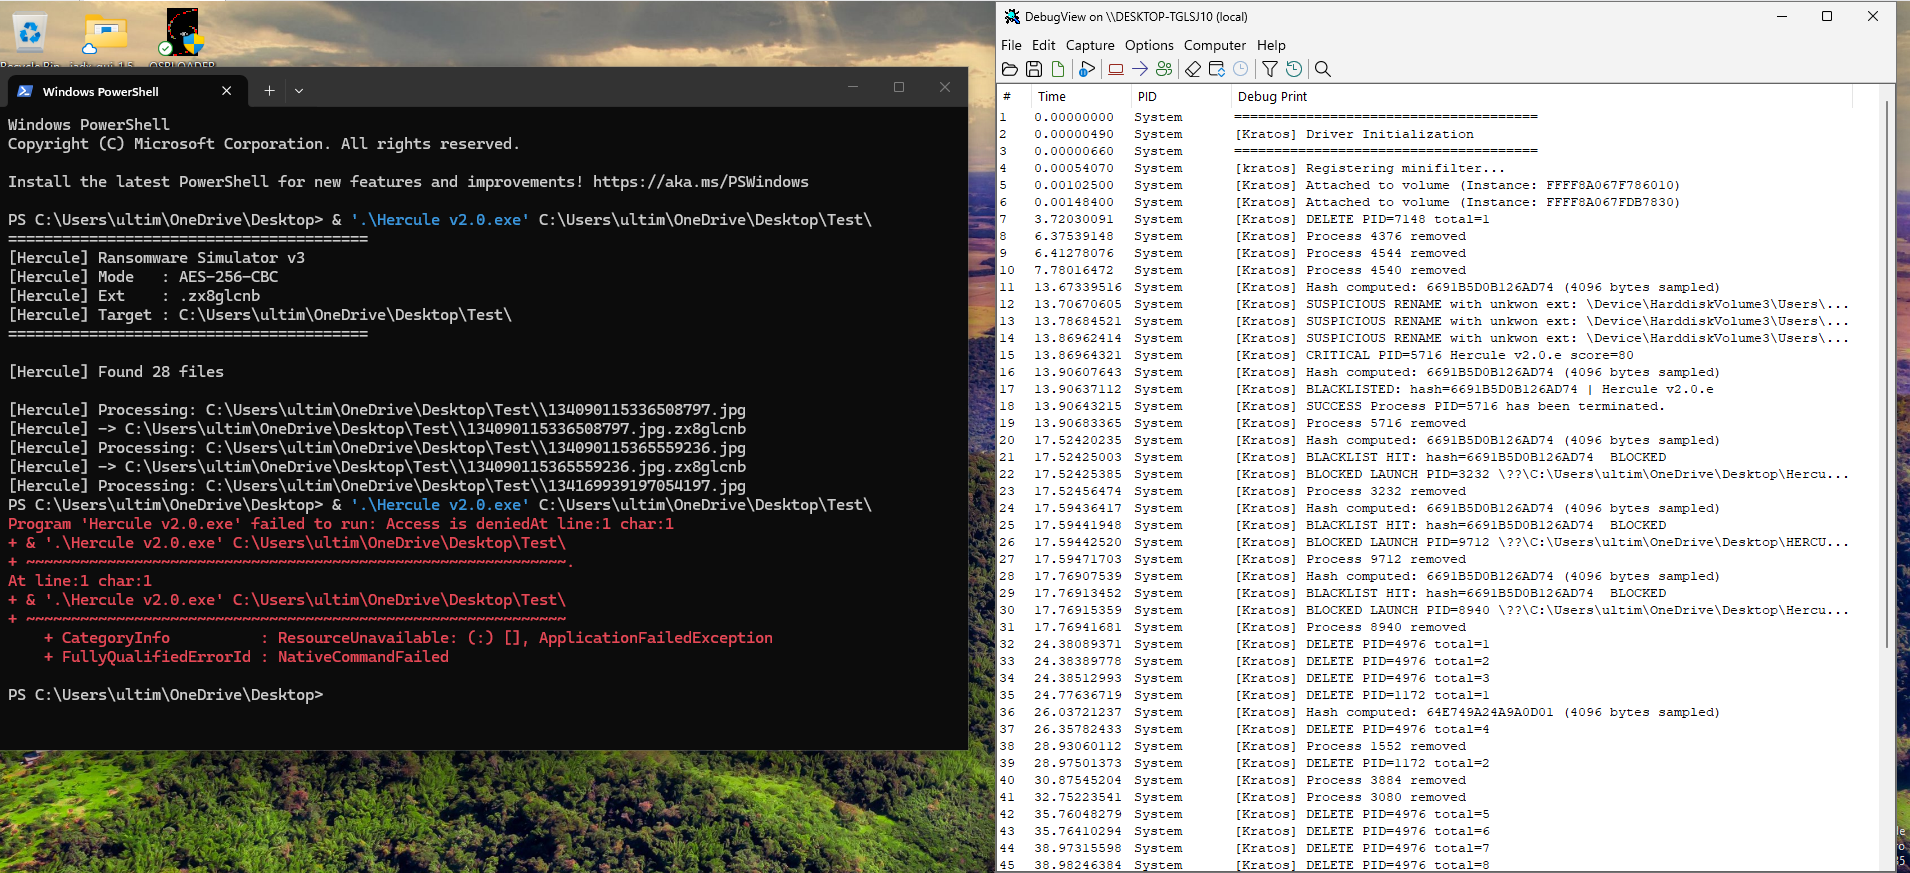
kratosminifilter preview

kratosminifilter

GitHubmukendi/kratosminifilter

Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize

anomaly-detectiondefensive-toolsincident-response+2
410 days ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k1 day ago
BlackLotusDetection preview

BlackLotusDetection

GitHubbakedmuffinman/blacklotusdetection

Created to help detect IOCs for CVE-2022-21894: The BlackLotus campaign
forensicsincident-responseioc-management+2
3 years ago
log4shell_ioc_ips preview

log4shell_ioc_ips

GitHubhackinghippo/log4shell_ioc_ips

log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
incident-responseinformation-gatheringioc-management+3
374 years ago
cve-collector preview

cve-collector

GitHubpassword123456/cve-collector

Automated CVE collector that crawls cvedetails.com, parses HTML for vulnerabilities with CVSS ≥ 6, and stores results in a delimiter-based file…

crawlerinformation-gatheringthreat-intelligence+1
602 years ago
MOVEit-CVE-2023-34362 preview

MOVEit-CVE-2023-34362

GitHubaditibv/moveit-cve-2023-34362

This repository investigates the exploitation of CVE-2023-34362 in the MOVEit file transfer server by the TA505 (Cl0p) ransomware group. It explores…
educationexploitationincident-response+3
2 years ago
macOSTriageCollectionScript preview

macOSTriageCollectionScript

GitHubwithsecurelabs/macostriagecollectionscript

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
digital-forensicsforensicsincident-response+2
315 years ago
CVE-2025-68645-Exploiting-Zimbra-Webmail-LFI-Vulnerability preview

CVE-2025-68645-Exploiting-Zimbra-Webmail-LFI-Vulnerability

GitHubfaysalferdous/cve-2025-68645-exploiting-zimbra-webmail-lfi-vulnerability

Defender-focused reference pack for CVE-2025-68645 Zimbra LFI, including Sigma/Splunk detection rules, WAF mitigation snippets, IOC patterns, and…
educationincident-responseioc-management+3
7 months ago
vt-py-scanner preview

vt-py-scanner

GitHubneorai/vt-py-scanner

Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
forensicshash-analysisinformation-gathering+3
610 months ago
panrapidcheck preview

panrapidcheck

GitHubhackinglz/panrapidcheck

Extract useful information from PANOS support file for CVE-2024-3400

forensicsincident-responseioc-management+3
21 year ago
CVE-2025-60787-Detection-motionEye-RCE-via-Config-Injection preview

CVE-2025-60787-Detection-motionEye-RCE-via-Config-Injection

GitHubgarethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection

Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…

container-securityexploitationintrusion-detection+5
6 months ago
CVE-2022-29072 preview

CVE-2022-29072

GitHubsentinelblue/cve-2022-29072

** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…
exploitationincident-responselog-analysis+3
84 years ago
Wireshark preview

Wireshark

GitHubkirkdjohnson/wireshark

Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

command-and-controldigital-forensicseducation+9
32 years ago
CVE-2026-54984 preview

CVE-2026-54984

GitHubkagancapar/cve-2026-54984

CVE-2026-54984 / ZDI-26-543: Windows ICC file parsing out-of-bounds write (CWE-122, CVSS 7.8)
curated-resourcesthreat-intelligencevulnerability-analysis
1 month ago
Event-ID-263-Arbitrary-File-Read-on-Checkpoint-Security-Gateway-CVE-2024-24919- preview

Event-ID-263-Arbitrary-File-Read-on-Checkpoint-Security-Gateway-CVE-2024-24919-

GitHubcyberbibs/event-id-263-arbitrary-file-read-on-checkpoint-security-gateway-cve-2024-24919-

Step-by-step SOC incident response walkthrough for CVE-2024-24919 arbitrary file read on Check Point gateways, covering detection, analysis,…

educationforensicsincident-response+3
1 year ago
Previous1234Next