
bothan
 audibleblink/bothan
Is this IP a C2 server?
command-and-controldefensive-toolsinformation-gathering+3
audibleblink/bothanIs this IP a C2 server?
 helixar-ai/mcp-security-checklist
MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 princessauroraj/chinese-cybercrime-research
Resources to learn more about Chinese-language cybercrime actors.
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 jorgeorchilles/presentations
Slides and materials for conference presentations
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
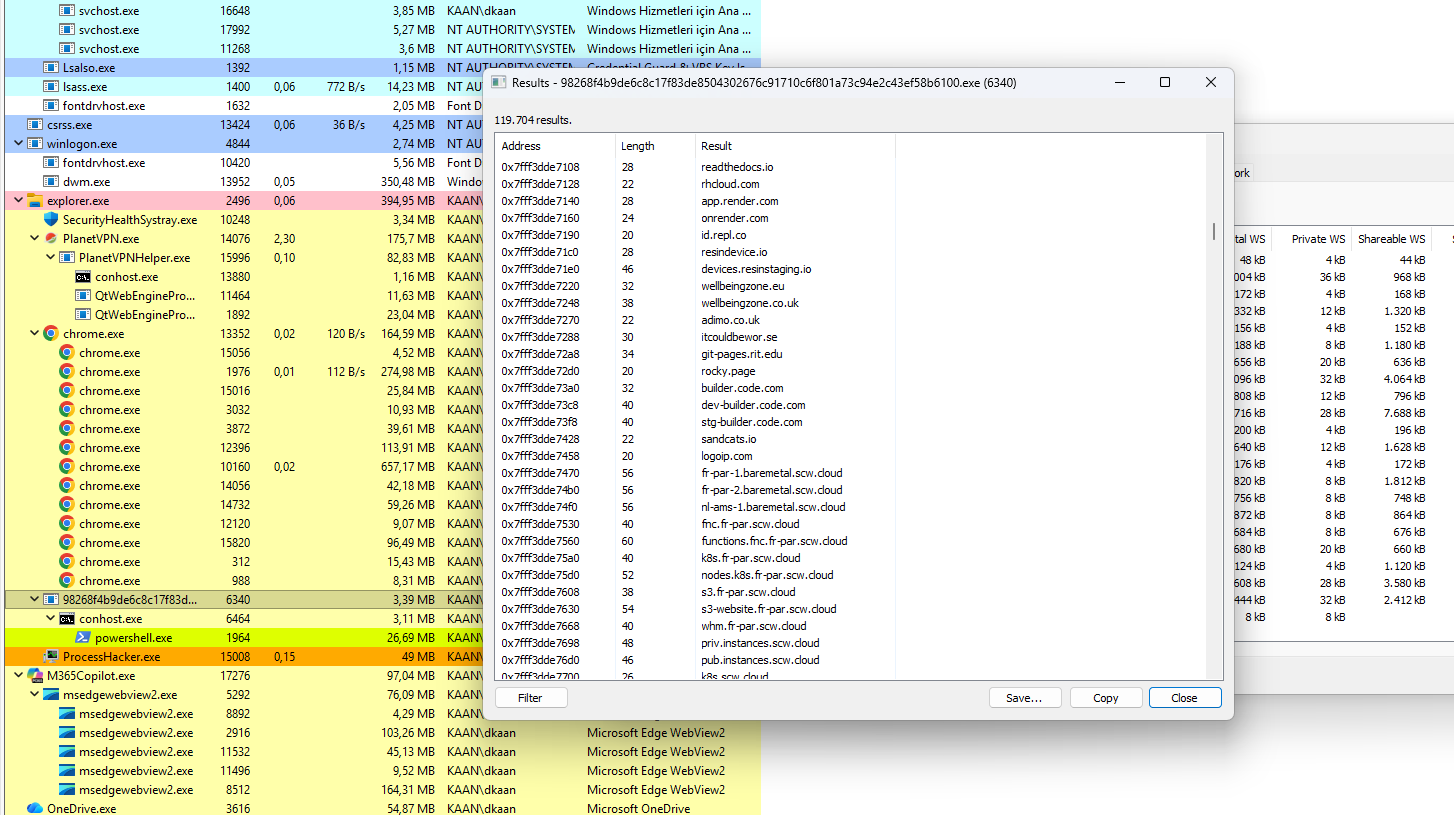 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 pcrosby-1990/cip-security-poc
Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…
 navytitanium/eitest-tools-scripts-iocs
IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…

 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…