
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
ai-ide-config-guard preview

ai-ide-config-guard

GitHubtrerb/ai-ide-config-guard

Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
code-analysiseducationmisconfiguration+4
6 months ago
CVE-2025-55182-Researching-process preview

CVE-2025-55182-Researching-process

GitHubcybersecurity-enthusiasts-ce/cve-2025-55182-researching-process

Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…

curated-resourceseducationexploitation+6
6 months ago
fibratus preview

fibratus

GitHubrabbitstack/fibratus

Security sensor for realtime threat detection and protection
defensive-toolsforensicsincident-response+3
2.5k15 days ago
YARA_Rules preview

YARA_Rules

GitHubmalgamy/yara_rules

Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
curated-resourcesdefensive-toolsincident-response+3
653 years ago
threat-research preview

threat-research

GitHubthreatray/threat-research

IoCs and YARA rules from Threatray's Threat Research
forensicsincident-responseioc-management+2
204 days ago
gitlab-cve-2026-85706-ioc preview

gitlab-cve-2026-85706-ioc

GitHubjithinkrishnanrs/gitlab-cve-2026-85706-ioc

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
defensive-toolsincident-responseinformation-gathering+8
21 month ago
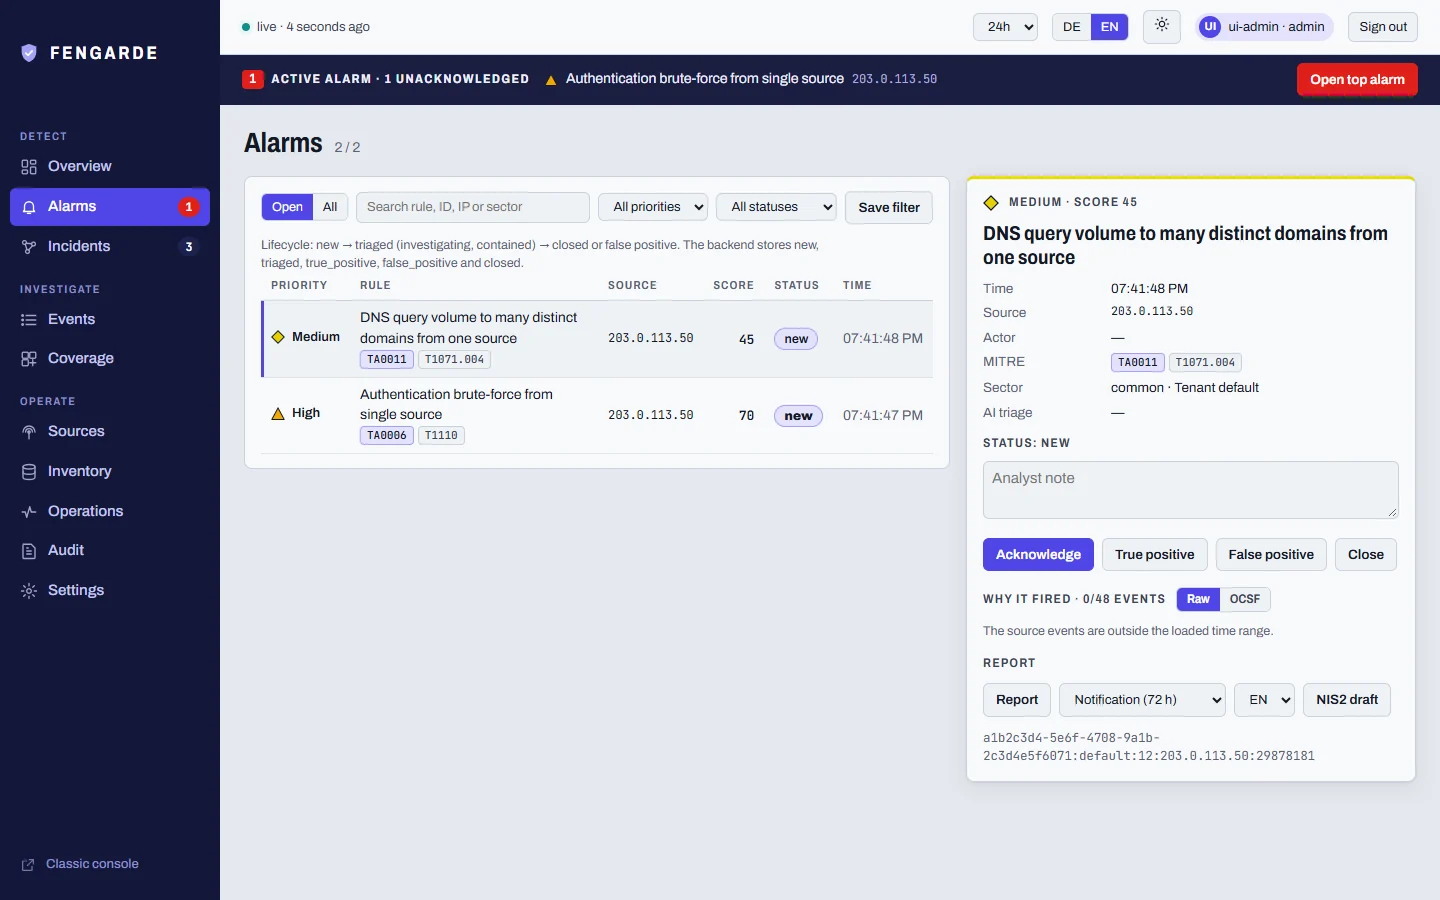
fengarde preview

fengarde

GitHubsupermhel/fengarde

Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…

ai-securitydefensive-toolsincident-response+4
154 days ago
ZeroScout preview

ZeroScout

GitHubsumidcyber/zeroscout

🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…

defensive-toolsdigital-forensicseducation+7
1111 months ago
scan preview

scan

GitHubatomdrift-project/scan

0-day malware detection for binaries, source & scripts (that doesn't suck)

binary-analysiscode-analysisdefensive-tools+9
22518h 19m ago
sigint-hombre preview

sigint-hombre

GitHubmalvuln/sigint-hombre

Dynamically generated Suricata rules from real-time threat feeds

defensive-toolsdns-analysisintrusion-detection+4
149 months ago
Yara-rules preview

Yara-rules

GitHubbartblaze/yara-rules

Collection of private Yara rules.
defensive-toolsdigital-forensicsincident-response+3
3889 months ago
yaml2yara preview

yaml2yara

GitHubnccgroup/yaml2yara

Generate bulk YARA rules from YAML input

digital-forensicsincident-responseintrusion-detection+4
226 years ago
PasteHunter preview

PasteHunter

GitHubkevthehermit/pastehunter

Scanning pastebin with yara rules

data-exfiltrationinformation-gatheringosint+1
1.1k5 years ago
Yara-Rules preview

Yara-Rules

GitHubpandare9x/yara-rules

Repository of Yara Rules

curated-resourcesdefensive-toolsmalware-analysis+2
14811 days ago
yara-rules preview

yara-rules

GitHubdr4k0nia/yara-rules

A collection of my yara rules
defensive-toolsmalware-analysisthreat-intelligence
343 years ago
Detection preview

Detection

GitHubsifalcon/detection

Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
curated-resourcesdigital-forensicsincident-response+4
243 years ago
synacktiv-rules preview

synacktiv-rules

GitHubsynacktiv/synacktiv-rules

Public repository of Sigma and YARA rules created by Synacktiv
forensicsintrusion-detectionioc-management+3
211 year ago
security-vulnerability-in-Microsoft-Office. preview

security-vulnerability-in-Microsoft-Office.

GitHubahmed-tarek22752/security-vulnerability-in-microsoft-office.

Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…

digital-forensicseducationincident-response+6
222 days ago
Previous1234Next