awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

OWASP Secure Agent Playbook Project

DDoS botnet research and indicators of compromise from Nokia Deepfield ERT

A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…

CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.

Analysis of state-sponsored WhatsApp phishing infrastructure with real-time QR hijacking and device surveillance

An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.

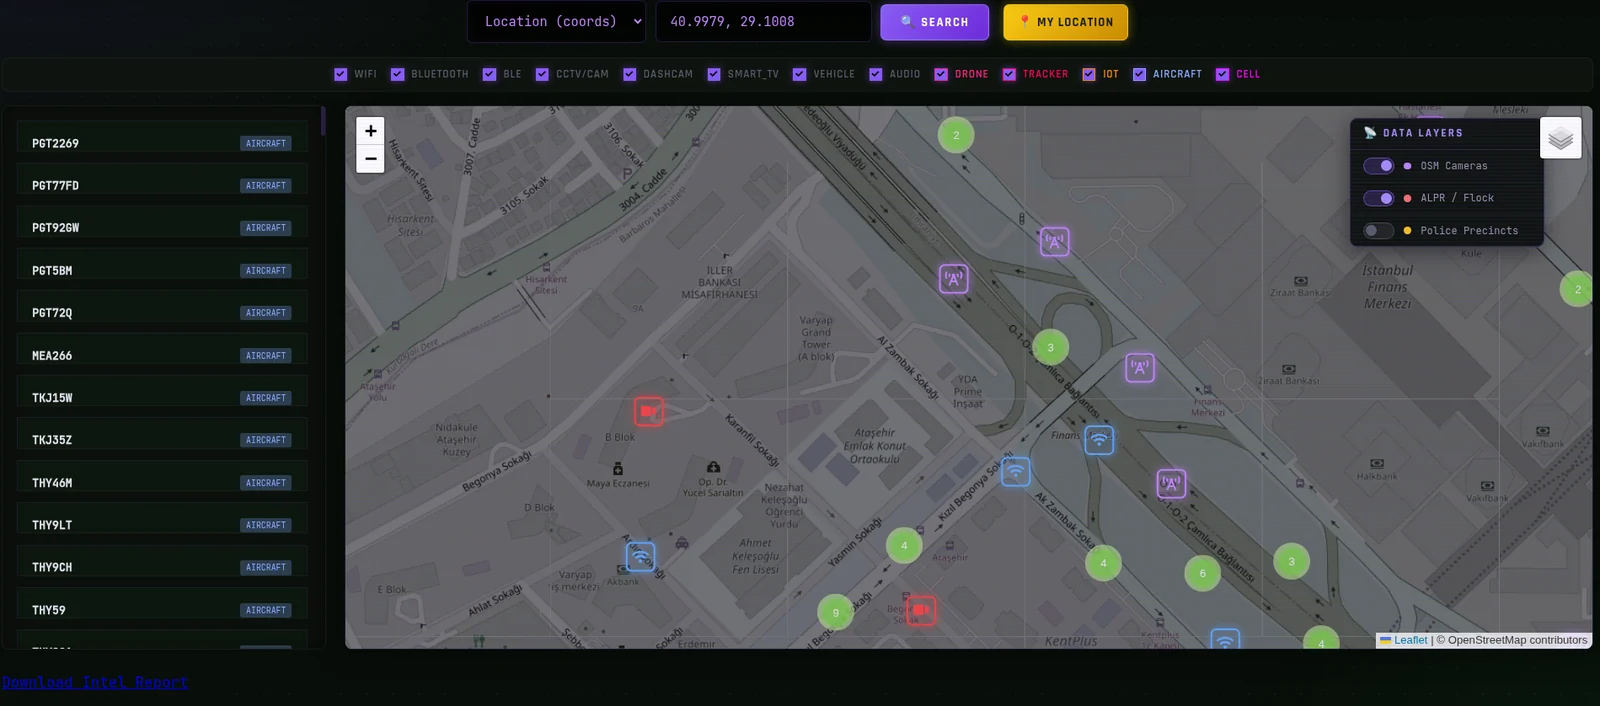
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…