
cve-2025-8088
 travisbgreen/cve-2025-8088
cve-2025-8088_detection
exploitationintrusion-detectionioc-management+3
travisbgreen/cve-2025-8088cve-2025-8088_detection
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 faysalferdous/cve-2025-68645-exploiting-zimbra-webmail-lfi-vulnerability
Defender-focused reference pack for CVE-2025-68645 Zimbra LFI, including Sigma/Splunk detection rules, WAF mitigation snippets, IOC patterns, and…
 eliushhimel/citrix-honeypot
Citrix ADC (NetScaler) Honeypot. Supports detection for CVE-2019-19781 and login attempts
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 paspke/scavenger_scanner
Detect CVE-2025-54313 eslint-config-prettier supply chain attack IOCs on Windows
 atlas-ghostshell/cve-2025-27558_patching
Patching CVE-2025-27558 vulnerability that had affected my linux image.
 digitalshadows/cve-2019-19781_iocs
Curated indicators of compromise (IOCs) for CVE-2019-19781, including IP addresses and whois data from honeypot logs to aid threat detection and…
 elshaheedy/cve-2025-29927-sigma-rule
Sigma rule for detecting CVE-2025-29927 exploitation via suspicious x-middleware-subrequest HTTP headers in Next.js applications, with detection…
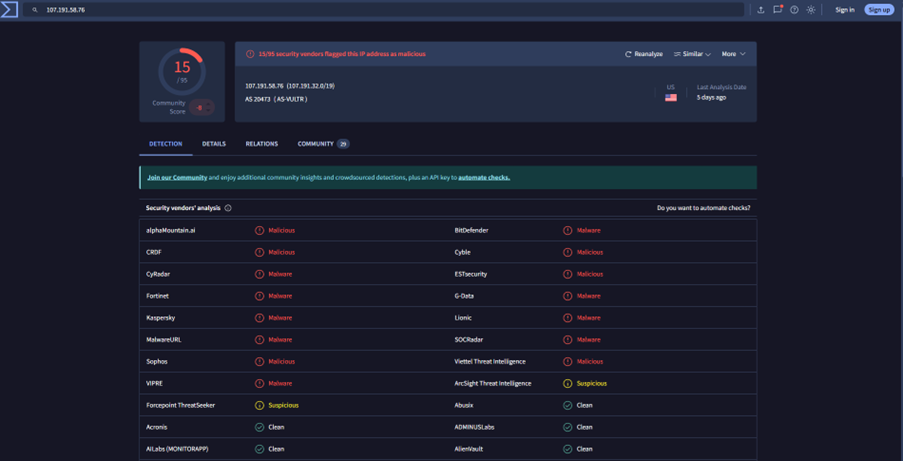 michaael01/letsdefend--soc-342-cve-2025-53770-sharepoint-exploit-toolshell
Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload…
 nivdolgin/cve-2018-13379
Hunting CVE-2018-13379
 mandiant/ioc-scanner-cve-2019-19781
Indicator of Compromise Scanner for CVE-2019-19781
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 kiteworks/security-advisories
Publishes Kiteworks security advisories and CVE disclosures, including vulnerability details, disclosure policy, and bug bounty information for…
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 logesh-git001/cve-2025-55182
"One crafted HTTP request can compromise your entire server." — React Security Team, Dec 2025
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…