
check-cve-2026-23111
 criann/check-cve-2026-23111
Script to check if system are vulnable to cve-2026-23111
configuration-auditingeducationincident-response+4
criann/check-cve-2026-23111Script to check if system are vulnable to cve-2026-23111
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 otrf/ossem
Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…
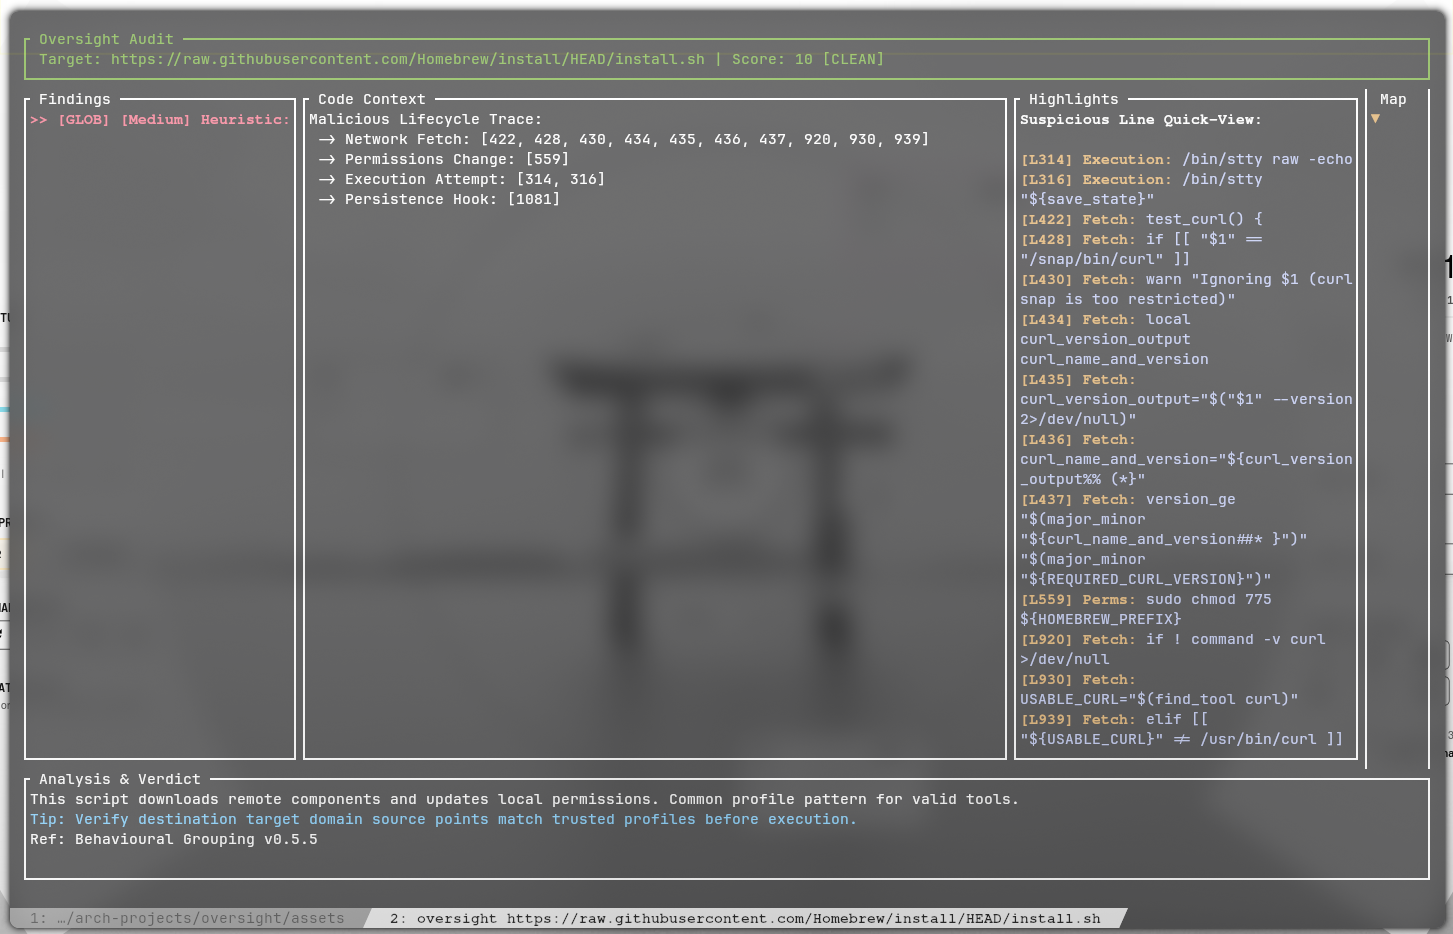 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
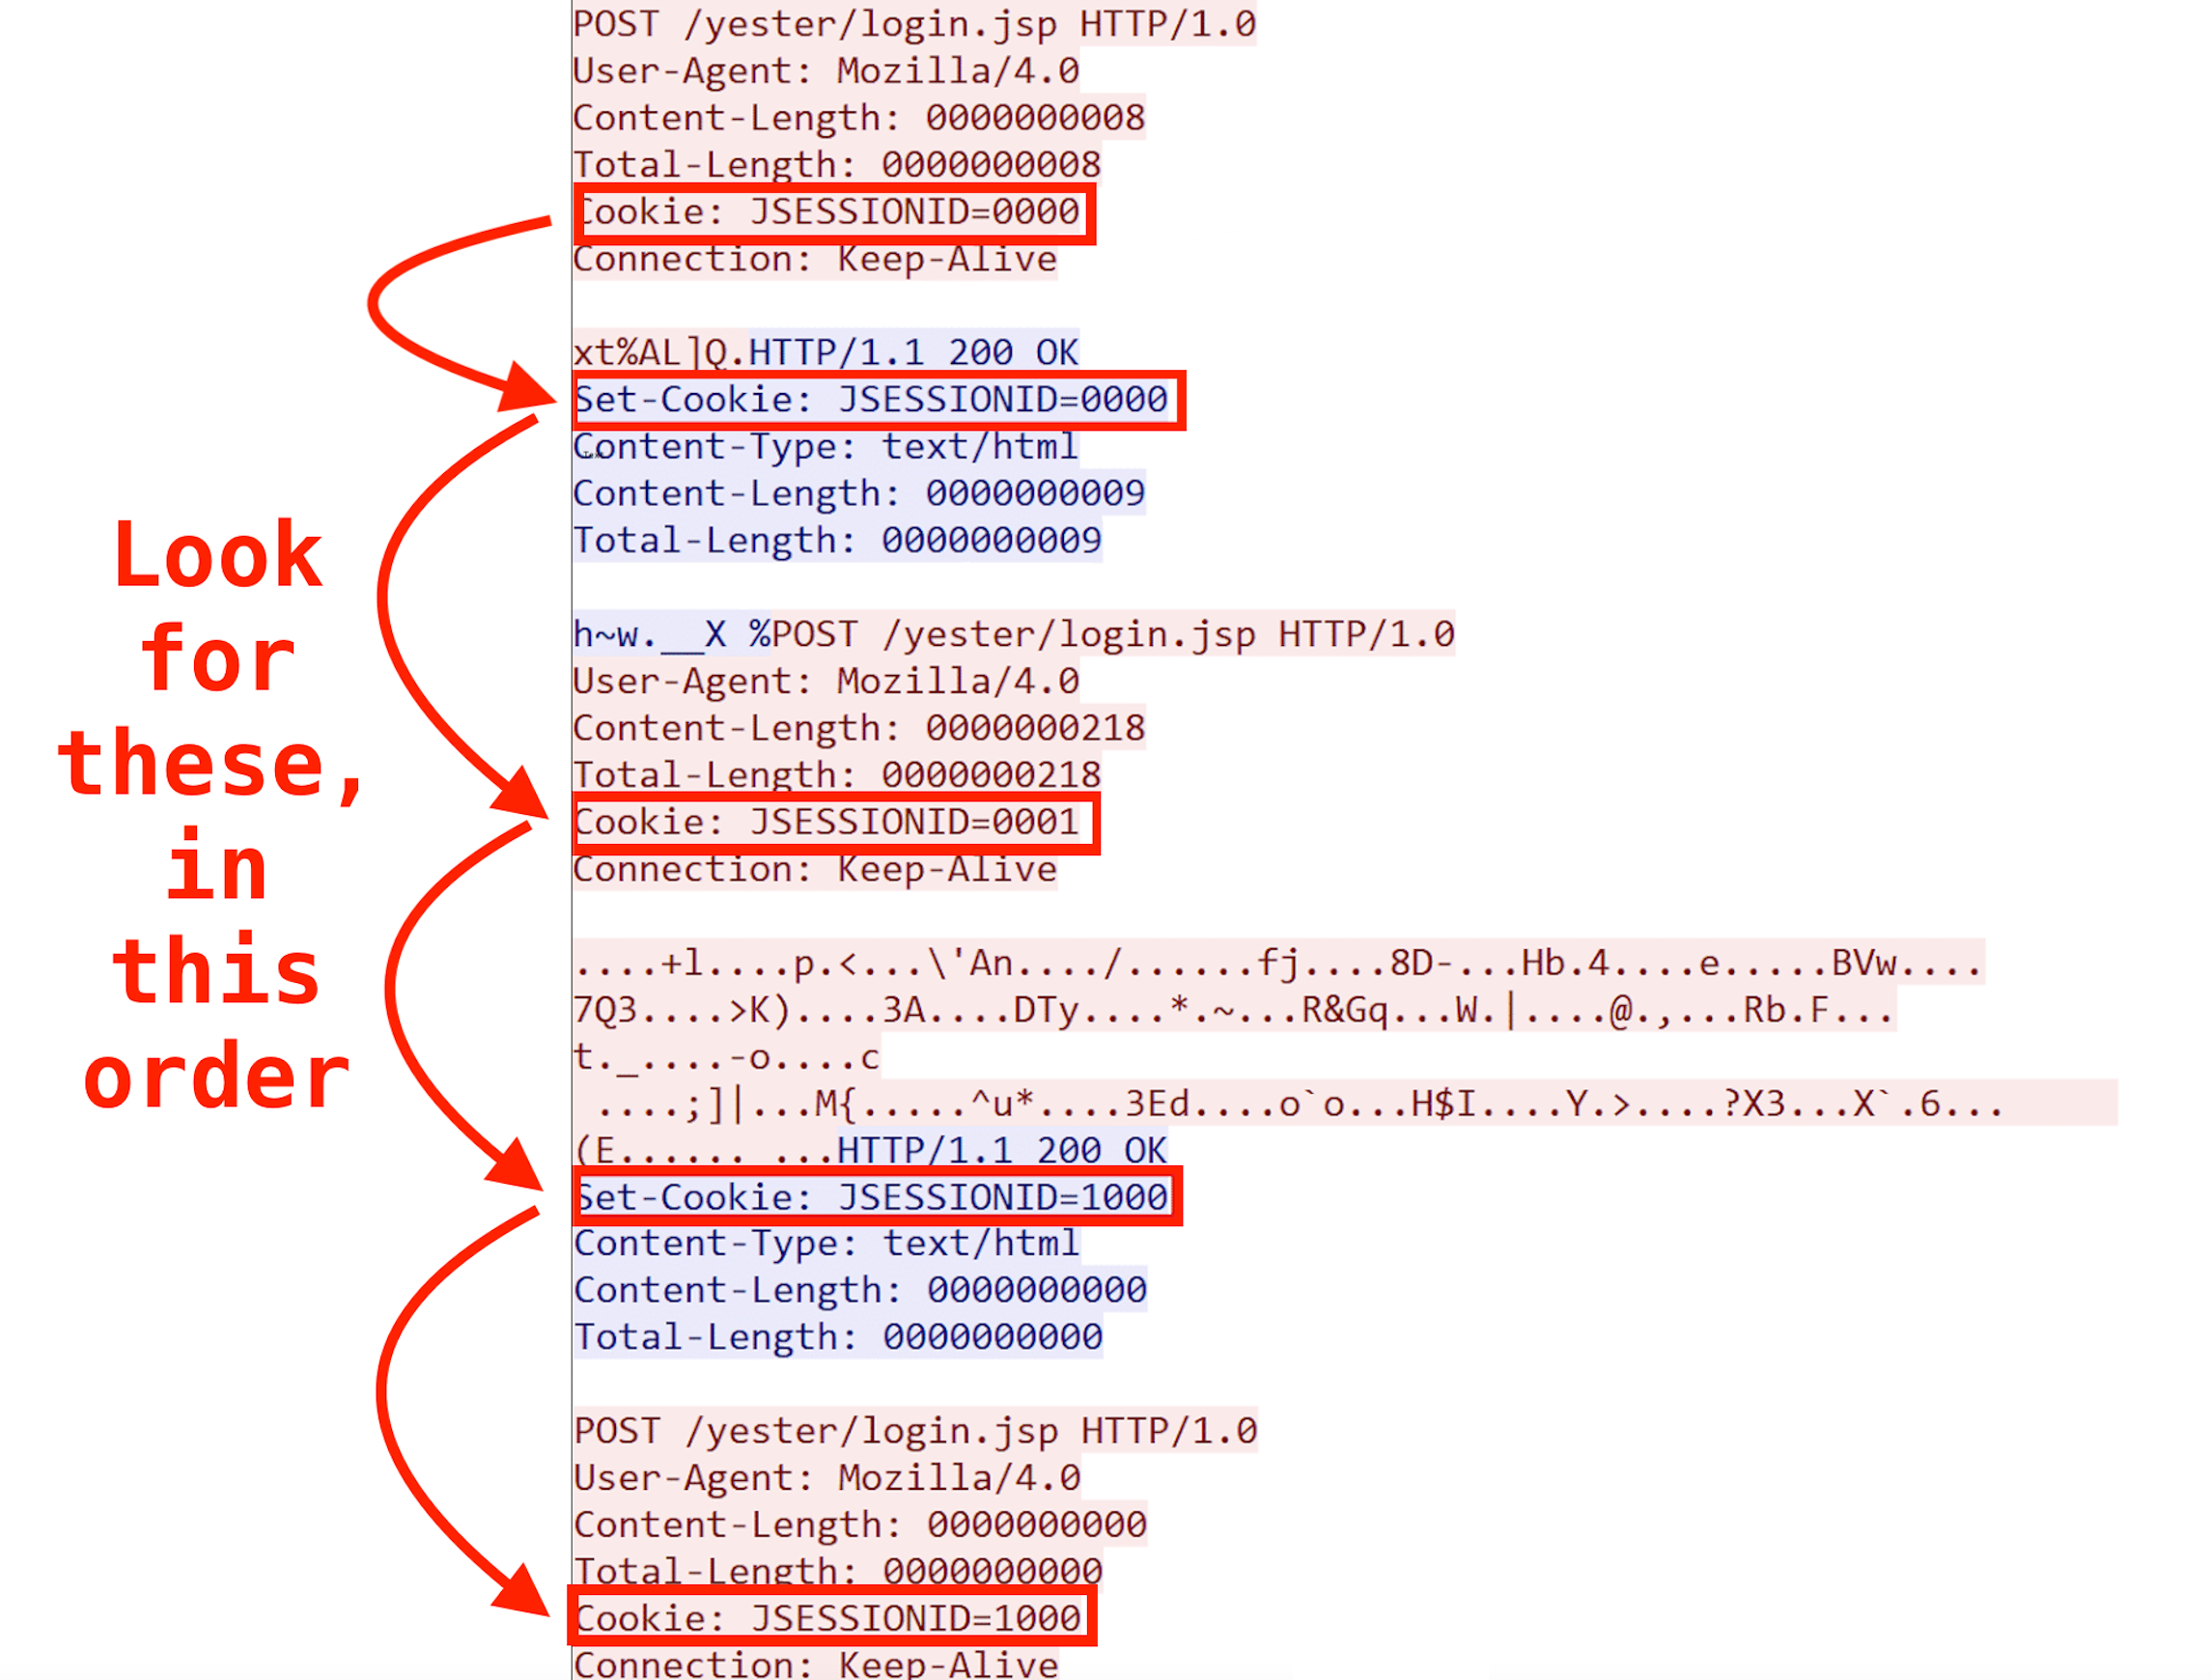 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration