

Honeypot-Project
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
defensive-toolseducationincident-response+5
109
owasp/honeypot-projectDeploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
 owasp/honeysap
HoneySAP: SAP Low-interaction research honeypot
 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
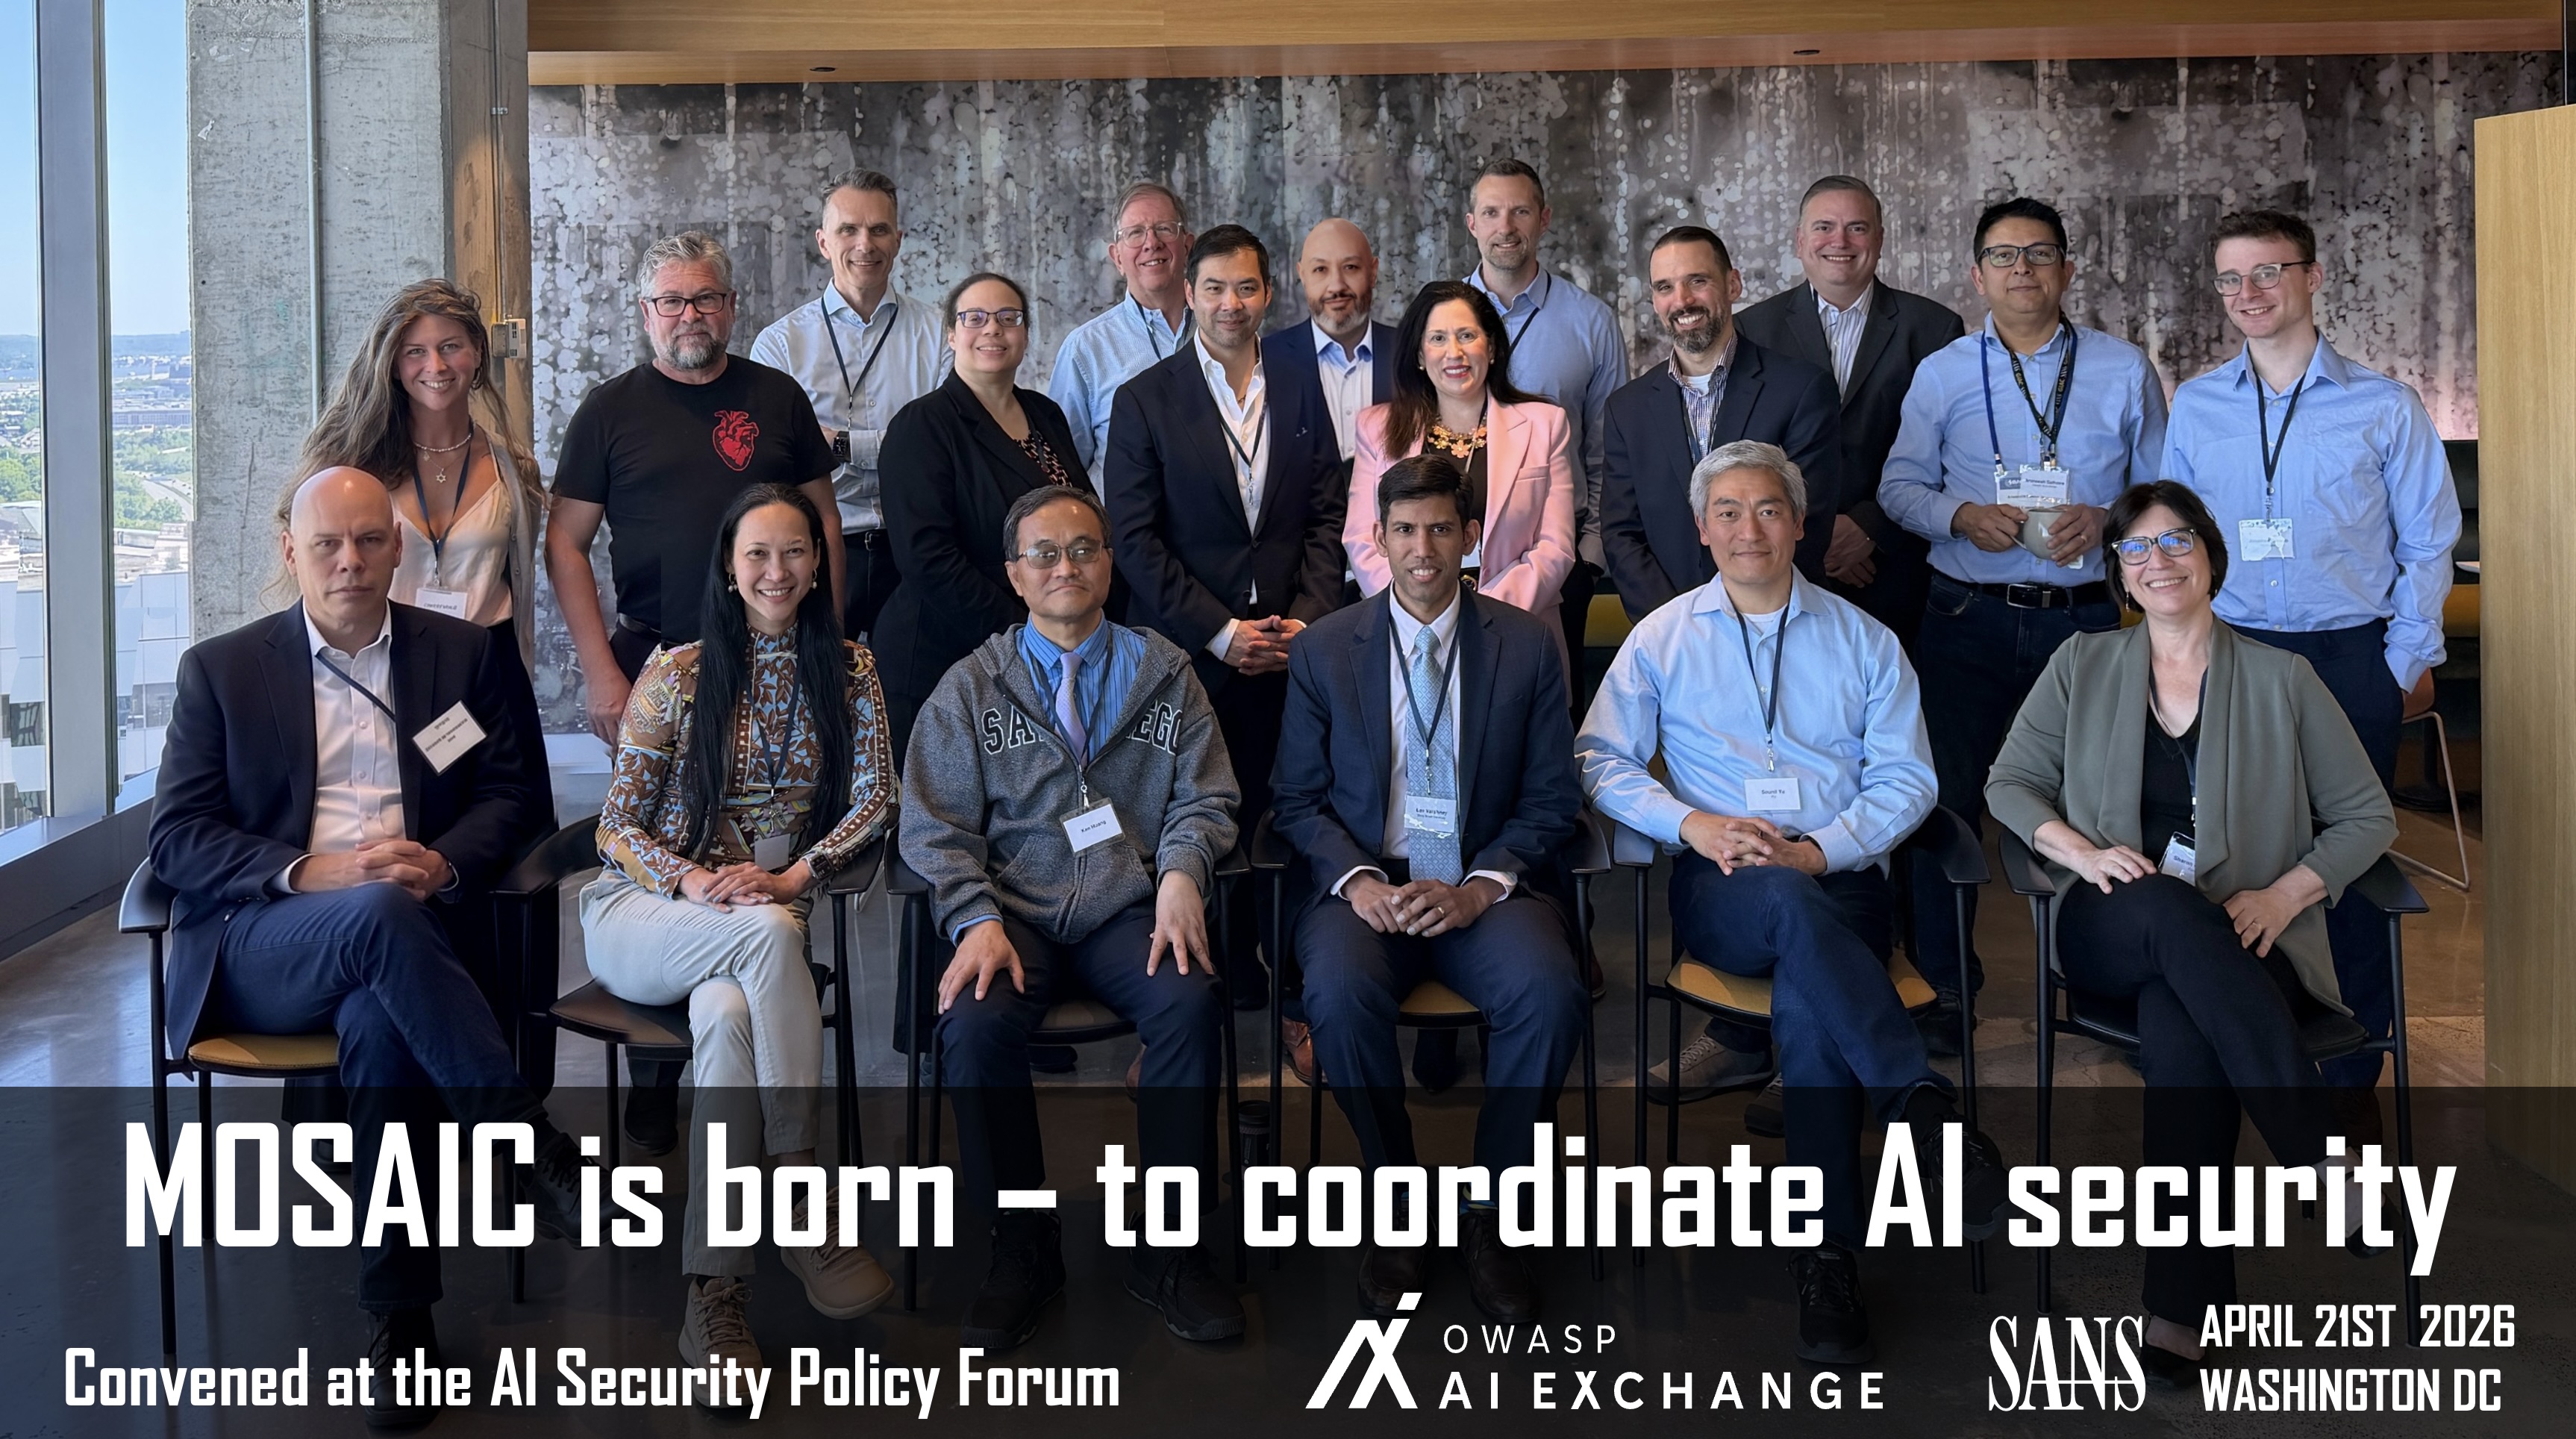 owasp/mosaic
Coordination structure for AI security standards and guidelines, reducing fragmentation and providing clear guidance for securing AI systems across…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
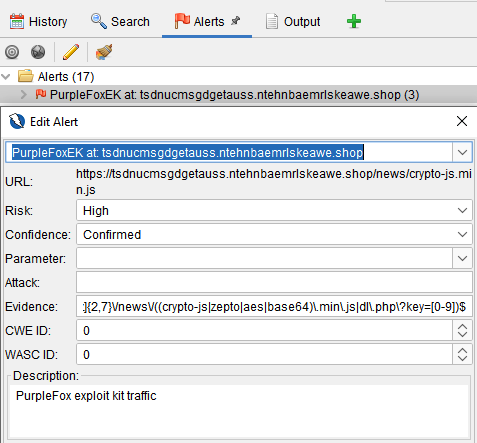 malwareinfosec/fiddlezap
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.