
Malcolm
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
digital-forensicsdns-analysisforensics+9
2.5k
cisagov/malcolmContainerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
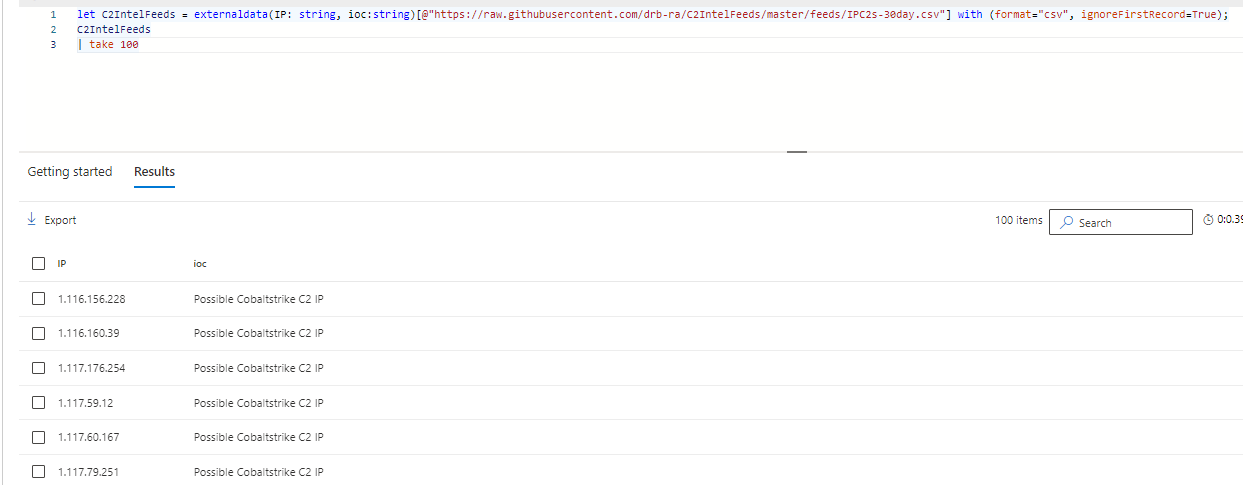 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 sophoslabs/iocs
Sophos-originated indicators-of-compromise from published reports
 paloaltonetworks/unit42-timely-threat-intel
A collection of files with indicators supporting social media posts from Palo Alto Network's Unit 42 team to disseminate timely threat intelligence.
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 aquasecurity/vuln-list-update
Automated vulnerability data aggregator that collects advisories from NVD, OSV, Alpine, Red Hat, and 20+ other sources into a unified parsable format…
 akamai/akamai-security-research
This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.
 gendigitalinc/ioc
Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
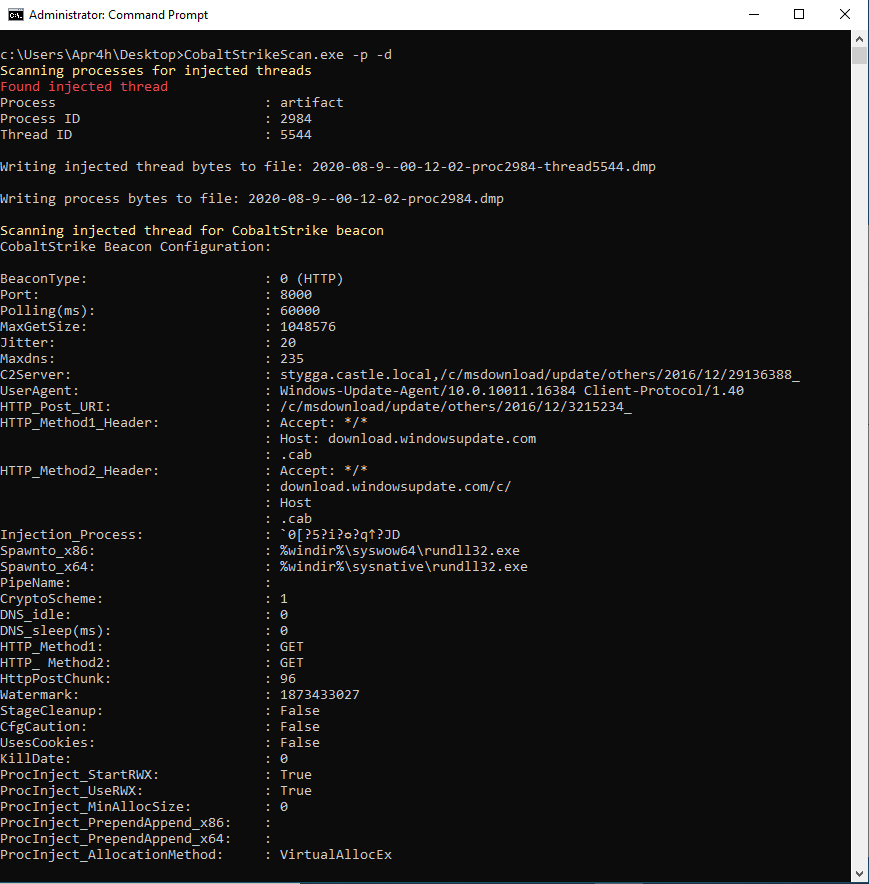 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration

 back2root/log4shell-rex
PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
 fhightower/ioc-finder
Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…