
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
16 results
intercept preview

intercept

GitHubsmittix/intercept

iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
bluetooth-securityeducationembedded-systems-security+7
2.4k
2 days ago
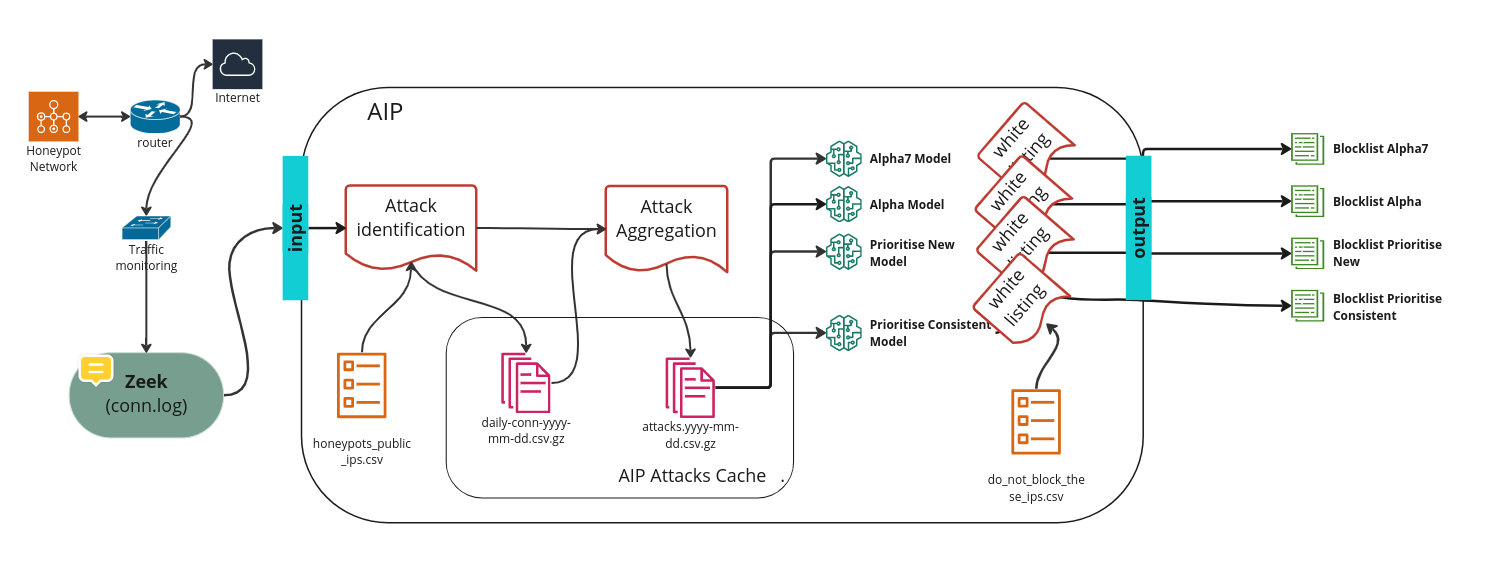
AIP preview

AIP

GitHubstratosphereips/aip

Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
information-gatheringintrusion-detectioniot-security+3
324 days ago
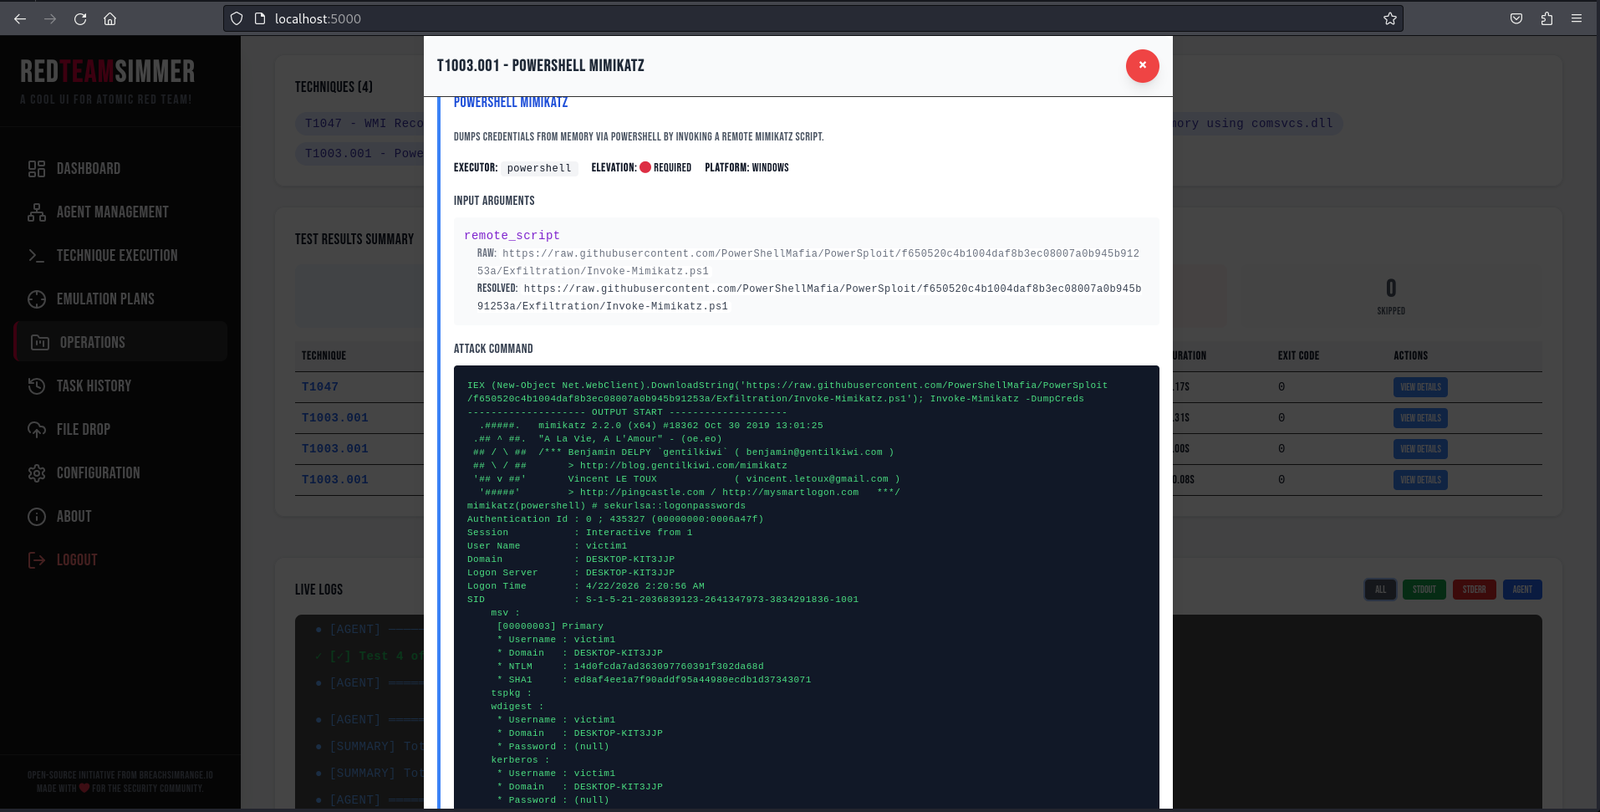
RedTeamSimmer preview

RedTeamSimmer

GitHubbreachsimrange/redteamsimmer

Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
adversarial-attackcommand-and-controldefensive-tools+7
131 month ago
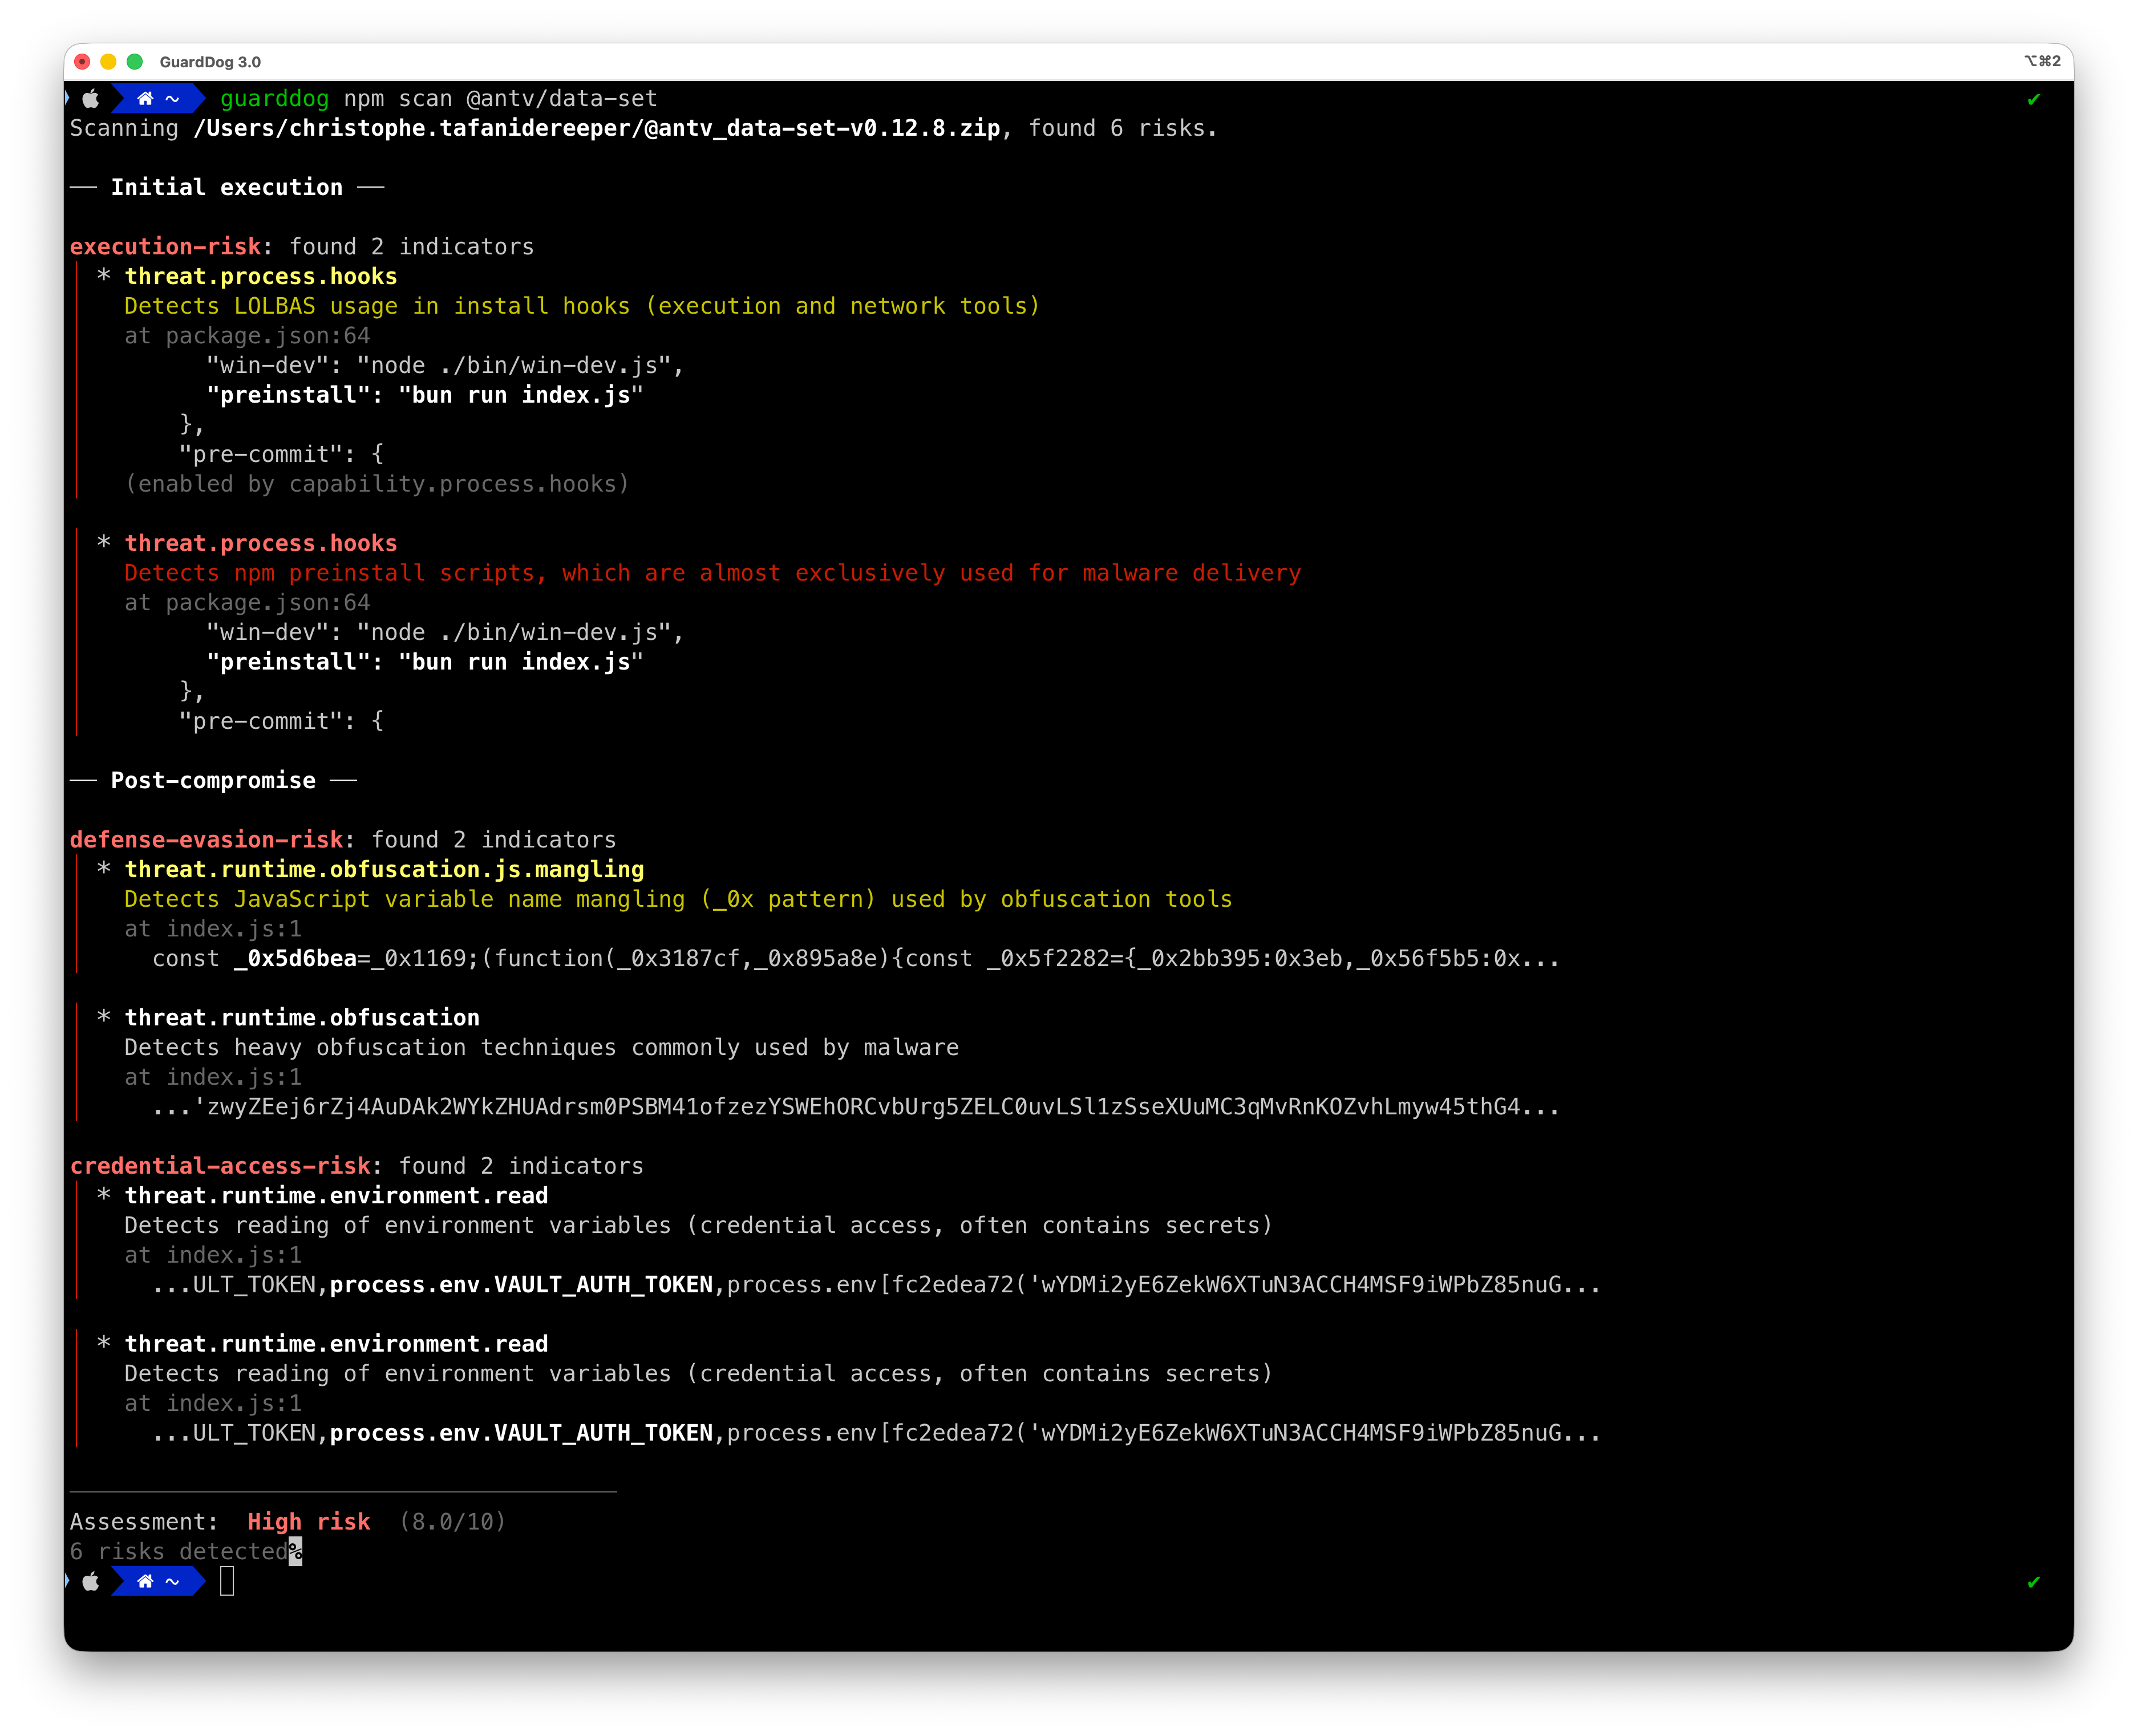
guarddog preview

guarddog

GitHubdatadog/guarddog

🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
code-analysisdevsecopsdynamic-analysis-sandboxing+6
1.2k1 month ago
strelka-ui preview

strelka-ui

GitHubtarget/strelka-ui

Strelka Web UI for File Submission and Analysis
authenticationdefensive-toolslog-analysis+2
751 month ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log
ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
oversight preview

oversight

GitHubrakosn1cek/oversight

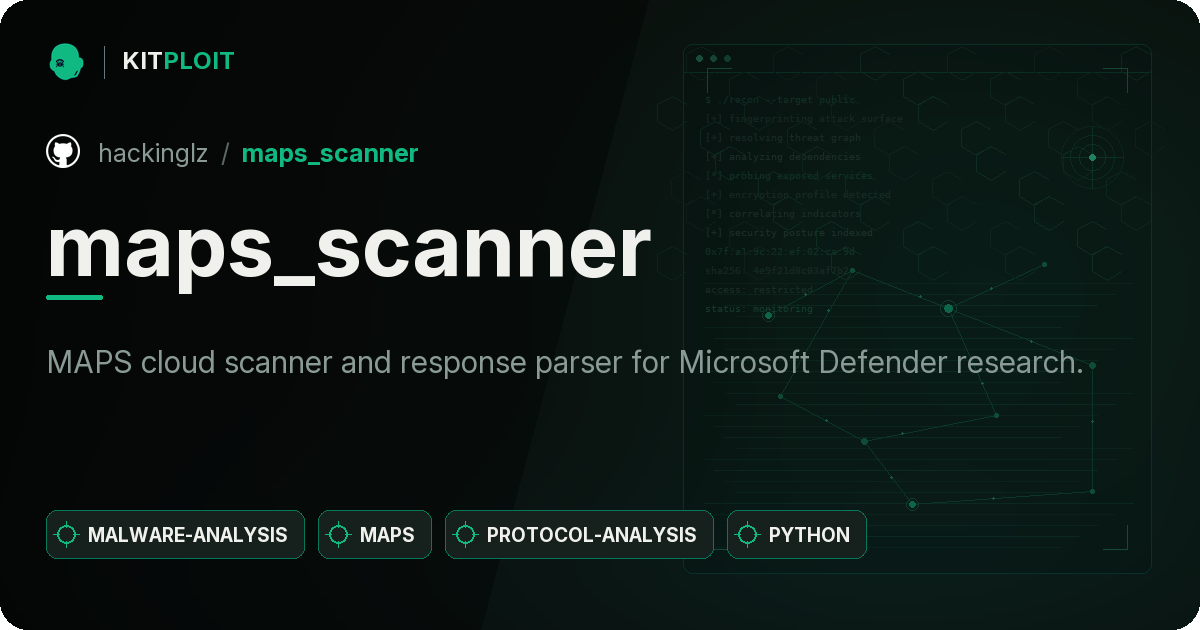
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
code-analysisdevsecopsdynamic-analysis-sandboxing+7
392 months ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.
api-security-testingdynamic-analysis-sandboxingfuzzing+6
968 months ago
cve-2025-55182-scanner preview

cve-2025-55182-scanner

GitHubtechgaun/cve-2025-55182-scanner

Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
forensicsincident-responsemalware-analysis+3
310 months ago
TERM1B1TB0T preview

TERM1B1TB0T

GitHubmykethearchangel/term1b1tb0t

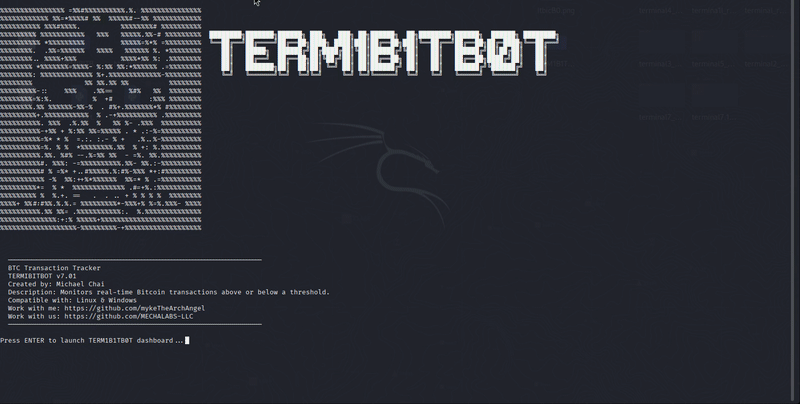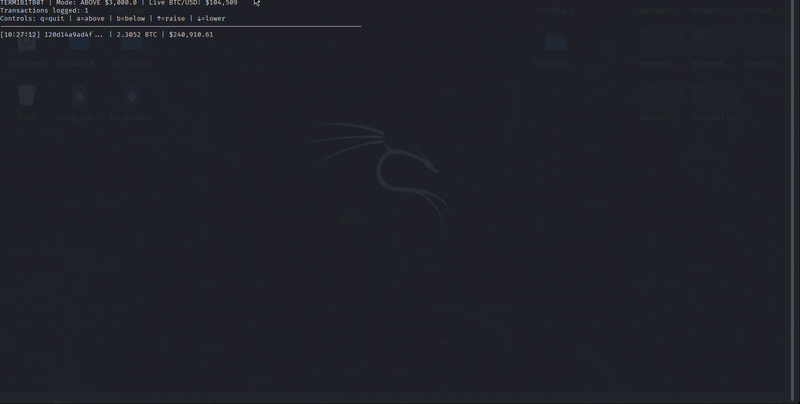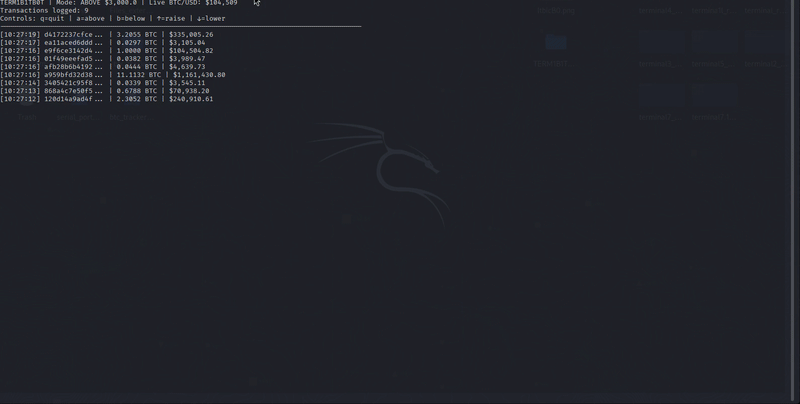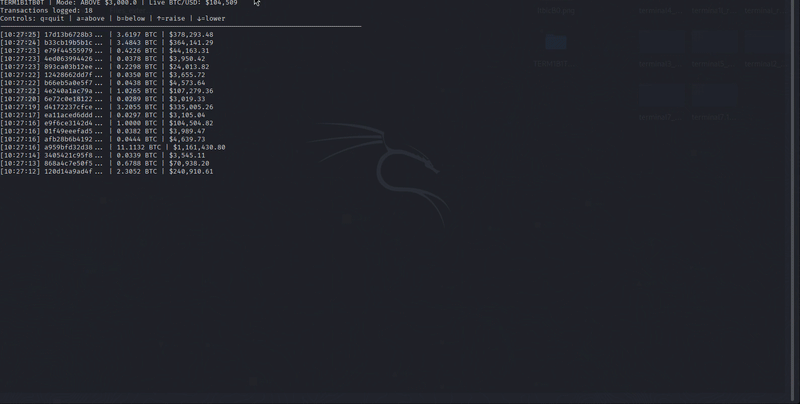
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.
cryptographygeneral-purpose-utilitiesinformation-gathering+2
1211 months ago
PatrowlHears preview

PatrowlHears

GitHubpatrowl/patrowlhears

PatrowlHears - Vulnerability Intelligence Center / Exploits
defensive-toolsexploitationinformation-gathering+3
1671 year ago
ThePhish preview

ThePhish

GitHubemalderson/thephish

ThePhish: an automated phishing email analysis tool
digital-forensicsemail-securityincident-response+5
1.4k2 years ago
ThreatScraper preview

ThreatScraper

GitHubamorath/threatscraper

Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…
information-gatheringmalware-analysisthreat-intelligence+1
73 years ago
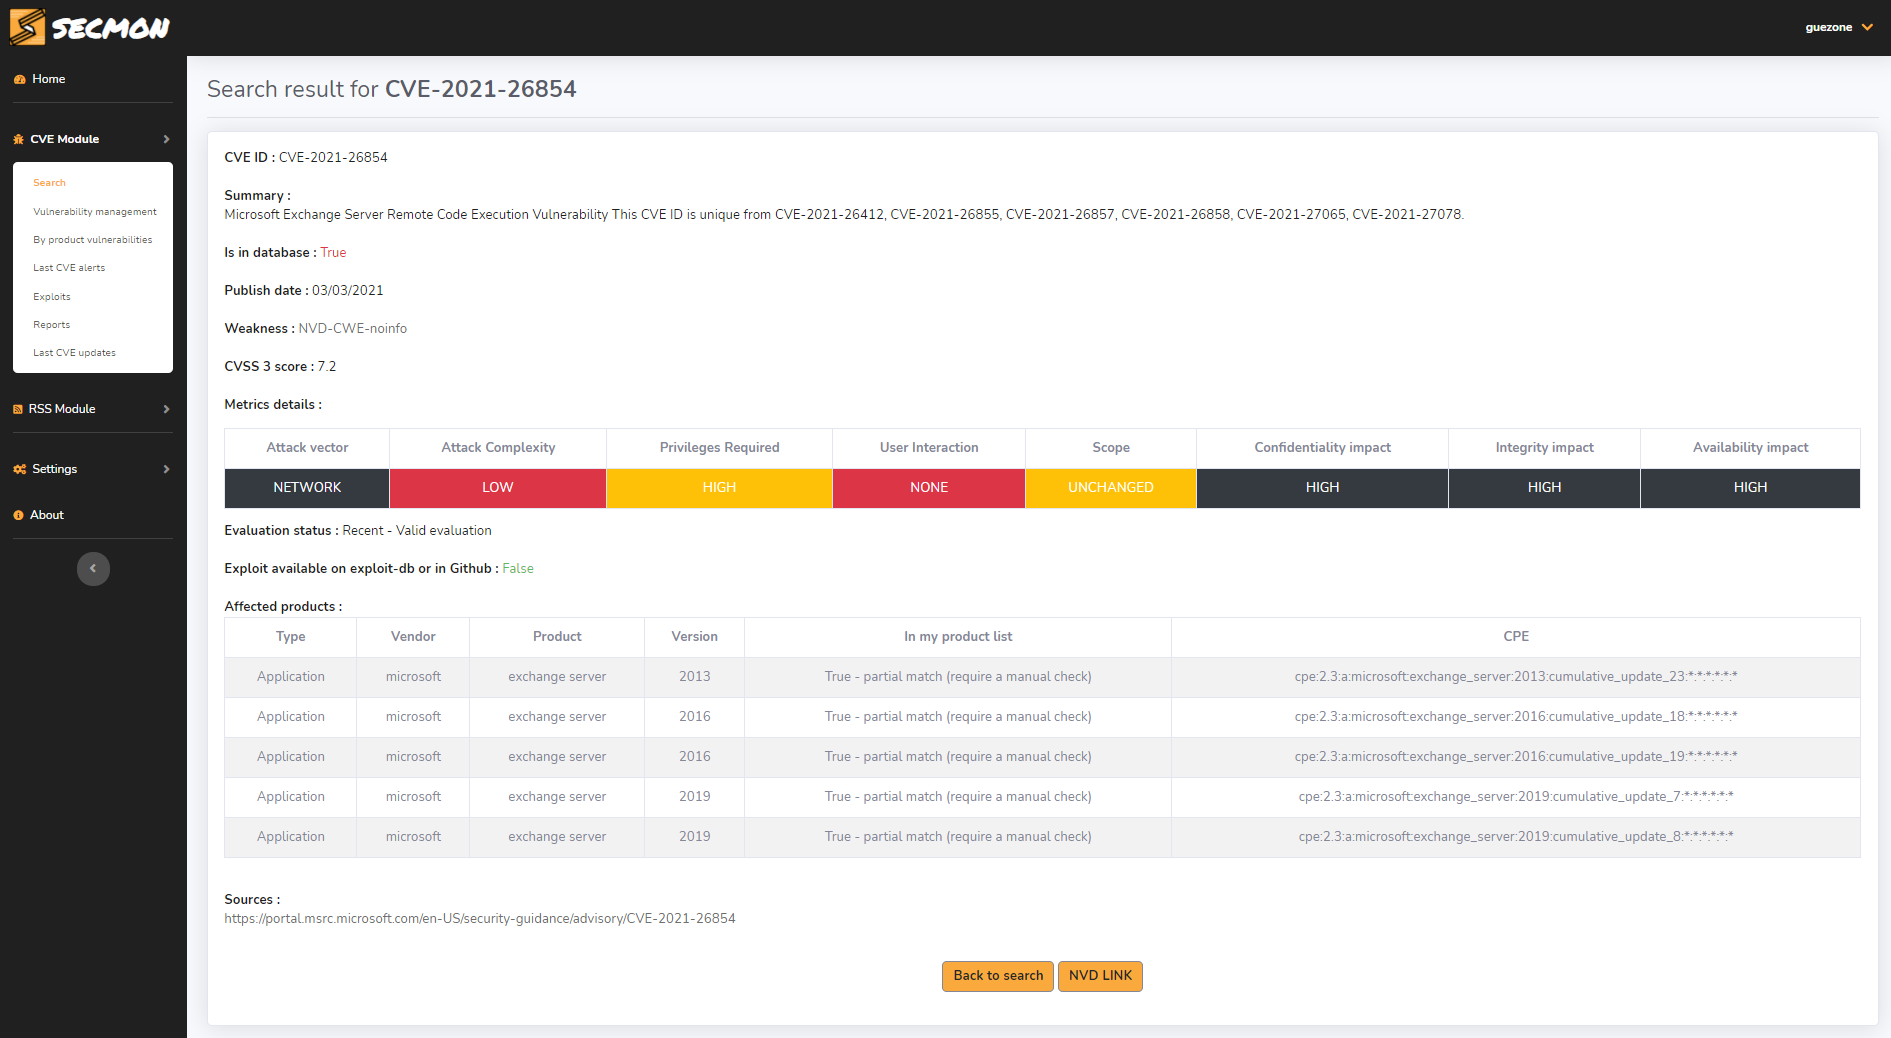
SECMON preview
Archived

SECMON

GitHubalb-uss/secmon

SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
email-securityexploitationinformation-gathering+4
2684 years ago
fatt preview

fatt

GitHub0x4d31/fatt

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic
network-forensicspacket-sniffing-analysisthreat-intelligence
6844 years ago
joy preview

joy

GitHubcisco/joy

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.

anomaly-detectiondigital-forensicsdns-analysis+7
1.4k6 years ago