regipy
 mkorman90/regipy
Regipy is an os independent python library for parsing offline registry hives
digital-forensicsforensicsincident-response+1
mkorman90/regipyRegipy is an os independent python library for parsing offline registry hives
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 zerodayvpn/cve-2026-41089-netlogon
🛡️ Official AI Security Tool diagnostic module for CVE-2026-41089 (Windows Netlogon Stack Buffer Overflow RCE). Features technical writeup, attack…
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 gubiczap/cve-2026-31431-checker
Shell scanner for CVE-2026-31431 "Copy Fail" — a local privilege escalation via Linux kernel page cache corruption (algif_aead/AF_ALG). Checks kernel…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
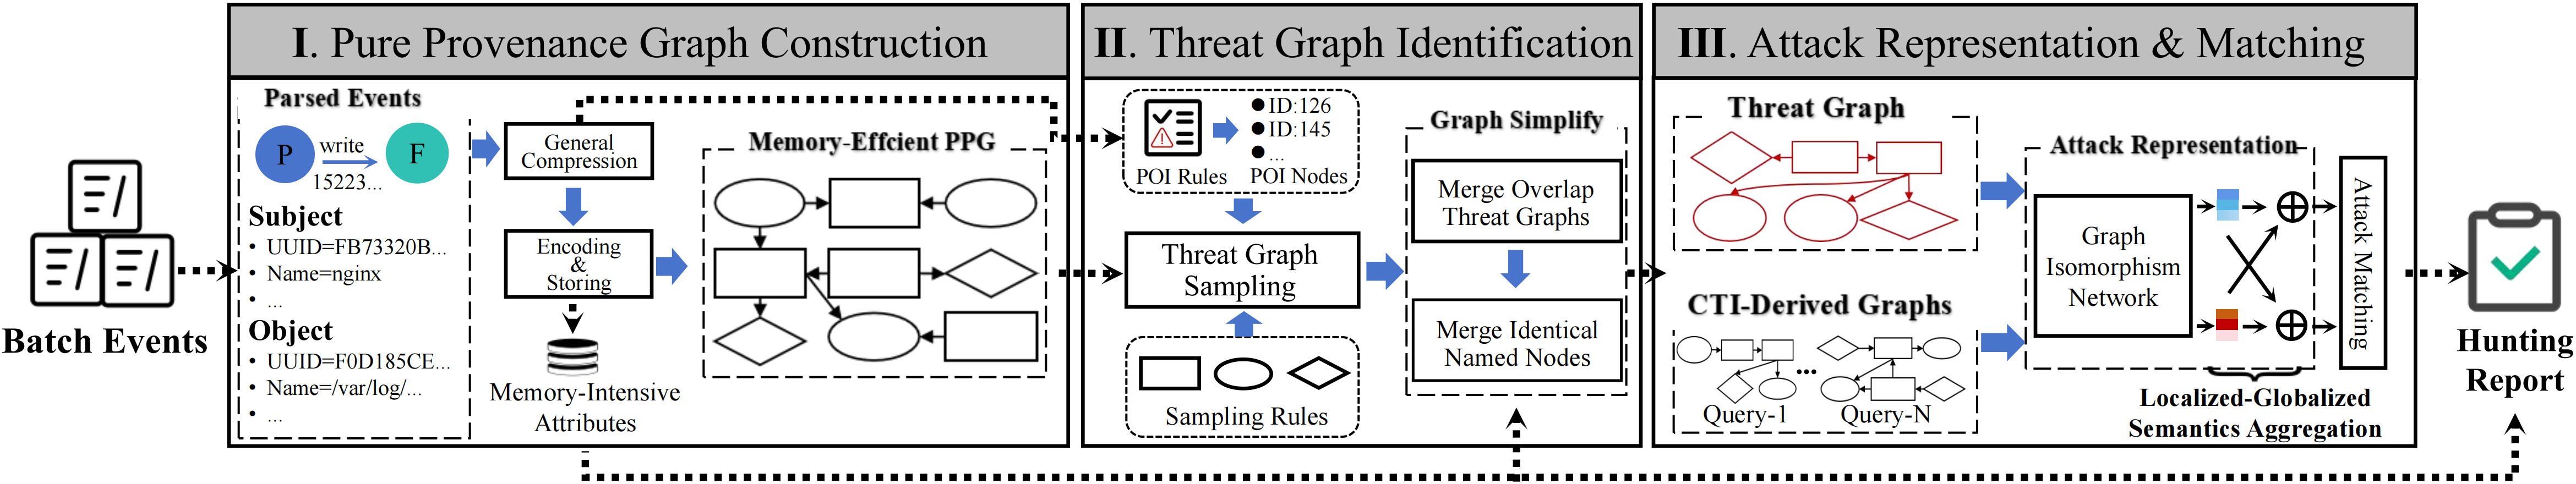 xueboqiu/prohunter
Graph-based threat detection system using inexact graph vector matching to compare threat graphs with CTI-derived attack query graphs for automated…
 xakepnz/enterpriseattack
A lightweight Python module to interact with the [MITRE ATT&CK®](https://attack.mitre.org/) Enterprise dataset. Built for speed with minimal…
 jacobsoo/amtracker
Android Malware Tracker
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 alexverboon/psmdatp
PowerShell Module for managing Microsoft Defender Advanced Threat Protection
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
 murataydemir/greyenergy-mini-module-malware-analysis
GreyEnergy Mini Module Malware Analysis (Turkish)
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.