

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
102 results
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

anomaly-detectionanti-botdefensive-tools+11
8.6k
8h 25m ago
tenzir preview

tenzir

GitHubtenzir/tenzir

Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…

incident-responselog-analysisnetwork-security+1
76613h 2m ago
spamassassin preview

spamassassin

GitHubapache/spamassassin

Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.

defensive-toolsemail-securitymachine-learning+1
34517h 52m ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k18h 26m ago
RansomLook preview

RansomLook

GitHubransomlook/ransomlook

Yet another Ransomware gang tracker
crawlerdefensive-toolsinformation-gathering+3
67719h 39m ago
pmg preview

pmg

GitHubsafedep/pmg

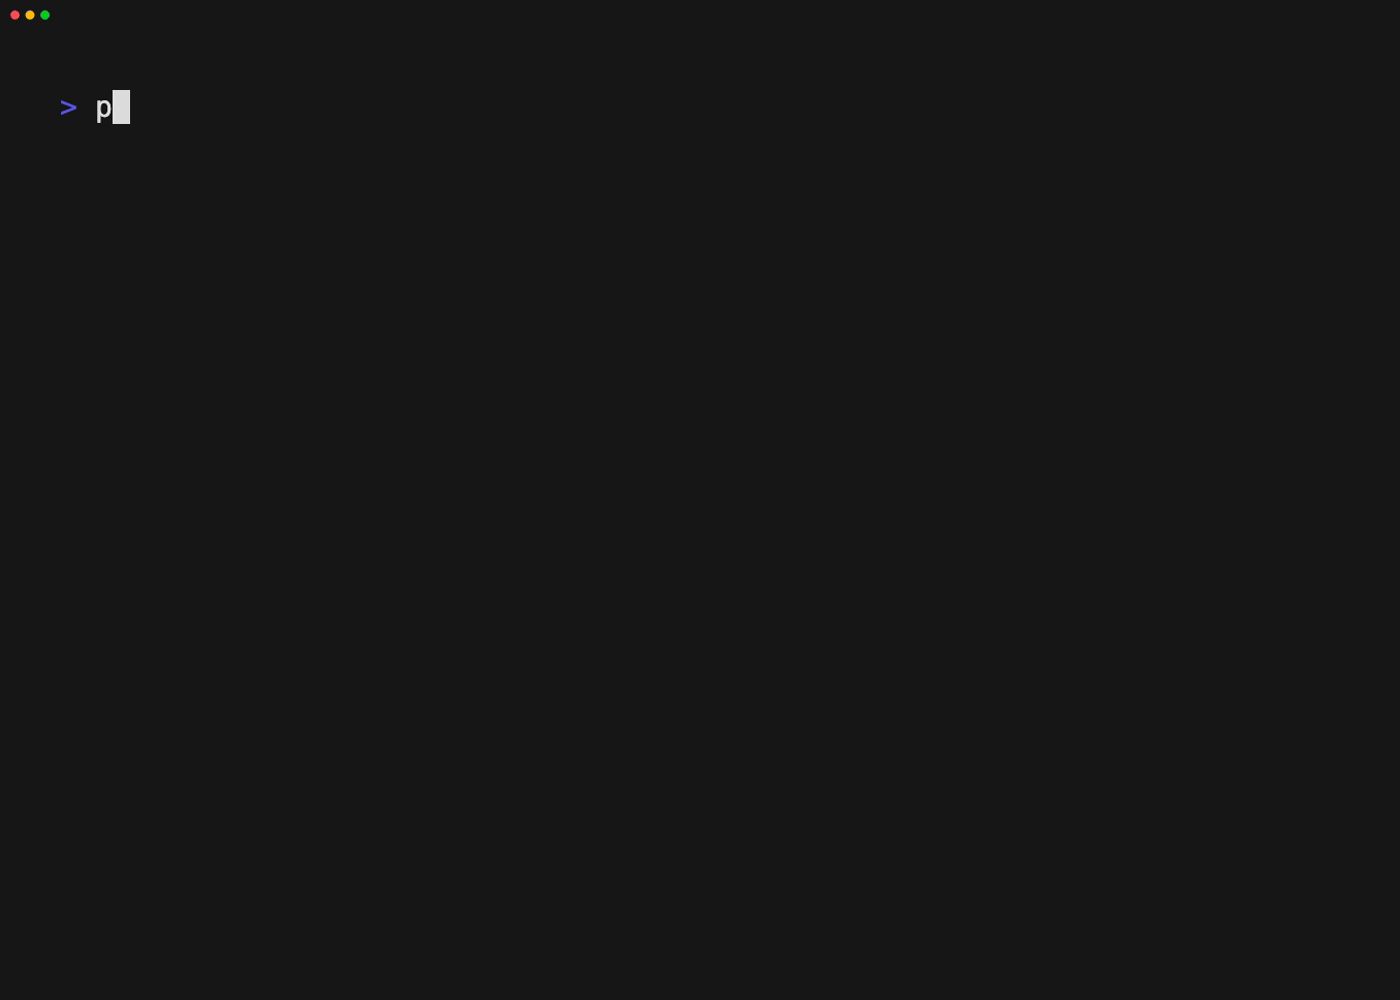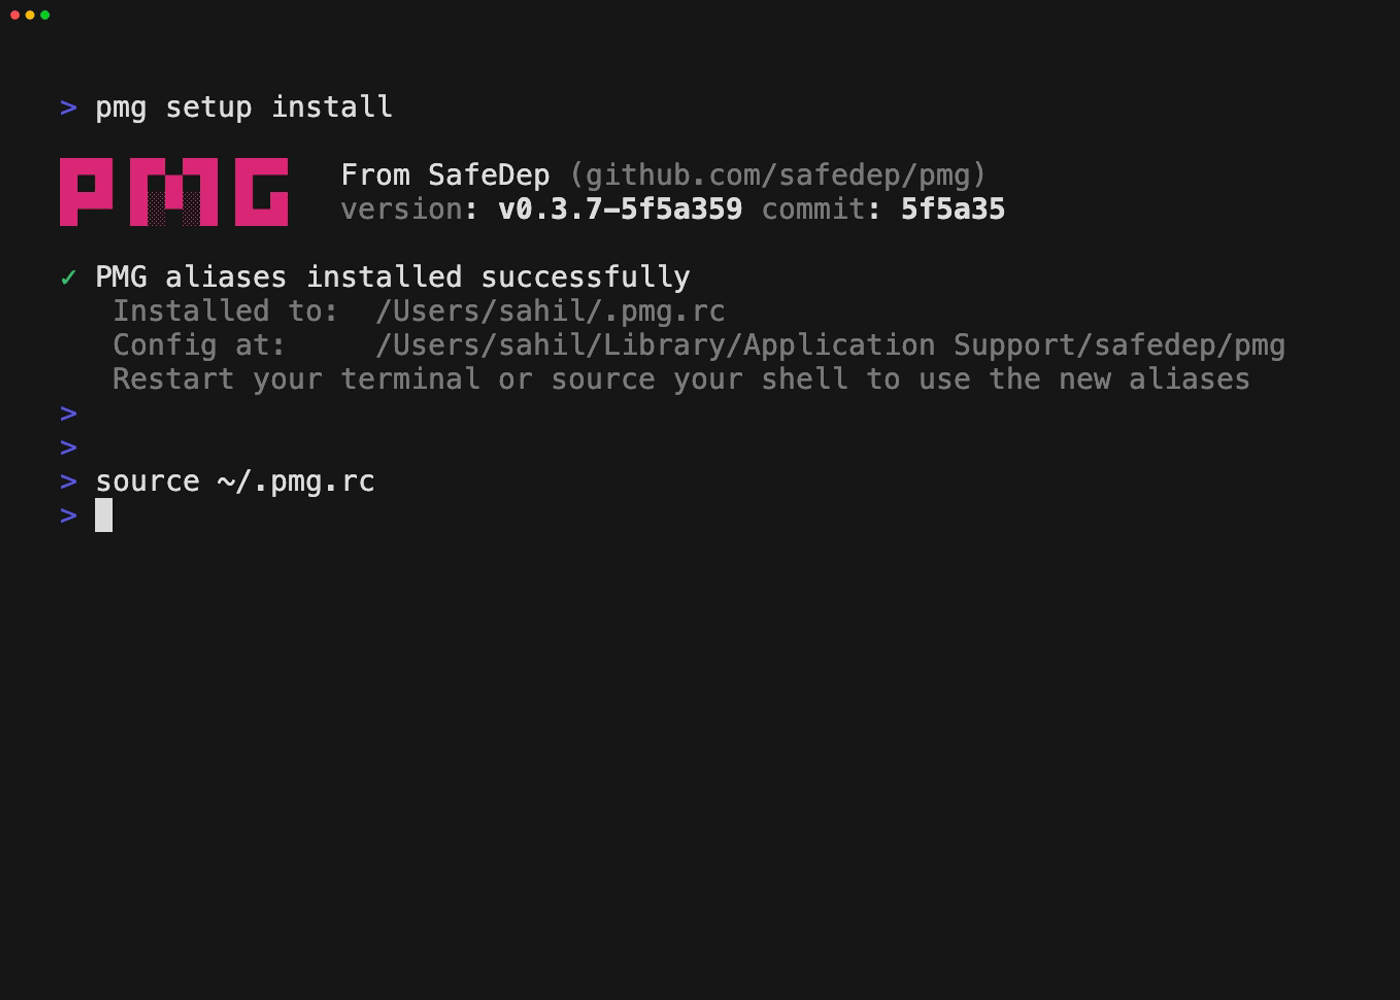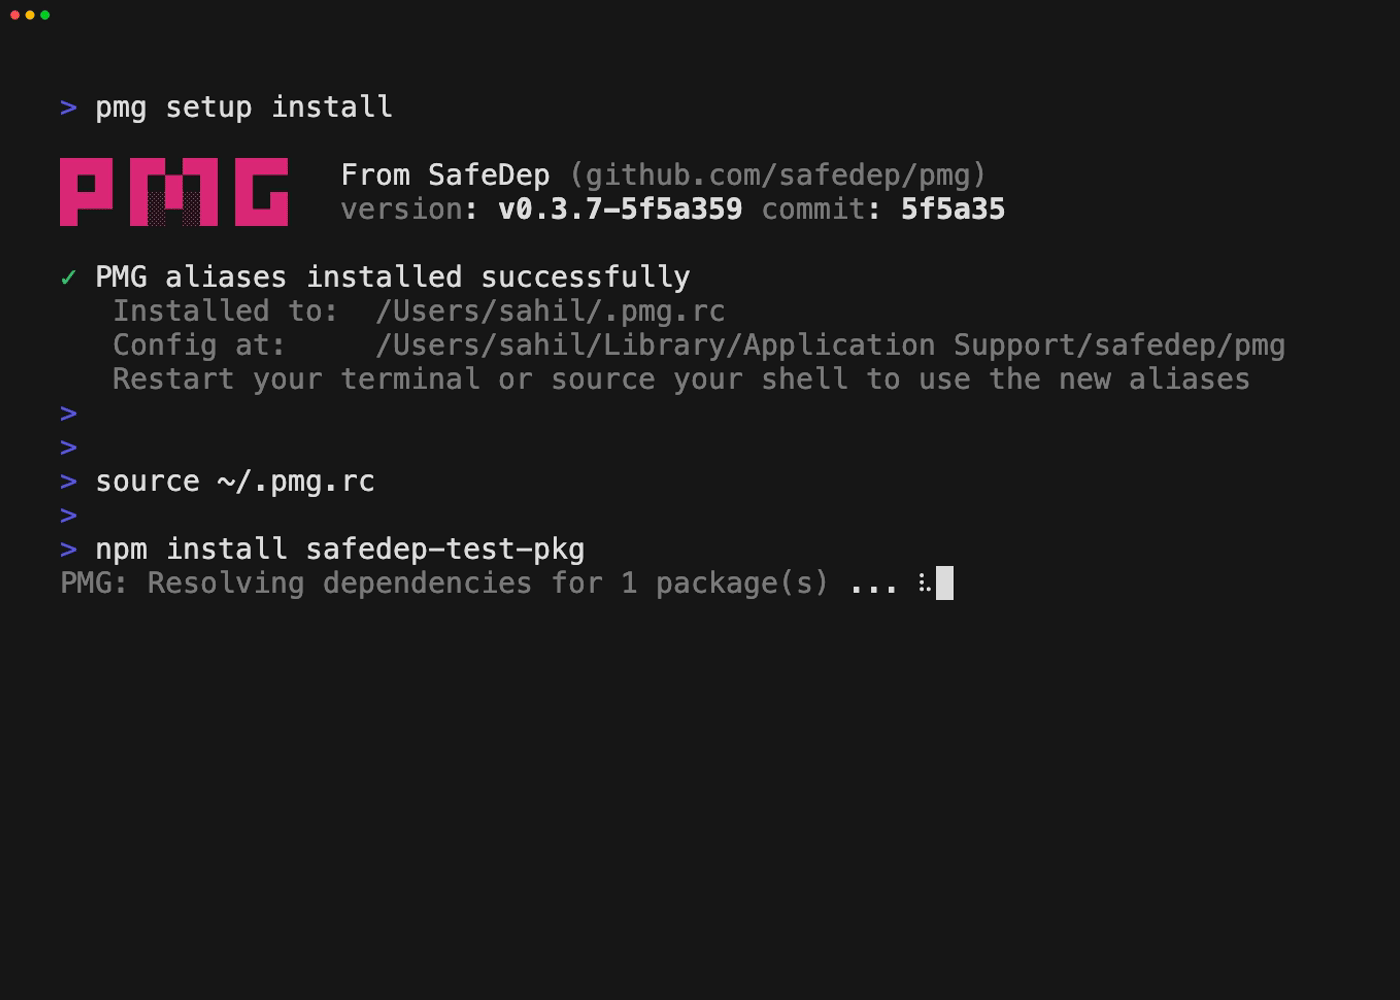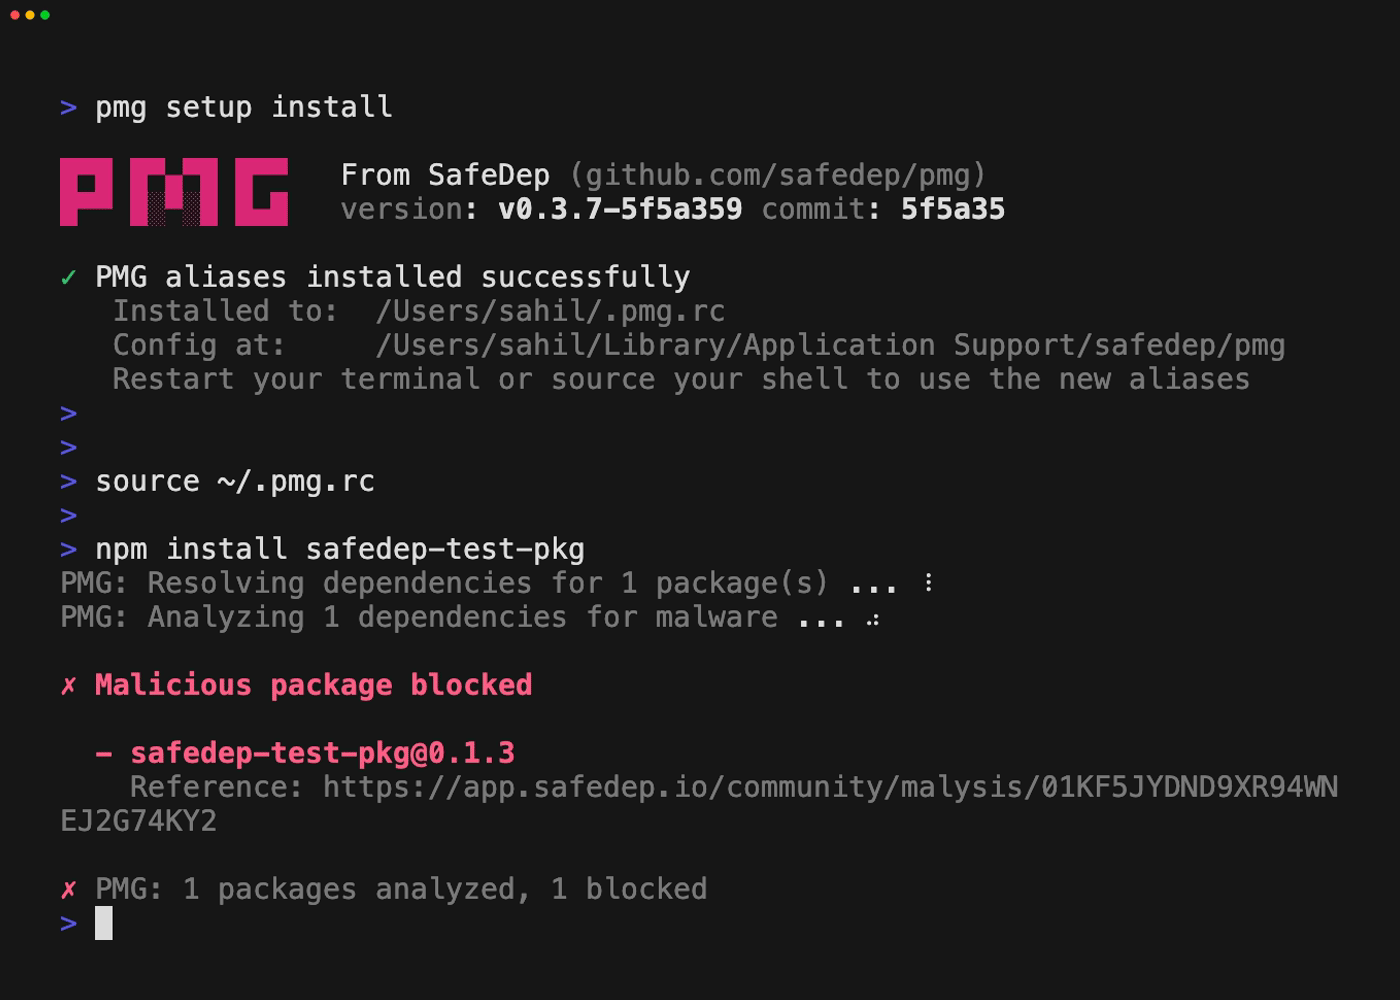
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.

cloud-securitycontainer-securitydevsecops+6
5530 days ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

android-securitydigital-forensicsdisk-forensics+7
15.5k1 day ago
cyberbro preview

cyberbro

GitHubstanfrbd/cyberbro

A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.

defensive-toolsdns-analysiseducation+9
6953 days ago
SSHintel preview

SSHintel

GitHubsonitbahl/sshintel

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

incident-responseintrusion-detectionlog-analysis+2
33 days ago
FIASSE preview

FIASSE

GitHubowasp/fiasse

A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)

code-analysiscurated-resourcesdevsecops+7
143 days ago
tpotce preview

tpotce

GitHubtelekom-security/tpotce

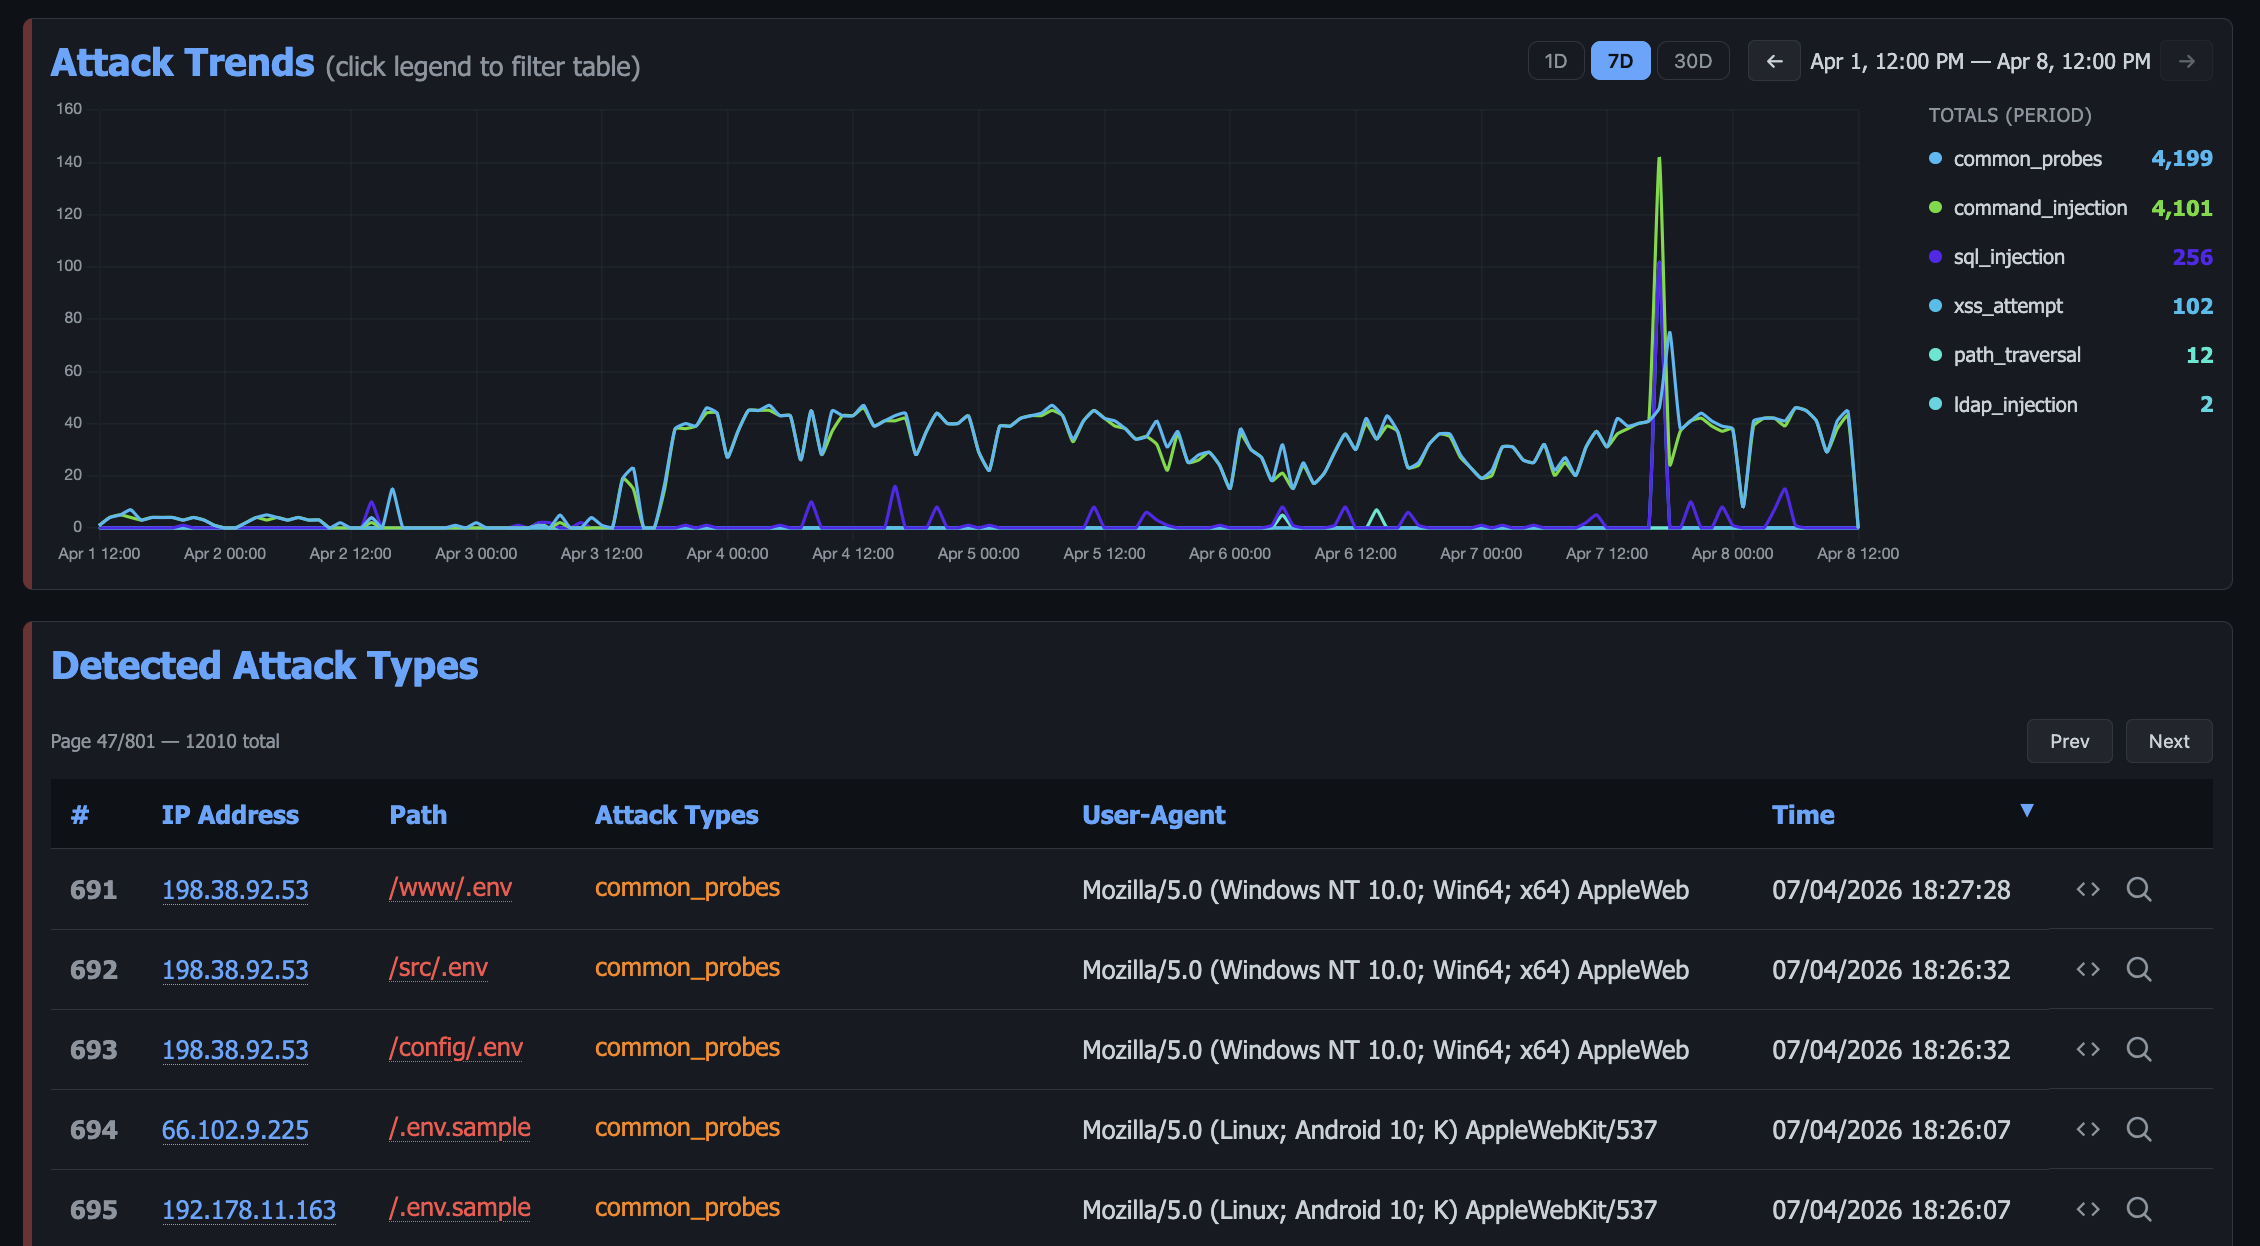
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
defensive-toolseducationinformation-gathering+7
9.6k4 days ago
Krawl preview

Krawl

GitHubblessedrebus/krawl

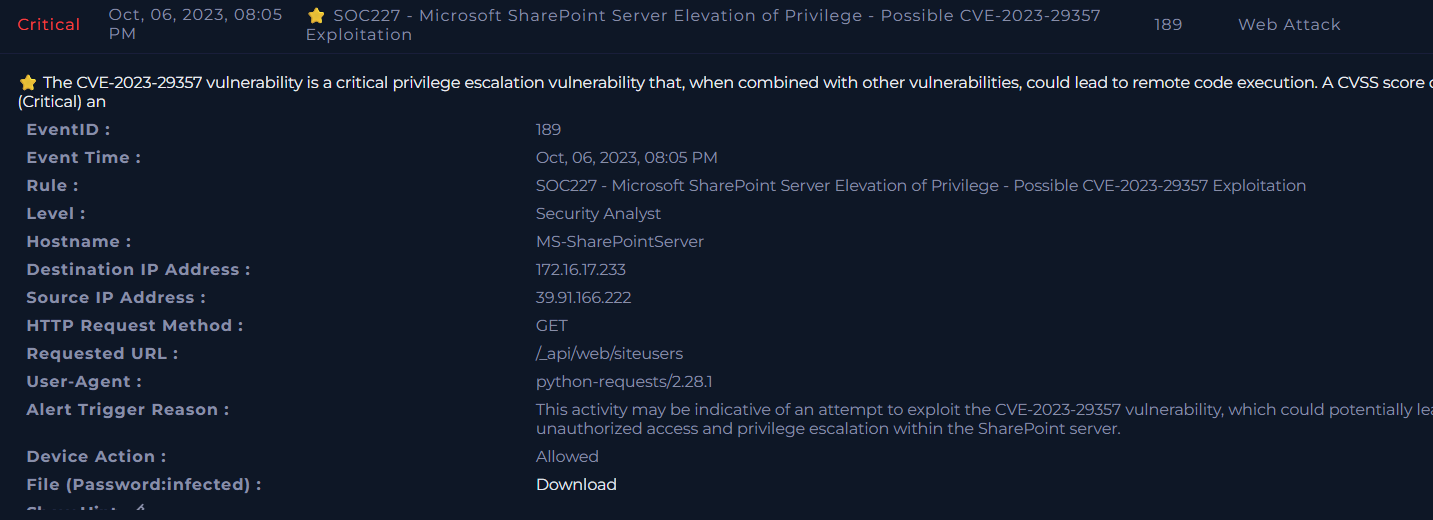
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
ai-securityanti-botcloud-security+6
7854 days ago
Sharepoint-cve-2023-29375-incident-response preview

Sharepoint-cve-2023-29375-incident-response

GitHubzedocun/sharepoint-cve-2023-29375-incident-response

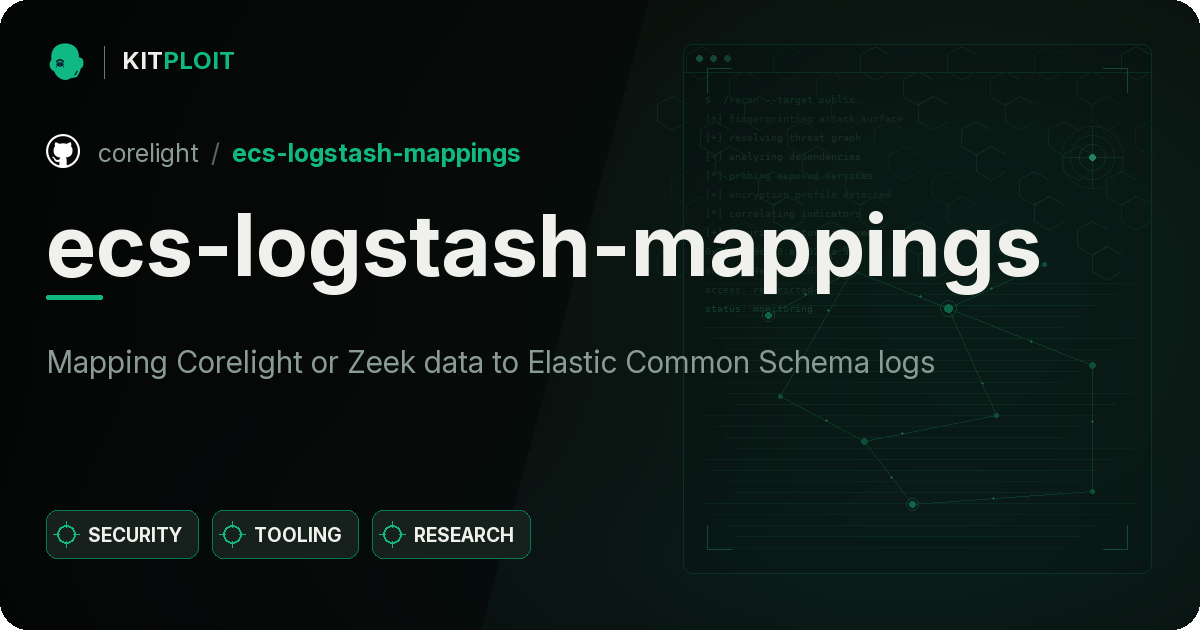
End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29357) using SIEM logs,…
digital-forensicseducationincident-response+3
14 days ago
ecs-logstash-mappings preview

ecs-logstash-mappings

GitHubcorelight/ecs-logstash-mappings

Mapping Corelight or Zeek data to Elastic Common Schema logs

incident-responseintrusion-detectionlog-analysis+2
126 days ago
dissect.cobaltstrike preview

dissect.cobaltstrike

GitHubfox-it/dissect.cobaltstrike

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
binary-analysiscommand-and-controldigital-forensics+4
2126 days ago
owLSM preview

owLSM

GitHubcybereason-public/owlsm

Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
cloud-securitycontainer-securitydefensive-tools+4
2806 days ago
Threat-Hunting preview

Threat-Hunting

GitHuba2awais/threat-hunting

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

educationincident-responseinformation-gathering+4
866 days ago
chainsaw preview

chainsaw

GitHubwithsecureopensource/chainsaw

Rapidly Search and Hunt through Windows Forensic Artefacts

defensive-toolsdigital-forensicsforensics+4
3.7k7 days ago
Previous123456Next