

mcpsafetywarden
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
ai-securitysecret-detectionstatic-analysis+3
9
gautamvarmadatla/mcpsafetywardenProxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 supermhel/fengarde
Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
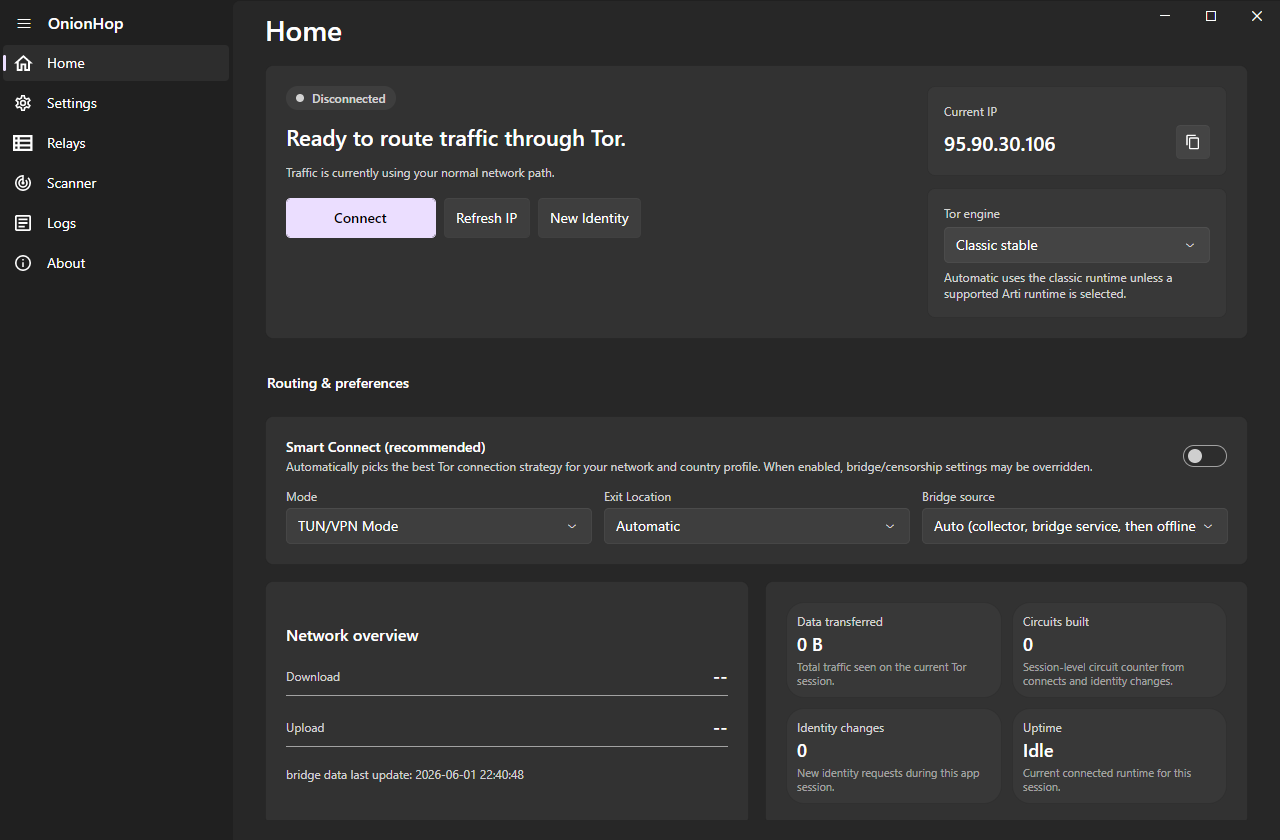 center2055/onionhop
Privacy-first Desktop app that routes your traffic through Tor - Anonymous browsing made simple
 specterops/nemesis
Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
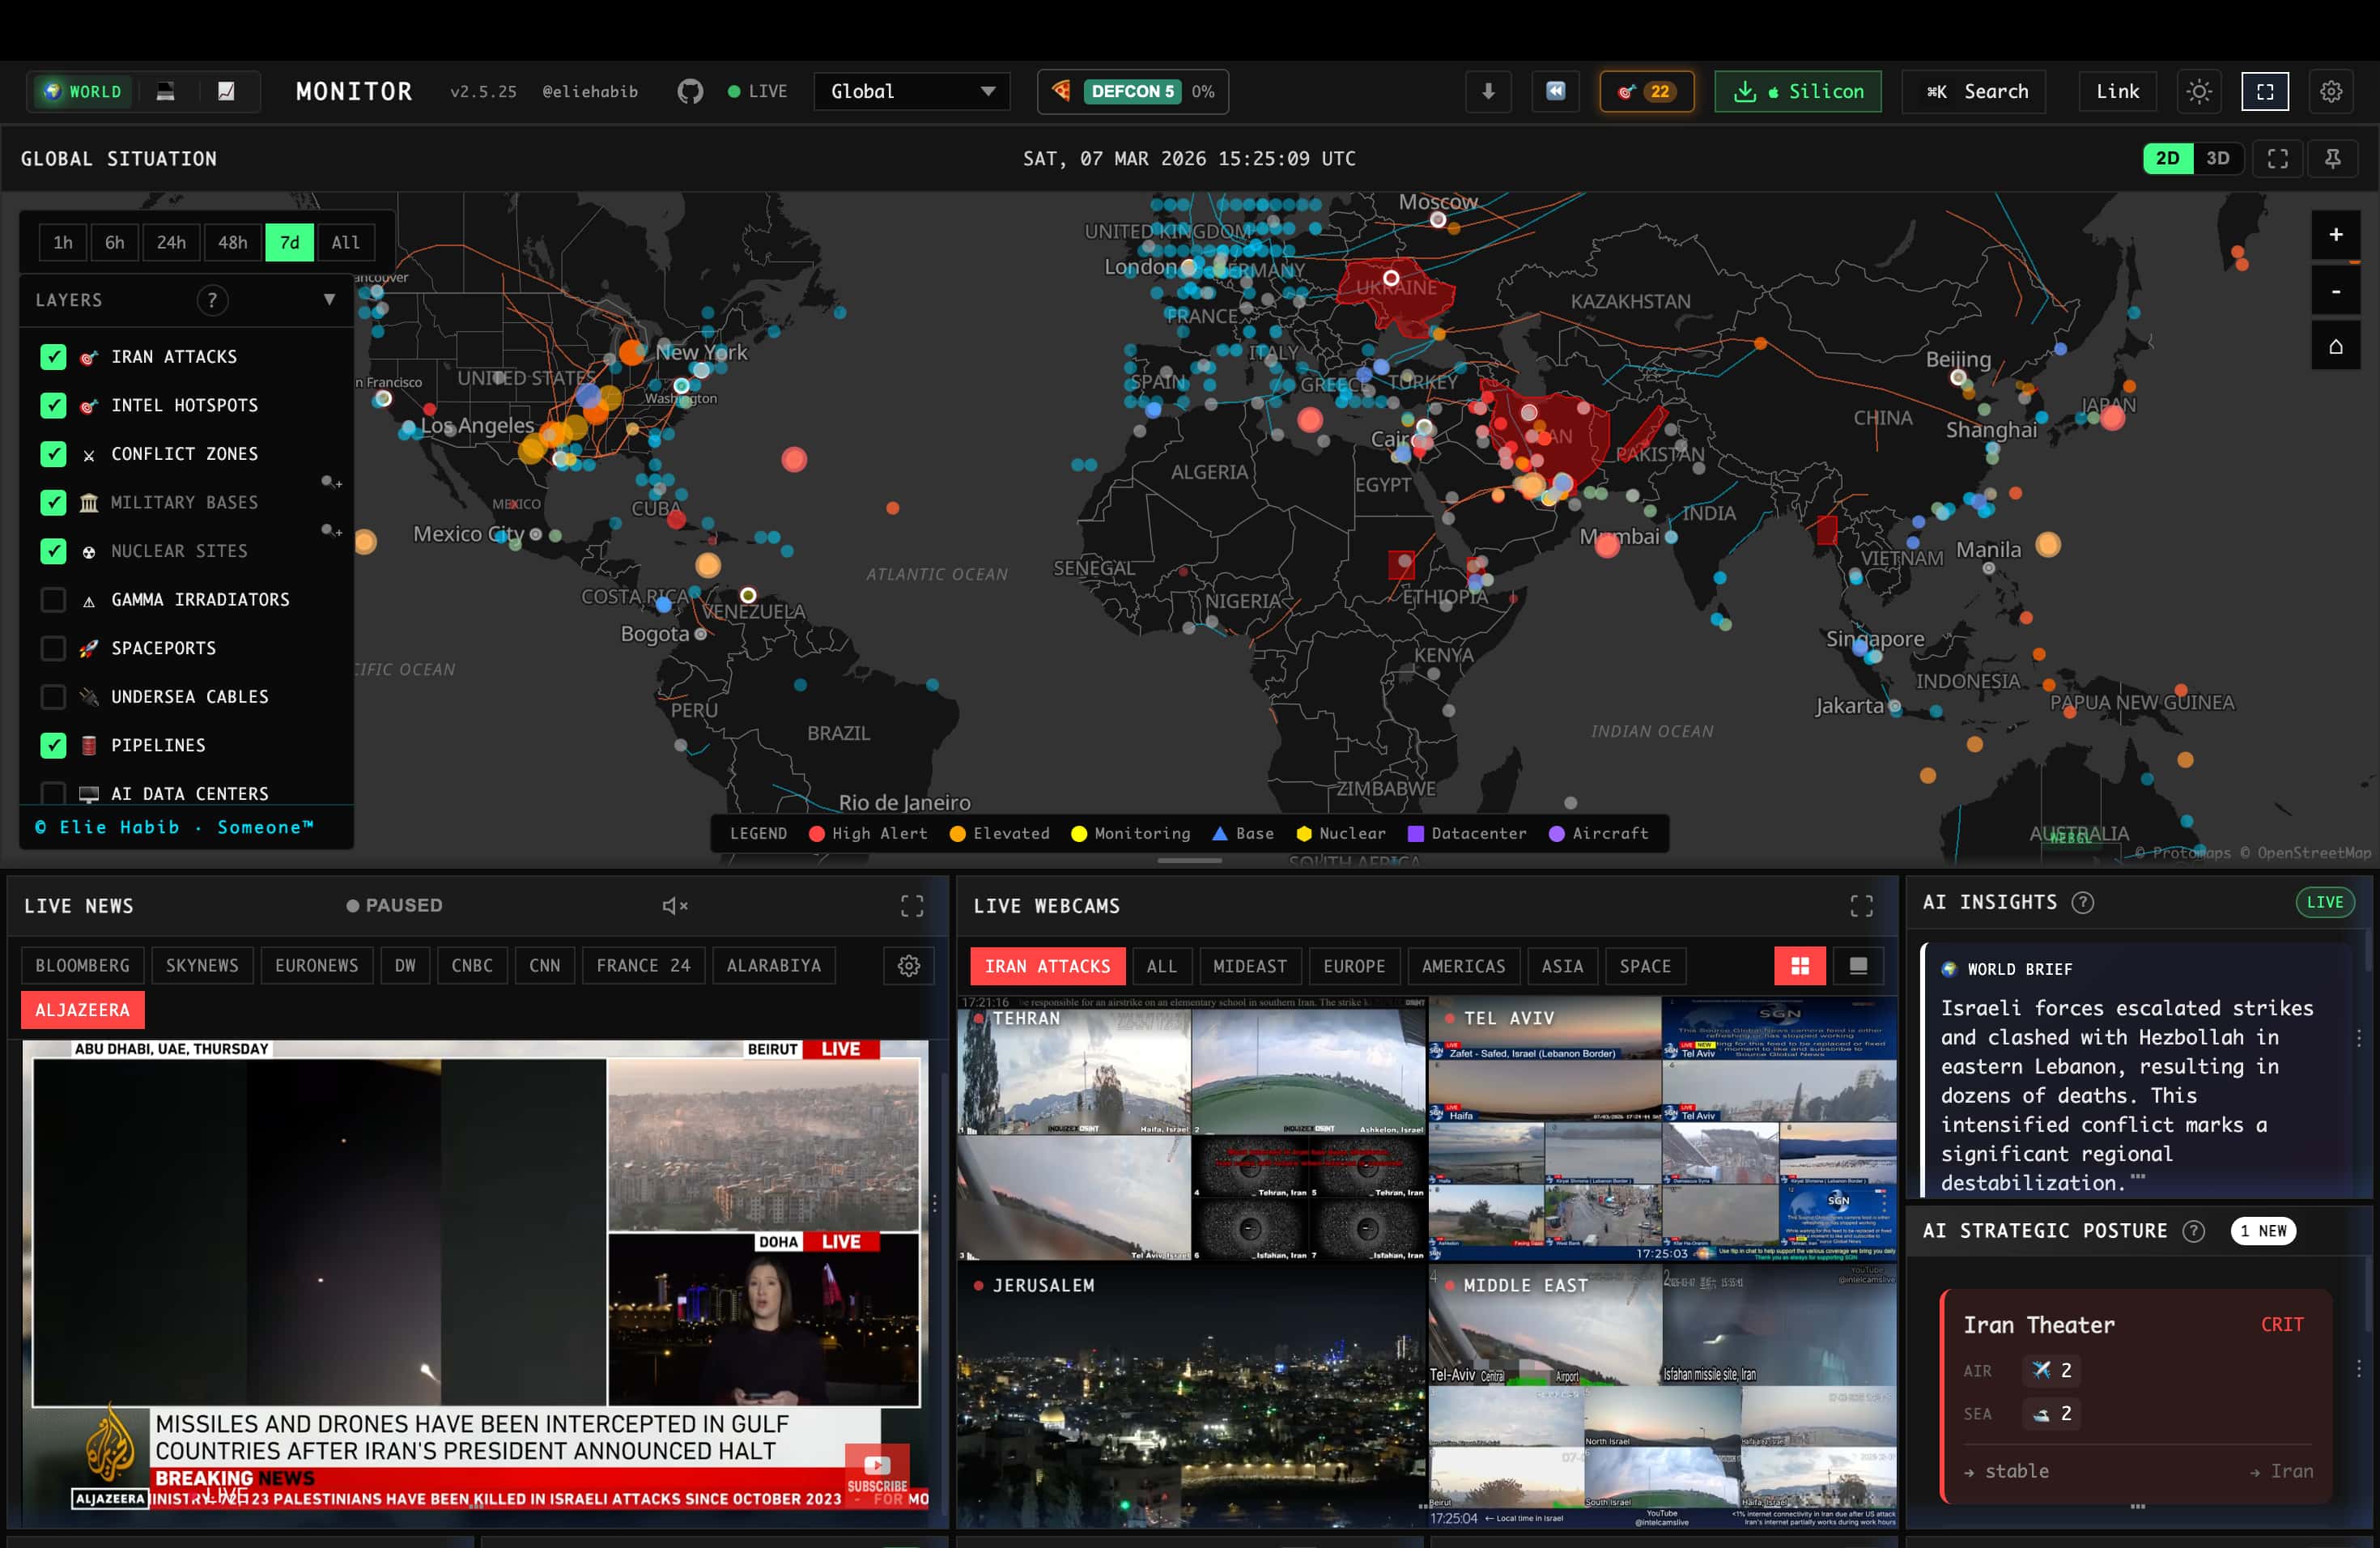 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 mandiant/vulnerability-disclosures
Curated repository of vulnerability disclosures from Mandiant, including CVEs discovered through internal research, red team assessments, and wild…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 cyberactivity/tyr
Tools collection to explore cyber security data like: * NVD CVE, CVE vendors, Cpe and CpeMatch, * Mitre CWE, CAPEC and Att&ck * Cisa (kev) data
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
 cyber-bansalai/vmware-vcenter-2026
Indicators and a read-only hunt guide for VMware vCenter CVE-2026-123890, from Google's report. One source, not tested, will go stale. Check the…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
 drb-ra/c2intelfeeds
Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…